# Control every app and privilege on your endpoints
## Just-in-time access control
Grant temporary application execution and privilege elevation, then automatically revokes access based on policy.
*Available only in Endpoint Central with Application Control and Endpoint Privilege Management add-on*
### Autonomous approval for elevation requests
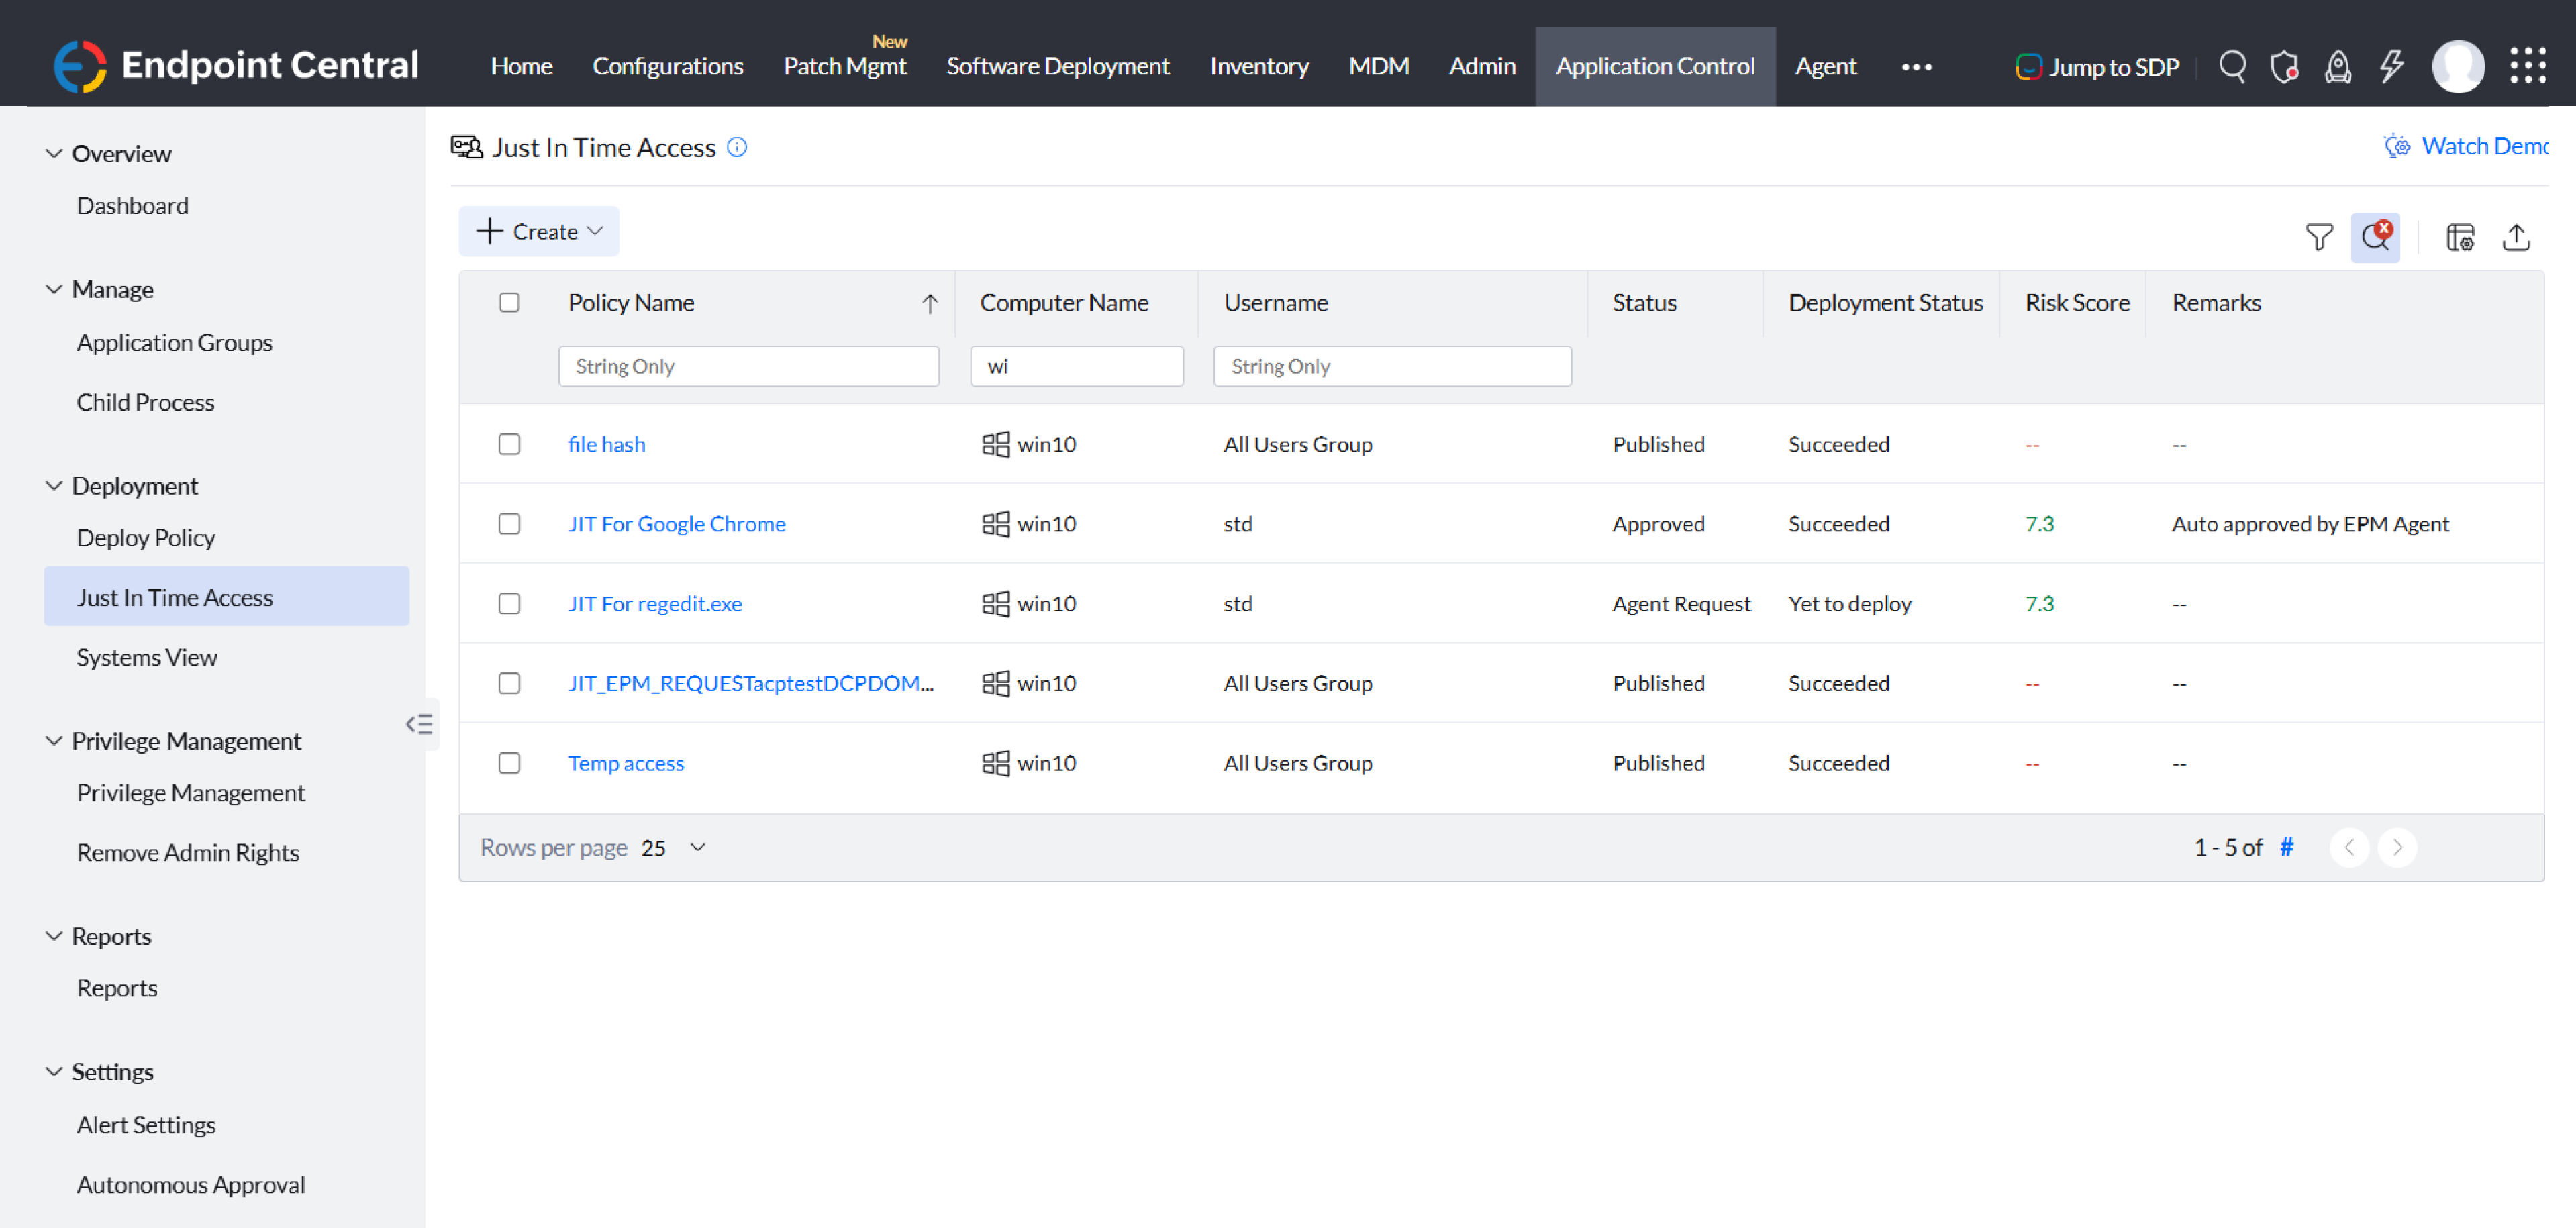
Automatically approve trusted elevation requests using confidence scoring and policy context.
### Eliminate shadow IT risk
Gain visibility into unapproved software and decide what runs in your environment.
### Just-in-time access control
Grant temporary application execution and privilege elevation, then automatically revoke access based on policy.
### Passwordless application elevation
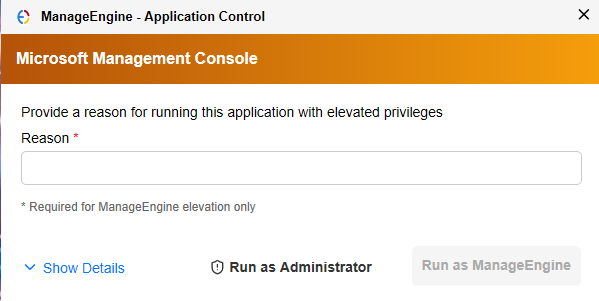
Run approved applications with elevated privileges without exposing admin credentials.
### Identify and remove unnecessary admin rights
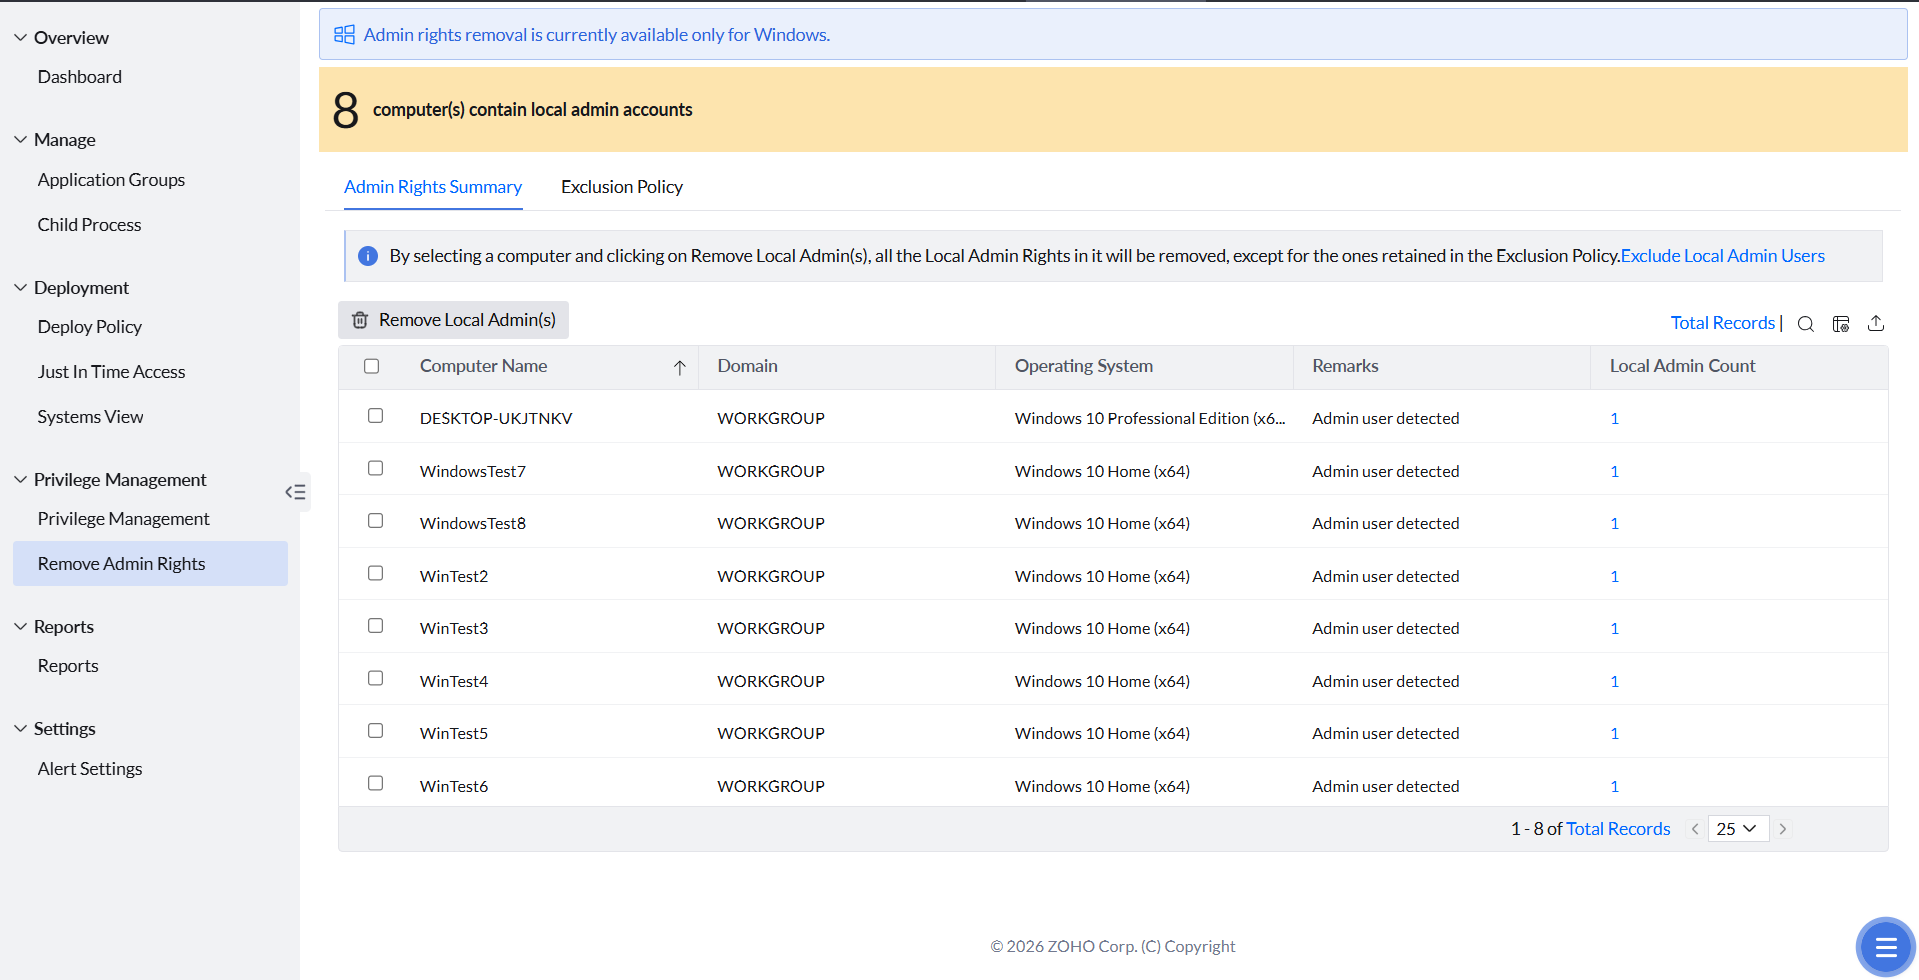
Detect systems with local admin accounts and remove excess privileges.
## Block the unknown. Elevate only when necessary.
### Application Control

Stop unauthorized applications from running on endpoints.
-  [Allowlist](https://www.manageengine.com/application-control/application-allowlisting.html?acp-new-homepage-features) and [blocklist apps](https://www.manageengine.com/application-control/application-blocklisting.html?acp-new-homepage-features)
- Create rules to allow trusted applications and block risky or unapproved software.
-  [Audit unauthorized applications and block events](https://www.manageengine.com/application-control/unmanaged-applications.html?acp-new-homepage-features)
- See what would be blocked before enforcement. Track unmanaged executions and block attempts.
-  [Just-in-time application access](https://www.manageengine.com/application-control/just-in-time-access.html)
- Temporarily allow specific apps when needed and revoke access automatically.
### Endpoint Privilege Management

Grant temporary admin access when users need it.
-  [Eliminate excessive admin privileges](https://www.manageengine.com/application-control/remove-admin-rights.html?acp-new-homepage-features)
- Eliminate standing local admin access to reduce attack surface.
-  [Passwordless, app-specific elevation](https://www.manageengine.com/application-control/request-access.html?acp-new-homepage-features)
- Elevate only the app or task without sharing admin passwords.
-  [Just-in-time elevation access](https://www.manageengine.com/application-control/just-in-time-access.html?acp-new-homepage-features)
- Grant time-bound elevation and auto-revoke based on policy.
-  [Elevate control panel and administrative tools](https://www.manageengine.com/application-control/how-to/epm-elevate-com-objects.html?acp-new-homepage-features)
- Allow standard users to securely access Control Panel applets and built-in administrative tools without full admin rights.
## Know what runs. Control what matters.
Discover what runs, validate in audit mode, then apply policy-based control.
### 01. Discover

Identify applications running across endpoints.
### 02. Audit

Monitor execution and policy impact without disrupting users.
### 03. Enforce

Allow only approved applications and blocks everything else by policy.
## Pick the Right Path to Control
Start free to validate policies. Upgrade when you are ready to roll out controls at scale.
| Free Edition | Professional Edition |
|---|---|
| $0
up to 25 endpoints | $6
/ endpoint per year* |
-  Application allowlisting and blocklisting
-  Audit mode visibility for apps and elevation
-  Policy-based control for execution and privilege
-  Elevation workflows without sharing admin credentials
-  Reporting and activity trail for governance
The more you scale, the lesser you pay per endpoint.
*for 1000 endpoints*
### Explore Endpoint Central
Want complete endpoint protection?
+ Everything in Application Control Plus
-  Vulnerability management
-  Patch Management
-  Enterprise data security
-  Data loss prevention
-  Endpoint detection and response
-  Enterprise browser security
-  Peripheral device control