Install, Uninstall & Migrate Agents with a GPO Tool
Windows GPO is a powerful and versatile tool. Agent can be installed, uninstalled or migrated using the GPO light-weight tool.
Advantages
- The GPO Lightweight Tool is a simple and user-friendly tool for configuring Group Policy Objects (GPO) to deploy agent installations, whether through startup processes or scheduled tasks.
- It also allows to uninstall/ re-install agents through GPO without complexity on configuring the GPO.
Disadvantages
- The disadvantages of the GPO startup script and scheduled task methods are inherited.
- Note:
- The GPO lightweight tool only supports .exe files and does not support .MSI files.
- Kindly use account with Domain Admin credentials .
- If a new GPO policy is applied, the installation for existing installed agents will be skipped on all machines. The remaining agents will be installed according to the new policy. This applies to Installation policies. A Migration policy runs the Cleanup Tool and the agent installer on all computers linked to the policy, including computers where the agent is already installed, unless they are excluded.
- The agent installer added to the tool is installed on the computers as it is. An installer downloaded earlier may be of an older version, and an agent installed from an older installer does not upgrade automatically.
Follow the steps given below to create a Group policy and link it with OUs and Domains:
Steps
1. Select the account details
- Open the Domain Controller of the required AD in which the GPO needs to be configured.
- To download the GPO tool for build version [old version here] click here.
- To download the GPO tool for build version [new version here] click here.
- Execute the Tool As an administrator
- Select "Continue with above details" and click next.
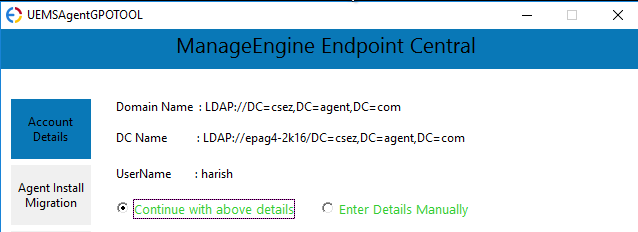
- If you encounter an error in fetching the domain or domain controller name or if you would like to execute the tool from another machine instead of the domain controller machine, select the enter details manually option. Kindly use account with domain admin credentials privilege.
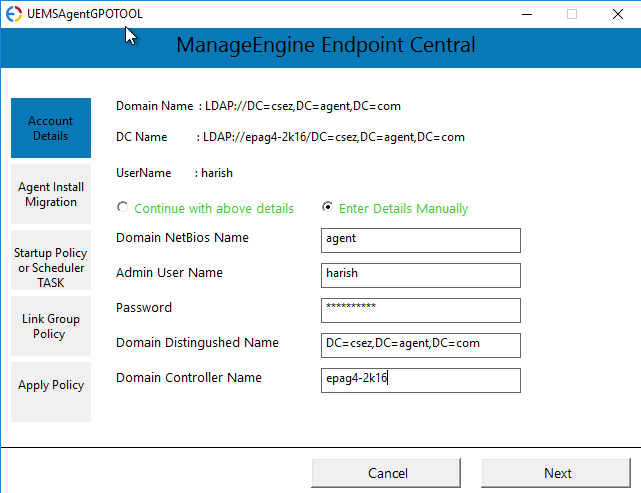
To get the domain or OU Distinguished name, follow these steps:
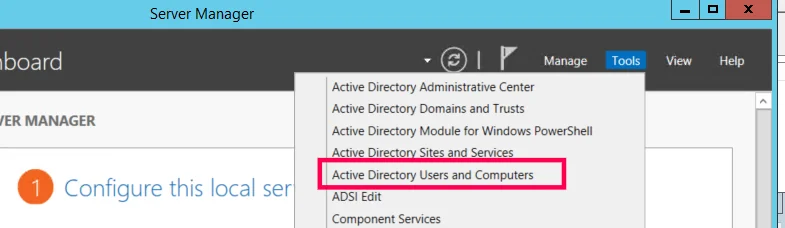
- Under Administrative tools, open the active directory users and computers.
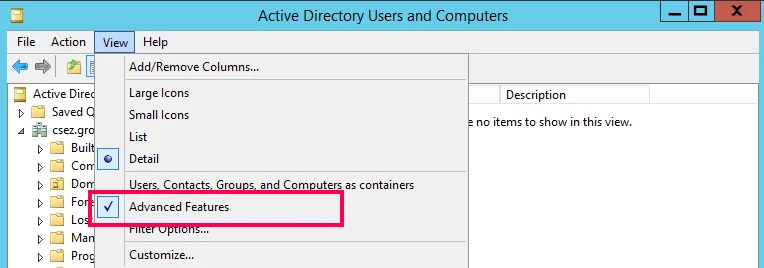
- Under View, enable Advanced Features.
- Right click on the OU / Domain and Select Properties -> Attribute Editor -> distinguishedName -> View
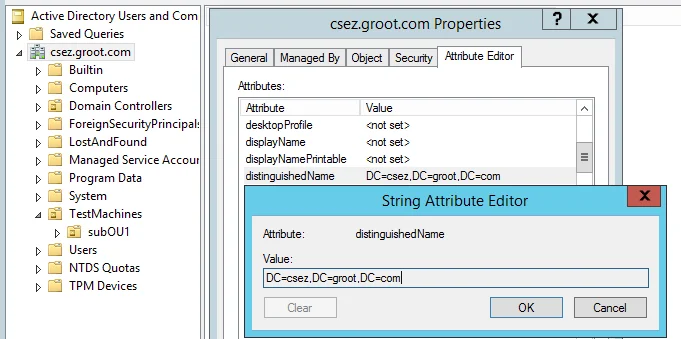
- A GPO can be linked only to an Organizational Unit or to the domain. It cannot be linked to default containers such as Computers, Users or Builtin. For computers in a default container, select Entire Domain in the Link the GPO step.
2. Choose the required action
- Select the required action ( Installation \ Uninstallation \Migration)
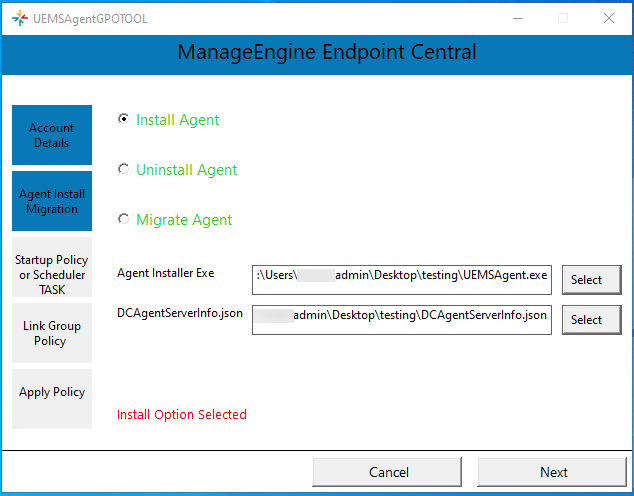
If you choose installation, For the agent installer .exe, follow these steps:
- Open the server web console.
- Navigate to Agent -> Scope of Management -> Computers.
- Under the Managed Computers tab, click Bulk Installation. You can also click Download Agent and then select the Bulk agent install link. To learn how to fill in the agent and deployment details on this screen, see Bulk agent installation using a deployment token.
- Click Download Agent. A .zip file is downloaded.
- Copy the Deployment Token.
- Extract the .zip file. It contains the agent installer .exe and DCAgentServerInfo.json.
- In the GPO tool, click Select next to Agent Installer .exe and choose the extracted .exe.
- Click Select next to DCAgentServerInfo.json and choose the extracted JSON file.
- Paste the copied Deployment Token in the Bulk Install Token field.
- Click Next.
NoteIf your Endpoint Central server is on a build version lower than [Insert Build Number], the agent will download as a single .exe. In this case, you will not have or need the DCAgentServerInfo.json file. In the GPO tool, click Select next to Agent Installer .exe and choose the downloaded .exe.NoteIf your Endpoint Central server is on a build version lower than [Insert Deployment Token Build Number], navigate to Agent -> Computers, select the required remote office, choose the Windows OS Platform, and click Download Agent.
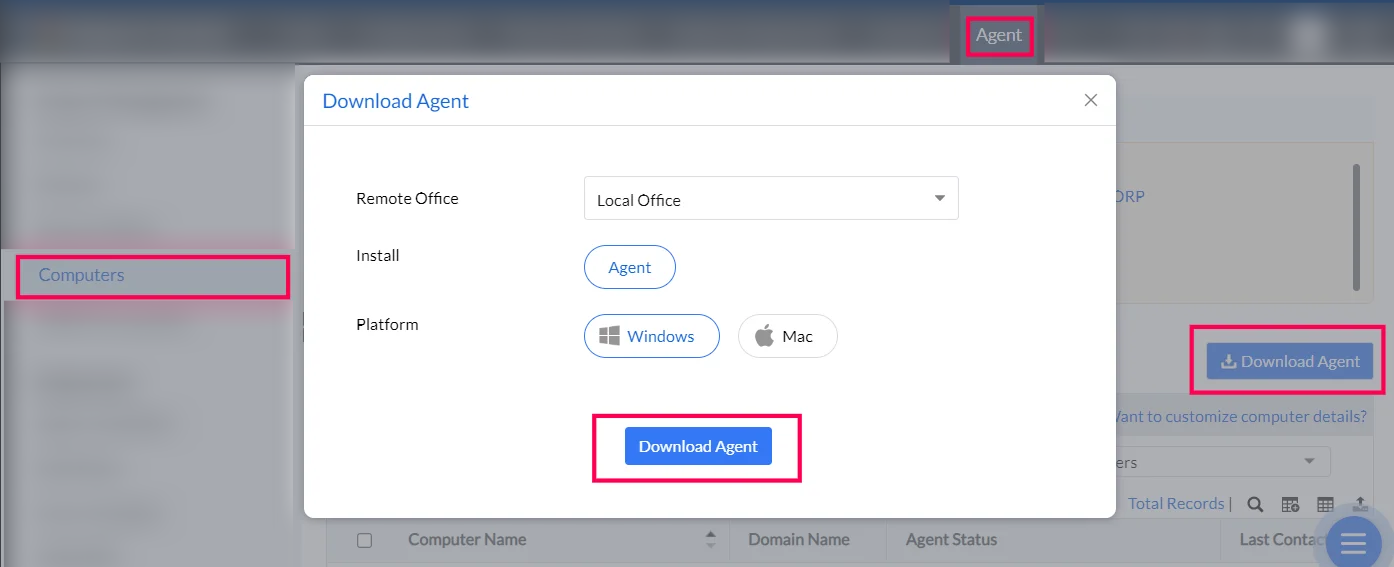
If the domain has multiple remote offices with Distribution Servers, select the Local Office agent and configure IPSCOPE under Agent -> Settings -> IP SCOPE. The computers are then moved to the correct remote office automatically, based on their IP address. For details, see Managing roaming users.
If you choose uninstallation use the AgentCleanupToolClient.exe. Follow the steps given in this document to generate the Cleanup tool.
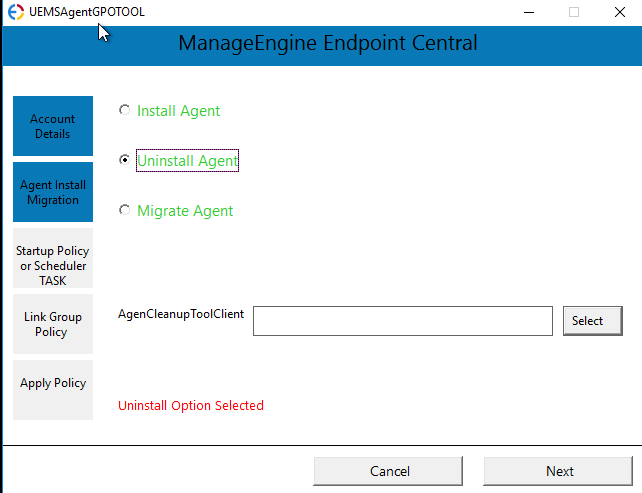
If you choose migration, use Agent Installer exe and AgentCleanupToolClient.exe. Follow the steps given in this document to generate the Cleanup tool.
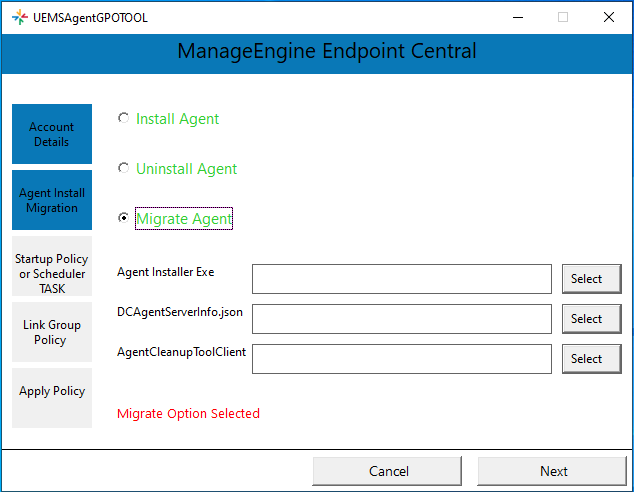
For the agent installer .exe, follow these steps:
- Open the server web console.
- Navigate to Agent -> Scope of Management -> Computers.
- Under the Managed Computers tab, click Bulk Installation. You can also click Download Agent and then select the Bulk agent install link. To learn how to fill in the agent and deployment details on this screen, see Bulk agent installation using a deployment token.
- Click Download Agent and extract the downloaded .zip file.
- Copy the Deployment Token.
- In the GPO tool, select the extracted .exe in Agent Installer .exe, the extracted JSON file in DCAgentServerInfo.json, and the Cleanup tool in AgentCleanupToolClient.
- Paste the copied Deployment Token in the Bulk Install Token field.
- Click Next.
3. Choose the Policy details
- Enter the Name of the GPO [eg : MEECAgentInstall ] -> Enter the policy type [Startup or scheduler ] -> Select the Script type [powershell script is always recommended]
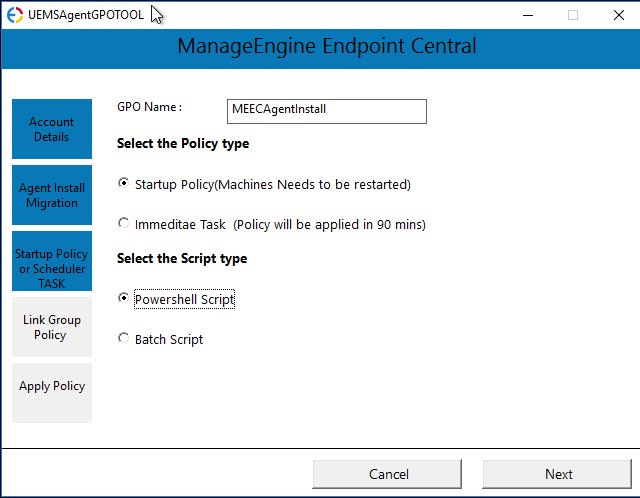
-BulkInstallToken value in the PowerShell script is the Deployment Token you copied from the Bulk Installation screen.4. Link the GPO
- To apply policy to entire domain, select "Entire Domain".
- To apply the policy to a specific OU , enter the OU distinguished names and click next. (To obtain the OU distinguished name, refer to the first step.)
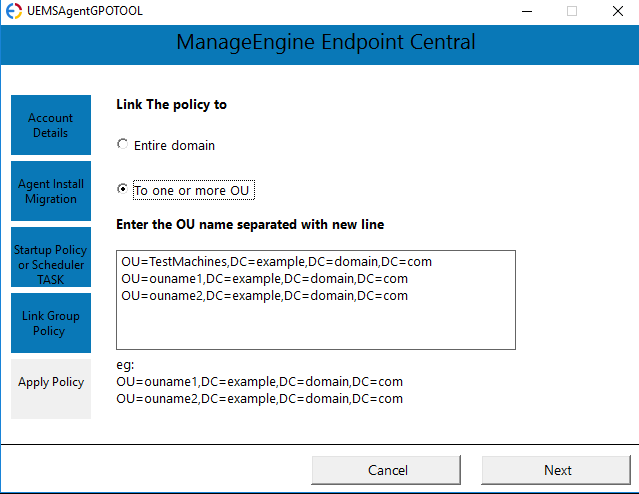
5. Confirm the details
- Confirm the policy details and click next
- The policy has been successfully created
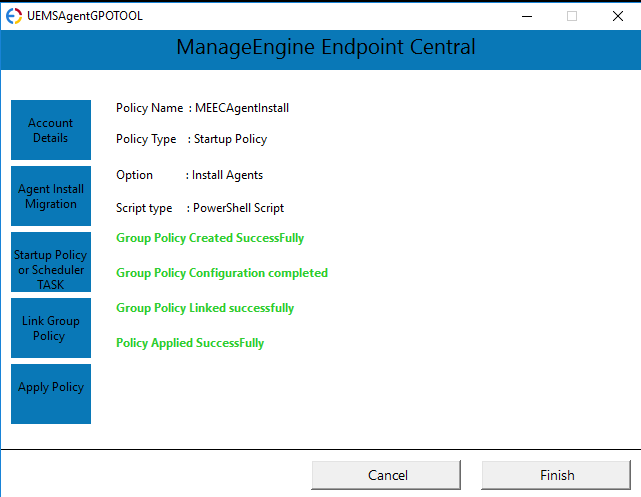
To test the policy in a machine Immediately after creation, follow the steps below:
- Open the client machine -> Command prompt as an admin and execute the command gpupdate /force
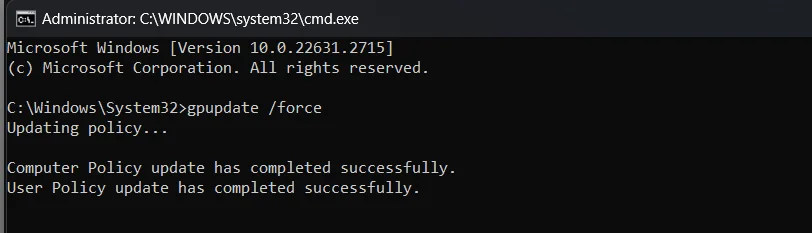
- Once the policy update is completed restart the machine if the "Start-up" policy is configured.
- For "Immediate Task" policy will be applied once the policy update is completed.