First, configure Audit File System policy using GPOs and add SACL entries at file/folder level. Next, track EventID 4663 using EventViewer or PowerShell. However, you may also use auditing solutions like ADAudit Plus.
- Native auditing
- Powershell
- ADAudit Plus
- FAQ and troubleshooting
In Active Directory (AD) environments, unauthorized or unplanned file changes can pose significant security and compliance risks. To check who last modified a file in Windows shall be performed with help of EventViewer, PowerShell commands and real-time auditing solutions like ADAudit Plus.
Following are the steps involved to track who modified a file or folder in a Windows server with EventViewer:
1. Tracking who last modified a file using Native Auditing
1.1 Enabling file auditing policies using GPMC.
In order to record the file activities performed in a Windows Server, file auditing policies have to be enabled using GPMC for domain joined-servers or using Local Security Policy for a local server.
The following are the steps involved to enable the auditing policies.
- For domain-joined servers
- Open the Group Policy Management Console (GPMC) or execute the command gpmc.msc in Run.
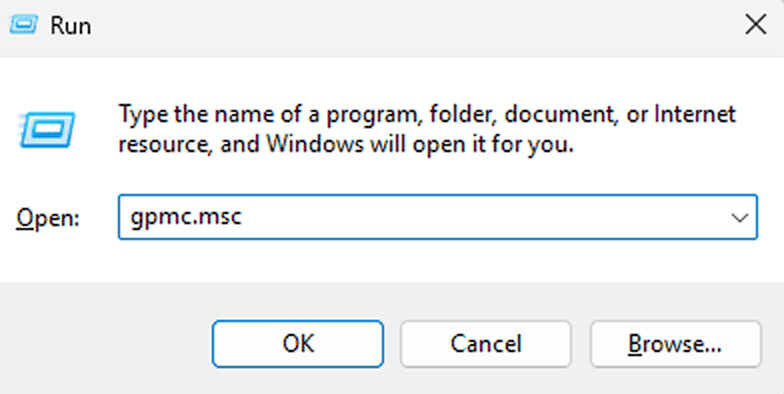
Fig 1: Run menu with "gpmc.msc" command - Navigate to the preferred domain.
- For all user accounts: Right-click the domain name and select Create a GPO in this domain, Link it here. For select users in an OU: Right-click on the OU and select Create a GPO in this domain, Link it here.
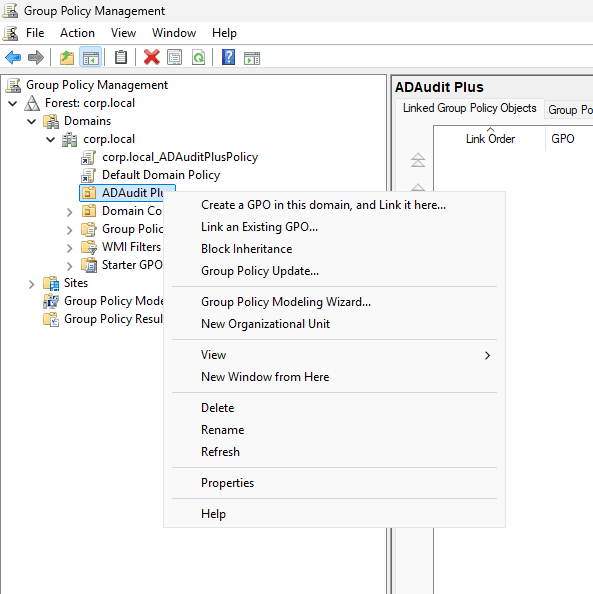
Fig 2: Default domain policy in GPMC - Provide a relevant name for the GPO, right click it and select Edit.
- Navigate to Computer Configuration > Polices > Windows Settings > Security Settings.
- Open the Group Policy Management Console (GPMC) or execute the command gpmc.msc in Run.
- For a local server
- Open the Local Security Policy console or execute the command secpol.msc.
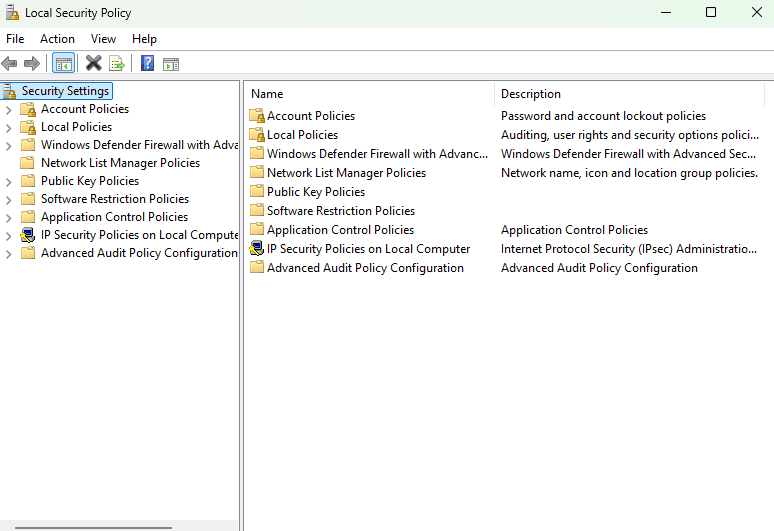
Fig 3: Security settings in Local Security policy
- Open the Local Security Policy console or execute the command secpol.msc.
- Select Advanced Audit Policy configuration and navigate to Audit Policies > Object Access > Audit File System.
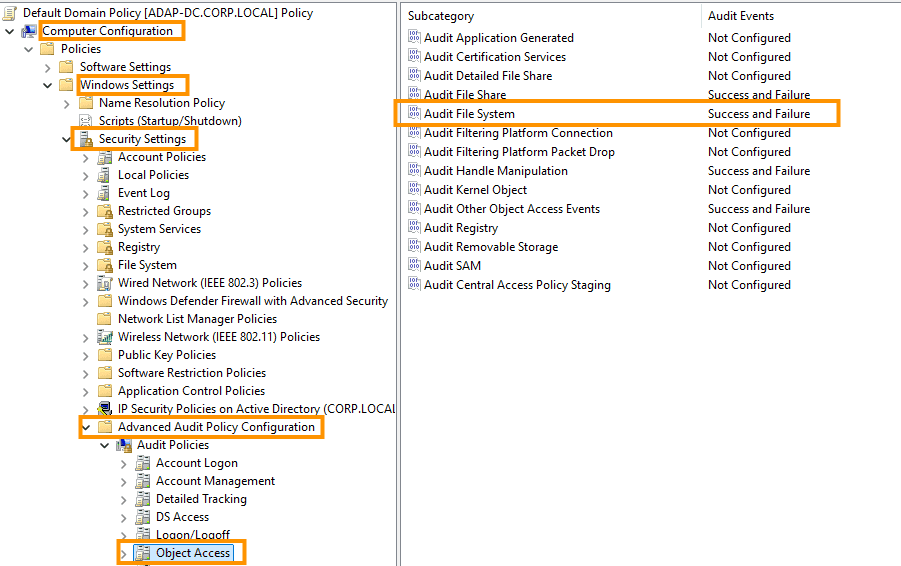
Fig 4: Audit File system policy Note
Audit File System is an audit policy to track access/modifications performed to a file/folder.
- Select Success and Failure checkboxes to audit both attempts.
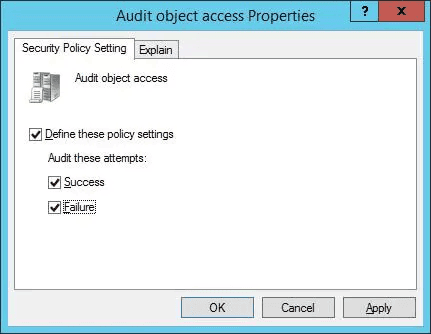
Fig 5: Audit File System policy settings - Click Apply and then Ok to close the window.
Only for domain-joined servers:
Go back to the GPMC, right-click the OU or domain to which newly created GPO was linked to.
Select Group Policy Update to instantly apply the enabled audit policies.
1.2 Adding Auditing (SACL) entries at file/folder level
SACL is a Windows security feature that is used to record attempts to access or modify objects such as files, folders, registry keys. Thus, in order to track who modified, SACL entries must be added at the file/folder level.
Below are the steps used to add a SACL entry:
- Open Windows Explorer and navigate to preferred file/folder.
- Right click it and select Properties.
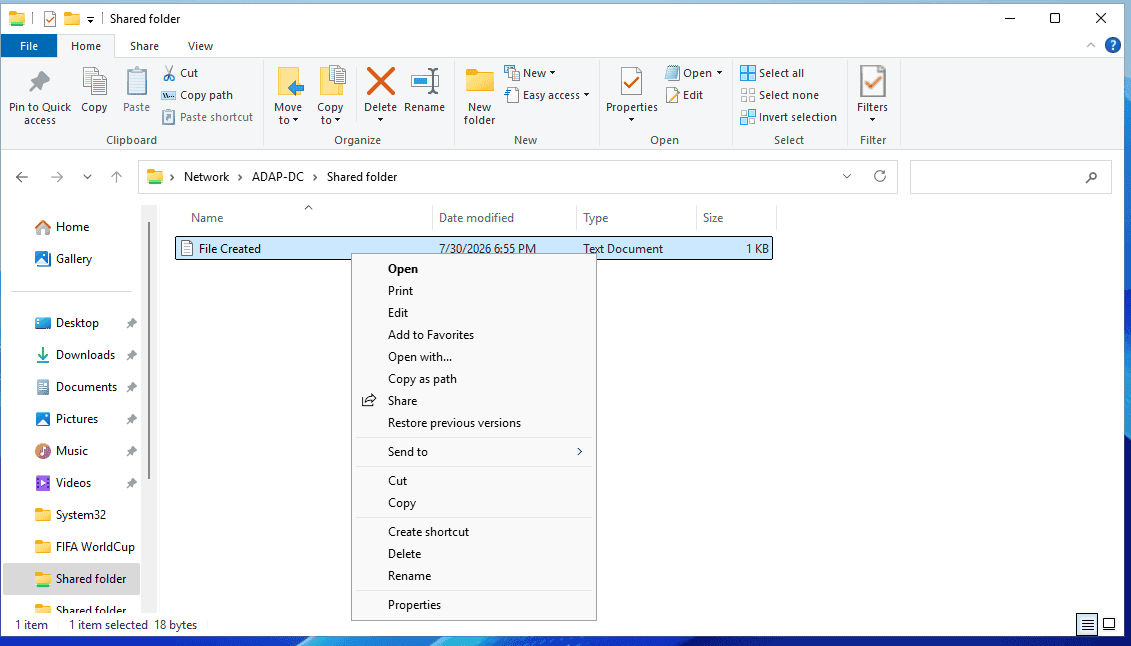
Fig 6: Navigating to file properties - Switch to Security tab and click on Advanced option to view the Advanced Security Settings.
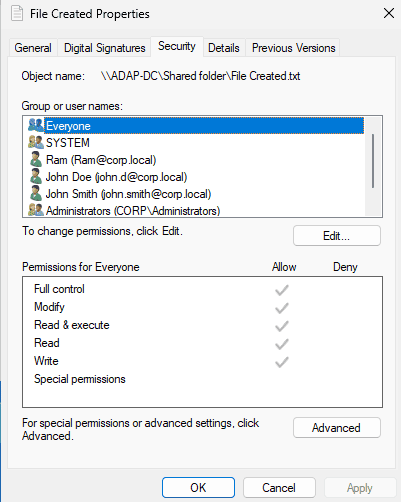
Fig 7: Advanced Security Settings - Switch to Auditing that displays existing auditing entries.
- Click Add to create a new auditing entry.
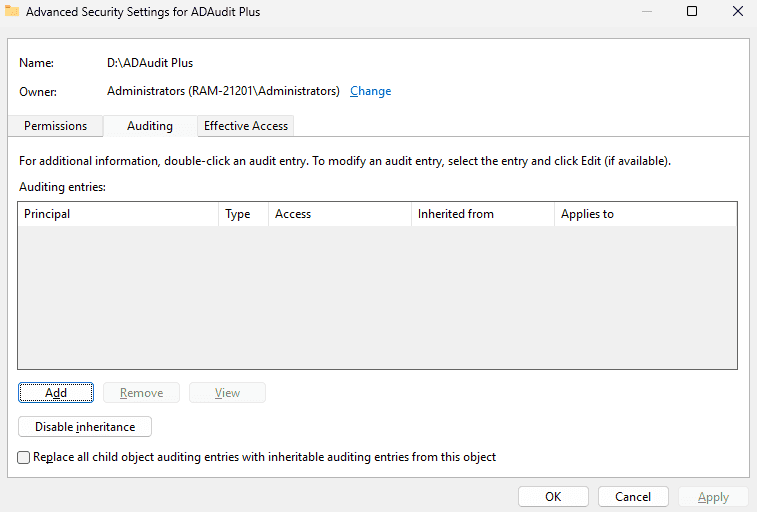
Fig 8: Adding SACL entries - Select Everyone under Principal option to audit changes by all user accounts.
- Click on Advanced security permissions, and select the preferred actions. Below are the recommended actions to be enabled:
Access Type Description Example ReadData Someone opened or read the file’s contents. A user opened a text document. WriteData Someone changed or overwrote the file’s contents. A user saved edits to a Word or Excel file. AppendData Someone added new data to the end of the file without replacing existing content. A program added new lines to a log file. ReadAttributes Someone checked the file’s basic info, like its size or modified date. File Explorer displayed the file’s details. WriteAttributes Someone changed file properties such as the timestamp. A script modified the last modified date. - Click Ok to save the auditing entry.
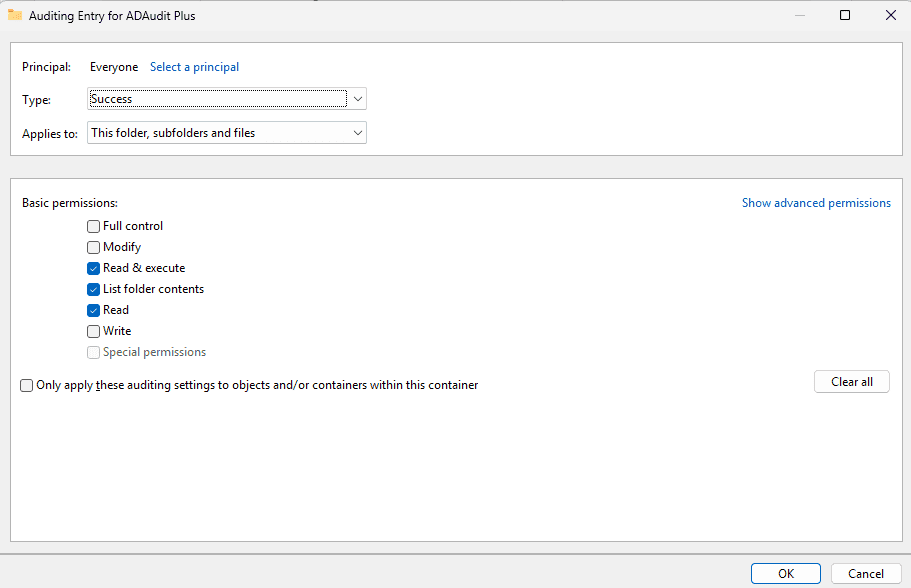
Fig 9: Configuring Auditing Entry - Click Apply and, then Ok.
1.3 How to check who last modified a file in EventViewer
Once the auditing policies and auditing entries are configured, the events created can be viewed in EventViewer.
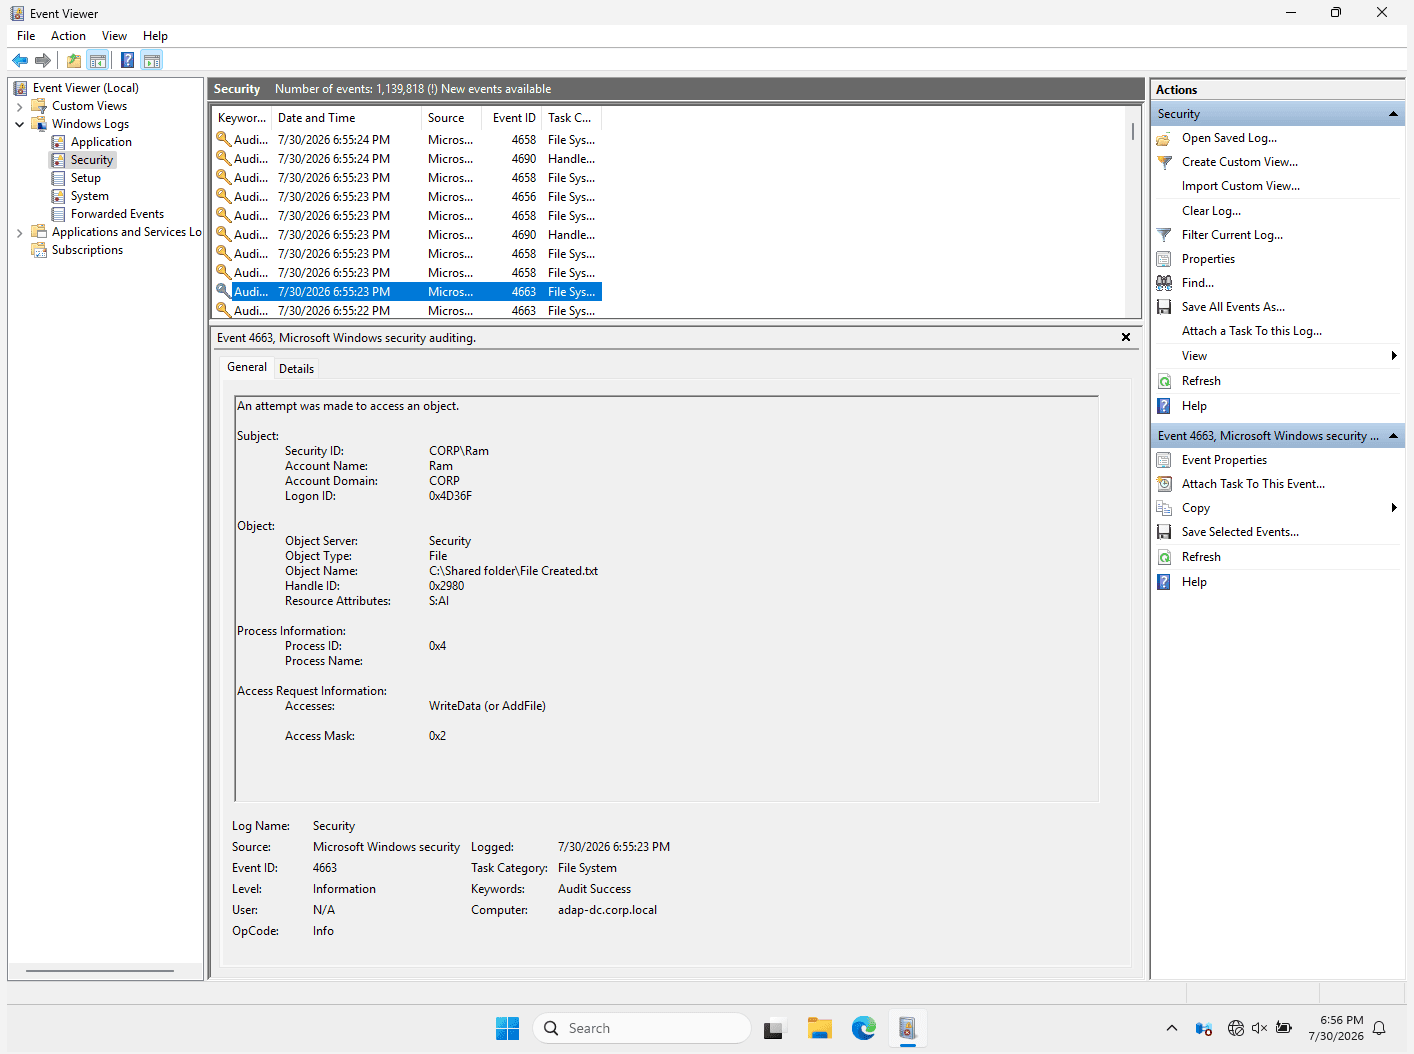
Event ID 4663 - An attempt was made to access an object is generated when a particular operation is performed on an object like files/folder. This helps in identifying if file activities such as Read, Write, Delete, or Moved were performed. Using this event, we can derive:
- Account Name: The user who accessed or modified a file/folder.
- Object Name: The complete path of the file or folder.
- Accesses: The type of modification performed.
- Process Name: The program used to perform the modification.
Tip
You can also use EventID 4663 to track who moved a file from one folder to another. When a file is moved, an event is triggered with Accesses as DELETE with the original path and an event with Accesses as WriteData is triggered with the destination path.
Tracking EventID 4663 using Event Viewer
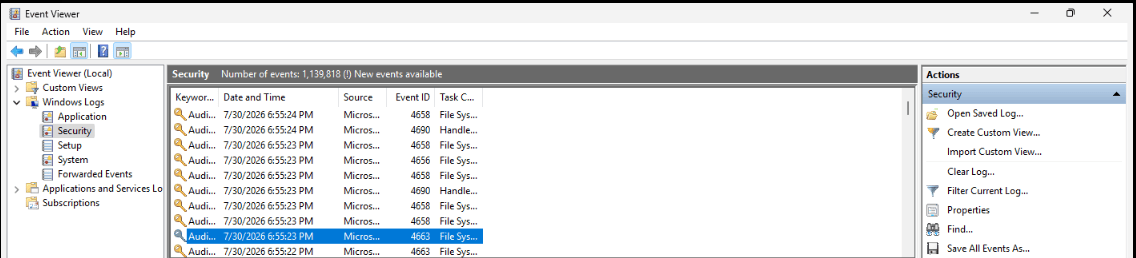
- Open EventViewer or execute the command eventvwr.msc using Run command
- On the right pane, navigate to Security > Filter current log
- In the pop-window and under All Event IDs, enter 4663 to filter all its occurrences
- Double-click on each occurrence and view its properties.
2. How to track who last modified a file/folder using PowerShell
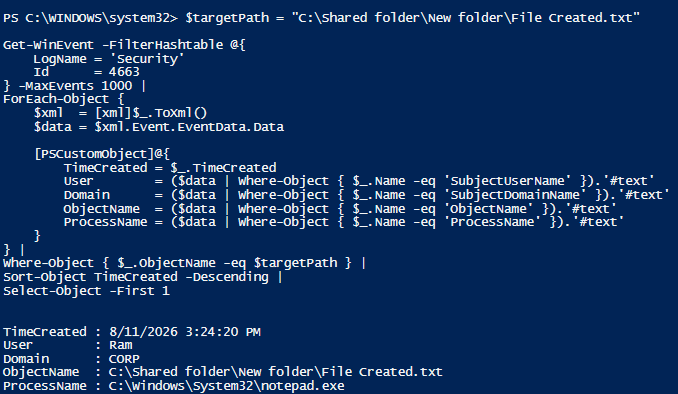
Get-WinEvent is a PowerShell cmdlet that is used to retrieve event logs recorded. With the help of the "-FilterHashtable" parameter added to the cmdlet, event logs shall be filtered based on their properties such as Id, Log Name, Time created etc.
Below is a sample PowerShell command that retrieves the latest occurrence of EventID 4663 i.e, the latest modification performed to file/folder. The output provides the timestamp, username, domain, exact file/folder path, and the process used for modification.
$targetPath = "C:\Your\Target\Path"
Get-WinEvent -FilterHashtable @{
    LogName   = 'Security'
    Id        = 4663
} -MaxEvents 1000 |
ForEach-Object {
    $xml = [xml]$_.ToXml()
    $data = $xml.Event.EventData.Data
    [PSCustomObject]@{
        TimeModified = $_.TimeCreated
        User        = ($data | Where-Object { $_.Name -eq 'SubjectUserName' }).'#text'
        Domain      = ($data | Where-Object { $_.Name -eq 'SubjectDomainName' }).'#text'
        ObjectName  = ($data | Where-Object { $_.Name -eq 'ObjectName' }).'#text'
        ProcessName = ($data | Where-Object { $_.Name -eq 'ProcessName' }).'#text'
    }
} |
Where-Object { $_.ObjectName -eq $targetPath } |
Sort-Object TimeModified -Descending |
Select-Object -First 1
Limitations of using native AD auditing or powershell commands
- Imminent risk of older logs getting overwritten after a period of time due to limited security size log.
- High alert noise since for every object access, Event ID 4663 is triggered.
- The auditing entries (SACL) must be added for every file/folder.
- Complexity of powershell queries increases when multiple files/folders are involved.
- Powershell commands have to be executed in the server where file/folder is present.
3. How to track who last modified a file/folder using ADAudit Plus
An auditing solution like ADAudit Plus offers built-in reports to track changes made to file/folders not from one server but from all the Windows servers configured. In ADAudit Plus, you'll find dedicated reports to track all file activities such as creation, deletion, modified etc. Each report provides information on:
- Who made the change
- What was the change
- When did the change
Follow the below steps to track who last modified a file in ADAudit Plus:
- Open ADAudit Plus.
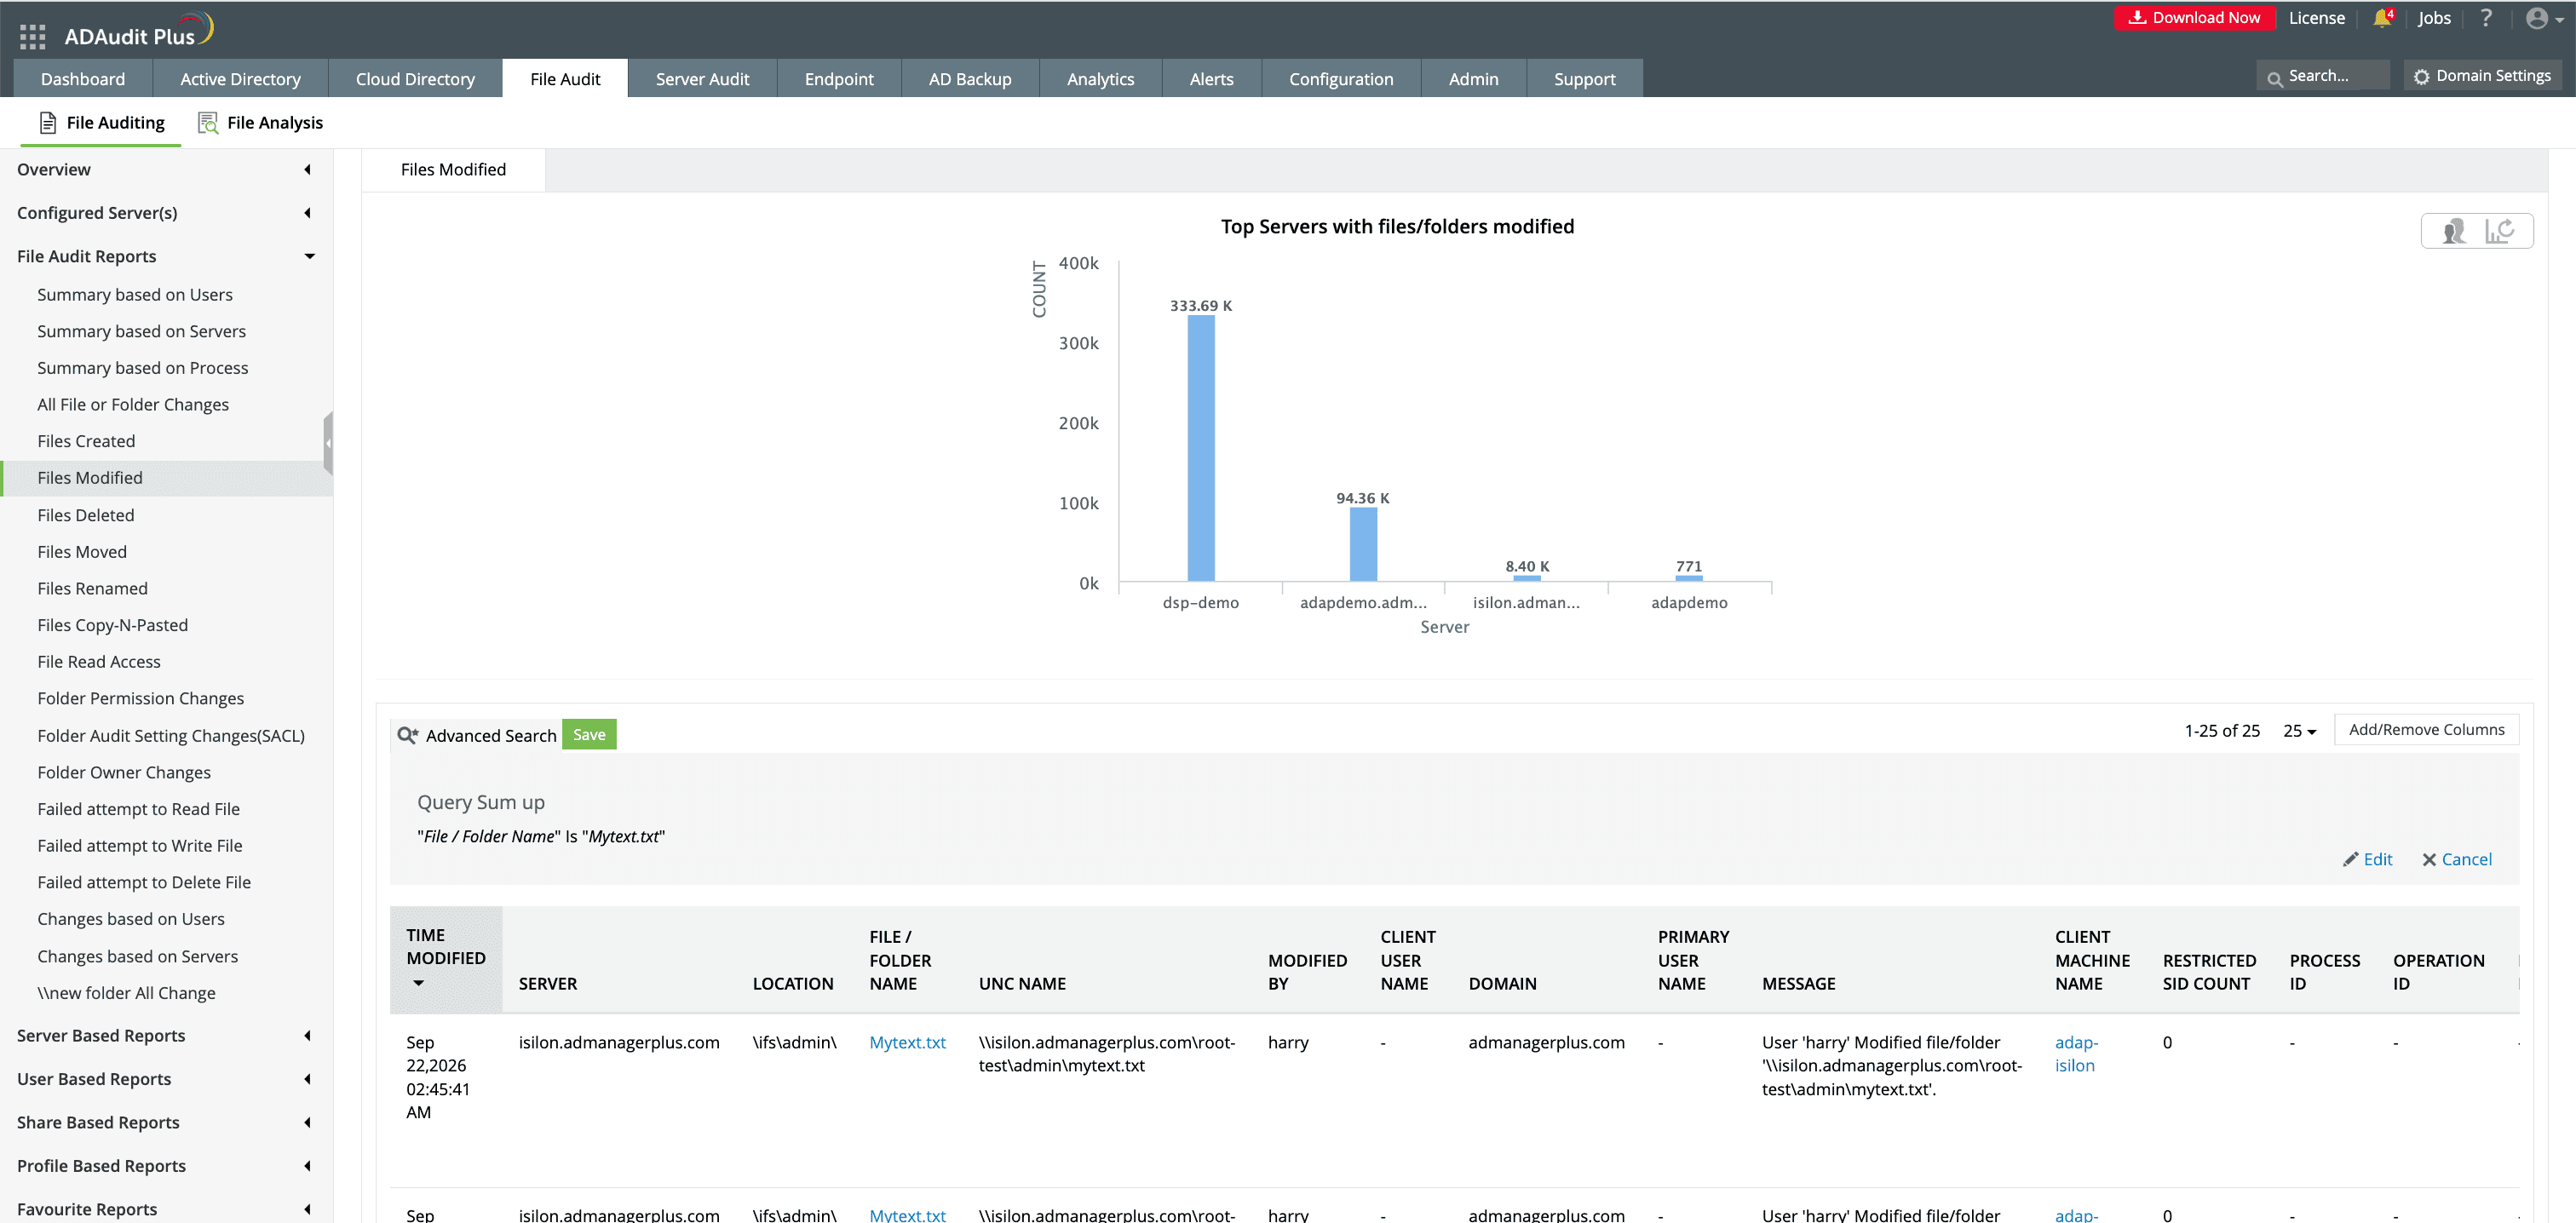
- Navigate to File Audit > File Audit reports> Files Modified.
- Click on Advanced Search, select the filter options "File/Folder name", "Is" and enter the name of the file/folder.
- Click on Search to apply filter.
- Using the column "Modified By" in the report, identify the list of users who have modified the specified file.
A one-stop solution for all your IT auditing, compliance, and security needs
ADAudit Plus provides capabilities like file change auditing, shared folder monitoring, compliance reporting, attack surface analysis, response automation, and more for diverse IT systems.
FAQ and Troubleshooting
You can track the file movement with EventID 4663. Two events are created when a file/folder is moved between two folders. One with Access for Delete with source folder as ObjectName and the other with Accesses as WriteData with ObjectName as the folder to which it is moved to.
Double-click the Event ID 4663 in EventViewer to view its details. You can identify the user account and the domain they belong to using the Account Name and Domain fields.
Experience
ADAudit Plus for free
With ADAudit Plus, you can:
- Get full visibility into file changes
- Audit multi-vendor NAS file servers
- Detect anomalous file activities
- Generate file audit trails
- And much more