Agentic AI security and governance
Close the agent governance loop with SecureAI. One platform for agent discovery, governance, gateway enforcement, and AI security posture management.
ManageEngine is trusted by

An AI agent with access is an identity.
Secure and govern it like one.
Adopt agentic AI with the controls you already run and close the security gaps. SecureAI discovers your agents, assigns an owner for each one, certifies what they can reach, and enforces those decisions at the gateway.
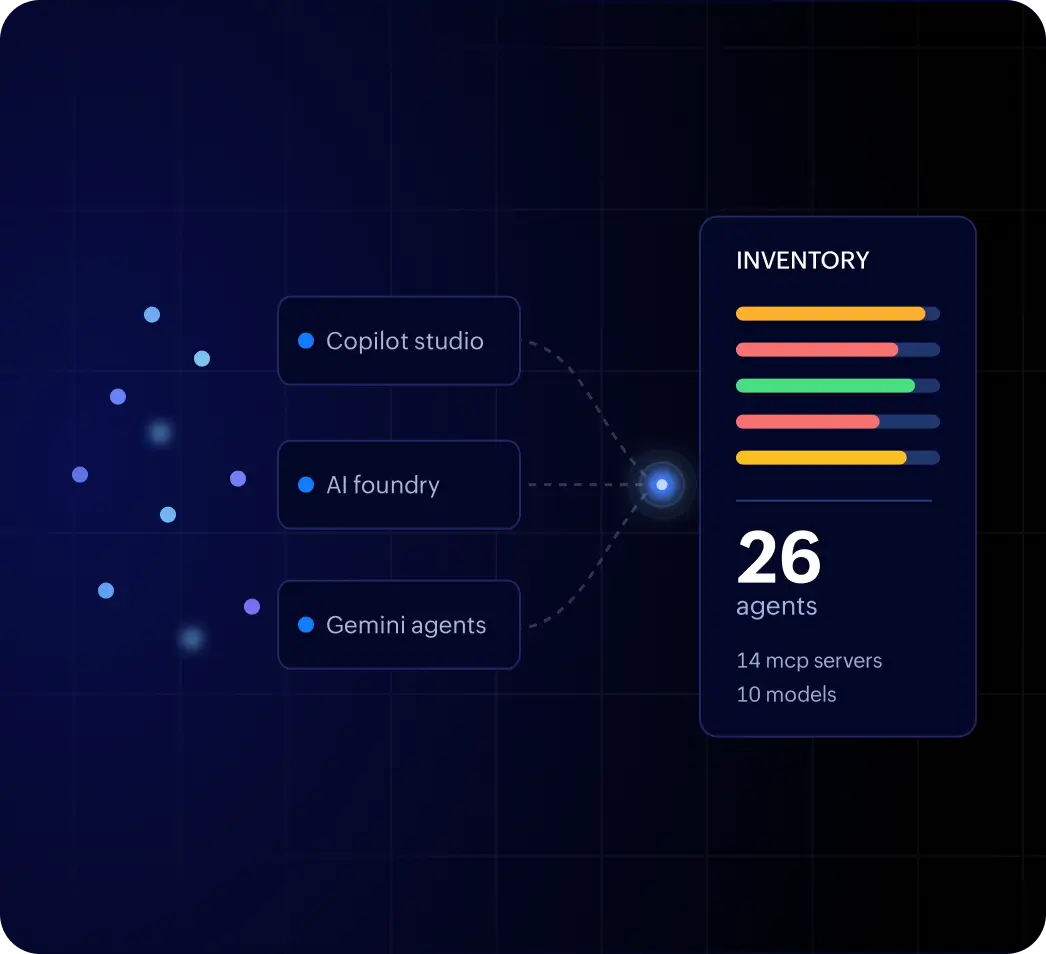
Know where your agents are
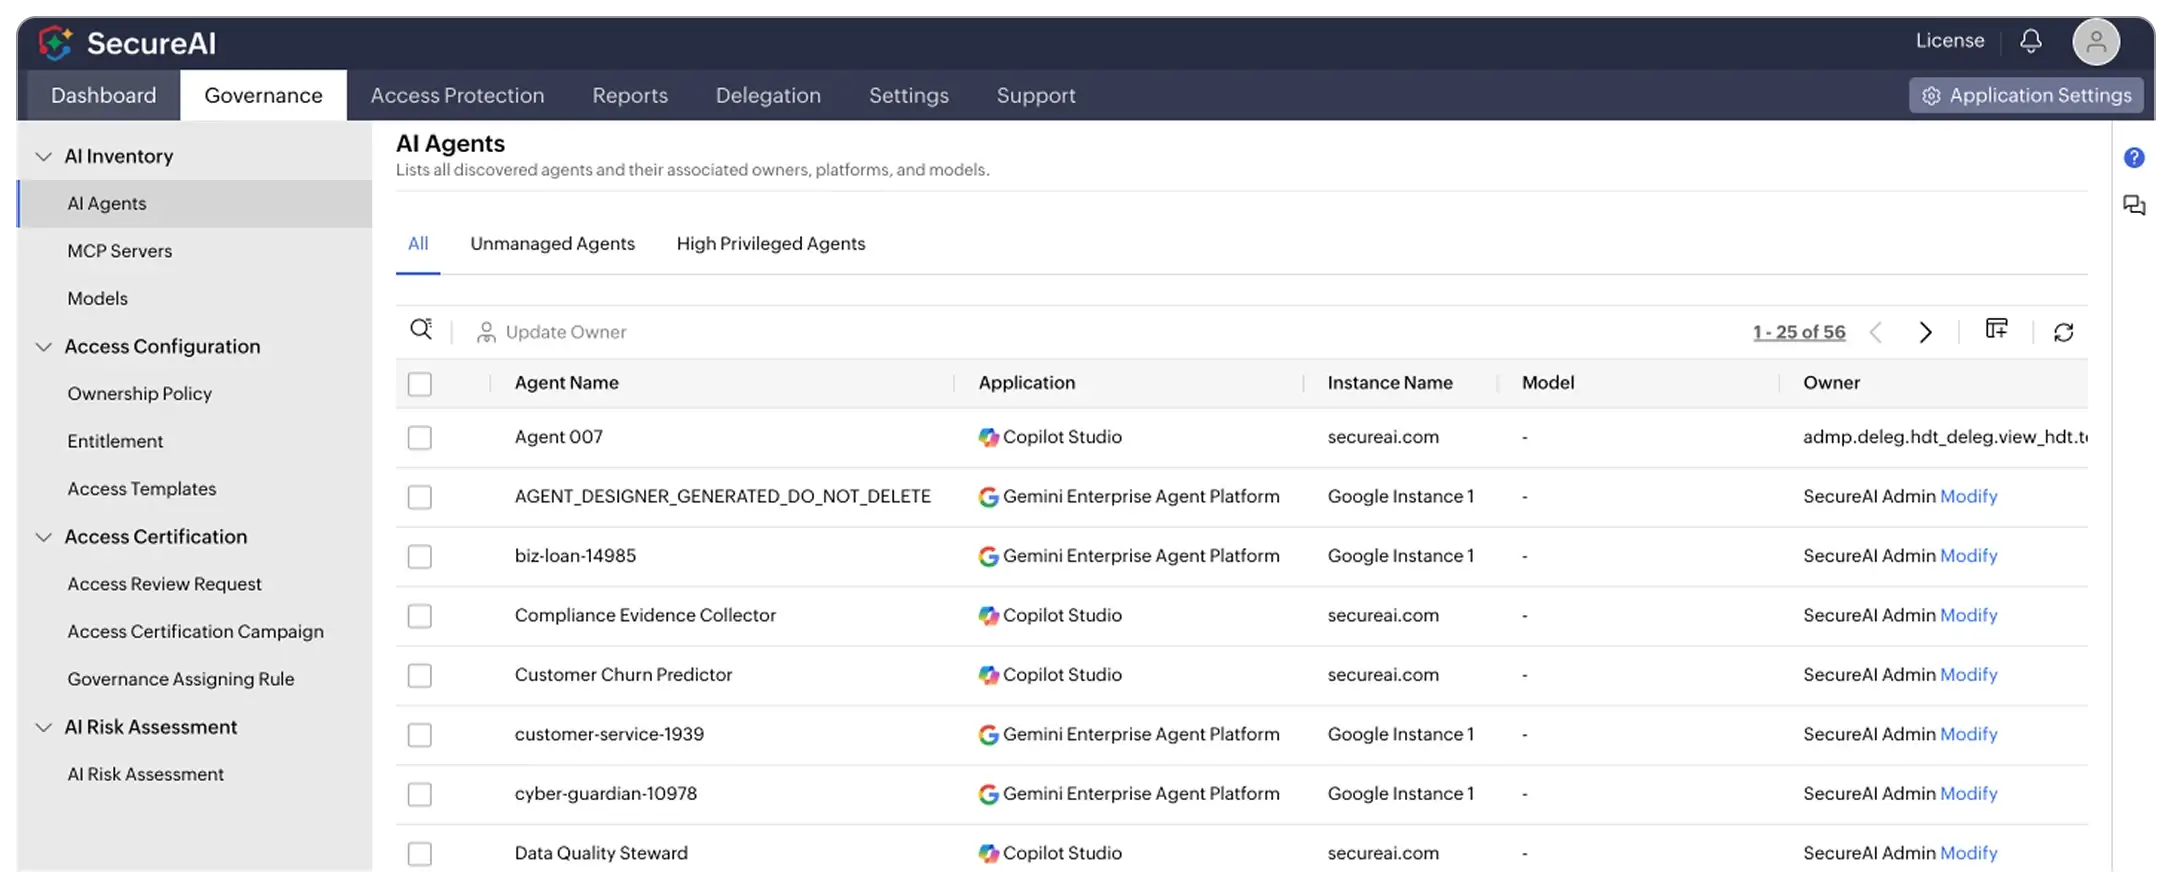
One inventory that covers every connected platform, so you don’t have to estimate how many agents are running or guess who owns them.
- Agents from Copilot Studio, Foundry, Zia and Gemini Enterprise Agent Platform in one list.
- MCP servers and models are discovered alongside the agents calling them.
- Unmanaged and high privileged agents are discovered and categorized.
Review what they can access
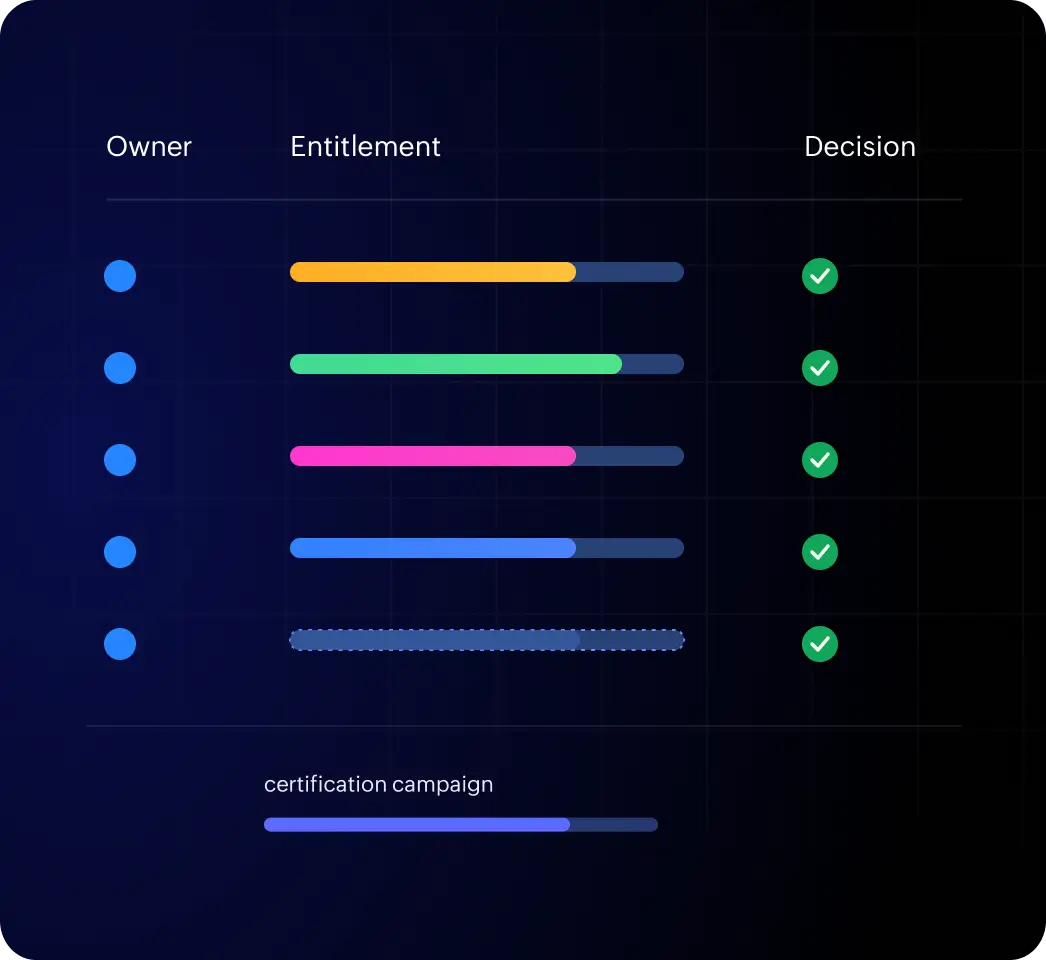
Entitlements, ownership, and access certification applied to agents the same way human access has had for years.
- Ownership policies assign an accountable owner for each agent as they become discovered.
- Entitlements are consolidated from connected directories and applications.
- Certification campaigns to certify or revoke agent access on a schedule.
Define what they can do
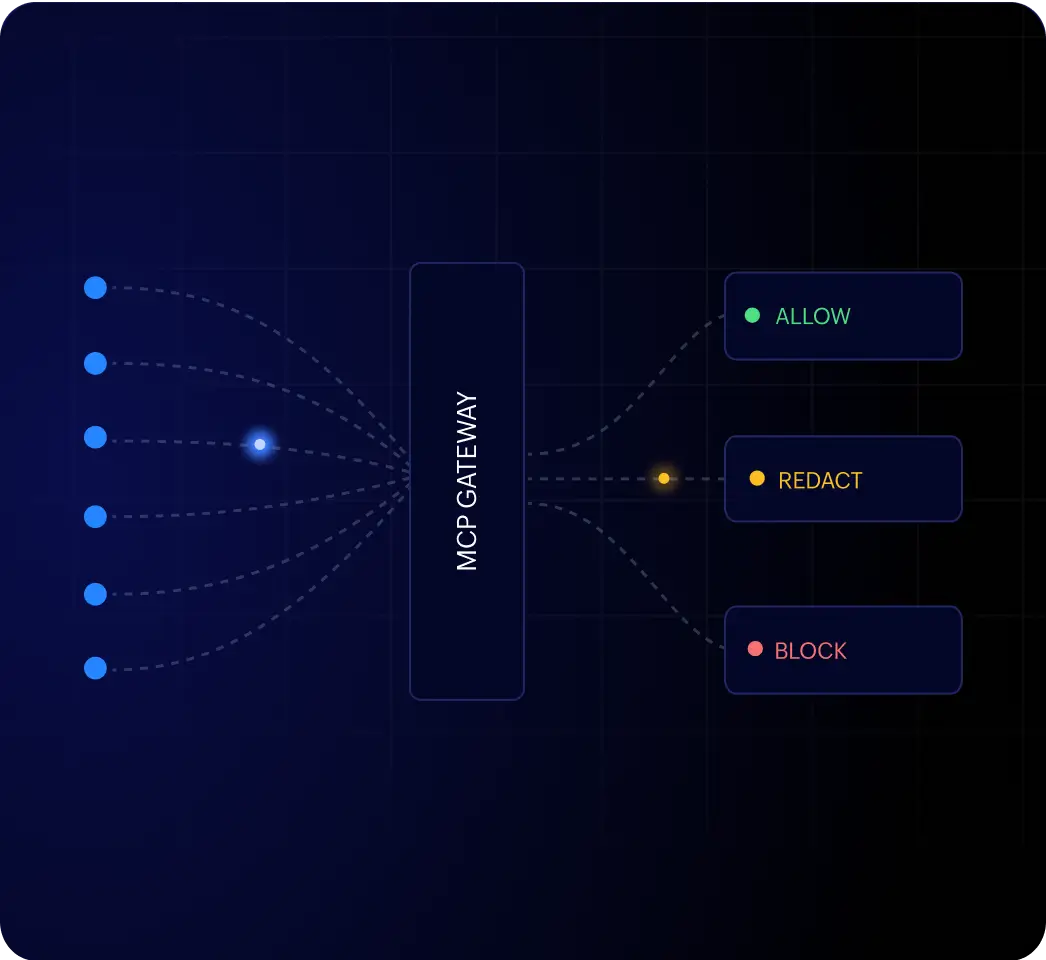
Allow, redact, or block MCP calls with access and data loss prevention (DLP) policies at the SecureAI gateway.
- Policies are scoped by identity, time, IP address, location, and MCP servers.
- DLP inspection occurs on tool input and output, with configurable redaction text.
- Three verdicts at the gateway to allow and audit, redact and allow, or block.
Prove what they did
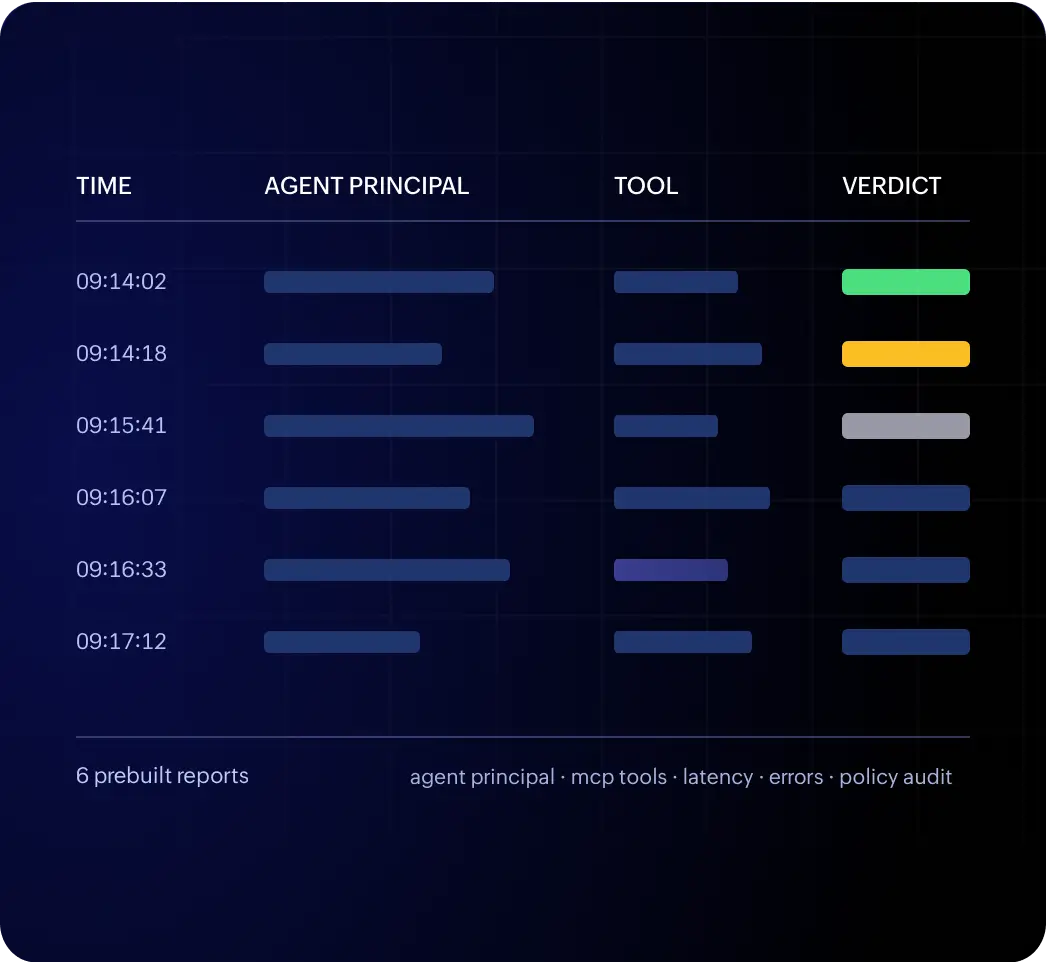
See who owns which agents, what each agent is entitled to, every MCP call, and much more.
- Gateway activity with the policy decision is recorded against each MCP call.
- Prebuilt reports for agent usage, MCP tool usage, errors, latency, and inactive servers.
- Ownership and entitlement records that sit behind the gateway log.
Everything an agent
can reach in one view
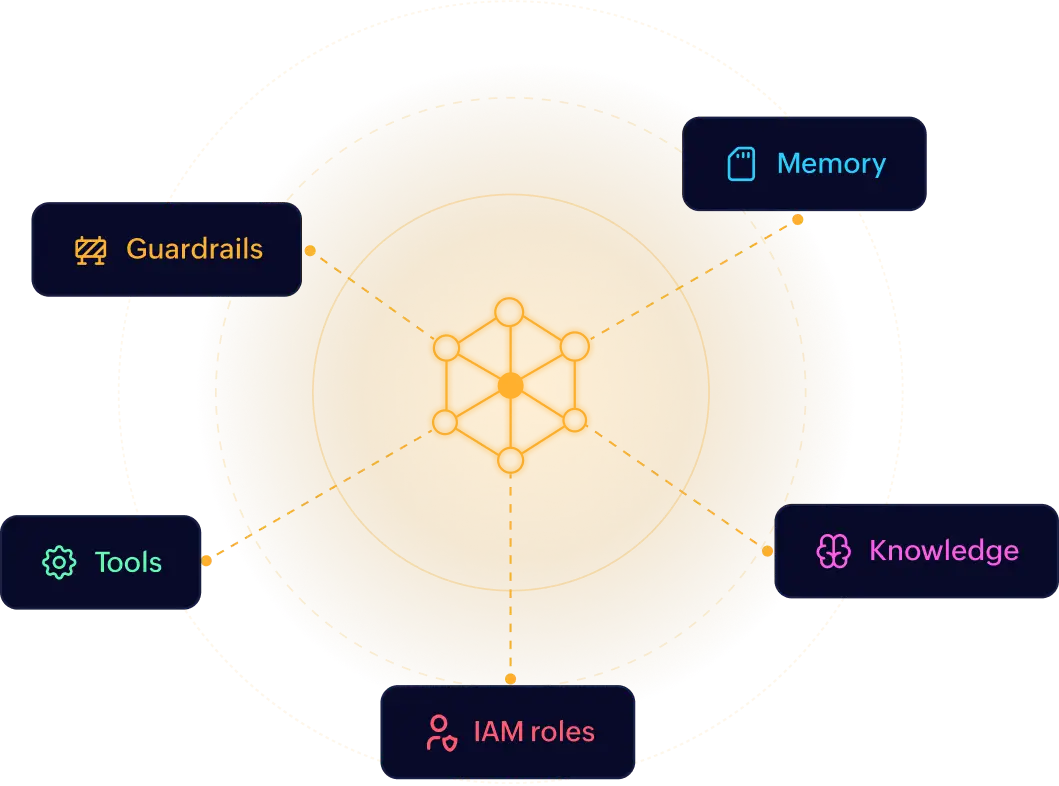
See an agent's access end to end—from memory to MCP servers—and understand the full picture before deciding what it keeps during access certification.
- Maps unowned agents to the resources agents can reach
- Traces access from the role to the resource(s) that role unlocks
- Gives reviewers the full access path before they approve or revoke
- Shows an owner exactly what they’re being made accountable for
A gateway that sits in front of every MCP server
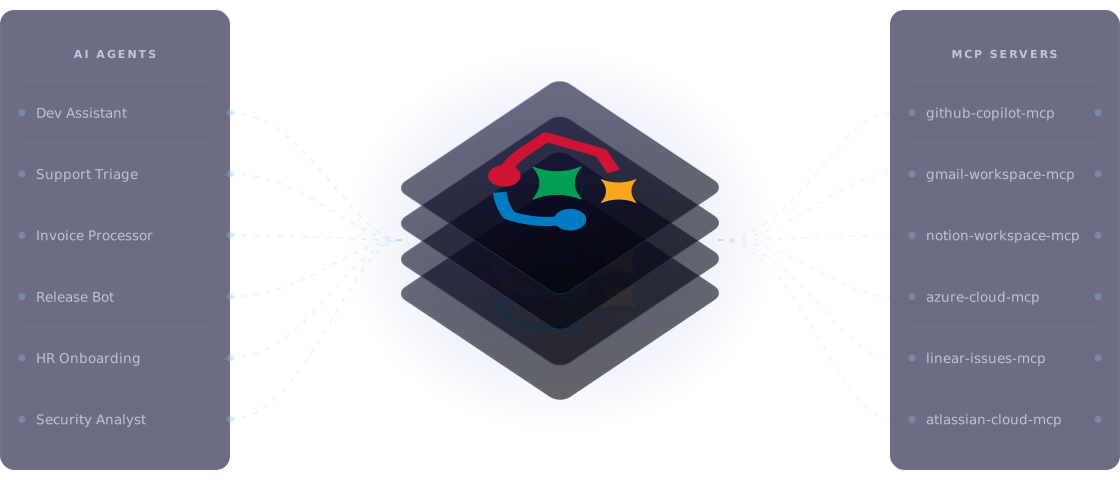
Governance decides what access agents should have, but SecureAI's MCP gateway makes sure that access is what they get. Check every MCP call against your policies, approve the calls that match them, redact the data you flagged, and block what falls outside.
Know where your AI vendors leave you exposed
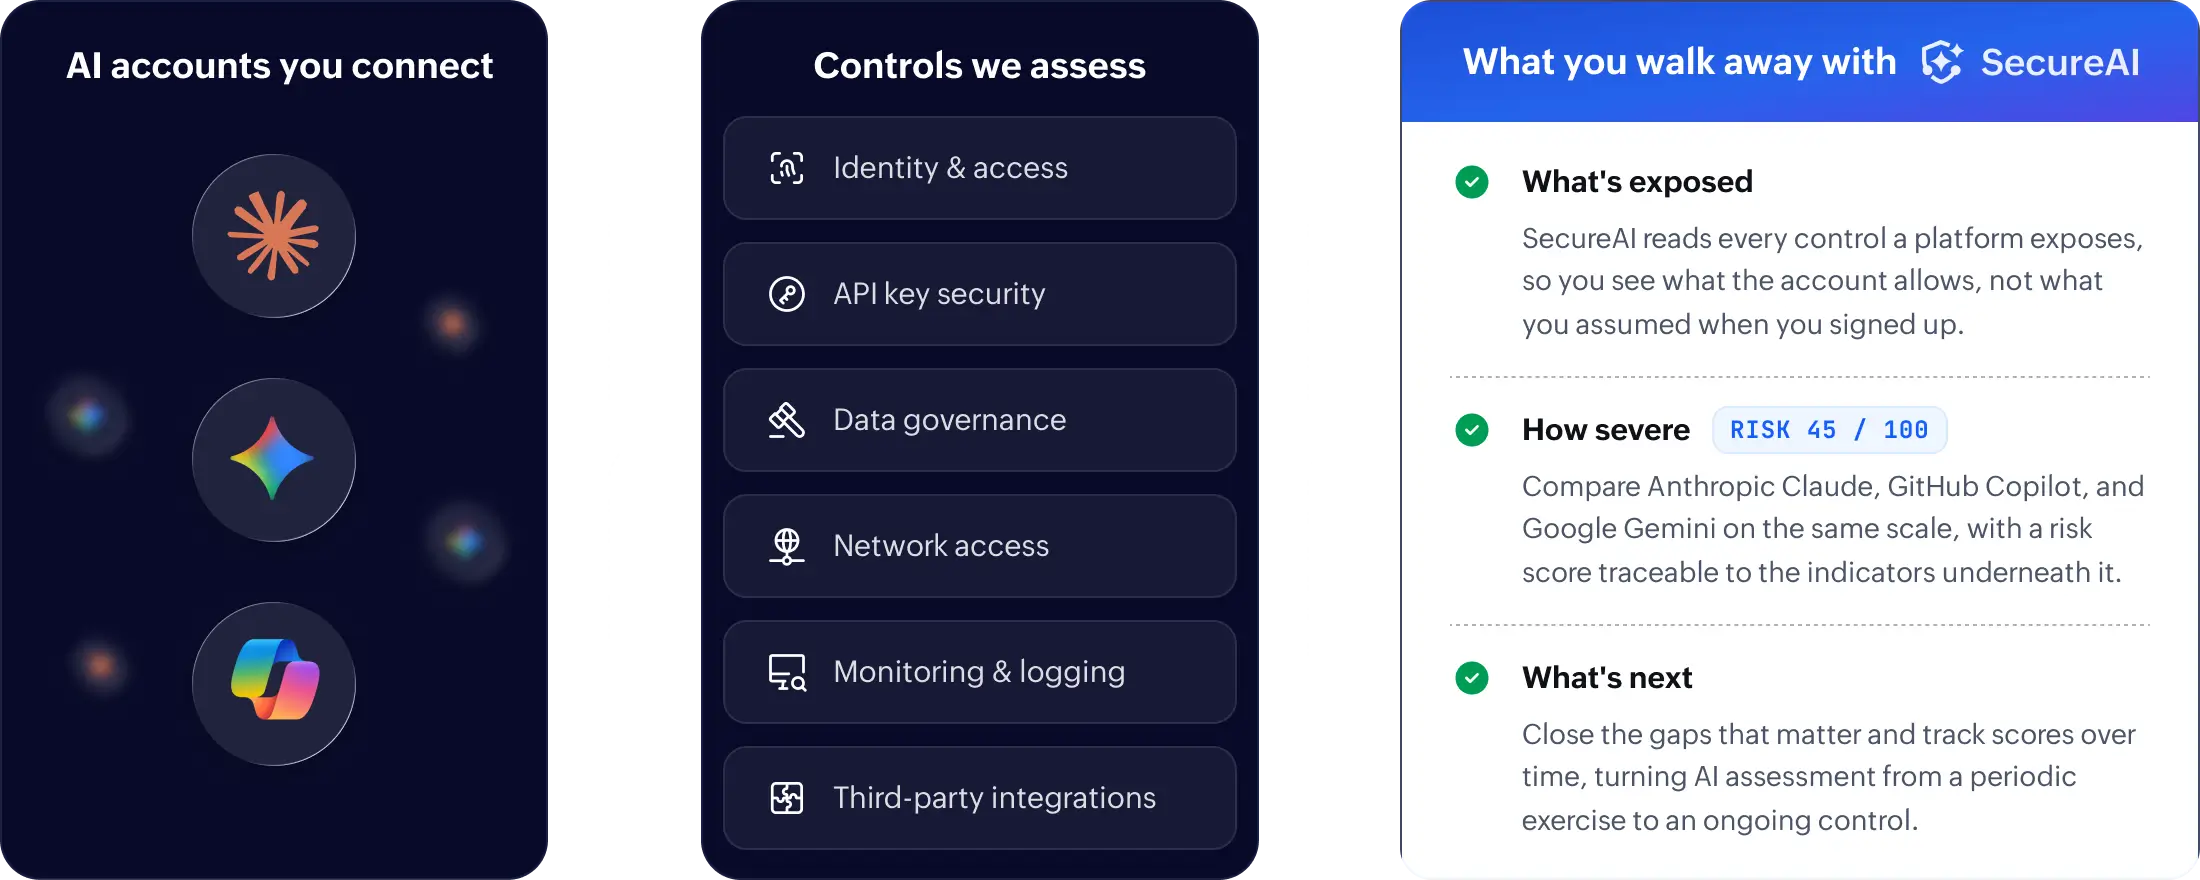
Assess every AI account against enterprise security controls and see where each one falls short. Get a risk score, track it over time, and give your auditors evidence instead of assurance.
Why SecureAI?
ManageEngine SecureAI, the agentic AI security and governance component of AD360, brings visibility, governance, and control to the AI agents your teams build and use, so you always know which agents exist, who is responsible for them, and what they can access.
Full agent lifecycle management in a single platform
Discovery, governance, gateway enforcement, and audit for AI agents, from creation through decommissioning.
Identity governance and administration (IGA)-native governance
Access certification, entitlement bundles, and ownership assignment applied to AI agent identities, using the same principles enterprise IGA programs already run for identities.
Framework-anchored
Controls mapped to OWASP, MITRE ATLAS, EU AI Act, NIST AI RMF, and AI TRiSM.
Built by ManageEngine
Two decades of enterprise IT management experience, applied to agentic AI.
FAQs
Agentic AI security governs autonomous AI agents that hold credentials, make decisions, and act on enterprise systems independently. Traditional IAM, CASB, and DLP tools were not designed for non-human identities.
Agentic AI governance extends identity governance and administration to AI agents. It covers ownership assignment for every agent, entitlements review, access certification campaigns, framework-aligned policies, and delegation across the agent lifecycle.
Traditional IAM governs human identities and static service accounts, while DLP inspects content flows on defined channels. SecureAI treats each AI agent as a governed identity with an owner, entitlements, and an audit trail.
Every new MCP server adds another endpoint, credential set, and policy surface, and agents connect to each one directly. An MCP gateway consolidates that surface into a single URL where identity, tool access, data inspection, and audit apply uniformly across every MCP server behind it.
An AI agent identity is the identity assigned to an autonomous AI agent so it can be governed inside enterprise systems, separate from the human user who created it. It has an owner, an entitlement set, and credentials or a service account, plus a defined lifecycle from provisioning through revocation.