Vulnerability Remediation
Remediating vulnerabilities by deploying patches is a crucial part of maintaining a secure infrastructure. Using the patch management feature of Endpoint Central MSP, you can remediate vulnerabilities manually or through automated patch deployment.
Overview
Patches are released by vendors to fix security flaws, bugs, or performance issues in software and systems. Neglecting to address vulnerabilities can expose an organization to significant risks. When vulnerabilities are left unpatched, attackers can exploit them to gain unauthorized access to critical systems, leading to data breaches, theft, or corruption. Hence, vulnerability remediation is essential for ensuring a secure and resilient infrastructure.
Remediating Vulnerabilities without a Deployable Patch
When a vulnerability does not have a patch that can be deployed directly from the console:
- Navigate to Threats & Patches → Threats → Vulnerabilities and select the vulnerability.
- Review its Patch Availability and the instructions under Remediation.
- If Patch Availability is Manual Fix Required, follow the displayed remediation instructions. If they identify an applicable vendor update, such as a Windows cumulative update, deploy that update to the affected systems.
- If Patch Availability is Not Available and the remediation information states that a fix is expected in an upcoming update, wait until the vendor releases the official fix.
- If the latest available software version is still affected and the vendor has not released a fixed version, installing that latest version will not clear the vulnerability. Follow any vendor-provided workaround shown under Remediation. If no workaround is available, contact the software vendor or the relevant product support team.
- After applying the specified fix, run a vulnerability scan on the affected systems. The vulnerability is cleared when the scan confirms that the installed version is no longer affected.
Vulnerability Remediation through Manual Deployment of Patches
To find the patches associated with a specific CVE, navigate to Threats & Patches → Patches → Supported Patches and apply the CVE ID filter. If the filter returns no results, no supported patch is currently mapped to that CVE. Open the vulnerability and review its Remediation information for the available resolution.
To identify the updates for a specific CVE that are currently pending on your managed endpoints, navigate to Threats & Patches → Patches → Missing Patches and apply the CVE ID filter. The filtered view lists the CVE-related updates that are missing from your managed systems.
To remediate vulnerabilities through manual deployment of patches:
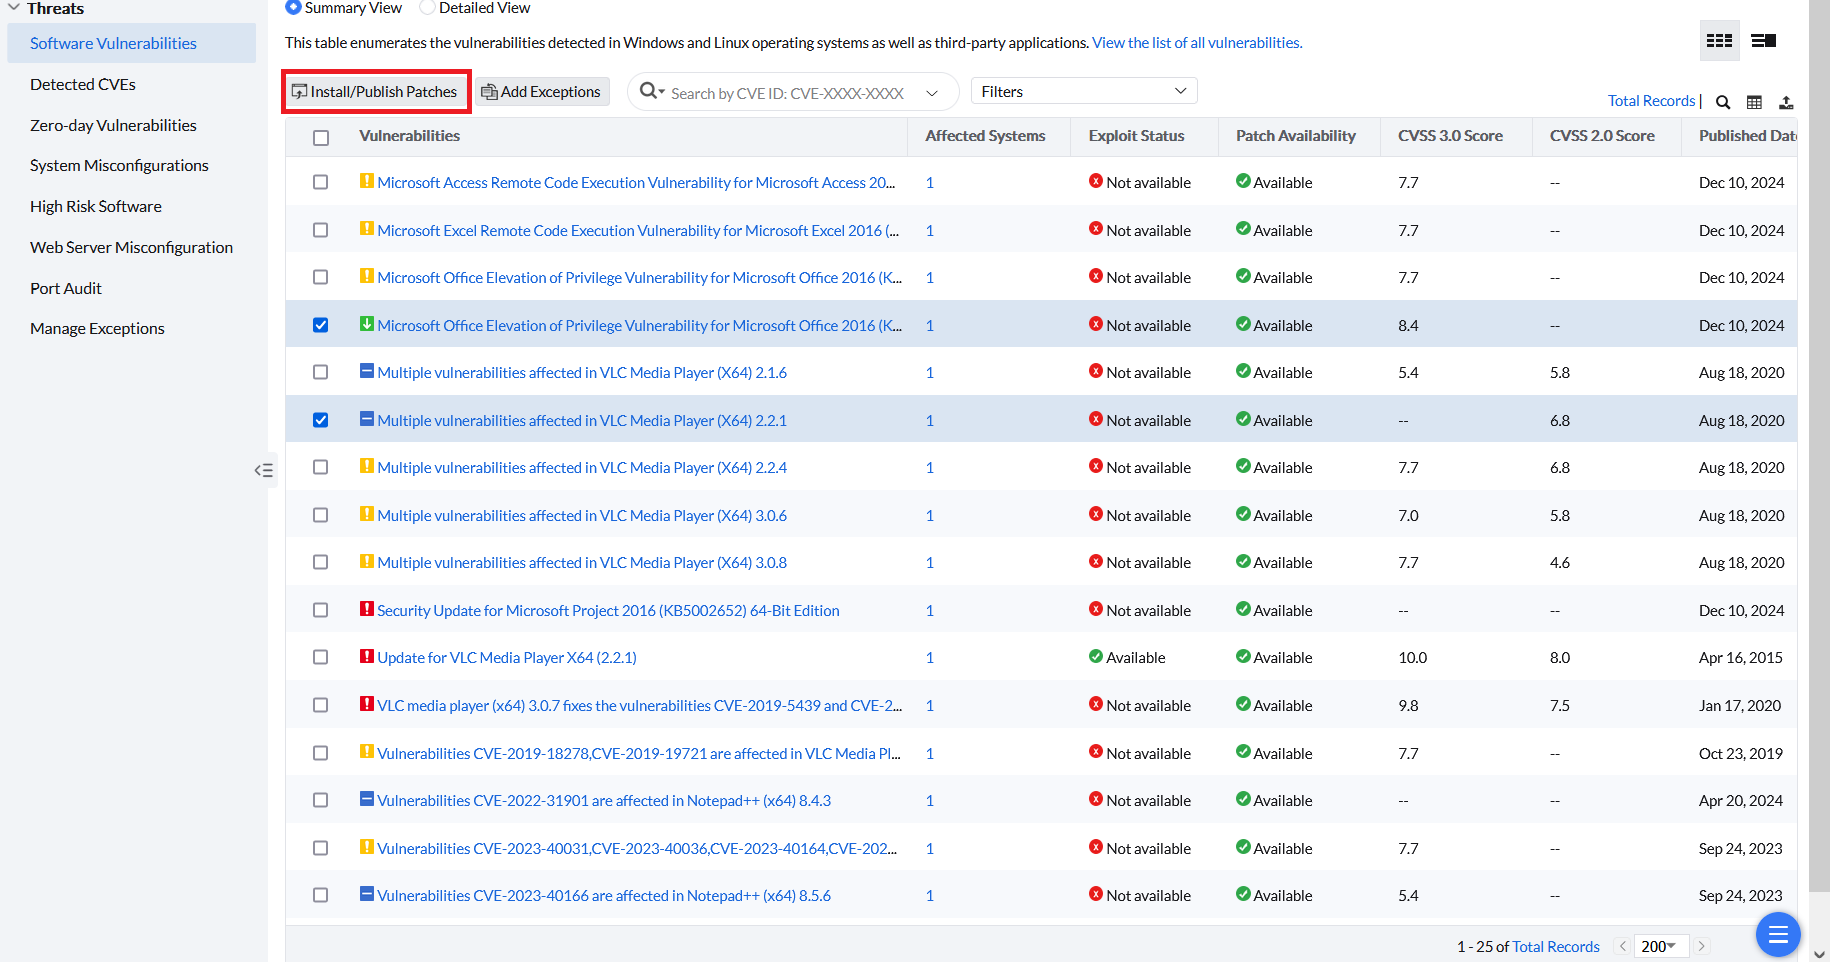
- From the Software Vulnerabilities or Zero-day Vulnerabilities section, select the required vulnerabilities for which a patch is available and click Install/Publish Patches.
- From the Detected CVEs section, select the required vulnerabilities and click Fix CVEs.
When a vulnerability affects multiple operating systems, deploy the applicable patches separately for each platform:
- Open Software Vulnerabilities and select the required vulnerability.
- Click the affected system count.
- Apply the Windows platform filter, select the applicable entries, and click Install Patch.
- Repeat the platform filtering and deployment separately for macOS and Linux, where applicable.
- Verify that every selected patch installs successfully.
You will be redirected to the Install/Uninstall Patch window, where the required missing patches to address the selected vulnerabilities will be listed. Configure the manual deployment settings to install these patches. To learn more about configuring manual deployment settings, refer to this page.
Automated Vulnerability Remediation
As enterprises grow and their IT environments become more complex, manually applying patches across many servers, workstations, and devices becomes increasingly difficult. Automated patch deployment allows you to scale patching efforts, applying updates to thousands of devices simultaneously.
Once you configure automated patch deployment, if the required patch is available and is approved, vulnerability remediation automatically occurs without requiring additional manual intervention — these approved patches will be deployed to the chosen targets automatically.
To learn more about configuring automated patch deployment tasks, refer to this page.