Native SOAR in Log360 — full release walkthrough
The visual playbook builder, parallel execution, and custom Python functions in action, with product team Q&A.
The latest releases across every stage of the threat lifecycle, plus a new AI layer that runs across all of them. Read the release notes.
Q3 2026 · Log360 Cloud
Log360 Cloud expands its AI capabilities with alert investigation, a conversational assistant, AI agents, and MCP support. Zia helps analysts move from raw security data to actionable insight, so they can spend less time searching and piecing together information and more time responding to threats.
Capabilities
The Zia Alert Investigation Agent turns a selected alert into a structured investigation, helping analysts move from an initial alert to a clear picture of the attack in minutes instead of hours. It identifies and enriches entities, correlates related alerts and logs, reconstructs the attack chain, and presents the findings with suggested next steps.
Ask Zia lets analysts interact with Log360 Cloud using natural language questions about logs and alerts and get answers directly. Analysts can ask follow-up questions to explore the results further, summarize findings, and narrow down information based on their investigation needs.
Zia Agents brings prebuilt and custom AI agents into Log360 Cloud. Security teams can deploy prebuilt agents such as the User Activity Review Agent and Alert Correlation Agent, or build their own agents with no code. This helps teams delegate repetitive analysis or assessments to autonomous AI agents.
Log360 Cloud now supports the Model Context Protocol (MCP) through the Zoho MCP Server. Analysts can query Log360 data, investigate alerts, manage configurations, create incidents, and take other actions from Claude, Copilot, Cursor, or any MCP-compatible AI client.
Q2 2026 · Log360 Cloud
Automate incident response using visual playbooks, custom functions, parallel execution, reusable workflows, and marketplace integrations.
Capabilities
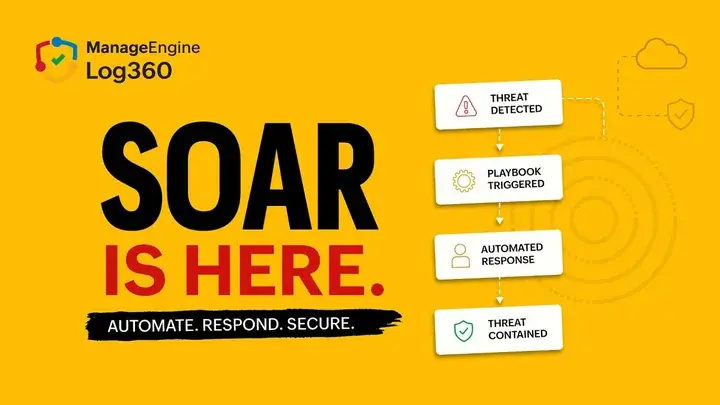
SOAR is now built directly into Log360 Cloud, enabling analysts to automate investigation and response workflows from a unified platform. Use the visual playbook builder to create low-code workflows with branching, parallel execution, custom functions, and coordinated remediation actions across security tools.
Run multiple playbooks in parallel from a single alert and reuse common workflows through nested playbooks. Retry and fallback mechanisms help maintain execution continuity, while manual retries resume from the exact point of failure instead of restarting the workflow.
Extend playbooks with custom logic using Python or Deluge functions. Build reusable workflows for threat enrichment, data parsing, ticket creation, endpoint actions, and organization-specific response logic.
Log360 Cloud adds 7 new marketplace extensions, including CrowdStrike Falcon, Bitdefender GravityZone and Okta with support for 300+ response actions across endpoint security, identity, cloud, and threat intelligence platforms.
Securely manage integrations and authentication from a centralized connections framework. Configure reusable connection profiles for endpoint platforms, identity providers, cloud services, and threat intelligence tools to simplify orchestration across your security stack.
Q3 2025 · Log360
Build precise detections and scale them with a centralised detection console, object-level alert scoping, clustered log ingestion, and cloud-delivered detection content.
Capabilities
We've redesigned how Log360 detects threats. Centralised detection console now brings together correlation logic, threat intelligence, MITRE ATT&CK mapping, UEBA insights, and a rule builder that supports standard, anomaly-based, and advanced detection logic. Detection Insights shows how noisy each rule is and how often it fires, so you can tune it for fewer, sharper alerts.
Fine-tune alert scope using filters based on users, groups, and OUs. These filters apply across predefined rules for use cases like privilege escalations, suspicious password resets, and admin group changes — helping reduce noise from irrelevant accounts like test users or developer machines. It's precise detection, not suppression.
Log360 now supports horizontal scalability with clustered log processors and role-based specialisation for alerting, correlation, and search. You can also collect logs from distributed sites and process them centrally — ensuring high performance even in large hybrid environments.
Get continuously updated detection content mapped to MITRE ATT&CK with no manual imports. Delivered securely from the cloud, this content is curated for emerging threats and multivector attacks, ensuring your detection logic stays current.
Q3 2025 · Log360 Cloud
Log360 Cloud now includes Zia Insights, which helps analysts understand alerts in context so they can investigate faster.
Capabilities
Generate human-readable summaries from alerts, incidents, and logs with one click so analysts start an investigation with context instead of raw events.
Map activities to MITRE ATT&CK® techniques for deeper threat context.
View attack timelines that reconstruct event sequences visually.
Get remediation tips tailored to the log type and context.
This release transforms threat investigation workflows, bringing clarity, speed, and actionable insight to threat investigation, right inside your SIEM.
Join the webinars
Walk through this quarter's release with the product team.
The visual playbook builder, parallel execution, and custom Python functions in action, with product team Q&A.
Related resources