Log360 Cloud is now live in the   UK Data Center with local data residency, lower latency, and EMEA-ready compliance.

Simplify Security
operations
with a scalable, cloud SIEM.

Gain unmatched visibility, detect threats and respond with native SOAR, and ensure compliance with confidence.

Over 280,000 organizations across 190 countries trust ManageEngine to manage their IT

Over 280,000 organizations across 190 countries trust ManageEngine to manage their IT

Recognized by

independent review platforms and analyst firms

  •  
     

    4.1/5

    Software advice

  •  
     

    4.1/5

    Capterra

  •  
     

    4.1/5

    G2

The benefits of using
Log360 Cloud as your cloud SIEM


Access and manage log data from anywhere


Rein in Shadow IT by tracking unsanctioned app usage


Collect logs from both on premises and cloud (AWS) environment.


Accelerate
security operations with
AI investigations, and
natural-language analysis.


Scale your network architecture without worrying about the log volume


Expedite case management with a rich library of out-of-the-box playbooks.


Audit security events and meet IT compliance requirements with ease


What is a cloud SIEM?

A cloud SIEM solution uses cloud technology to collect, analyze, and correlate security data from various sources within an organisation’s IT infrastructure. It provides real-time threat detection, incident response, and compliance management capabilities, all from the cloud. It uses cloud-native architecture for greater flexibility and ease of access when managing cybersecurity. It reduces the complexity of deploying a SIEM solution on-premises.

Learn more about cloud SIEM 
Collect logs
 

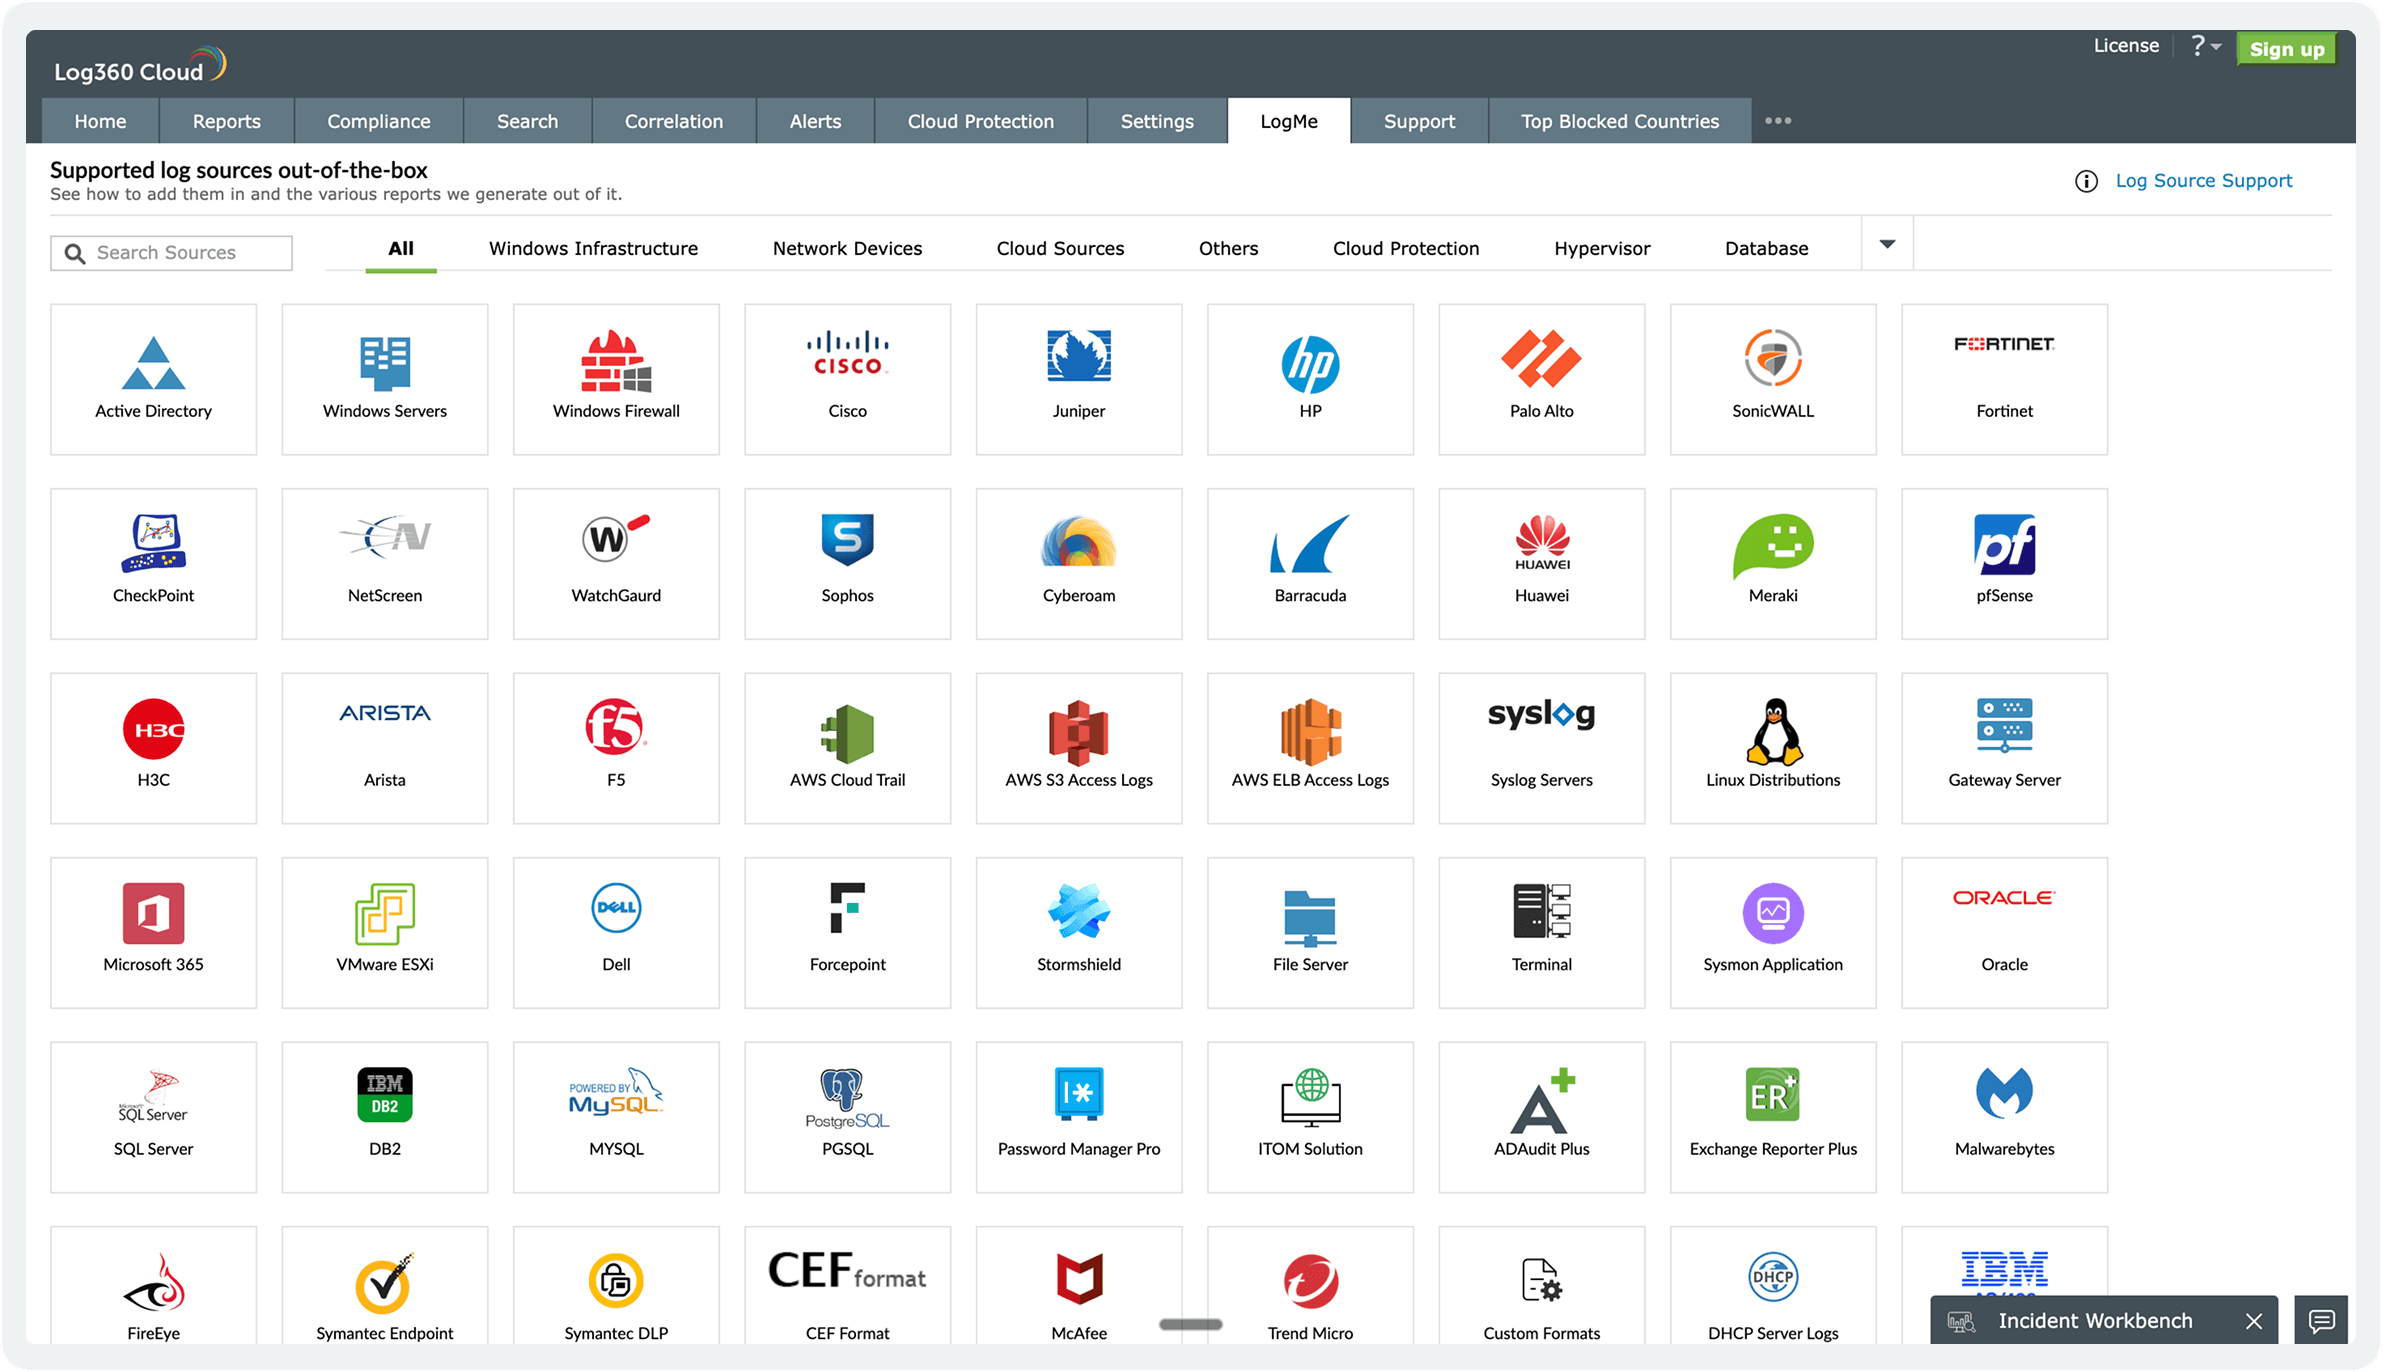
Collect logs

Ingest log data from various sources, including Windows and Linux servers, endpoints, databases, business apps, cloud environment, and more.
Audit reports
 

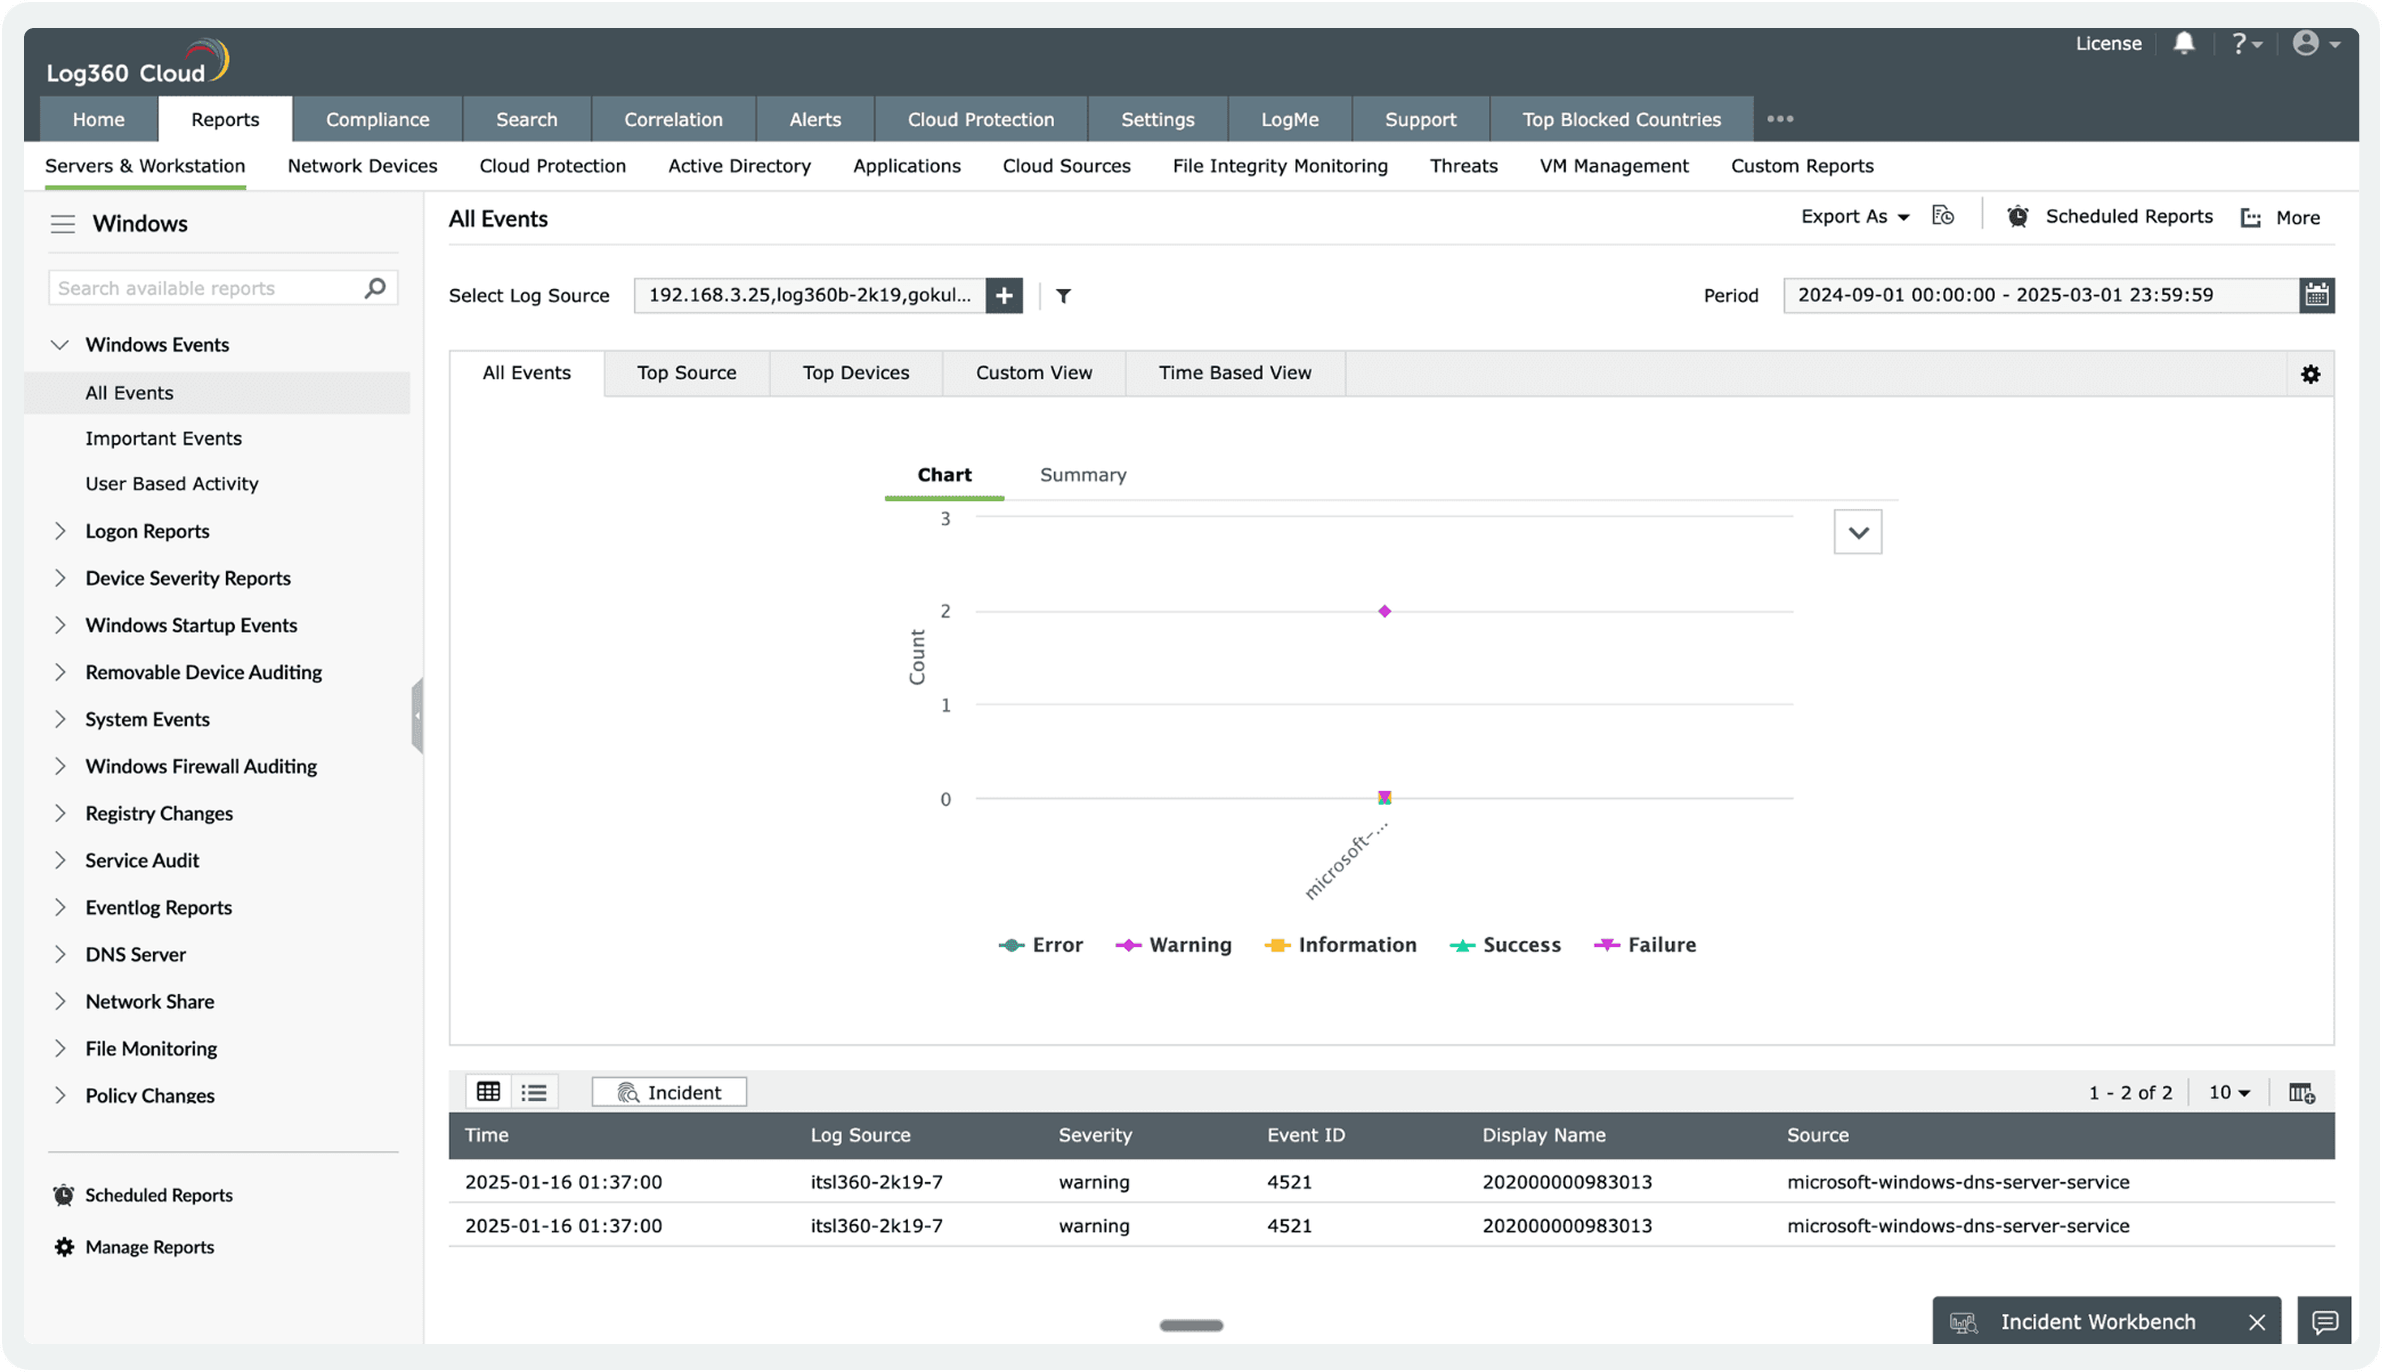
Audit reports

Investigate critical security incidents thoroughly by examining who performed actions, their location, and the timestamps, all facilitated by predefined security audit reports
Detect threats
 

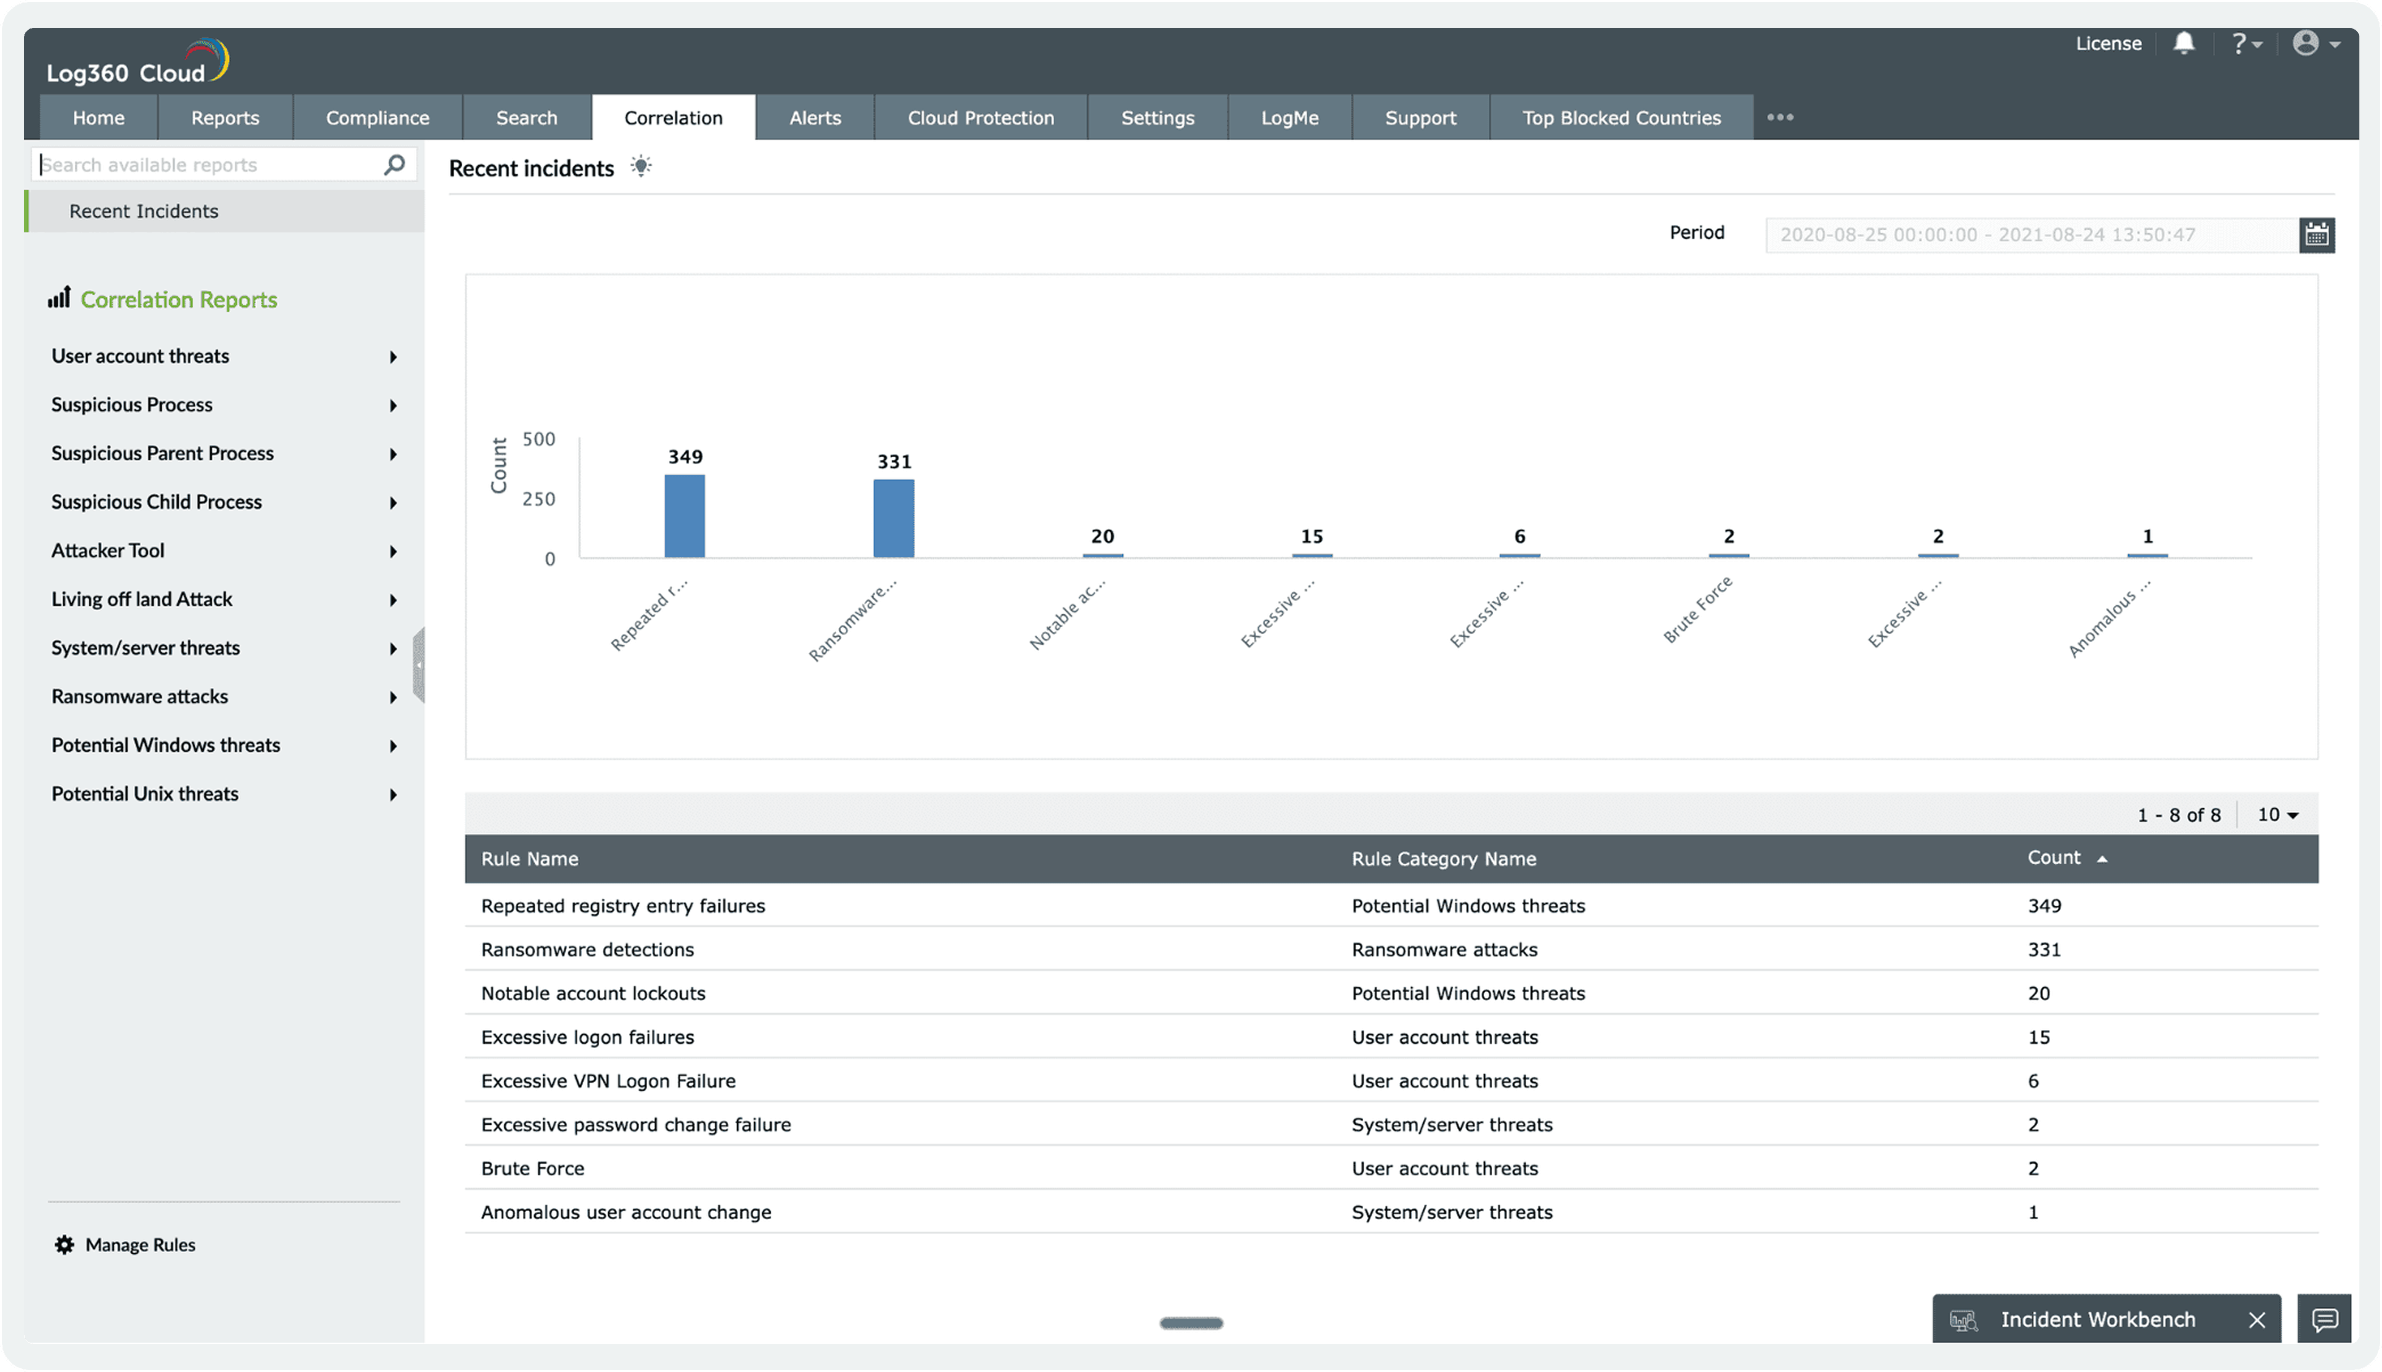
Detect threats

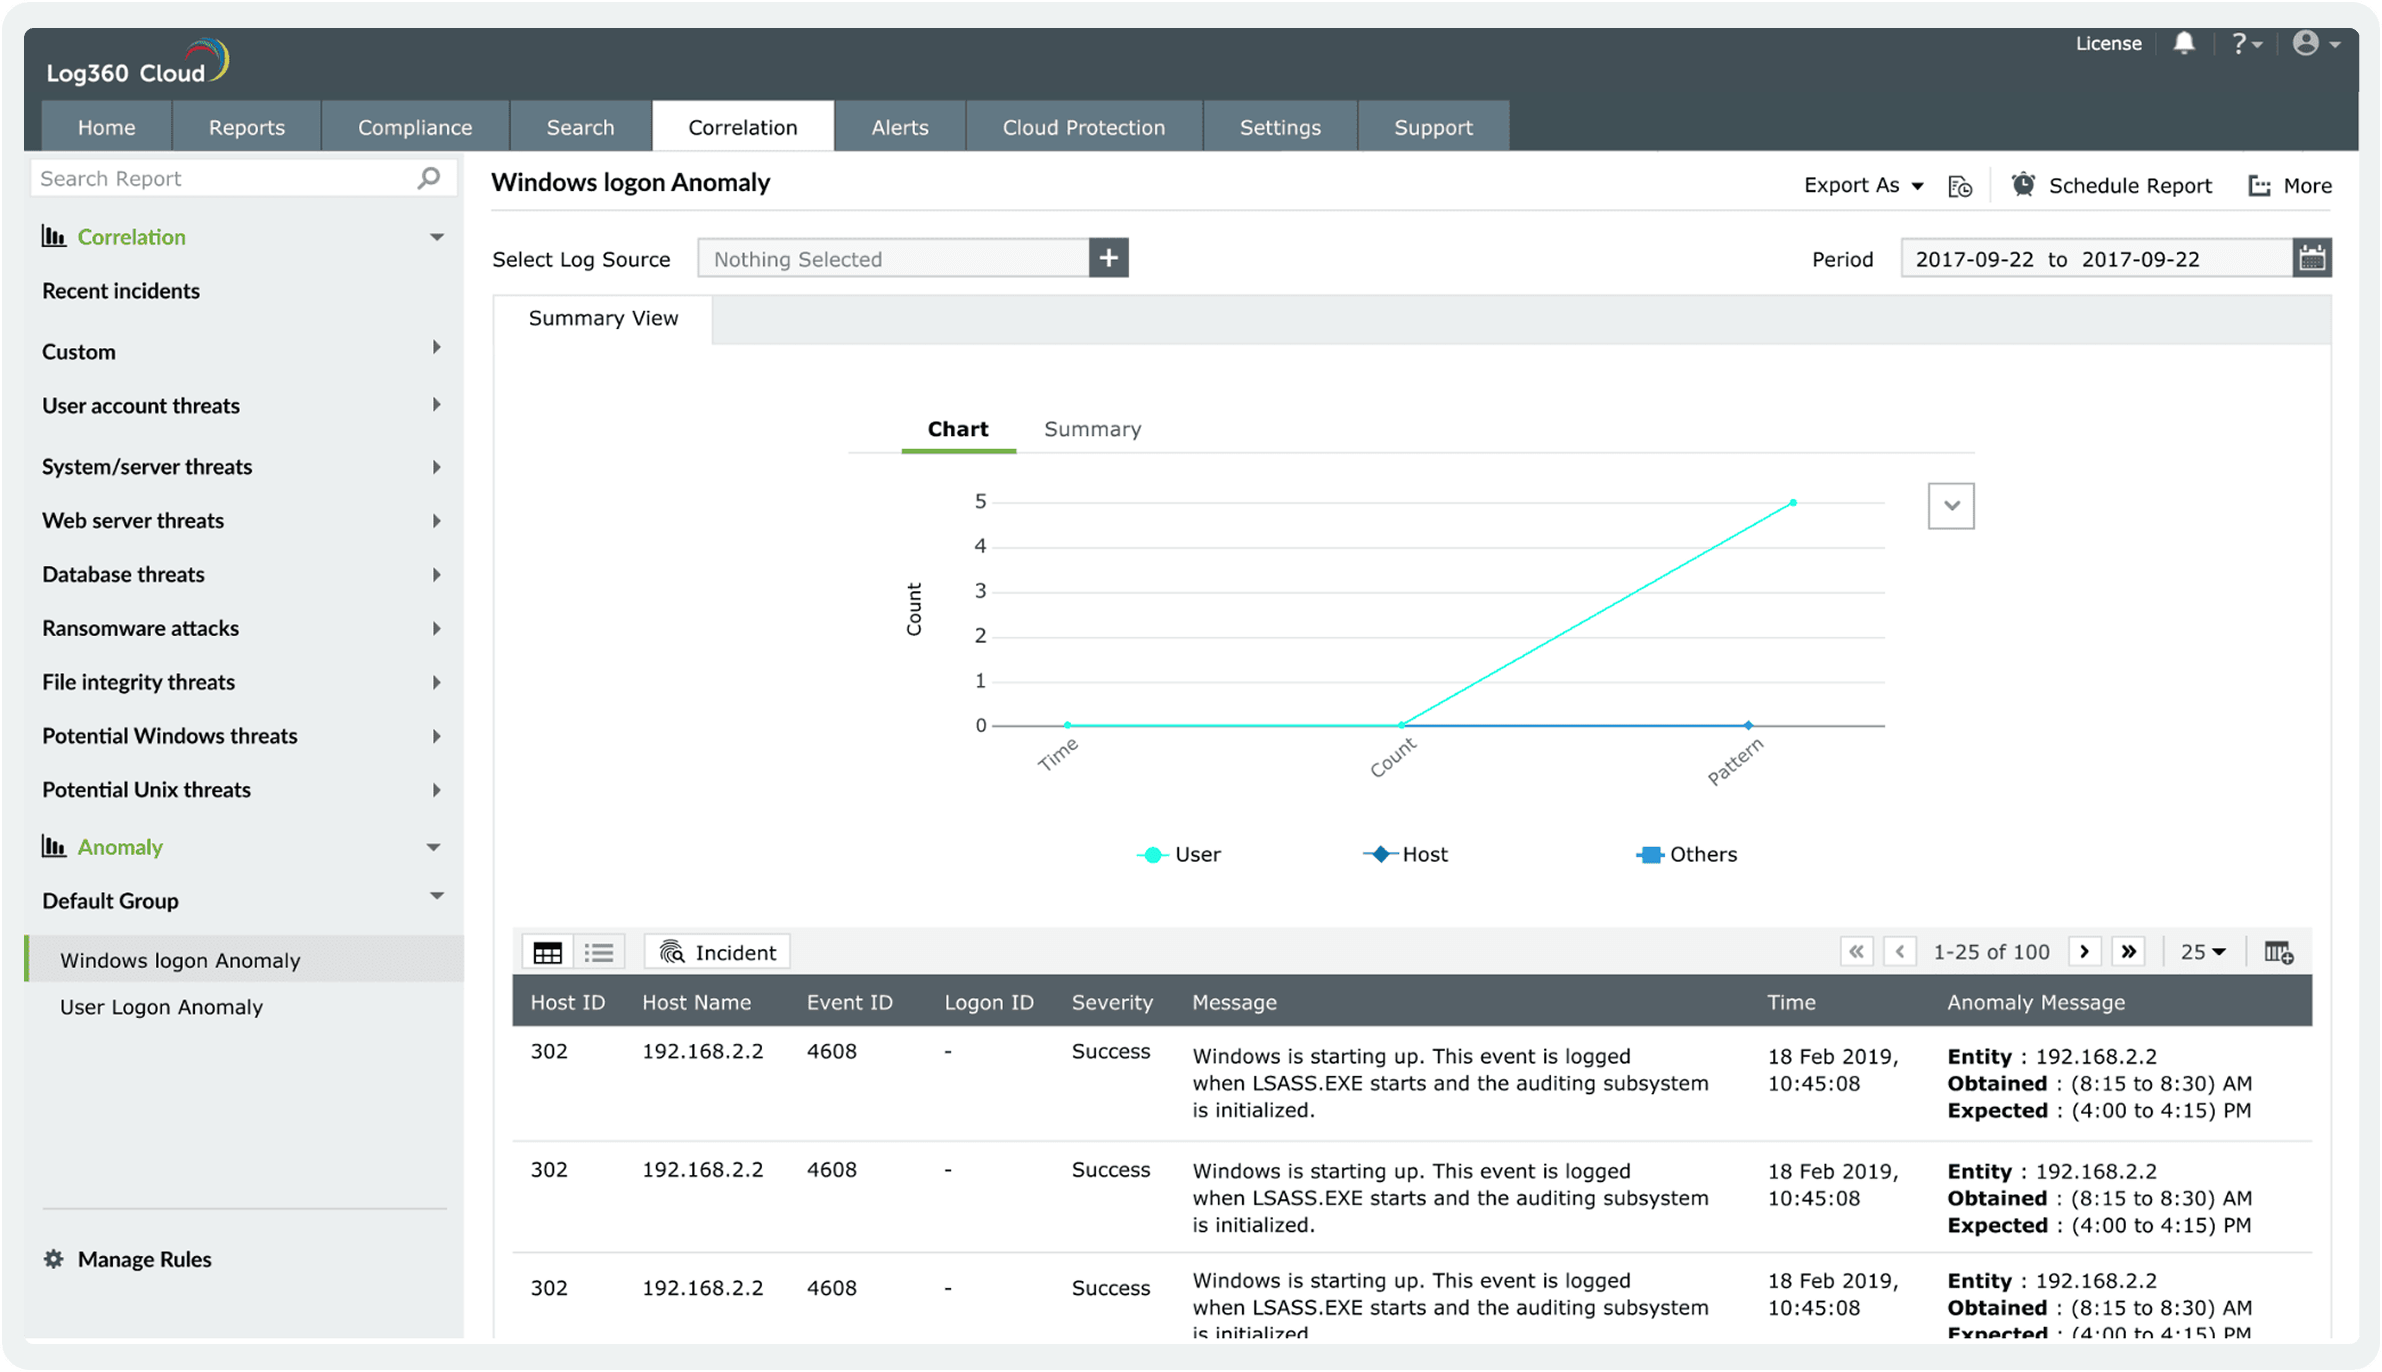
Instantly identify complex threats by correlating events across your entire network. The engine analyzes logs in real-time, triggering alerts on suspicious patterns and anomalies.
Behavior analytics
 

Behavior analytics

Proactively hunt for slow-moving and evasive attacks. ML-powered analytics continuously learns and adapts, identifying patterns that bypass traditional rule-based security
Investigate threats
 

Investigate threats

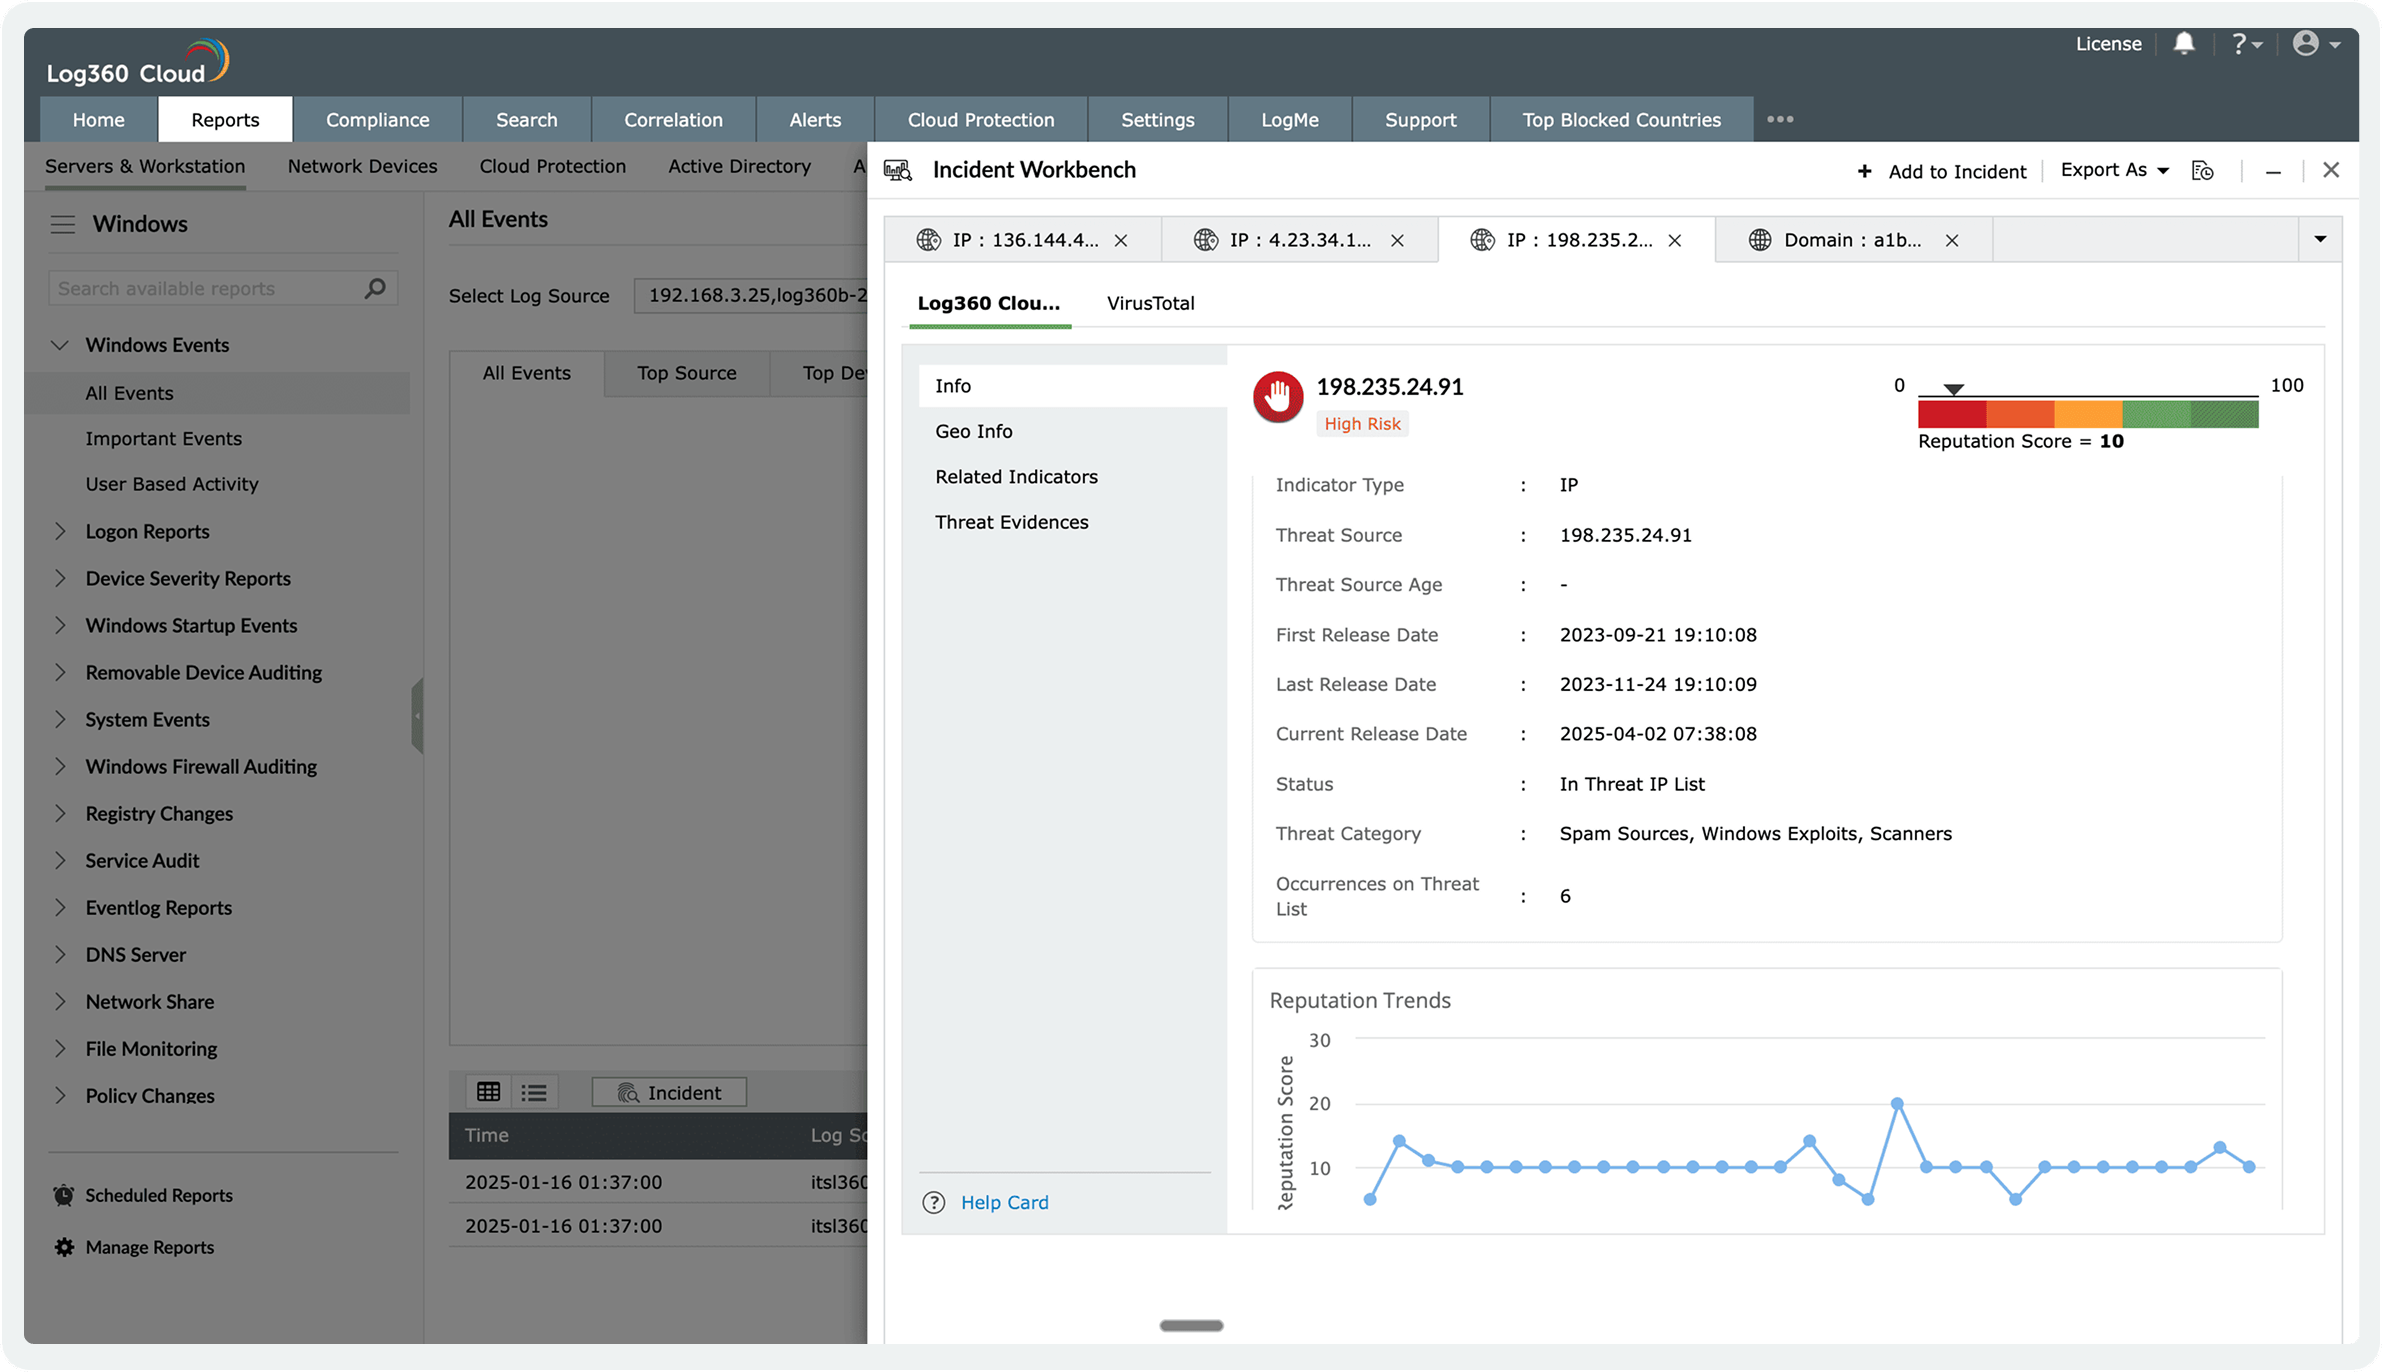
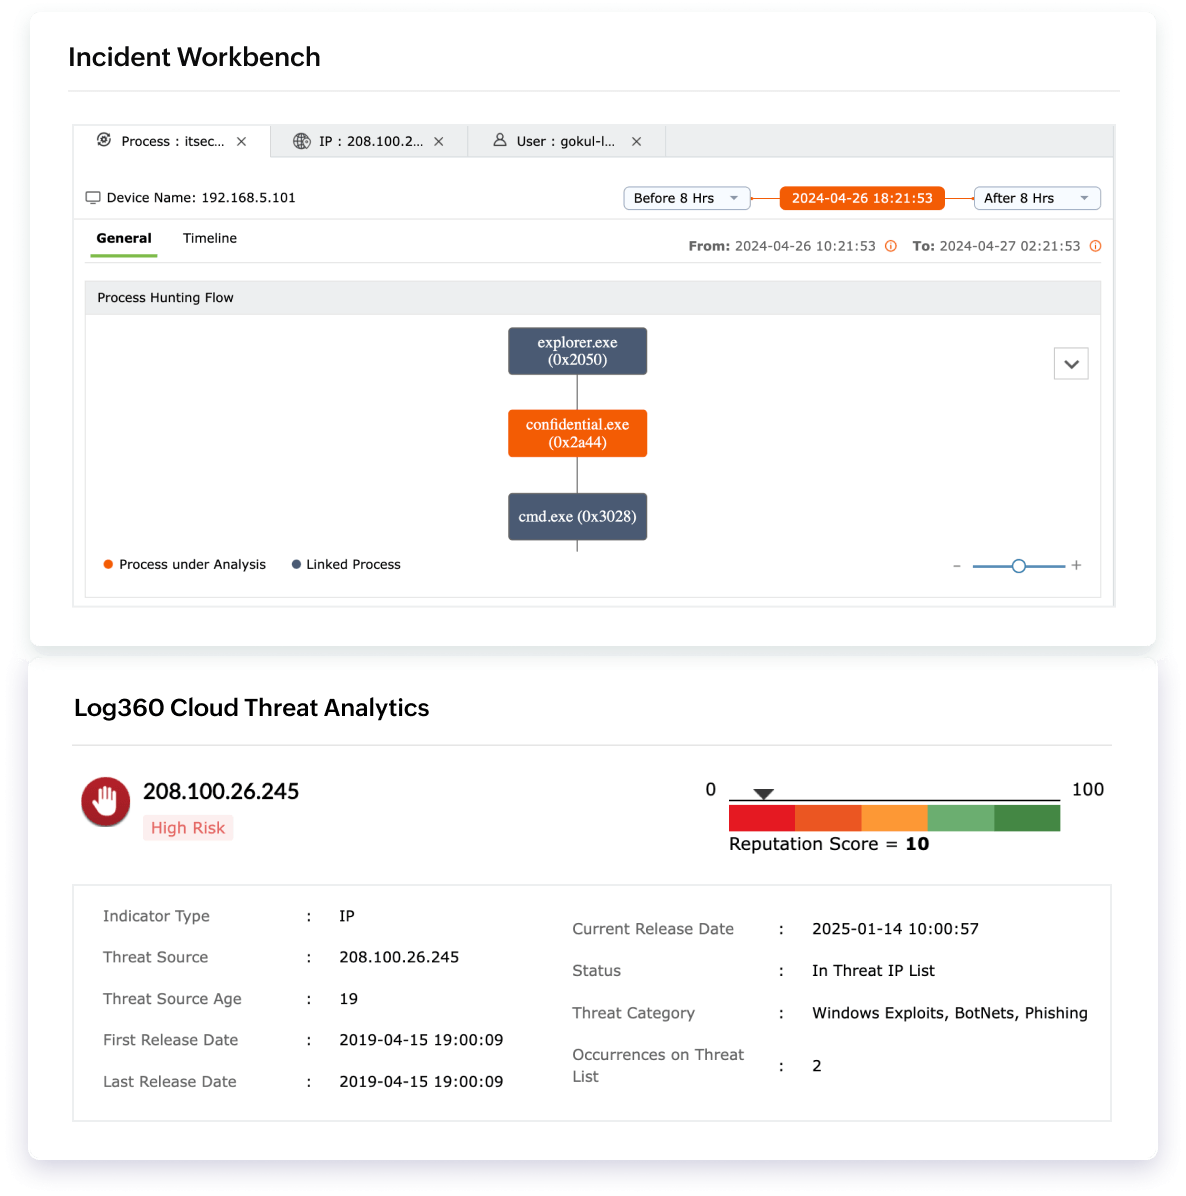
Accelerate incident response with enriched context. The workbench consolidates user, device, and threat intelligence, providing a comprehensive view for rapid investigation.
Protect cloud apps
 

Protect cloud apps

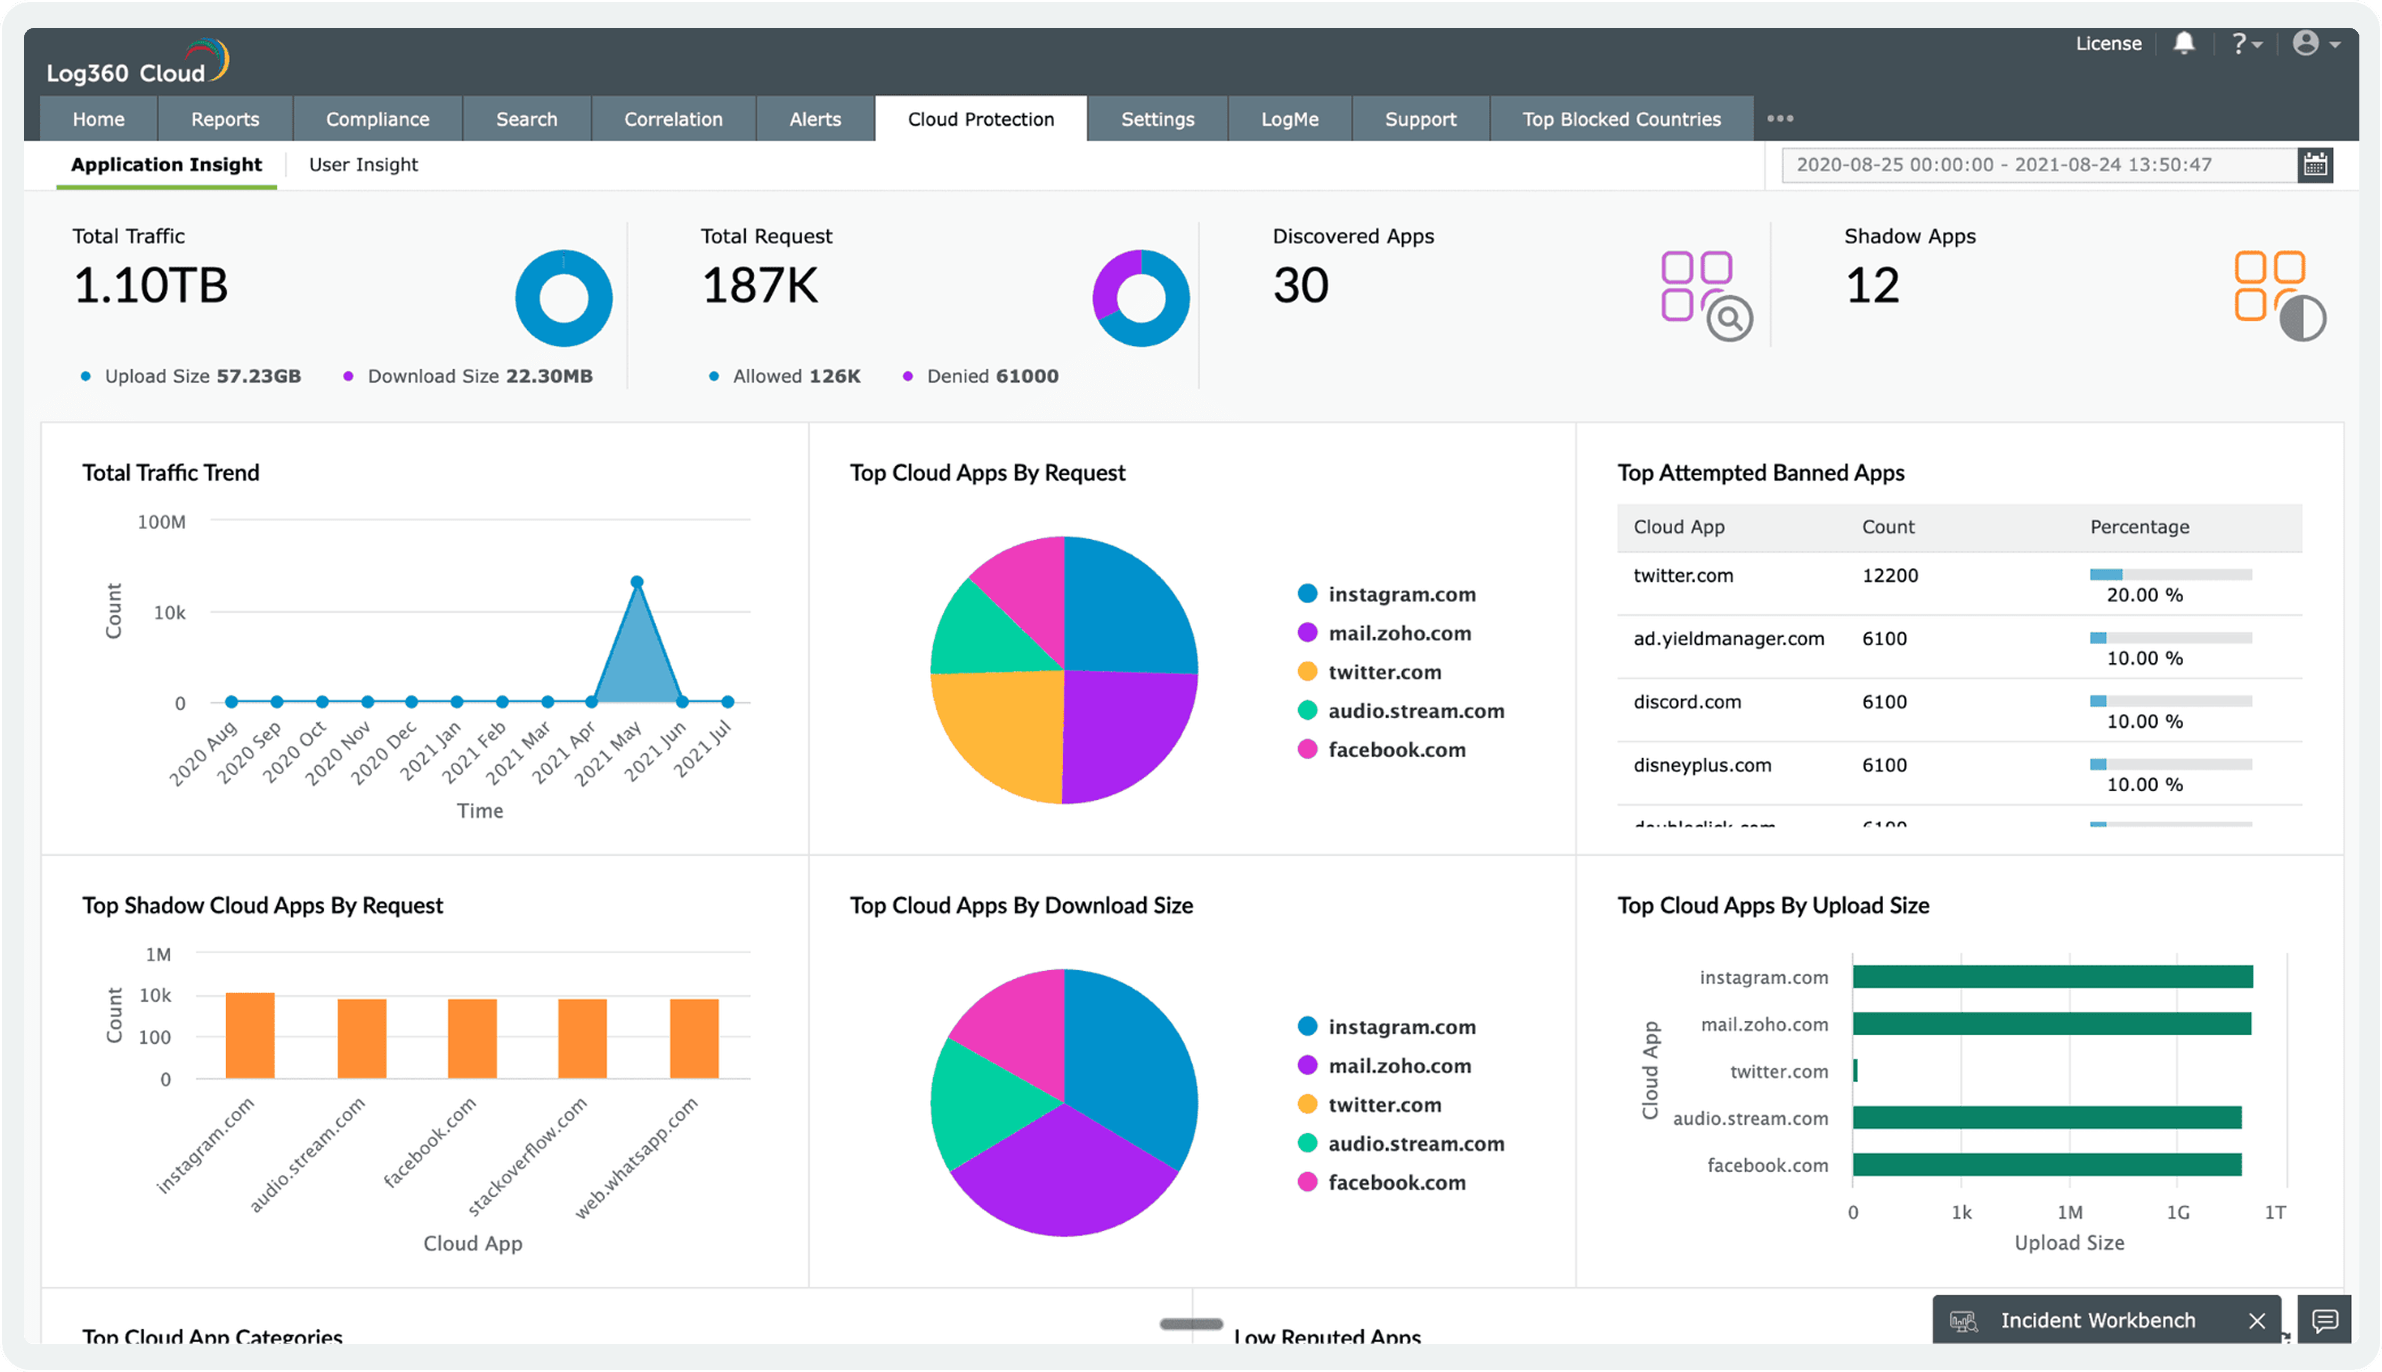
Track cloud app usage, detect shadow IT, and enforce security policies. Monitor both sanctioned and unsanctioned apps to safeguard sensitive data.

Cloud-based SIEM for enhanced
security and compliance

  • Cloud log management
  • Detection rules
  • AI SOC
  • UEBA
  • Threat intelligence
  • Native SOAR
  • Cloud compliance
  • Identity security

Unparalleled security visibility from log analysis

Experience the power of cloud-based log management with Log360 Cloud. Gain deep insights into security, access, system, and application logs across your network. With Log360 Cloud, you can:
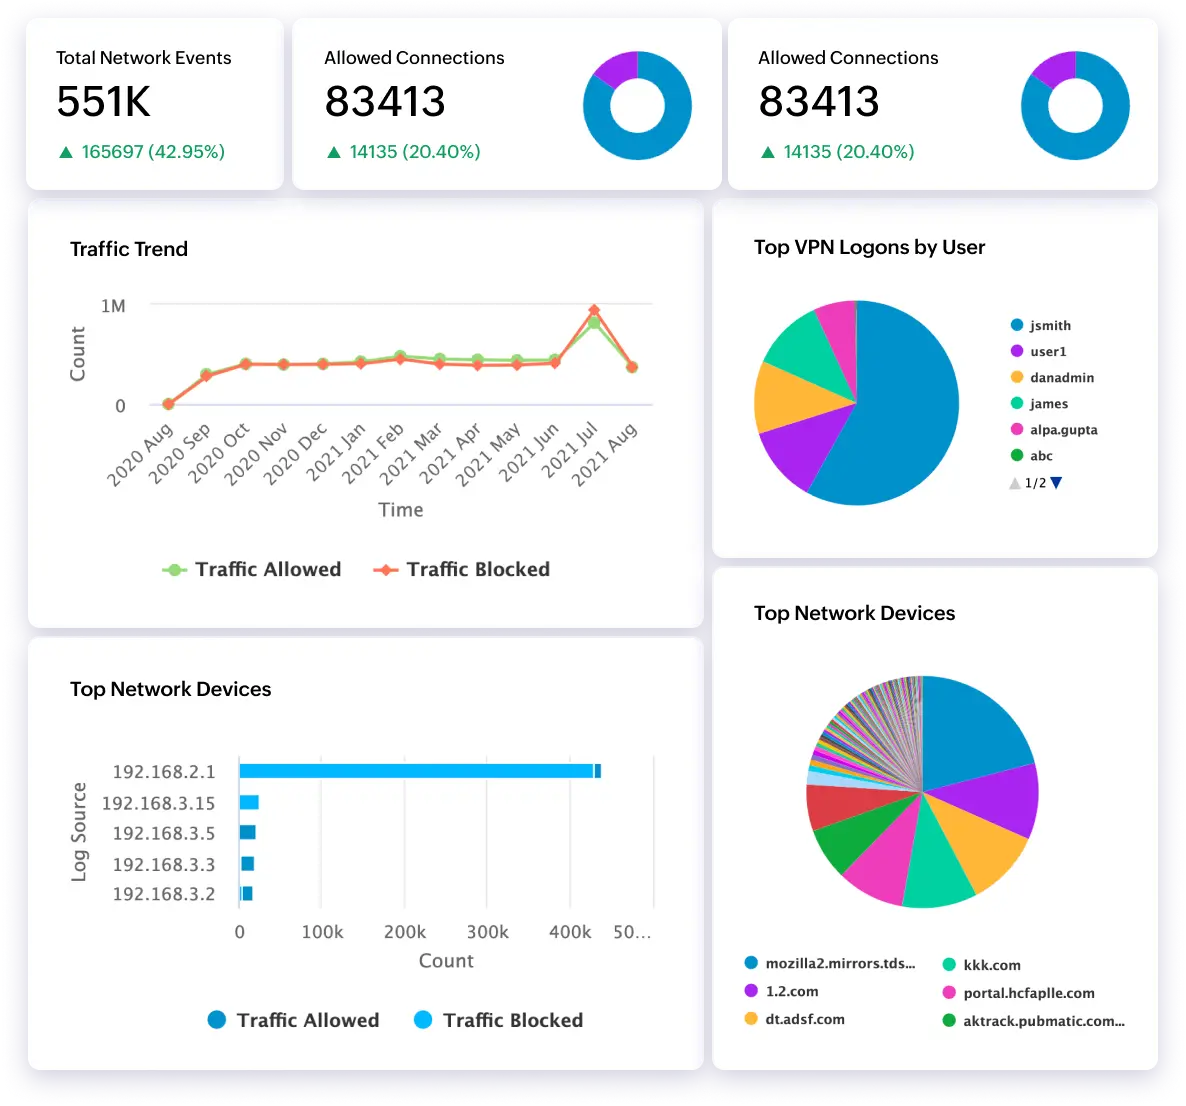
  • Streamline log collection and storage: Automatically and securely collect and store logs from Windows servers, syslog sources, applications, and cloud platforms.
  • Conduct thorough log analysis: Leverage advanced search and correlation capabilities to quickly identify and investigate security events.
  • Ensure compliance: Securely archive log data for forensic analysis and regulatory mandates using our flexible storage options. Leverage pricing plans to optimize log storage costs while securely archiving log data.
Explore cloud log management 
Unparalleled security visibility from log analysis
Explore Log360 Cloud's detection rule library

Detection rules for sophisticated threats

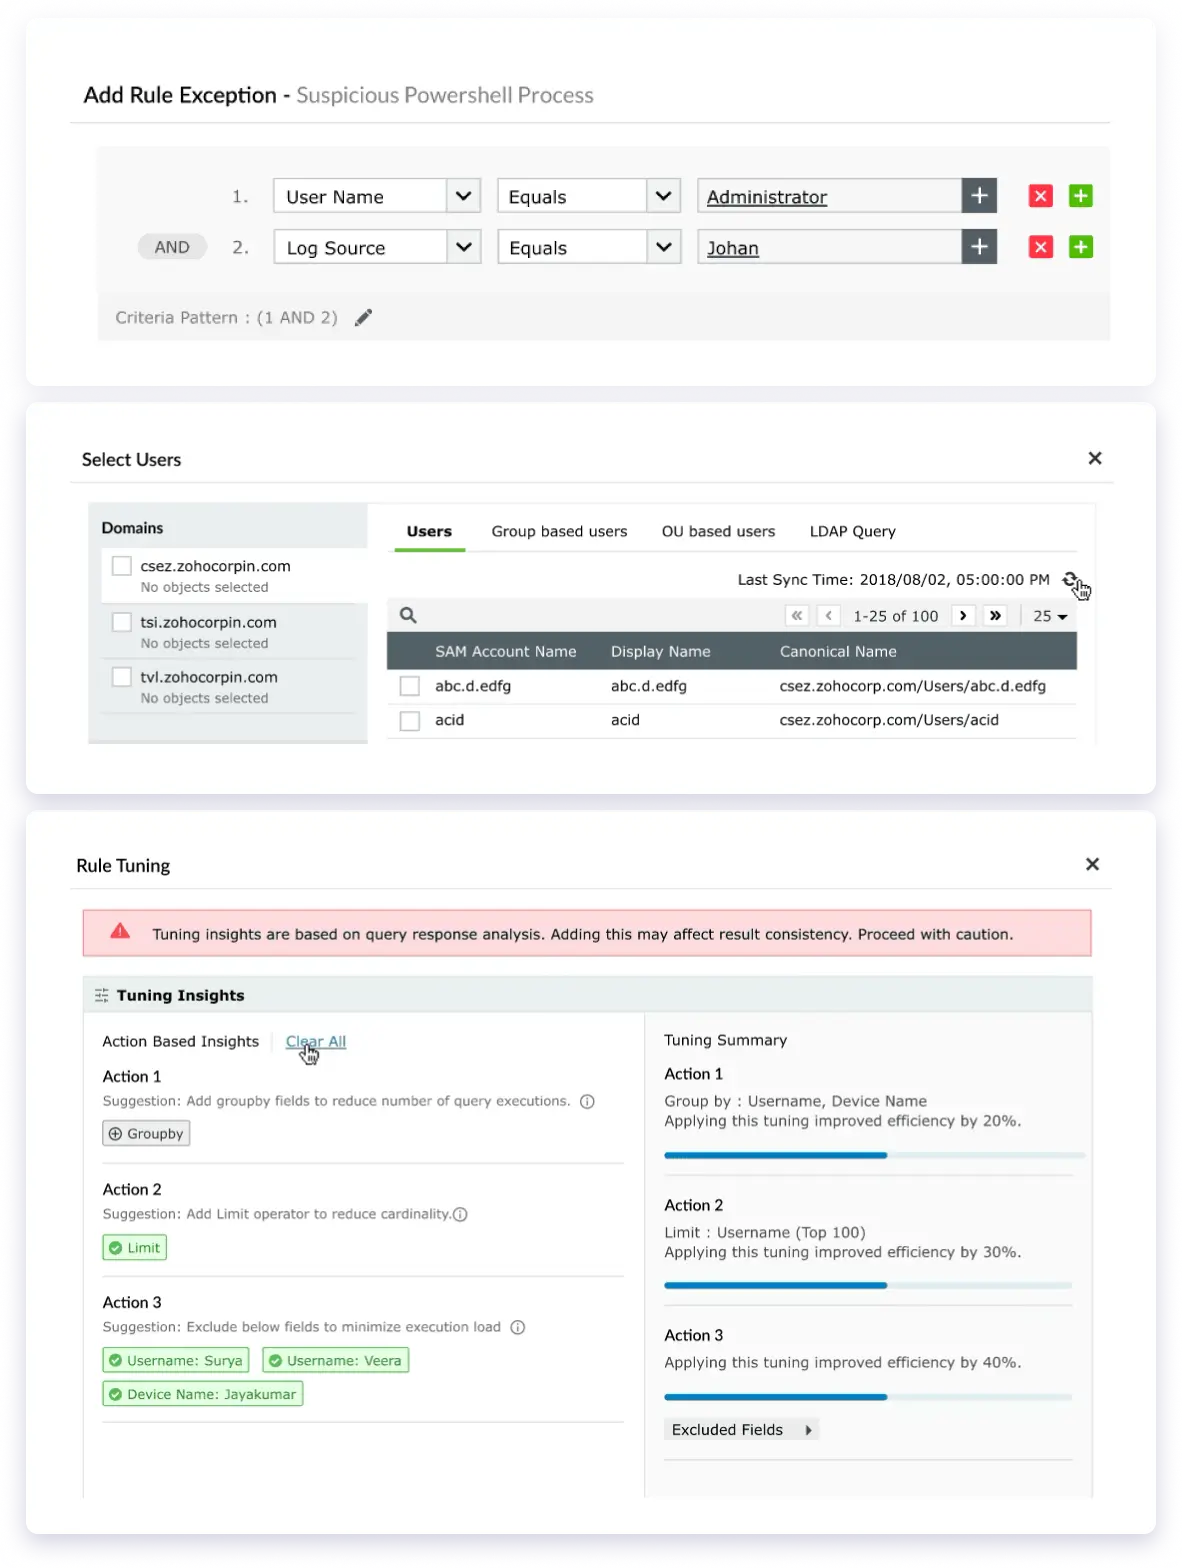
Cut through the noise with threat detection built for precision. Log360 Cloud delivers 2000+ MITRE-mapped detection rules covering correlation, anomaly, and threat intelligence, designed to reduce false positives and surface real threats. With Log360 Cloud, you can:

  • Manage detections from a single pane: Access correlation rules, anomaly rules, and threat intel matches through one centralized console, no more toggling between modules.
  • Tune rules without writing queries: Create and customize Standard, Anomaly, and Advanced detection rules using an intuitive visual builder. No SPL, KQL, or scripting needed.
  • Filter out the noise at the source: Apply exclusions at the user, group, OU, or device level across predefined rules to focus only on high-value signals.
  • Act on tuning recommendations: Get actionable insights on your noisiest rules and optimize detection performance with guided recommendations.
Explore Log360 Cloud's detection rule library 

Anomaly detection

Go beyond traditional rule-based detection by identifying deviations in user and entity behavior patterns using anomaly rules. Detect potential insider threats like logon anomalies, compromised accounts, and data exfiltration attempts, before they escalate. With UEBA, you can:
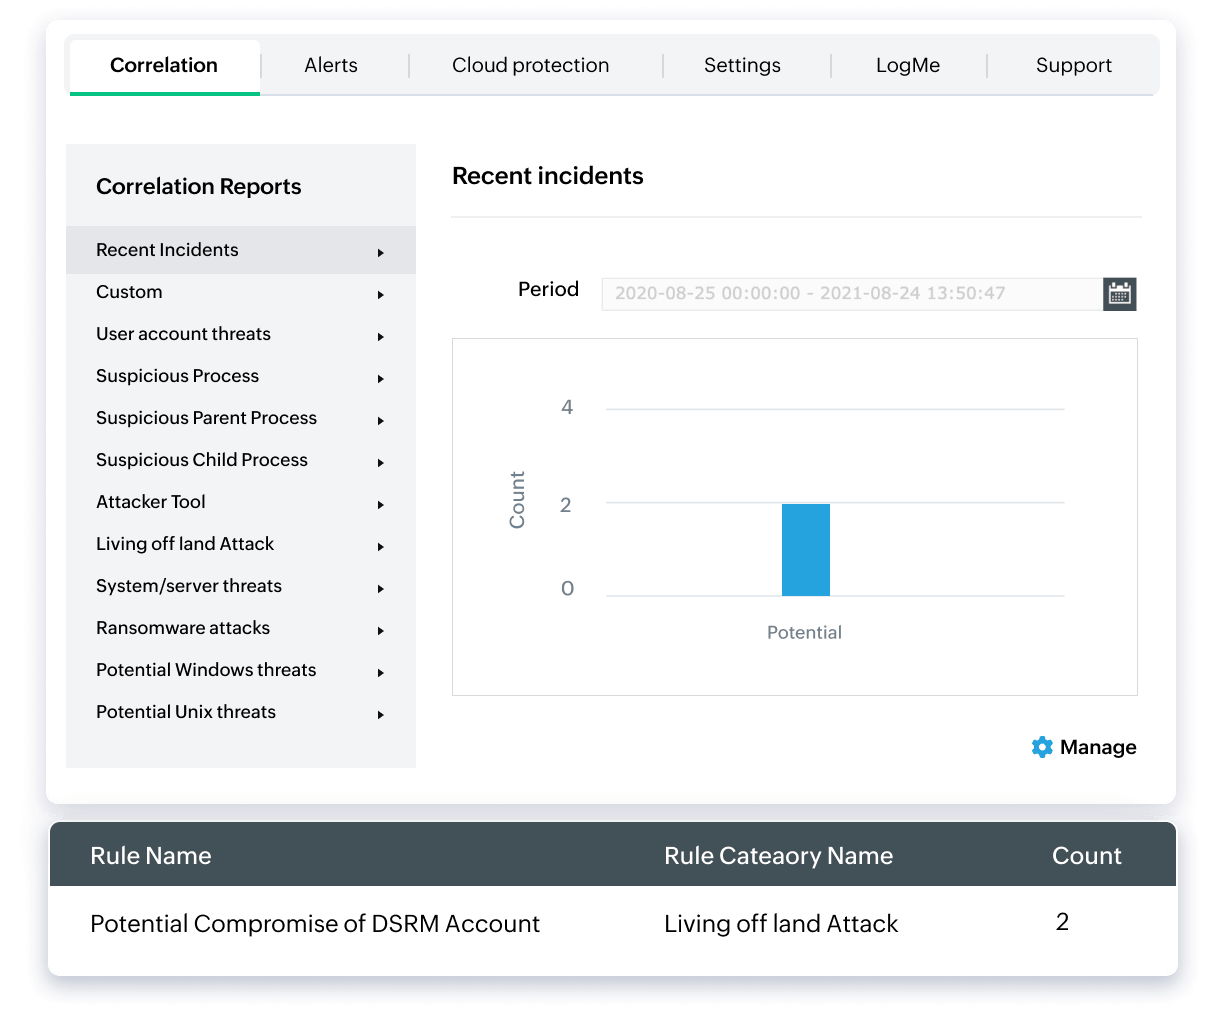
  • ML-based anomaly detection: Automatically detect deviations from normal behavior using machine learning algorithms.
  • Accurate detection: Identify threats based on time, count, and pattern anomalies for higher precision.
  • Proactive threat identification: Uncover anomalous behavior such as unusual logins or file transfers early on.
  • Integrated risk scoring: Identify high-risk users and entities with scores based on triggered anomalies and predefined behavioral indicators.
  • Custom anomaly rule creation: Create single or bulk anomaly rules tailored to your environment.
Anomaly detection
Preconfigured threat intelligence and advanced threat analytics

Preconfigured threat intelligence and advanced threat analytics

Empower your defenses with a threat intelligence database featuring over 600 million malicious URLs, domains, and IP addresses. With Log360 Cloud's integrated platform, you get:

  • Seamless integration with threat data: Connect effortlessly with STIX/TAXII-formatted threat feeds for industry-specific coverage.
  • Real-time insights: Benefit from BrightCloud-powered analytics that provide reputation scores and threat types for malicious entities.
  • Enhanced security analytics: Integrate dynamic threat data into our detection engine for faster, more effective responses.

Streamline SecOps with a unified platform for automated response and orchestration

Move beyond isolated actions and bring consistency to every response. Log360 Cloud's native SOAR connects your tools, standardizes decision making, and automates execution so your team can investigate and respond with speed and precision.
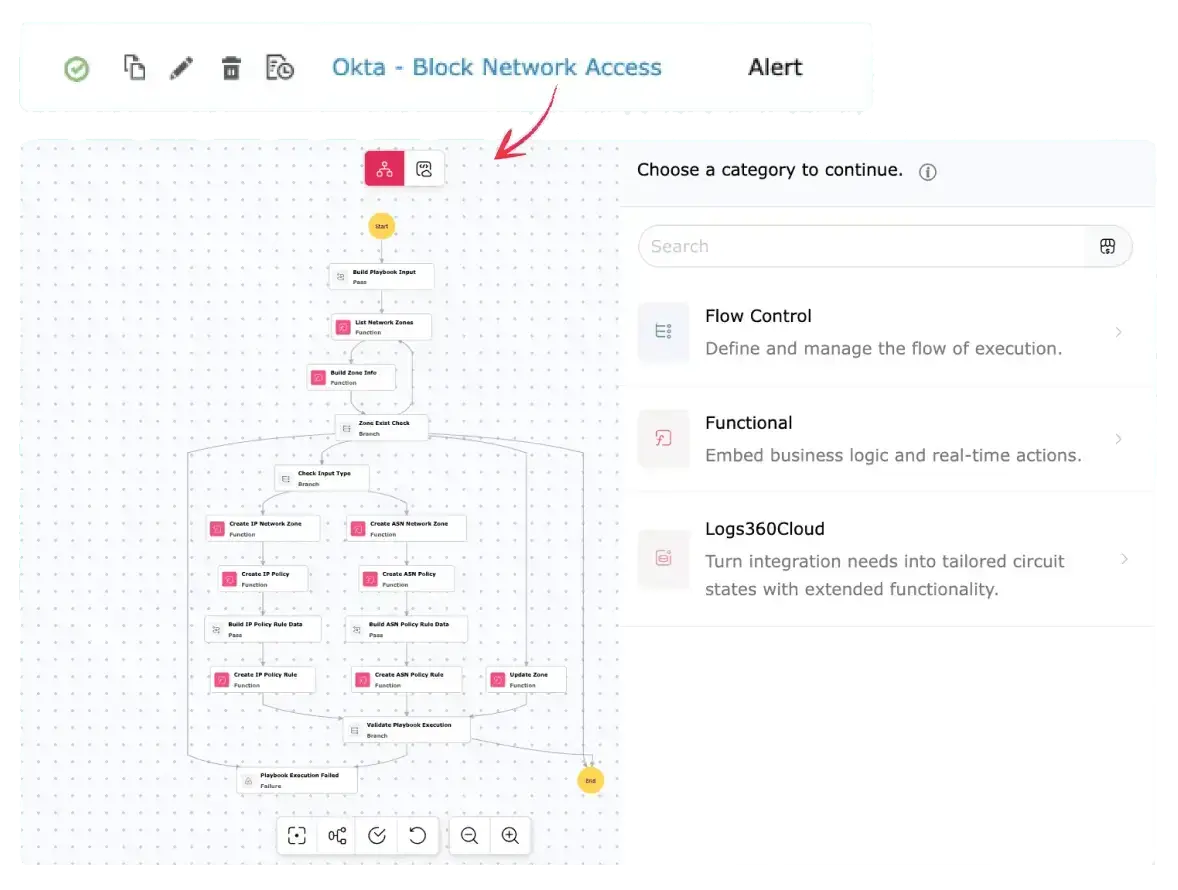
  • Execute playbooks with confidence: Run pre-built and custom playbooks that guide investigations and response from start to finish, ensuring every action follows a proven path.
  • Automate response without complexity: Design workflows using a visual builder that eliminates manual steps and reduces dependency on scripts or external tooling.
  • Coordinate actions across your stack: Trigger actions across integrated security tools from a single workflow, eliminating swivel chair operations and fragmented response.
  • Extend workflows with custom logic: Embed Python or Deluge scripts in playbooks to handle edge cases and complex logic, and reuse them across workflows for flexible automation.
Explore Log360 Cloud's playbook library  
Streamline SecOps with a unified platform for automated response and orchestration
Audit-ready compliance reports and violation alerts

Audit-ready compliance reports and violation alerts

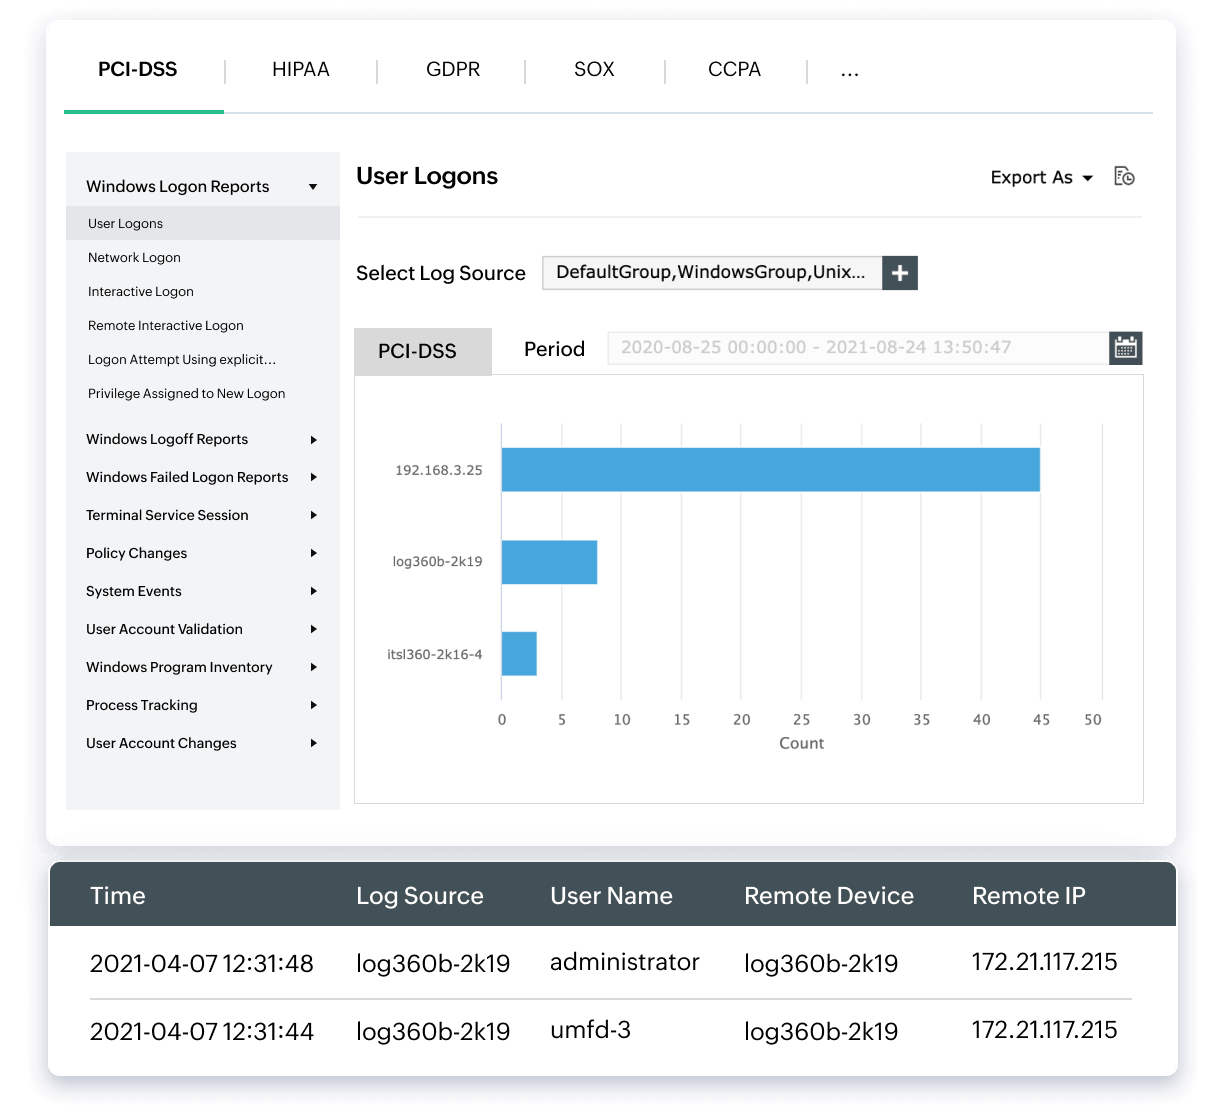
Log360 Cloud streamlines compliance while enhancing your security posture. It provides:

  • Effective compliance management: Use pre-built audit report templates (PCI DSS, GLBA, FISMA, SOX, HIPAA, ISO 27001, etc.) to demonstrate adherence to security standards, while securely storing log data in the cloud—eliminating costly hardware.
  • Continuous monitoring & remediation: Proactively monitor compliance with dedicated dashboards, identify gaps, and implement timely fixes.
  • Enhanced audit trails: Maintain detailed logs of user activity to swiftly detect and respond to suspicious access or data breaches.
Explore cloud compliance 

In-depth Active Directory auditing and monitoring

Protect identities during your cloud transition with Log360 Cloud. By monitoring Active Directory, it helps you:
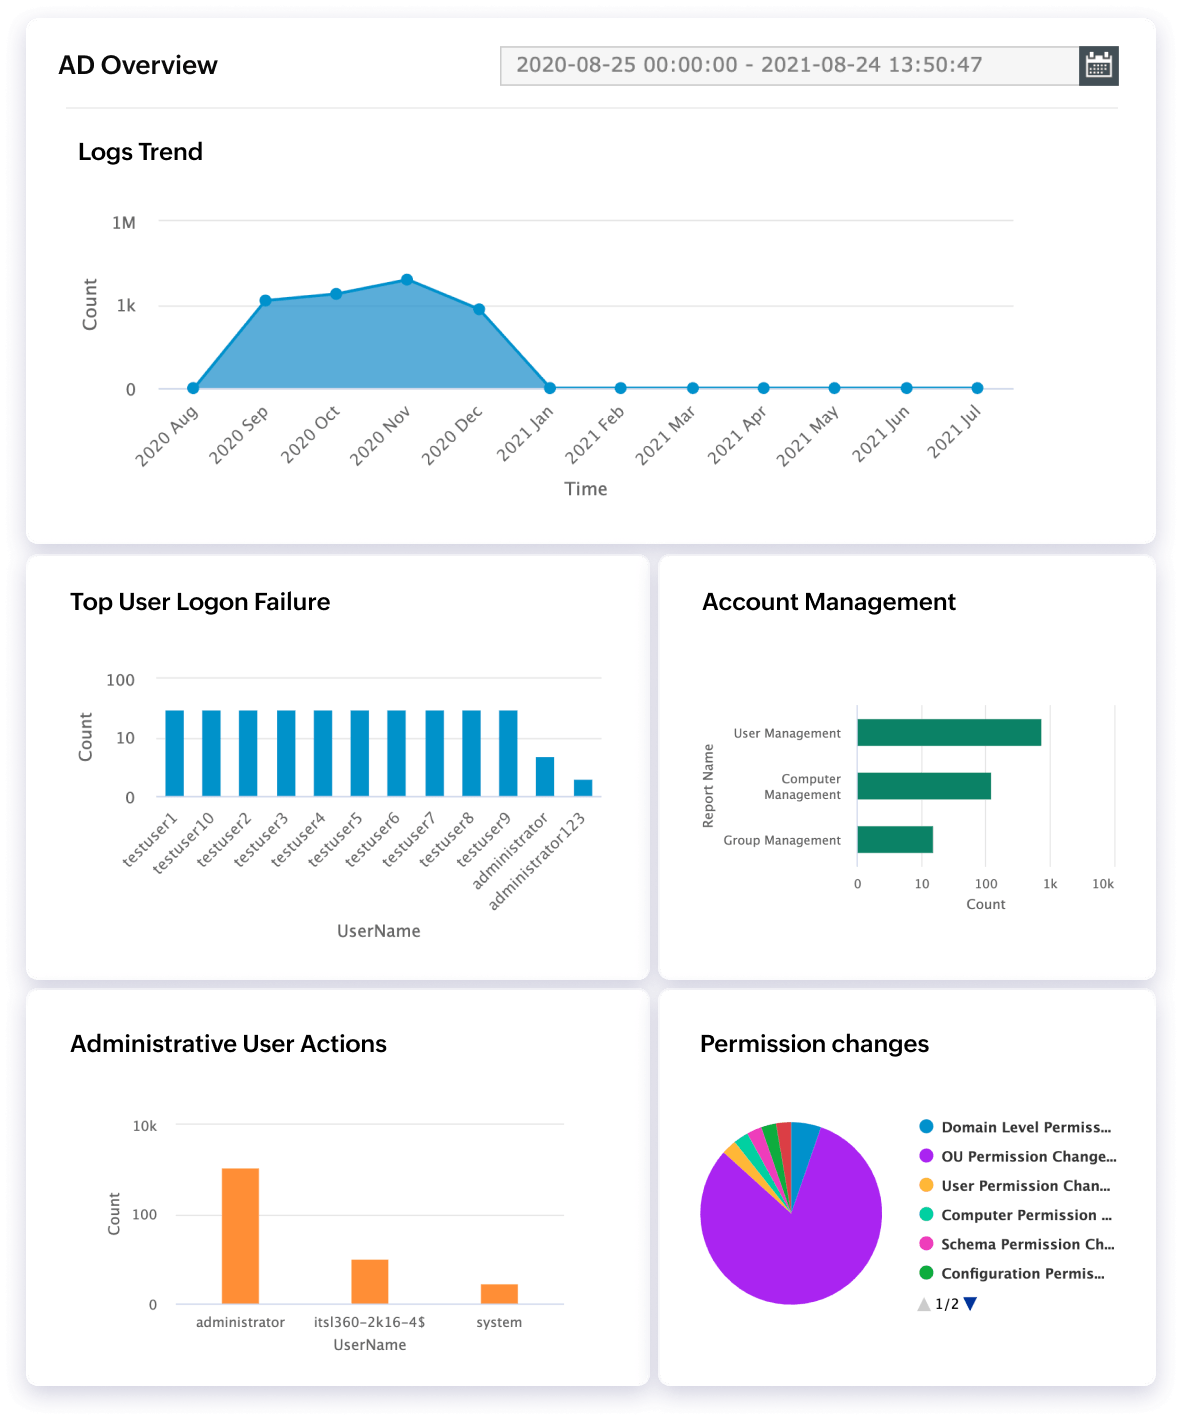
  • Granularly audit user activity: Gain deep visibility into authentication events and detect potential intrusion attempts or impersonation.
  • Monitor critical AD changes in real time: Instantly identify modifications to OUs, GPOs, and permissions to preempt insider threats.
  • Detect identity-based attacks: Continuously monitor for privilege escalations, lateral movements, and credential stuffing.
  • Automate user behavior monitoring: Automatically flag unusual account activities—such as frequent lockouts or logins from disparate locations—to catch threats early.
Explore real-time AD auditing 
In-depth Active Directory auditing and monitoring

AI-powered security operations

Get more context from alerts, investigate threats faster, and work with security data in natural language. Zia brings AI-powered insights, investigation, search, and agents into Log360 Cloud to simplify everyday SOC tasks. With Log360 Cloud, you can:
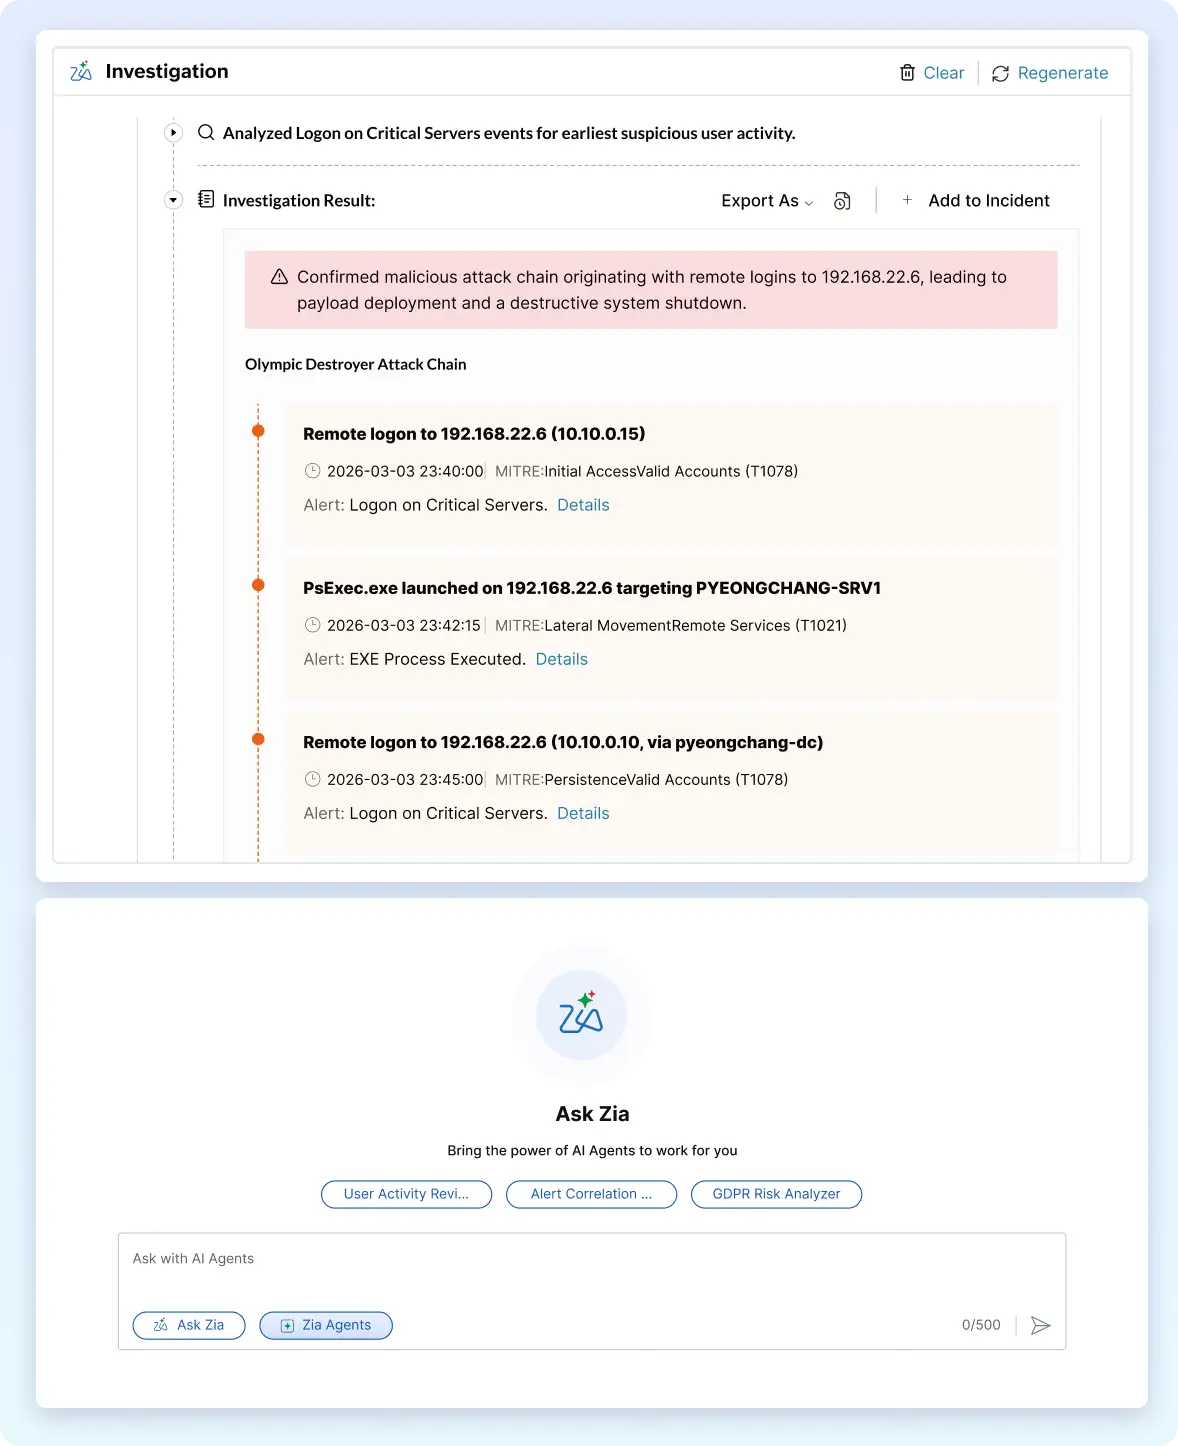
  • Understand alerts at a glance: Get concise summaries of what happened, its potential impact, relevant MITRE ATT&CK techniques, and recommended next steps.
  • Investigate alerts with AI: Correlate related alerts, logs, users, devices, and threat intelligence to reconstruct attack chains and identify the scope of a threat.
  • Search security data in natural language: Ask questions about logs, and alerts without writing queries or switching between modules.
  • Build and deploy AI agents: Use prebuilt agents or create custom agents without code to handle investigations, risk assessments, compliance tasks, and other SOC workflows.
Explore Zia AI capabilities in Log360 Cloud 
Zia AI investigation and Ask Zia agents in Log360 Cloud

Trusted by people like you


"We gained complete visibility into our server and security logs. The solution’s threat detection, event monitoring, and log analysis features have significantly improved how the organization tracks and responds to security events."

Dhanaraj K, Chief Information Security Officer,
Vibrant Screen

Key offerings of Log360 Cloud’s SIEM technology

Experience the transformative power of cloud-based log management with Log360 Cloud.

Know more 
01
06
 

Unified SIEM solution

With Log360 Cloud, experience the power of a unified platform that brings together essential cybersecurity capabilities. Our cloud-native SIEM solution leverages advanced correlation techniques for threat detection, ensures cloud data security with robust CASB features, and streamlines compliance efforts through effective auditing and monitoring. By integrating these critical elements, Log360 Cloud empowers organizations to achieve seamless security operations and protect their valuable assets.

Learn more 
02
06
 

SOAR: Automate critical SecOps workflows

Turn fragmented actions into decisive, automated workflows. With native SOAR in Log360 Cloud, your team moves from alert chasing to outcome driven response that is standardized, accelerated, automated, and consistent across your environment. Reduce manual effort, shorten MTTR, and accelerate investigations to contain threats before they escalate.

Learn more 
03
06
 

AI for every stage of security operations

Strengthen your SOC with AI capabilities built into Log360 Cloud. Gain contextual threat analysis, accelerate investigations, search logs and alerts using natural language, and use AI agents to automate security workflows. Built with Bring Your Own Key (BYOK) support and Model Context Protocol (MCP) integrations, Log360 Cloud fits seamlessly into your existing AI ecosystem.

Learn more 
04
06
 

CASB: Full visibility and control over cloud

Gain complete control over your cloud environment with Log360 Cloud’s CASB. Monitor cloud application usage to identify unauthorized shadow IT, gain deep insights into user activity, and quickly detect potential threats. Integrating CASB with cloud-based SIEM helps uncover shadow applications and build actionable context around threat actor behavior.

Learn more 
05
06
 

Security Platform: Flexibility to build security your way

Take full control of your security with Log360's unified platform approach. Seamlessly integrate your security tools through Open APIs, visualize data exactly how you need it, and extend functionality with custom extensions to meet your evolving needs. Build a security ecosystem that works exactly how you want it to work.

Learn more 
06
06
 

Cloud-based log storage: No upfront costs

Benefit from intuitive log collection, analysis, search, and storage with Log360 Cloud. Perform high-speed searches and meet compliance retention requirements using a flexible pricing plan paired with adaptive storage options. This scalable, cost-effective solution eliminates the need for upfront hardware investments and ongoing infrastructure maintenance.

Learn more 

Log360 Cloud pricing

Scalable, component-based pricing for modern cloud SIEM. Pay only for the components
you need and expand as your security operations evolve.

Explore pricing

Resources

What's Log360 Cloud?
PDF DOCUMENT

What's Log360 Cloud?

Learn more
 
Unique benefits of Log360 Cloud
ONLINE

Unique benefits of Log360 Cloud

Learn more
 
Log storage calculator
ONLINE

Log storage calculator

Learn more
 

FAQs on Log360 Cloud SIEM

What is SIEM?

A security information and event management (SIEM) solution is a cybersecurity cornerstone, empowering security operations centers to rapidly detect, prioritize, and respond to threats. It ensures compliance, strengthens security posture, and streamlines incident response. By ingesting and analyzing logs and security telemetry from across the network, SIEM tools employ advanced techniques like correlation and behavior modeling to proactively identify and mitigate security risks.

Learn more about SIEM 

What is SIEM-as-a-service?

SIEM-as-a-service (Security Information and Event Management) is a cloud-based solution that provides real-time analysis of security alerts generated by various network hardware and applications.

Key features include:

  • Log collection and aggregation from multiple sources
  • Real-time threat detection and alerting
  • Automated incident response capabilities
  • Compliance reporting and management
  • Scalable cloud infrastructure managed by the service provider

Cloud SIEM eliminates the need for organizations to maintain complex on-premises SIEM infrastructure, offering a more flexible and often more cost-effective security solution.

When should organizations choose cloud SIEM over on-prem SIEM?

Organizations should consider cloud SIEM over on-premises solutions in the following scenarios:

  • Limited IT resources: When there's a lack of in-house expertise to manage complex SIEM infrastructure.
  • Cost considerations: To avoid large upfront capital expenses for hardware and software licenses.
  • Scalability needs: For businesses experiencing rapid growth or fluctuating demand.
  • Distributed workforce: To better support employees in multiple locations.
  • Faster deployment: When there's a need to implement SIEM capabilities quickly.
  • Desire for continuous updates: To benefit from the latest threat intelligence and feature updates without manual intervention.
  • Compliance requirements: To more easily meet regulatory standards that require robust log management and security monitoring.

To decide between an on-premise and a cloud SIEM, read our detailed blog on the topic here.

How does Log360 Cloud ensure the security of my log data?

Log360 Cloud employs multiple layers of security to protect your sensitive log data:

  • Encryption: All data is encrypted both in transit and at rest using industry-standard encryption protocols.
  • Access controls: Strict role-based access controls and multi-factor authentication are implemented to prevent unauthorized access.
  • Data isolation: Each customer's data is logically segregated to ensure data privacy.
  • Compliance: The service adheres to major compliance standards, including ISO/IEC 27001, 27017, and 27018; SOC 2 (including SOC 2 + HIPAA); SOC 1 (SSAE 18 & ISAE 3402 Type II); and ISO 9001:2015.
  • Regular audits: Periodic security audits and penetration testing are conducted to identify and address potential vulnerabilities.
  • Redundancy: Data is replicated across multiple secure data centers to ensure high availability and disaster recovery capabilities.
  • Secure APIs: All integrations and data transfers use secure APIs with proper authentication mechanisms.
  • Monitoring: Continuous monitoring of the cloud infrastructure for any security anomalies or potential threats.

Get started with secure cloud
log management in minutes

Sign up