Every log you collect becomes evidence. Parsed on arrival, retained to policy, and reportable against 30+ mandates.
4625 · logon failed · svc_backupPCI DSS 10.2.1.45145 · share access · HR/payrollHIPAA §164.312(b)sudo · /etc/shadow · rootPCI DSS 10.2.1.2deny · 203.0.113.44 → 10.4.2.0/24NIS 2 Art. 21including GDPR, HIPAA, PCI DSS 4.0, SOX, NIST, and more.
across on-premises, cloud, and hybrid environments.
with automated evidence collection and tamper-proof log archival.
that helps you avoid non-compliance.
Same twelve months, same regulations. The only thing that differs is whether the work is spread across the year or crammed into the three weeks before the audit.
Each one has a report behind it and a clause it satisfies.
Every administrative logon across AD, Microsoft 365, AWS, and Azure lands in one place as it happens. Just open the logon activity report, apply an object filter for the accounts that touch the cardholder environment, set the date range, and export. No data-gathering project needed.
PCI DSS 10.2.1.2 PCI DSS 10.5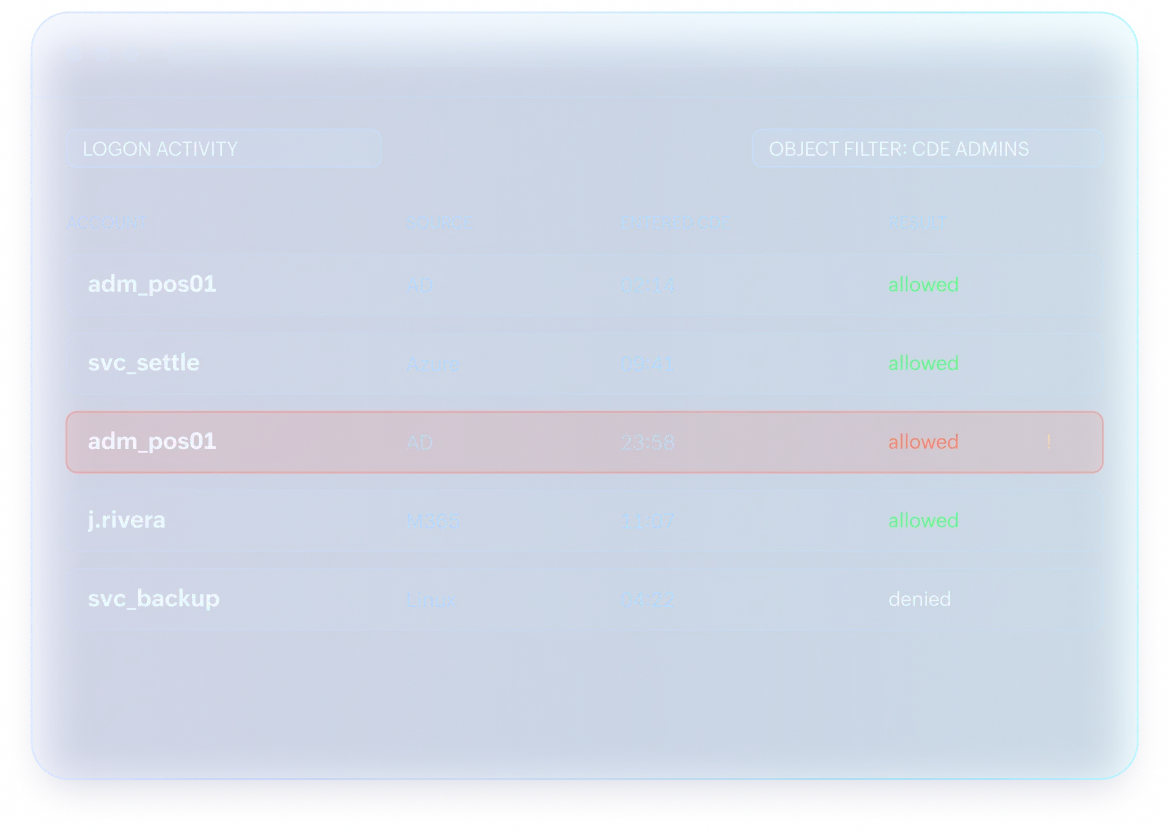
Every read, write, move, or delete against PHI is tracked across your Windows, NAS, and database stores. Search a single record and pull its full access history in one query—no reconstruction job required.
HIPAA §164.312(b) HIPAA §164.308(a)(1)(ii)(D)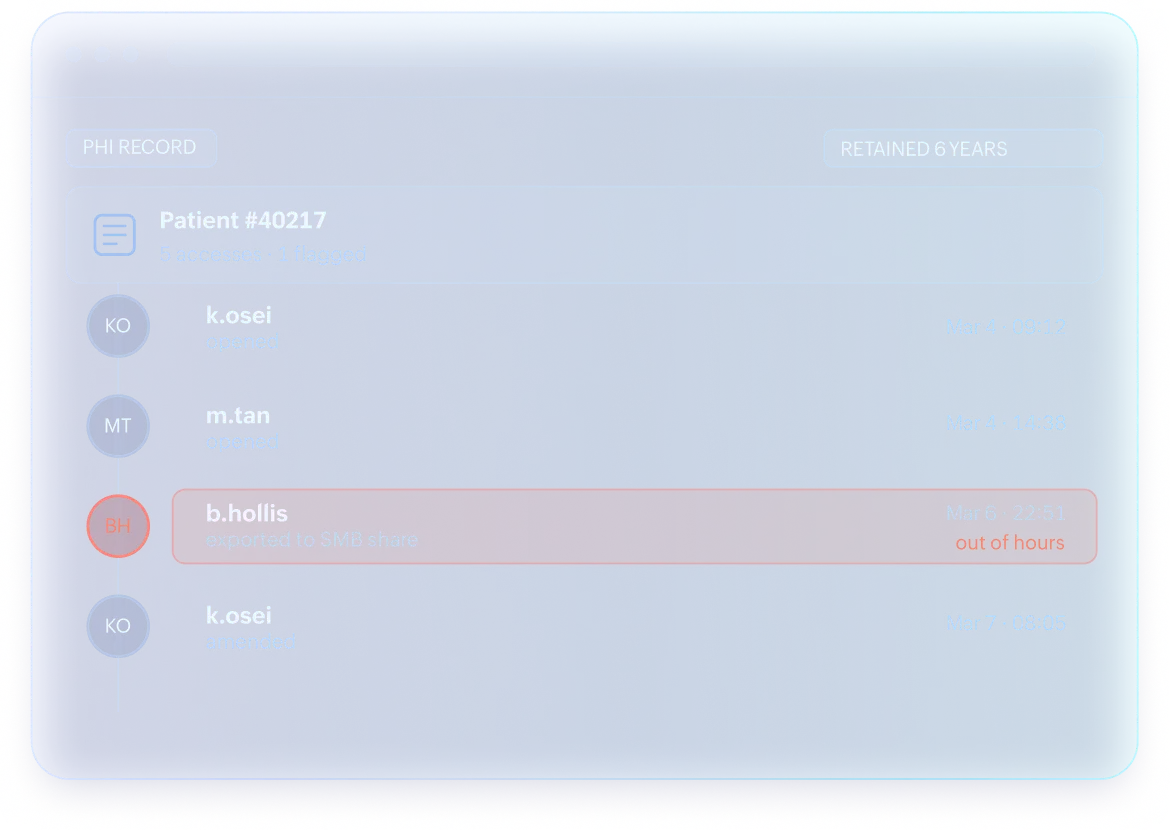
Every archive is encrypted, hashed, and timestamped on creation, and a periodic integrity check re-verifies every file on a schedule. Pull the report and see tampering detected and reported—not prevented by wishful thinking.
PCI DSS 10.3 ISO 27001 A.5.33 NIST AU-9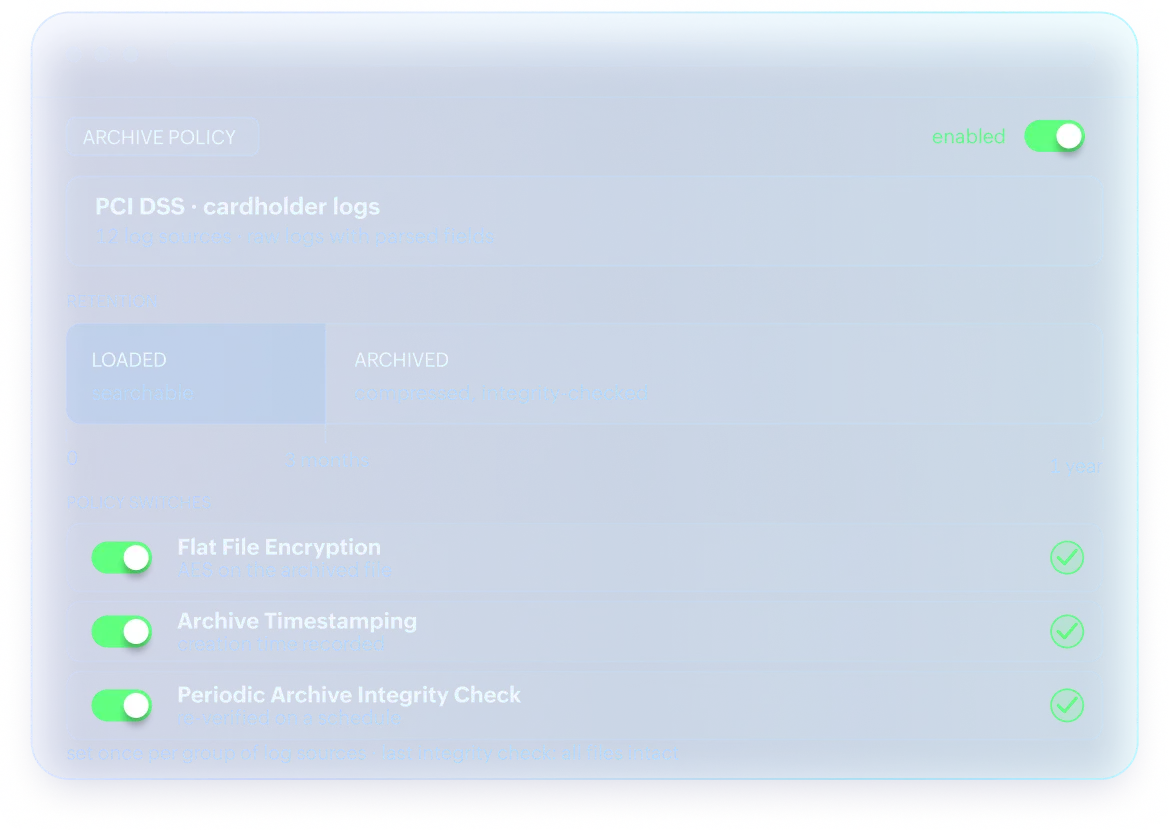
Open a tab per entity in the Incident Workbench—the user, the process, the external IP—for a side-by-side view. Let Zia write the summary while the SOAR playbook logs what was done.
NIS 2 Art. 23 DORA Art. 19 GDPR Art. 33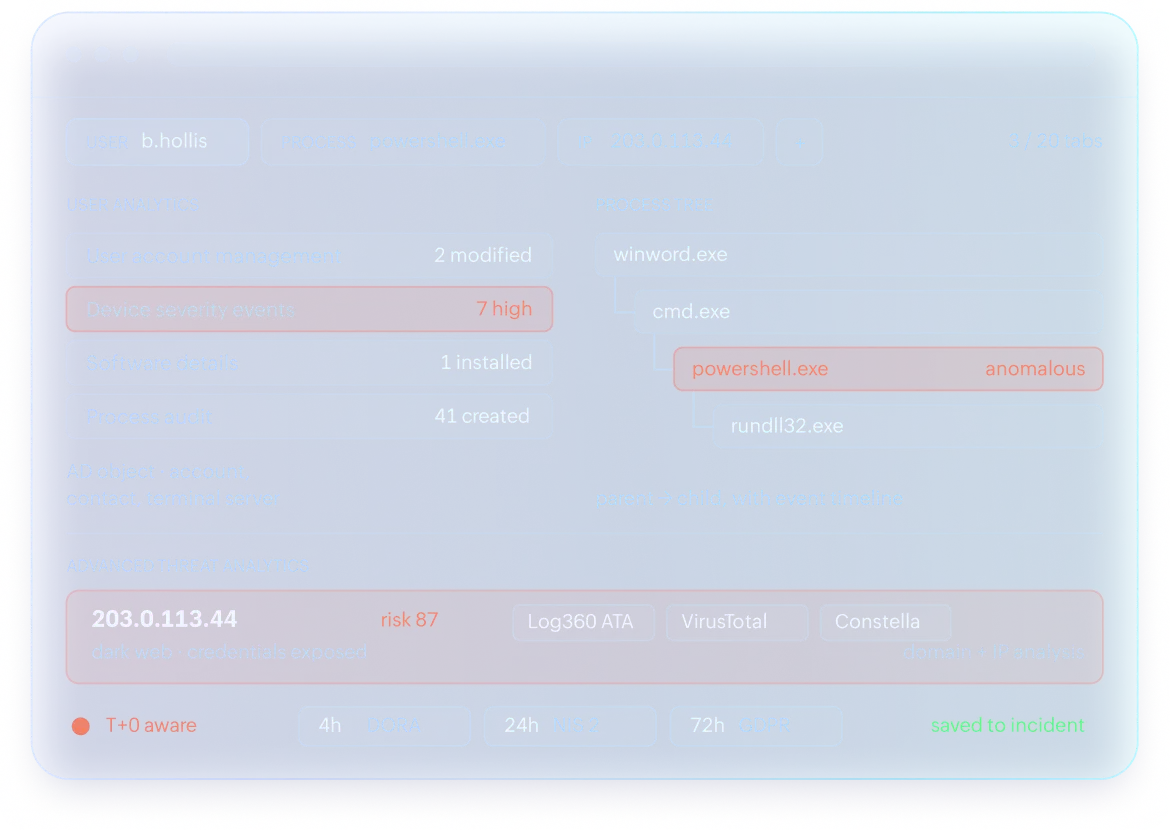
Group membership changes are tracked across AD and cloud directories. Skip the manual review—dormant privileged accounts surface on their own.
PCI DSS 7.2.4 ISO 27001 A.5.18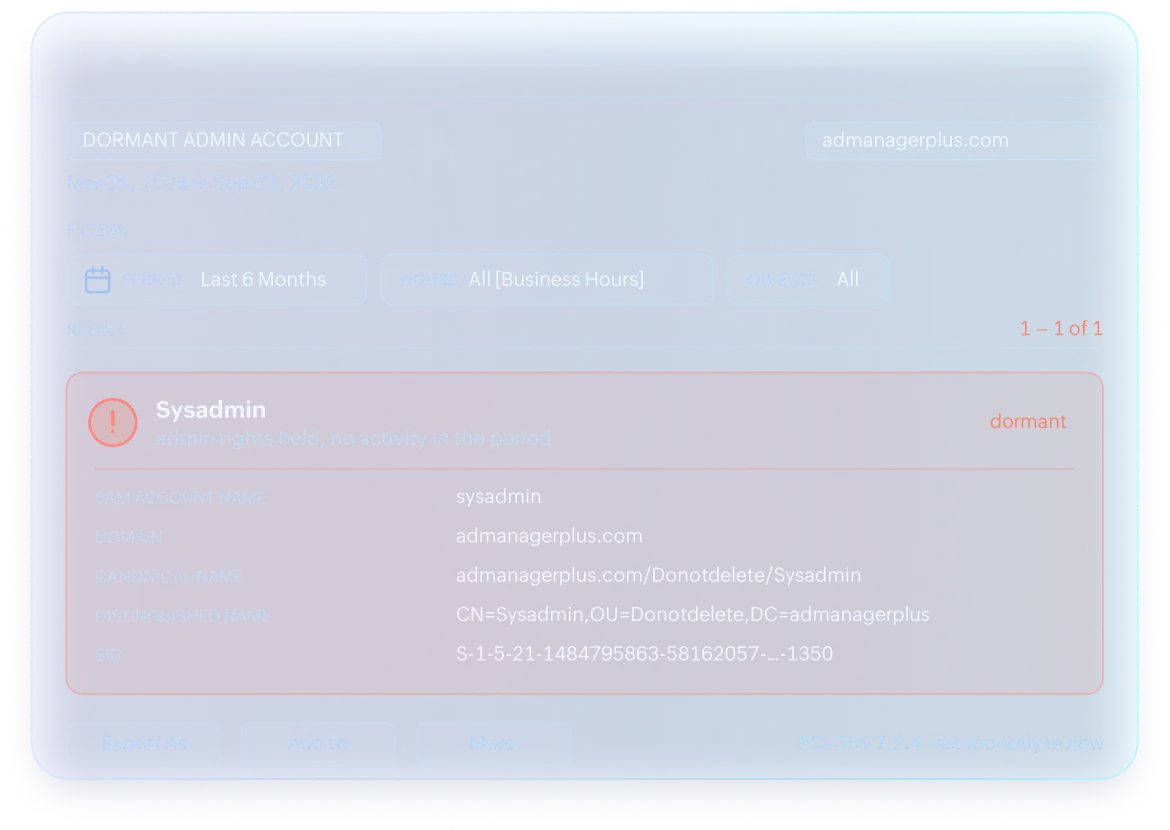
Collect the logs once, map them clause by clause, and answer every regulator from the same trail. Find yours by sector or by jurisdiction.
PHI access tracked across file servers, databases, and Microsoft 365.
Requirement 10 evidence, SOX change trails, and DORA incident timelines.
NIST-mapped controls with privileged activity watched continuously.
Multi-jurisdictional obligations answered from a single console.
Each extension ships predefined reports, alert profiles, and dashboards.
Six Log360 customers across healthcare, retail, manufacturing, and consumer services, each with a named framework.

The 2013–2022 revision put far more weight on cloud security controls. Vibrant Screen evaluated IBM QRadar, chose Log360 Cloud, then had its log-collection architecture designed around a policy that forbade open FTP ports.

More than 80 convenience stores means constant card transactions and one of the strictest mandates going. The earlier tools handled logs but fell short on compliance management; the prebuilt PCI DSS audit report turned demonstrating adherence into a filter-and-generate job.

“It’s easier to tell if someone’s trying to get in when they shouldn’t be.”
A 25-bed critical access hospital in Florida, with IT run on limited support. AD changes, user logons, and Microsoft 365 activity now land in one console, with alerts on out-of-hours access. Rated 9 out of 10.

Mitsubishi Elevator Europe · Manufacturing, Netherlands

MedCode Services · Healthcare IT, India

ThermOmegaTech · Manufacturing, US
Not the week the auditor books the meeting.

