With annual billing, Datadog Cloud SIEM is priced at $5 per million events analyzed. Your overall bill can also include additional costs for log ingestion, storage, and separately billed Workflow Automation, depending on how you use the platform.
Log360 Cloud is a powerful alternative to Datadog Cloud SIEM, bringing security information and event management (SIEM), user and entity behavior analytics (UEBA), security orchestration, automation, and response (SOAR), compliance, and log management together in a single security platform to help teams detect, investigate, and respond to threats across their entire IT environment.
Recognized by independent review platforms and analyst firms
| Capability | Log360 Cloud | Datadog Cloud SIEM |
|---|---|---|
| Out-of-the-box detection content | 2,000+ prebuilt rules—covering correlation, anomaly matching, and threat-intelligence matching—pre-tagged to MITRE ATT&CK at the sub-technique level. | Out-of-the-box rules maintained by Datadog's Security Research team and delivered with Content Packs. |
| Dark web monitoring | Integrated dark web monitoring using the Constella Intelligence feed to surface exposed credentials. | Requires integration with a third-party tool to perform dark web monitoring. |
| Insider threat detection | Logon anomalies, compromised accounts, privilege misuse, data exfiltration patterns, and prebuilt behavioral indicators. | Achievable through custom detection rules, entity risk scoring, and behavioral analytics. |
| Prebuilt regulatory reporting | Comes with 1,000+ ready-to-use compliance reports covering the PCI DSS, HIPAA, SOX, FISMA, the GLBA, ISO 27001, the GDPR, and the GPG 13. Reports are auditor formatted and can be scheduled or exported in PDF and CSV formats. | Takes a more build-your-own approach to compliance reporting. Teams can use dashboards, saved queries, and scheduled exports to compile compliance evidence, but there is no comparable library of pre-formatted audit reports. |
| Capability | Log360 Cloud | Datadog Cloud SIEM |
|---|---|---|
| Threat detection | ||
| Out-of-the-box detection content | 2,000+ prebuilt rules—covering correlation, anomaly matching, and threat-intelligence matching—pre-tagged to MITRE ATT&CK at the sub-technique level. | Out-of-the-box rules maintained by Datadog's Security Research team and delivered with Content Packs. |
| Detection methods | Standard correlation rules, machine learning (ML)-adapted anomaly rules, advanced multi-stage correlation, and threat-intel matches. | Threshold, new value, anomaly, anomaly threshold, impossible travel, sequence detection, and third-party alert ingestion. |
| Rule authoring and tuning | Visual builder with no SPL, KQL, or scripting. Apply exclusions at the user, group, OU, or device level, with guided tuning recommendations for your noisiest rules. | Code-free rule editor plus Datadog search syntax; detections can be managed as code through the API and Terraform. |
| Log360 Cloud comes out ahead for teams looking at the full detection workflow, with extensive prebuilt coverage, multiple ways to detect threats, and practical rule tuning built for security analysts. Datadog offers solid detection capabilities too, but leans more toward teams that want to build and manage detections through its search syntax and code-driven workflows. | ||
| Explore more | ||
| Threat intelligence | ||
| Built-in feeds | Threat-intel database of 600M+ malicious URLs, domains, and IPs; STIX/TAXII, VirusTotal, AlienVault OTX, and Webroot BrightCloud reputation scoring. | Built-in threat intelligence plus custom indicator of compromise (IoC) enrichment through reference tables. |
| Dark web monitoring | Integrated dark web monitoring using the Constella Intelligence feed to surface exposed credentials. | Requires integration with a third-party tool to perform dark web monitoring. |
| Log360 Cloud has the stronger threat intelligence story for teams that want more built into their SIEM software, with broad malicious-IoC coverage and dark web monitoring included. Datadog offers solid threat intelligence and supports bringing in your own feeds, but teams looking for dark web visibility or a more complete intelligence layer may need additional integrations. | ||
| Explore more | ||
| UEBA and behavioral analytics | ||
| UEBA | Dedicated ML-based UEBA module with time, count, and pattern anomaly detection, plus integrated risk scoring for users and entities. | Entity risk scoring, risk-based entity views, and anomaly and impossible travel detection provide comprehensive behavioral coverage. |
| Insider threat detection | Logon anomalies, compromised accounts, privilege misuse, data exfiltration patterns, and prebuilt behavioral indicators. | Achievable through custom detection rules, entity risk scoring, and behavioral analytics. |
| Explore more | ||
| Investigation and AI | ||
| Investigation workspace | Incident Workbench with threat-intel context plus UEBA signals rolled into chronological event views and process-lineage trees. | Signals Explorer for searching and analyzing security signals, Investigator for tracing related activity across timelines, and Work Management for assigning and tracking investigations. |
| AI assistance | Zia Insights summarizes events and maps them to MITRE techniques; the Alert Investigation Agent runs autonomous multi-stage investigations and reconstructs attack timelines; Ask Zia handles natural-language search and Zia Agents covers no-code agents. | Datadog's Bits AI natural-language search and Datadog's AI agents, charged separately through AI Credits. |
| AI billing | AI capabilities are included with the Enterprise edition, with no separate AI charge. | AI Credits are billed separately at $500 for 500 credits per month on annual billing, or $1.30 per credit on demand. |
| MCP integration | Supports MCP integration through the Enterprise edition, allowing external AI clients to connect with Log360 Cloud data and security workflows. | Offers a native MCP Server that connects AI clients directly to the Datadog platform, giving them access to platform data and capabilities. |
| Log360 Cloud has the stronger value proposition for teams that want AI built into the investigation process without adding another line item for AI usage. | ||
| It brings investigation and AI together in one workspace, giving analysts threat context, UEBA signals, event timelines, and process lineage in a single view. Its AI capabilities go beyond summarizing alerts, helping investigate incidents, reconstruct attack timelines, and explore security data using plain language. | ||
| Explore more | ||
| SOAR and automation | ||
| Native automation | Native SOAR is available in the Enterprise edition, with a drag-and-drop playbook designer and ready-to-use playbooks for common security tools such as CrowdStrike Falcon, Bitdefender, Sophos Central, Cisco Duo, and VirusTotal. | Provides Workflow Automation with reusable security blueprints and App Builder, while additional SOAR workflows are available through Content Packs. |
| Custom logic | Supports custom functions in Python and Deluge that can be reused across playbooks, making it easier to build automation around specific security workflows. | Supports custom workflow steps along with more than 1,750 prebuilt actions. App Builder is also available for teams that need to create custom applications, at $35 per app per month. |
| Custom playbook automation | Automation is included with the Enterprise edition, with no additional charge for individual playbook executions. | Workflow Automation starts at $10 for 100 executions per month with annual billing, working out to about $0.10 per execution. Both successful and failed executions count toward the usage limit. App Builder is priced separately. |
| Log360 Cloud gives security teams a straightforward path from detection to response, with native SOAR capabilities, ready-to-use playbooks, and support for custom Python and Deluge functions. Automation is included in the Enterprise edition, so teams can build and run response workflows without paying separately for each playbook execution. | ||
| Explore more | ||
| Compliance and audit | ||
| Prebuilt regulatory reporting | Comes with 1,000+ ready-to-use compliance reports covering the PCI DSS, HIPAA, SOX, FISMA, the GLBA, ISO 27001, the GDPR, and the GPG 13. Reports are auditor formatted and can be scheduled or exported in PDF and CSV formats. | Takes a more build-your-own approach to compliance reporting. Teams can use dashboards, saved queries, and scheduled exports to compile compliance evidence, but there is no comparable library of pre-formatted audit reports. |
| Continuous compliance monitoring | Provides dedicated compliance dashboards that continuously track activity against specific requirements, flag violations, and show where an event maps to a particular compliance clause. | Offers compliance monitoring through Cloud Security, with support for 15+ industry benchmarks such as the CIS, the PCI DSS, and SOC 2. Its approach is primarily focused on cloud security posture rather than ongoing, log-based compliance monitoring. |
| Platform certifications | Covers a broad set of security and service management standards, including ISO/IEC 27001, 27017, and 27018, SOC 1 and SOC 2, SOC 2 + HIPAA, and ISO 9001:2015. | Holds certifications and attestations including SOC 2, ISO 27001, CSA STAR, PCI DSS Level 1 Service Provider for Log Management and APM, and FedRAMP authorization for eligible government environments. |
| Identity and AD audit trail | Goes beyond collecting Windows and AD logs, with dedicated auditing for authentication events, OU and GPO changes, permission changes, account lockouts, and privileged user activity. | Can collect and search Windows Event Logs and AD data, but the auditing experience is focused on log analysis rather than a dedicated AD change auditing and reporting layer. |
| File server auditing | Provides dedicated file server auditing for file and folder access, modifications, deletions, and other changes, giving administrators a clear record of who accessed or changed sensitive files. | File integrity monitoring is available through Workload Protection and DevSecOps Enterprise. |
| Explore more -> | ||
| Deployment and tenancy | ||
| Deployment models | Offers cloud, on-premises, and MSSP deployment options across the Log360 product family, so organizations can choose the setup that best fits their infrastructure and security requirements. | Delivered as a SaaS platform, while supporting components such as the Agent and Observability Pipelines can run on-premises for local data collection and processing. The SIEM software itself remains cloud hosted. |
| Multi-tenancy for service providers | Provides a dedicated MSSP edition with per-tenant licensing and monthly billing, making it suited to service providers managing multiple customer environments from a single platform. | Supports MSPs through a parent-and-child organization model, with each customer managed in a separate child organization for data, users, and billing isolation. The multi-organization setup must be enabled by Datadog Support. |
| Log360 Cloud is the stronger fit for organizations that need deployment flexibility or purpose-built multi-tenancy, while Datadog is better suited to teams committed to a cloud-native SaaS model. | ||
| Commercial model | ||
| Primary unit of cost | Component-based licensing. You pay according to the number of log sources, domain controllers, file servers, cloud accounts, and endpoints you need to cover, with storage purchased separately. | Usage-based pricing. Cloud SIEM is charged per million events analyzed, on top of Datadog's separate log ingestion and storage costs. |
| Pricing structure | Starts at $1,095 per year for 10 log sources with the Professional edition, or $1,395 per year for Enterprise edition. Other components such as domain controllers, file servers, cloud accounts, and endpoints have their own pricing bands. | Cloud SIEM starts at $5 per million analyzed events per month with annual billing, $6 month-to-month billing, or $7.50 for on-demand billing. This is the SIEM analysis charge and does not include the underlying log ingestion and retention costs. |
| What else is metered | Search storage is $10/GB/year for Professional edition and $13/GB/year for Enterprise edition. Archival storage is $0.25/GB/year, while each GB of search storage also includes three times that amount in archival storage. | Log ingestion is $0.10/GB. Indexed log storage is charged separately based on retention, from $1.06 per million events for 3 days to $2.50 for 30 days on annual billing. Flex Logs storage starts at $0.05 per million events. Workflow Automation, AI Credits, and certain security products are also separately metered. |
| Behavior during a spike | A temporary increase in log volume does not change the underlying component license. The cost impact comes from the additional storage required to retain those logs. | Datadog allows usage to exceed the committed log volume, but the excess is charged at 150% of the annual committed rate. The 50% premium applies to the volume above the commitment, rather than changing the entire month's rate. |
Datadog's usage-based model can make historical investigations an additional cost event. When analysts need to bring archived logs back for investigation, rehydration is charged at $0.10 per compressed GB scanned, plus the contracted indexing rate for matching events.
That means an incident investigation can create an additional bill just when analysts need to dig deeper into historical activity.
With Log360 Cloud, three times as much archival storage is included for every GB of search storage, and archived logs can be reloaded for investigation without affecting the existing search-storage allocation. This gives security teams more predictable costs when they need to investigate what happened months ago.
We have received your request for a personalized demo and will contact you shortly.
With Datadog, security data is metered at multiple points: Log ingestion, indexing or retention, SIEM analysis, and workflow automation each come with their own usage-based charges.
Log360 Cloud keeps the licensing model simpler. You license the components and assets you need to monitor, then add storage as your retention requirements grow.
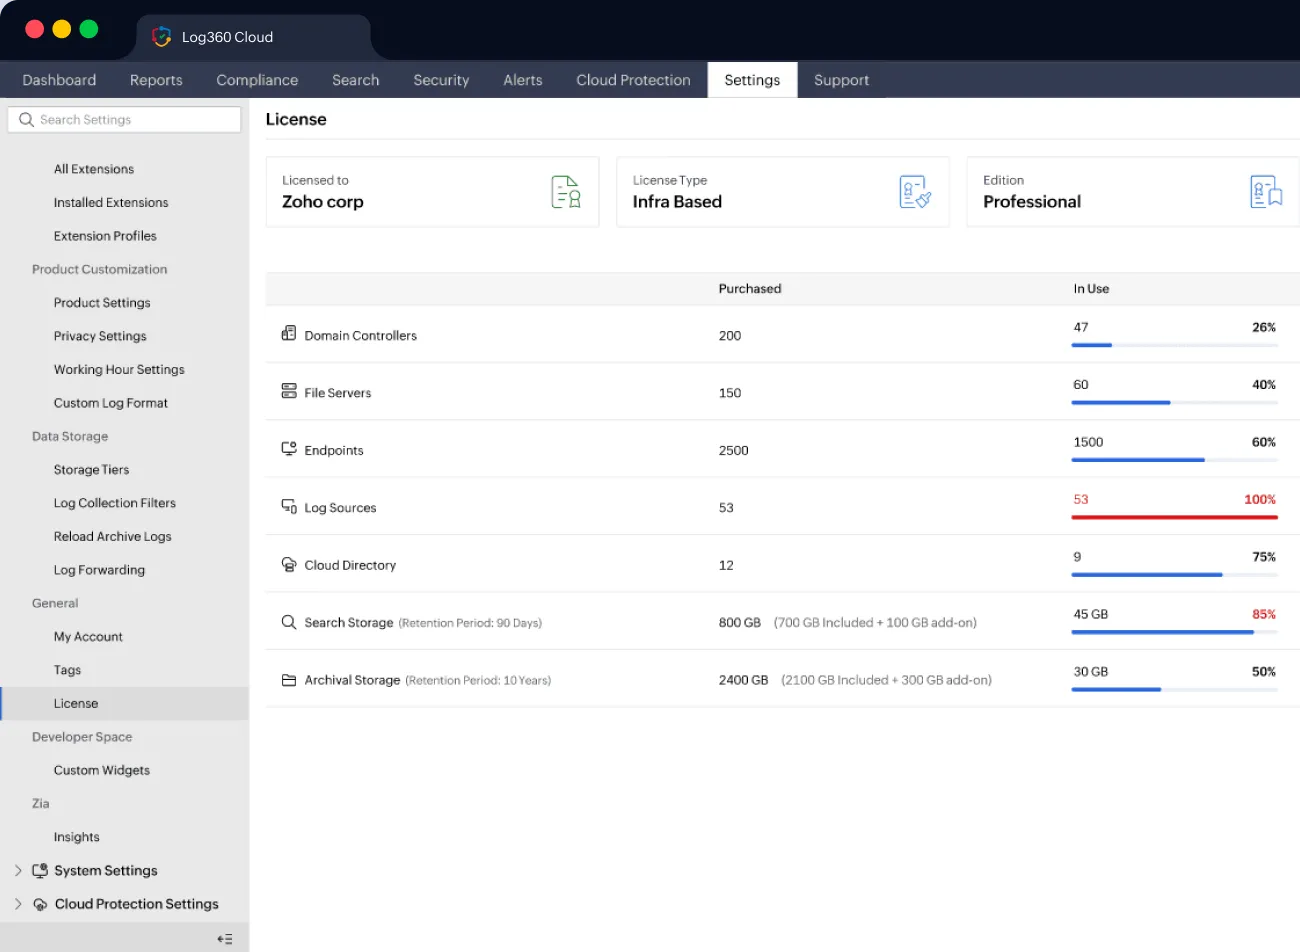
Log360 Cloud is built around security operations from the ground up. It comes with 2,000+ MITRE ATT&CK-mapped detection rules, UEBA with risk scoring for users and entities, native SOAR, and deep Active Directory (AD) and file-server auditing. It also brings prebuilt compliance and audit reporting into the same platform, so security teams can move from detection to investigation, response, and audit without stitching together separate tools.
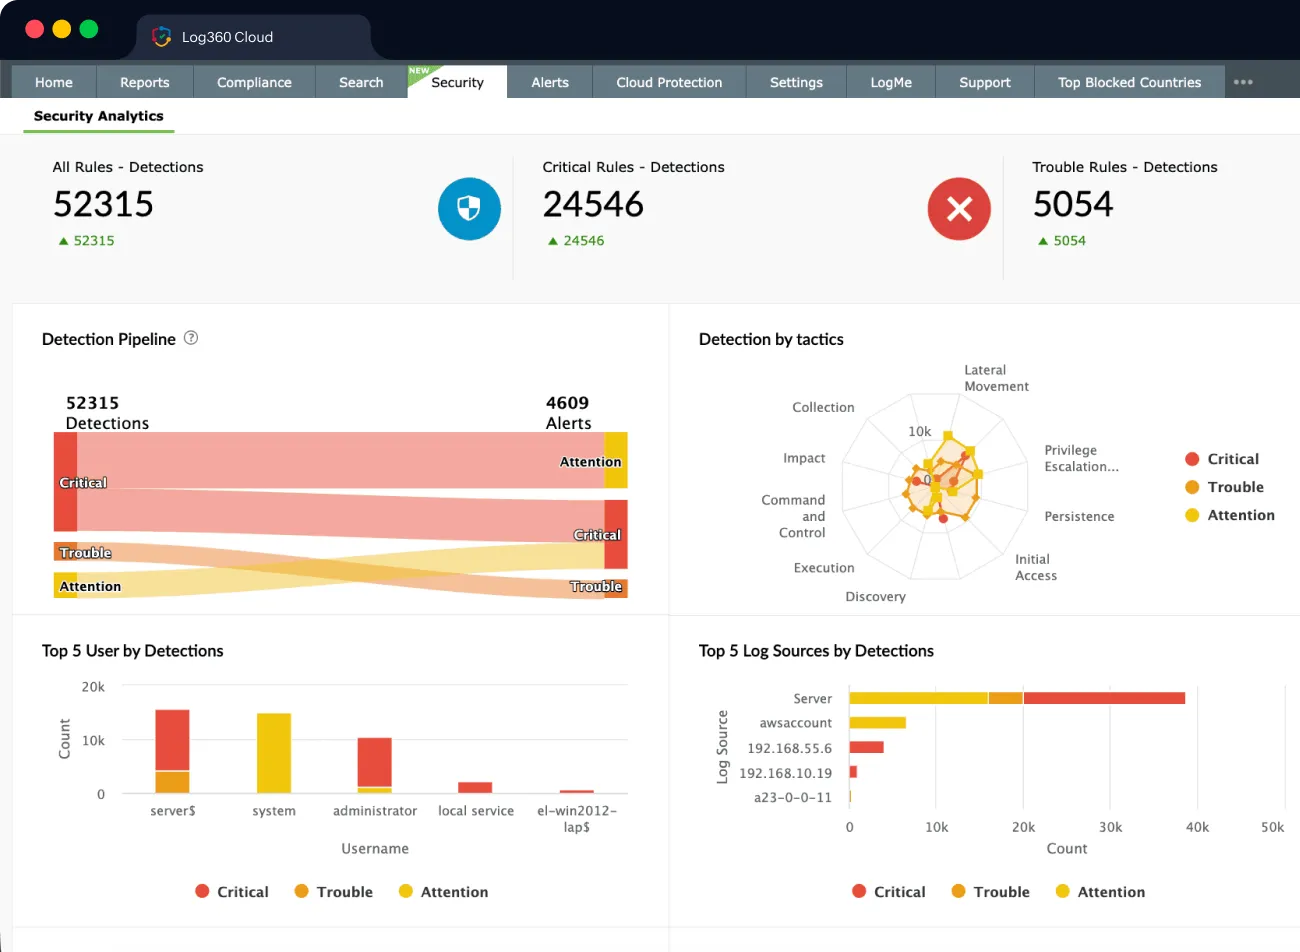
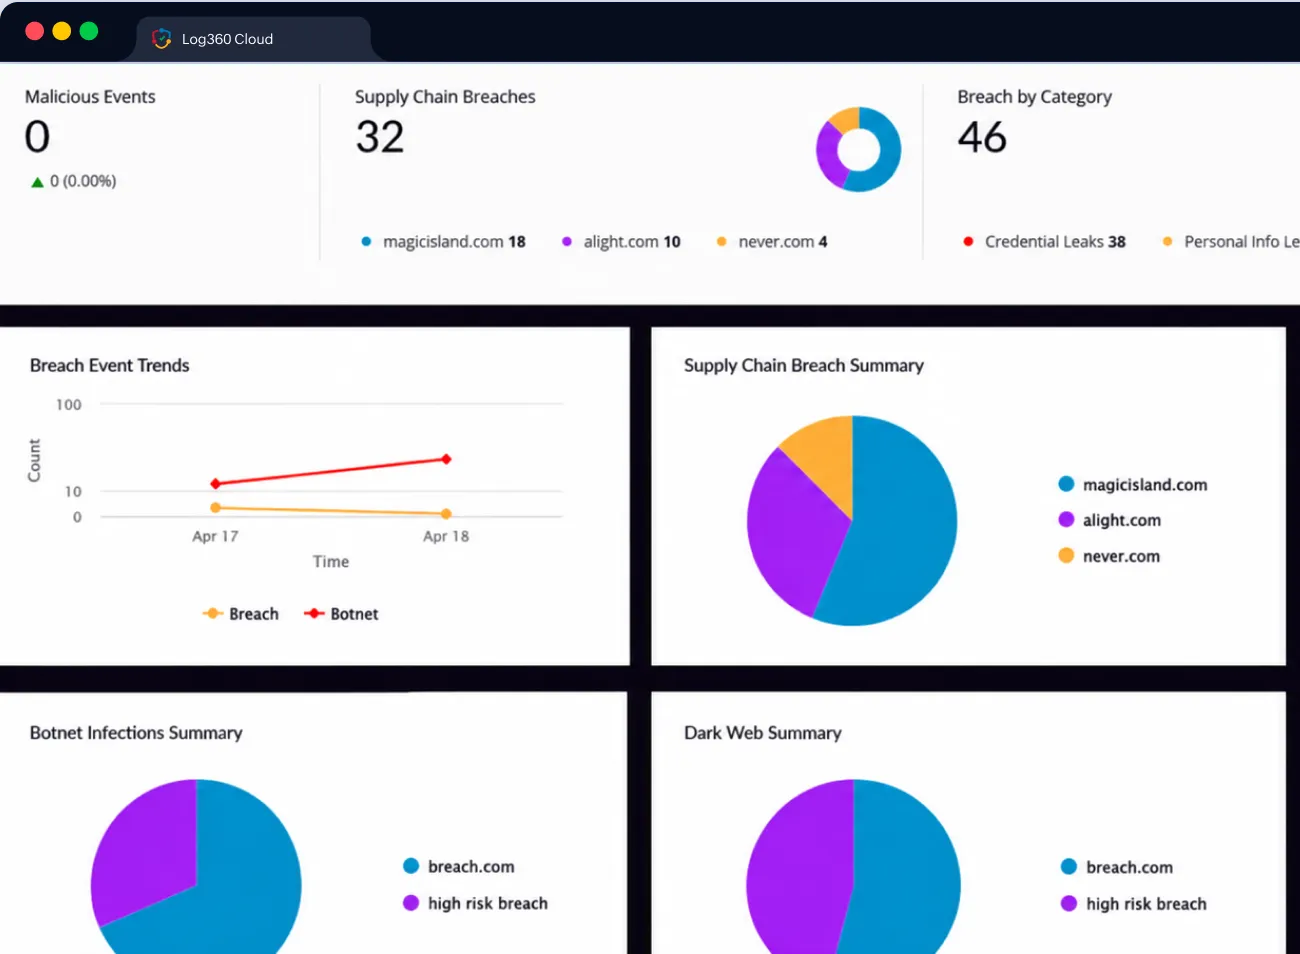
Datadog Cloud SIEM provides built-in threat intelligence and supports custom IoC enrichment, but you must integrate a third-party solution to get visibility into exposed credentials. Log360 Cloud's dark web monitoring, powered by the Constella Intelligence feed, surfaces exposed credentials, leaked PII, account takeover risks, and third-party data exposure directly in your SIEM console.
"We gained complete visibility into our server and security logs. The solution’s threat detection, event monitoring, and log analysis features have significantly improved how the organization tracks and responds to security events."
Dhanaraj K, Chief Information Security Officer, Vibrant Screen
Establishes behavioral baselines and identifies time, count, and pattern anomalies across users and entities, with dashboards showing risk levels, trends, and the activities contributing to the score.
Scan the deep and dark web to identify leaked PII and get notified of threats such as social engineering, account compromise, and third-party data exposures.
A library of ready-to-use playbooks covering integrations such as CrowdStrike Falcon, Bitdefender, Sophos Central, Cisco Duo, Okta, VirusTotal, Windows, and Linux, which can also be adapted and combined into larger workflows.
Zia Insights summarizes events and maps them to MITRE techniques, the Alert Investigation Agent runs autonomous multi-stage investigations, and the Zoho MCP Server lets AI clients such as Claude, Copilot, and Cursor query Log360 data.
More than 1,000 out-of-the-box reports covering security, operational, and compliance use cases, including HIPAA, SOX, FISMA, the PCI DSS, and the GDPR, with options to customize for specific requirements.
Available in both on-premises and cloud deployments. Log360 Cloud stores collected data in the regional data center associated with the selected location, helping you meet geographic and data residency requirements.
Get more security coverage in one platform with Log360 Cloud. Strengthen threat detection, speed up response, support compliance, and get better value than Datadog Cloud SIEM.
Your SIEM bill does not end with the license being purchased. How much data you collect and how long you need to keep it searchable or archived can have a real impact on your overall cost.
Use the Log360 Cloud storage calculator to get a practical estimate for your environment before you make a decision. It factors in the infrastructure you plan to monitor and your retention requirements, then shows how much storage you are likely to need.
Enter the number of log sources, endpoints, file servers, domain controllers, and cloud accounts you expect to monitor.
Set your Search and Archival retention periods based on your investigation and compliance needs. Search retention can be configured for up to three months, while archival retention can extend to 10 years.
The calculator estimates your Search and Archival storage requirements and shows how much is included with your Log360 Cloud subscription and whether you need additional storage.
License the components you want to monitor, then allocate Search and Archival Storage according to the retention each set of logs actually needs.
Moving to a new SIEM tool doesn't mean starting your security operations from scratch.
Your logs, security sources, and the use cases your SOC cares about are still the same. What changes is how that information and those use cases are configured and managed in the new platform.
The data sources you already monitor can continue to form the foundation of your security operations.
Windows, AD, Microsoft 365, AWS, Azure, firewalls, VPNs, DNS, endpoint security, and applications are all supported in Log360 Cloud, with 700+ log source integrations available.
If you rely on a custom application, you can also connect it through APIs rather than forcing it into a standard connector.
Datadog's detection rules, queries, suppressions, dashboards, and response workflows won't map directly to Log360 Cloud. Inventory critical detections, tuning settings, investigation dashboards, compliance reports, and response workflows.
Map them to Log360 Cloud's built-in capabilities, identify gaps that require custom rules or correlation logic, and recreate the necessary configurations and integrations. Validate critical use cases before completing the migration.
This depends on how much you've built around Datadog.
If you're mostly using standard integrations and out-of-the-box detection content, the transition is relatively straightforward. If you've accumulated hundreds of custom rules, dashboards, workflows, and third-party integrations, expect more time for mapping, configuration, and validation.
The easiest way to scope the move is to start with your critical use cases. Once you know what needs to stay, it's much easier to see what needs to be rebuilt, what can be configured differently, and what you don't need to carry over at all.
Get SIEM, UEBA, and SOAR in a single cloud solution built to eliminate complexity, accelerate response times, and secure your enterprise without hidden costs.
With annual billing, Datadog Cloud SIEM is priced at $5 per million events analyzed. Your overall bill can also include additional costs for log ingestion, storage, and separately billed Workflow Automation, depending on how you use the platform.
Log360 Cloud uses infrastructure-based licensing. You pay according to the log sources, domain controllers, file servers, cloud accounts, and endpoints you monitor, with search and archival storage available as separate add-ons.
Datadog Cloud SIEM cannot run as an on-premises SIEM deployment. Datadog Cloud SIEM is delivered as a cloud service, but it can collect telemetry from on-premises systems through the Datadog Agent and API-based integrations.
Datadog supports security automation through Workflow Automation, but it is a separately billed product. Published workflow executions are metered, with billing based on committed or on-demand executions. Log360 also includes SOAR capabilities in the Enterprise edition, with no additional charge for individual playbook executions.
Datadog Cloud SIEM retains security signals for 15 months, while searchable log retention depends on the selected Log Management plan. Log360 Cloud supports up to 90 days of Search retention, with Archival retention up to 10 years.
Log360 Cloud has a dedicated MSSP edition built for managing multiple customer environments, with centralized and segregated tenant views and support for up to 50 customers. That makes it the more purpose-built option for MSSPs.
ManageEngine is a division of Zoho Corp.