Securonix Unified Defense SIEM uses a GB/day pricing model across four packages: Basic, Standard, Advanced, and All-In. Pricing combines a committed capacity with pay-as-you-go usage and prenegotiated overage rates.
Securonix offers broad security analytics, but its tiered packaging and consumption-based pricing can complicate cost planning. ManageEngine Log360 Cloud combines SIEM, UEBA, threat detection, and compliance reporting with infrastructure-based licensing for more predictable budgeting.
Recognized by independent review platforms and analyst firms
| Particulars | Log360 Cloud | Securonix |
|---|---|---|
| AI assistance | Zia Insights summarizes logs, alerts, and incidents. The Alert Investigation Agent extracts entities, searches for related alerts and logs, builds an attack timeline, maps activity to ATT&CK, and recommends actions. Ask Zia supports natural-language queries, while Zia Agent Studio enables custom no-code agents. | Sam, the AI SOC analyst, automates and accelerates Tier 1 and Tier 2 work, such as triage, investigation, correlation, and response preparation. The Agentic Mesh coordinates specialized agents, with Agentic Guardrails governing their actions and human oversight. |
| MCP integration | The Zoho MCP Server lets compatible AI clients query Log360 data, investigate alerts, search logs, and perform supported actions through natural-language prompts. | Does not offer a native, dedicated MCP server. Integrating Securonix workflows with AI agents typically requires third-party integrations, security automation platforms, or centralized MCP gateways. |
| SOAR availability and licensing | Native SOAR is included in the Enterprise edition of Log360 Cloud, with no separate SOAR add-on or per-execution fee. | Includes SOAR Lite for routine automation, with playbooks of up to five steps. The All-In package includes full Securonix SOAR, alongside Autonomous Threat Sweeper and Securonix Investigate. |
| File server auditing | Provides file integrity monitoring for supported Windows file systems and NAS platforms, with predefined templates, alerts, and compliance-oriented reporting. | Does not offer a dedicated file integrity monitoring (FIM) module or packaged file server audit reporting comparable to Log360 Cloud's FIM capabilities. |
| Particulars | Log360 Cloud | Securonix |
|---|---|---|
| Log collection and data fidelity | ||
| Collection methods | Supports agent-based and agentless collection, syslog, and cloud or API integrations across several log sources. | Collects security telemetry from endpoints, networks, identities, cloud environments, and other sources through its data pipeline, agents, APIs, and integrations. |
| Parser maintenance | Provides predefined parsers for supported sources and supports custom parser rules for logs that need additional field extraction. | Uses platform parsing and normalization, with data onboarding and enrichment handled through its collection and data-pipeline architecture. |
| Custom applications | Collects custom application logs through syslog, file-based collection, or REST API integrations, with custom parser rules for extracting fields from log formats that lack a predefined parser. | Custom application logs can be ingested through the Data Pipeline using the configured collection source and parser. |
| Ingestion cost control | Log Collection Filters exclude selected events before they enter the platform. Storage Tiers then apply different retention policies to the log sources and categories assigned to each tier. | Data Pipeline Manager filters, classifies, and routes telemetry between Analytics, Investigation, and Basic tiers, allowing higher-priority data to receive more intensive analytics while lower-priority data is retained for other needs. |
| Threat detection and rule authoring | ||
| Detection content | Provides more than 2,000 predefined detection rules, continuously updated and maintained, covering insider threats, malware, external attacks, APT behavior, identity risks, anomalies, and correlation use cases. | Delivers threat models and analytics through Threat Labs' Threat Content as a Service approach. The models use security telemetry and curated threat intelligence to identify suspicious activity and emerging attack patterns. |
| Rule authoring | Provides a visual builder that enables security teams to create standard, anomaly, and advanced rules by configuring conditions, thresholds, filters, sequences, and exceptions without requiring extensive knowledge of a specific query language. | Analysts configure policies and threat models within the platform. Advanced searches and investigation queries require familiarity with Securonix's query and analytics workflows. |
| Explore more | ||
| UEBA and behavioral analytics | ||
| Behavioral analytics | Uses machine learning to establish baselines for users and entities and detect time-, count-, and pattern-based deviations from normal activity. | Establishes behavioral baselines, detects deviations in user and entity activity, and correlates related events into threat chains, using identity, asset, and threat context to prioritize risk. |
| Risk scoring | Assigns risk scores to anomalous users and entities. Dashboards show risk levels, trends, and contributing activity to help analysts prioritize investigations. | Uses dynamic risk scoring enriched with identity, asset, threat intelligence, and business context to prioritize users and entities requiring investigation. |
| Insider threat detection | Flags behavioral deviations associated with insider threats, such as unusual file access, suspicious permission changes, and activity outside established patterns. | Correlates behavioral changes, access patterns, data movement, and contextual signals to identify potential insider misuse and developing threats. |
| Custom anomaly detection | Allows administrators to configure custom anomaly rules and alert profiles to match their environment's monitoring requirements. | Enables creation and customization of behavior-based policies, alongside prebuilt threat models and use cases, to detect deviations from established behavioral baselines. |
| Explore more | ||
| Threat intelligence | ||
| Built-in intelligence | Maintains a threat intelligence repository of malicious IPs, domains, and URLs. Integrations with sources such as AlienVault OTX, VirusTotal, Webroot, and BrightCloud enrich security events with external indicator context. | Uses intelligence curated by Securonix Threat Labs in its detection content and analytics. Additional intelligence can be integrated through configured data sources and threat intelligence workflows. |
| Dark web monitoring | Integrates with Constella Intelligence to identify exposed credentials, personal information, financial information, and other compromised data associated with an organization. | Uses Threat Labs intelligence and ThreatQ to operationalize external threat intelligence. |
| Explore more | ||
| Investigation and AI | ||
| Investigation workspace | Incident Workbench brings incident timelines, affected entities, threat intelligence context, UEBA signals, and related security activity into one investigation view. | Securonix Investigate provides on-demand context and AI-assisted collaboration within the platform. |
| AI assistance | Zia Insights summarizes logs, alerts, and incidents. The Alert Investigation Agent extracts entities, searches for related alerts and logs, builds an attack timeline, maps activity to ATT&CK, and recommends actions. Ask Zia supports natural-language queries, while Zia Agent Studio enables custom no-code agents. | Sam, the AI SOC analyst, automates and accelerates Tier 1 and Tier 2 work, such as triage, investigation, correlation, and response preparation. The Agentic Mesh coordinates specialized agents, with Agentic Guardrails governing their actions and human oversight. |
| MCP integration | The Zoho MCP Server lets compatible AI clients query Log360 data, investigate alerts, search logs, and perform supported actions through natural-language prompts. | Does not offer a native, dedicated MCP server. Integrating Securonix workflows with AI agents typically requires third-party integrations, security automation platforms, or centralized MCP gateways. |
| SOAR and automation | ||
| SOAR availability and licensing | Native SOAR is included in the Enterprise edition of Log360 Cloud, with no separate SOAR add-on or per-execution fee. | Includes SOAR Lite for routine automation, with playbooks of up to five steps. The All-In package includes full Securonix SOAR, alongside Autonomous Threat Sweeper and Securonix Investigate. |
| SOAR architecture | Builds response workflows directly into the SIEM console, connecting alerts, investigations, and remediation playbooks in one platform. | Embeds SOAR into Unified Defense SIEM, integrating detection, investigation, and response workflows through a shared platform and analyst interface. |
| Prebuilt playbooks | Provides ready-to-import playbooks for common response tasks, including malware containment, credential compromise, and indicator-of-compromise enrichment. | Provides out-of-the-box playbooks for common security response scenarios, with integrations across endpoint, network, identity, email, and case management tools. |
| Playbook customization | Uses a visual builder with branching, parallel execution, wait, batch, and termination states. Custom functions can be written in Python or Deluge. | Uses a Playbook Designer to build workflows and combine automation tasks and integrations. SOAR Lite is limited to five steps per playbook; the full SOAR offering provides broader orchestration capabilities. |
| Explore more | ||
| Identity and file access auditing | ||
| AD auditing | Provides dedicated AD auditing for changes to users, computers, groups, organizational units, Group Policy Objects, and permissions, with audit reports and account lockout analysis. | Analyzes identity and directory events collected from connected sources for suspicious behavior, privilege misuse, and insider risk. |
| File server auditing | Provides file integrity monitoring for supported Windows file systems and NAS platforms, with predefined templates, alerts, and compliance-oriented reporting. | Does not offer a dedicated file integrity monitoring (FIM) module or packaged file server audit reporting comparable to Log360 Cloud's FIM capabilities. |
| Evidence gathering | Provides reports that help establish who changed a monitored setting or permission, when the change occurred, and what object was affected. | Can analyze collected change events as security telemetry. The depth of configuration-change reporting depends on the source data and configured analytics. |
| Compliance monitoring | ||
| Out-of-the-box compliance reports | Provides more than 1,000 reports overall, including compliance-oriented reporting for frameworks such as the PCI DSS, HIPAA, SOX, the GDPR, NIST's Cybersecurity Framework, and ISO 27001. | Provides compliance dashboards and reporting to support audit preparation, incident review, and security oversight, with reporting capabilities aligned to relevant regulatory and security frameworks. |
| Audit evidence and retention | Provides archival retention of up to 10 years, with archived logs reloadable into Search Storage for investigation or review. | Basic includes 90 days of hot storage and one year of cold storage according to published package information. Advanced and All-In include 365 days of hot storage. |
| Explore more | ||
| Retention and storage | ||
| Storage allocation model | Licenses Search Storage and Archival Storage separately. Search Storage is used for active investigation and analytics; Archival Storage retains logs for longer periods. | Uses package-based hot storage entitlements and Data Pipeline Manager (DPM) tiers for analytics, investigation, and cost-efficient retention. |
| Searchable retention | Supports a default 90-day Search Storage window, subject to the customer's licensed capacity and configured retention. Additional Search Storage can be purchased. | Basic and Standard include 90 days of hot storage; Advanced and All-In include 365 days of hot storage according to published package information. |
| Long-term retention | Supports archival retention of up to 10 years. For every gigabyte of Search Storage purchased, three times that capacity is provided as Archival Storage; archived logs can be reloaded for searching. | Basic includes one year of cold storage. Advanced and All-In provide 365 days of hot storage. |
| Deployment, data access, and multi-tenacy | ||
| Data ownership and deployment | Stores log data in the Log360 Cloud regional data center chosen by the customer. | Under Bring Your Own Snowflake and Bring Your Own AWS deployments, customers use their own cloud environment for the data plane while Securonix provides the application layer. |
| Deployment options | Available as a cloud SIEM solution or for on-premises deployment. | Offers fully managed SaaS with underlying infrastructure bundled into the subscription, as well as Bring Your Own Snowflake and Bring Your Own AWS deployment models. |
| Multi-tenacy | Offers a dedicated MSSP edition for managing multiple customer environments from a centralized console. | Provides multi-tenant deployment and centralized response workflows across tenants. |
We have received your request for a personalized demo and will contact you shortly.
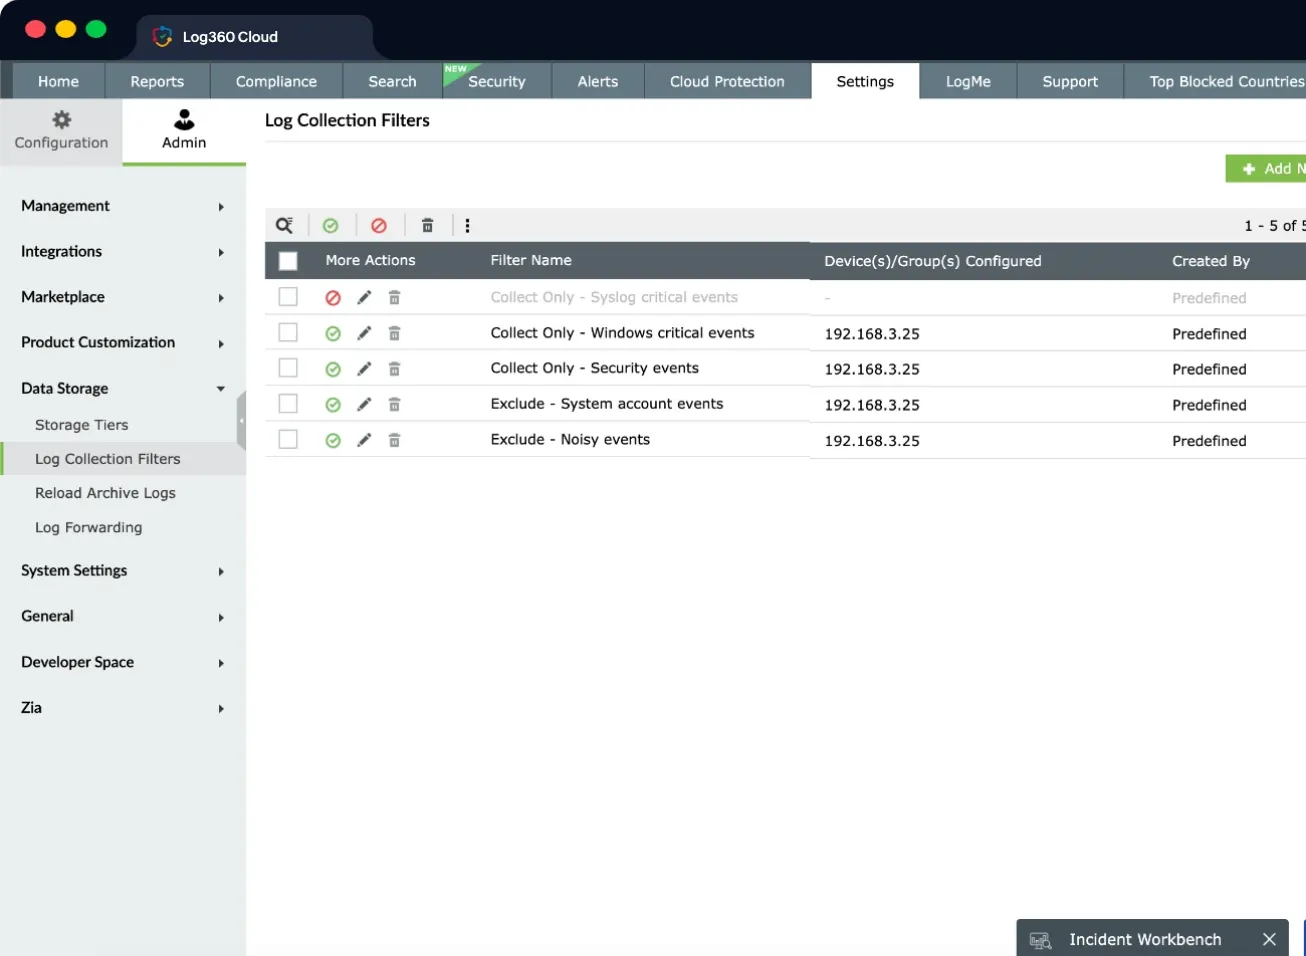
Log360 Cloud lets you configure collection filters to exclude unwanted events before they enter the platform. You can then assign different log sources to storage tiers, keeping important security records searchable for longer while archiving less frequently accessed data sooner.
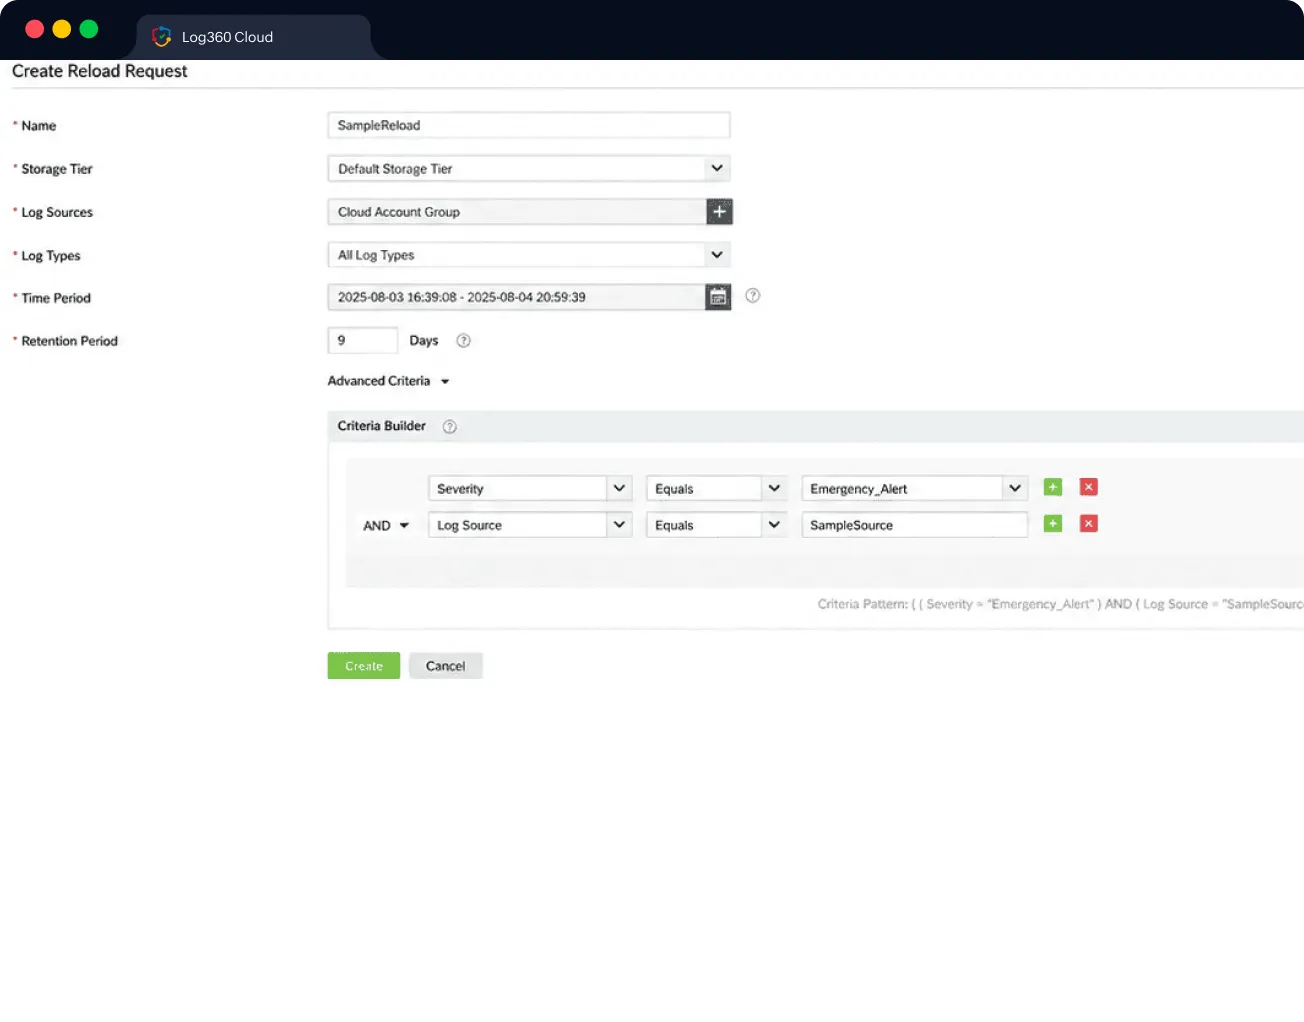
Log360 Cloud lets you reload archived logs into Search Storage when you need to investigate or report on historical activity. This allows you to retain evidence for longer periods without keeping all of it indexed for daily searches.
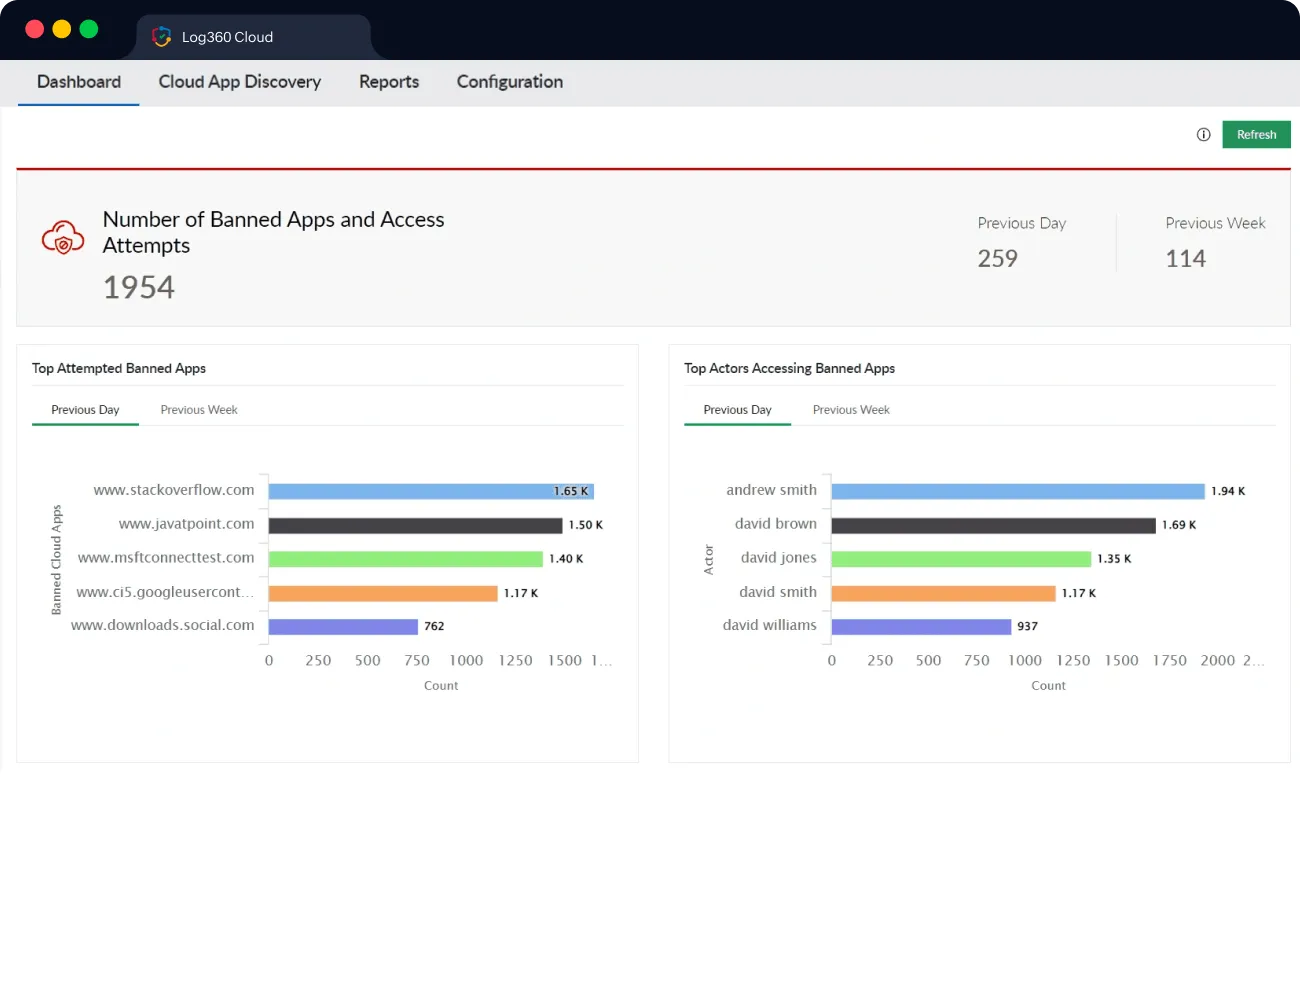
Log360 Cloud's cloud protection capabilities identify shadow applications, show which users access them, and provide visibility into sanctioned and unsanctioned app usage.
Establishes behavioral baselines and identifies time, count, and pattern anomalies across users and entities, with dashboards showing risk levels, trends, and the activities contributing to the score.
Scan the deep and dark web to identify leaked PII and get notified of threats such as social engineering, account compromise, and third-party data exposures.
A library of ready-to-use playbooks covering integrations such as CrowdStrike Falcon, Bitdefender, Sophos Central, Cisco Duo, Okta, VirusTotal, Windows, and Linux, which can also be adapted and combined into larger workflows.
Zia Insights summarizes events and maps them to MITRE techniques, the Alert Investigation Agent runs autonomous multi-stage investigations, and the Zoho MCP Server lets AI clients such as Claude, Copilot, and Cursor query Log360 data.
More than 1,000 out-of-the-box reports covering security, operational, and compliance use cases, including HIPAA, SOX, FISMA, the PCI DSS, and the GDPR, with options to customize for specific requirements.
Available in both on-premises and cloud deployments. Log360 Cloud stores collected data in the regional data center associated with the selected location, helping you meet geographic and data residency requirements.
Discover how a SIEM solution helps your organization get on top of emerging threats and enhance operational resilience.
Choosing the right SIEM tool means finding a solution that supports your security goals without slowing you down or complicating your workflow.
Query security data from your preferred AI tools using the Model Context Protocol (MCP). Bring Log360 Cloud insights into your existing AI workflows to investigate events, explore suspicious activity, and get answers using natural language.
Build, customize, and automate playbooks for incident response, integrating external tools and platforms to streamline security workflows.
Get detailed reports on activities across Exchange, Teams, SharePoint, OneDrive, and Microsoft Entra ID, expanding your detection pipeline with prebuilt detection rules targeting Microsoft-365-specific threats like brute-force attempts and excessive account lockouts.
"We gained complete visibility into our server and security logs. The solution’s threat detection, event monitoring, and log analysis features have significantly improved how the organization tracks and responds to security events."
Dhanaraj K, Chief Information Security Officer, Vibrant Screen
Get SIEM, UEBA, and SOAR in a single cloud solution built to eliminate complexity, accelerate response times, and secure your enterprise without hidden costs.
Securonix Unified Defense SIEM uses a GB/day pricing model across four packages: Basic, Standard, Advanced, and All-In. Pricing combines a committed capacity with pay-as-you-go usage and prenegotiated overage rates.
Log360 Cloud uses infrastructure-based licensing. You license the log sources, domain controllers, file servers, cloud accounts, and endpoints you want to monitor, with additional Search Storage and Archival Storage available as add-ons.
Securonix offers SOAR Lite for routine automation, with playbooks of up to five steps. Its All-In package includes full Securonix SOAR, along with Autonomous Threat Sweeper and Securonix Investigate. Log360 Cloud includes native SOAR in its Enterprise edition, with a visual playbook builder, more than 60 prebuilt playbooks, and custom functions written in Python or Deluge.
Log360 Cloud provides up to 90 days of searchable log retention and up to 10 years of archival retention. Archived logs can be reloaded into Search Storage for investigation. Securonix provides 90 days of hot storage with Basic and Standard and 365 days with Advanced and All-In, giving the higher packages a longer searchable retention window.
Not with the standard SaaS deployment, where the underlying infrastructure is bundled into the Securonix subscription. With Bring Your Own Snowflake or Bring Your Own AWS, you pay the cloud provider separately for the infrastructure used by the customer-managed data plane, in addition to the Securonix license. Log360 Cloud offers Search Storage and Archival Storage at published add-on rates within its pricing model.
ManageEngine is a division of Zoho Corp.