Moving objects in Active Directory is a routine part of keeping the directory organized: Relocating a user when they change departments, gathering decommissioned machines into a quarantine OU, or restructuring containers after a reorganization. Every move changes which OU holds the object, and with it, which Group Policy applies.
The Move-ADObject cmdlet in the PowerShell Active Directory module handles this for any object type, like users, computers, groups, and OUs, by pointing the object's distinguished name at a new target container. This guide covers three methods on how to move objects in Active Directory: Using the Move-ADObject cmdlet, the Active Directory Users and Computers (ADUC) console, and ADManager Plus, along with common error fixes you may face.
An Active Directory object is any entity the directory tracks, such as a user, computer, group, contact, or the OU, that contains them. OUs are the containers that hold those objects and give the directory its structure, typically arranged by department, location, or object type. Because Group Policy and delegated permissions are applied at the OU level, an object's OU determines both the policies it receives and who can control it.
Moving an object relocates it from one OU (the source) to another (the target). The object keeps its SID, group memberships, and attributes, but leaves behind the source OU's linked Group Policy and delegation, and picks up whatever applies at the destination. That policy shift, covered below, is the part worth thinking through before any move.
Before making any moves, make sure the following are in place:
Tools: The Active Directory PowerShell module must be available—it's installed with the Active Directory Domain Services (AD DS) role on a domain controller, or with the Remote Server Administration Tools (RSAT) on a Windows 10/11 Workstation.
Permissions: The account running the command needs delegated Write and Create/Delete rights on both the source and destination OUs. Being a member of the Domain Admins group provides these permissions.
Object identity: You'll need each object's distinguished name (DN) to reference it in the move command. You can retrieve the DN by querying the object in PowerShell or by viewing its properties in ADUC.
For the PowerShell method, import the Active Directory module and confirm that it is loaded:
									Import-Module ActiveDirectory

									Get-Module -Name ActiveDirectory
Every move needs the object's DN—its full LDAP path, such as CN=Jane Smith,OU=Sales,DC=corp,DC=com. The DN identifies the object and shows its current location in the directory. You can retrieve it using ADUC or PowerShell:
Get-ADUser -Identity jsmith | Select-Object Name, DistinguishedName
To move a computer object, use Get-ADComputer, optionally narrowing the search with -Filter and -SearchBase:
Get-ADComputer -Filter "Name -eq 'WKSTN-0421'" | Select-Object Name, DistinguishedName
With the source DN and the destination OU in hand, the move is a single command. Move-ADObject takes the object to move (-Identity) and the destination container (-TargetPath), both expressed as DNs.
Always preview first. The -WhatIf parameter reports what the command would do without changing anything. It's a cheap safety check that catches a mistyped DN before it moves the wrong object:
									Move-ADObject -Identity "CN=Jane Smith,OU=Sales,DC=corp,DC=com" `

									-TargetPath "OU=Marketing,DC=corp,DC=com" -WhatIf
When the preview looks right, run it for real by removing -WhatIf:
									Move-ADObject -Identity "CN=Jane Smith,OU=Sales,DC=corp,DC=com" `

									-TargetPath "OU=Marketing,DC=corp,DC=com"
A common hygiene task is cleaning up stale computer accounts that haven't logged in for an extended period and moving them to a quarantine OU for review before deletion. Get-ADComputer finds them by lastLogonDate, and the results are piped to Move-ADObject, which moves every returned account to the target OU in the same command. This example quarantines every computer inactive for more than 90 days:
									$cutoff = (Get-Date).AddDays(-90)

									Get-ADComputer -Filter 'LastLogonDate -lt $cutoff -and Enabled -eq $true' -Properties LastLogonDate |

									Move-ADObject -TargetPath "OU=Quarantine,DC=corp,DC=com" -WhatIf
Review the -WhatIf output, then remove the flag to execute. For a safer sequence, disable each stale computer account before moving it. A moved account keeps working but loses the Group Policy linked to its original OU, so a device still in use can slip out of management unnoticed. A disabled account can't authenticate to the domain, so if the machine is still needed, failed sign-ins surface it quickly, and you can re-enable it and move it back.
									$cutoff = (Get-Date).AddDays(-90)

									Get-ADComputer -Filter 'LastLogonDate -lt $cutoff -and Enabled -eq $true' -Properties LastLogonDate | ForEach-Object {

									Disable-ADAccount -Identity $_

									Move-ADObject -Identity $_ -TargetPath "OU=Quarantine,DC=corp,DC=com"

									}
The parameters below can be used with the Move-ADObject cmdlet.
| Parameter | Description |
|---|---|
| -Identity | The object to move, given as its DN, GUID, or SID |
| -TargetPath | The DN of the destination OU or container |
| -WhatIf | Previews the move without applying it: use it before every live run |
| -Confirm | Prompts for confirmation before the object is moved |
| -Server | Targets a specific domain controller on which to run the operation |
| -Credential | Runs the command as a different account with the necessary rights |
For a single move through the GUI, ADUC has a built-in Move command:
ADUC moves one object (or a multi-selected set) at a time, with no preview or logging. For large or repeatable moves, PowerShell or ADManager Plus is the better fit.
ADManager Plus is a web-based AD, Exchange, and Microsoft 365 management tool that moves single or multiple objects on a schedule from a point-and-click console, with no DNs to type and a full audit trail behind every action.
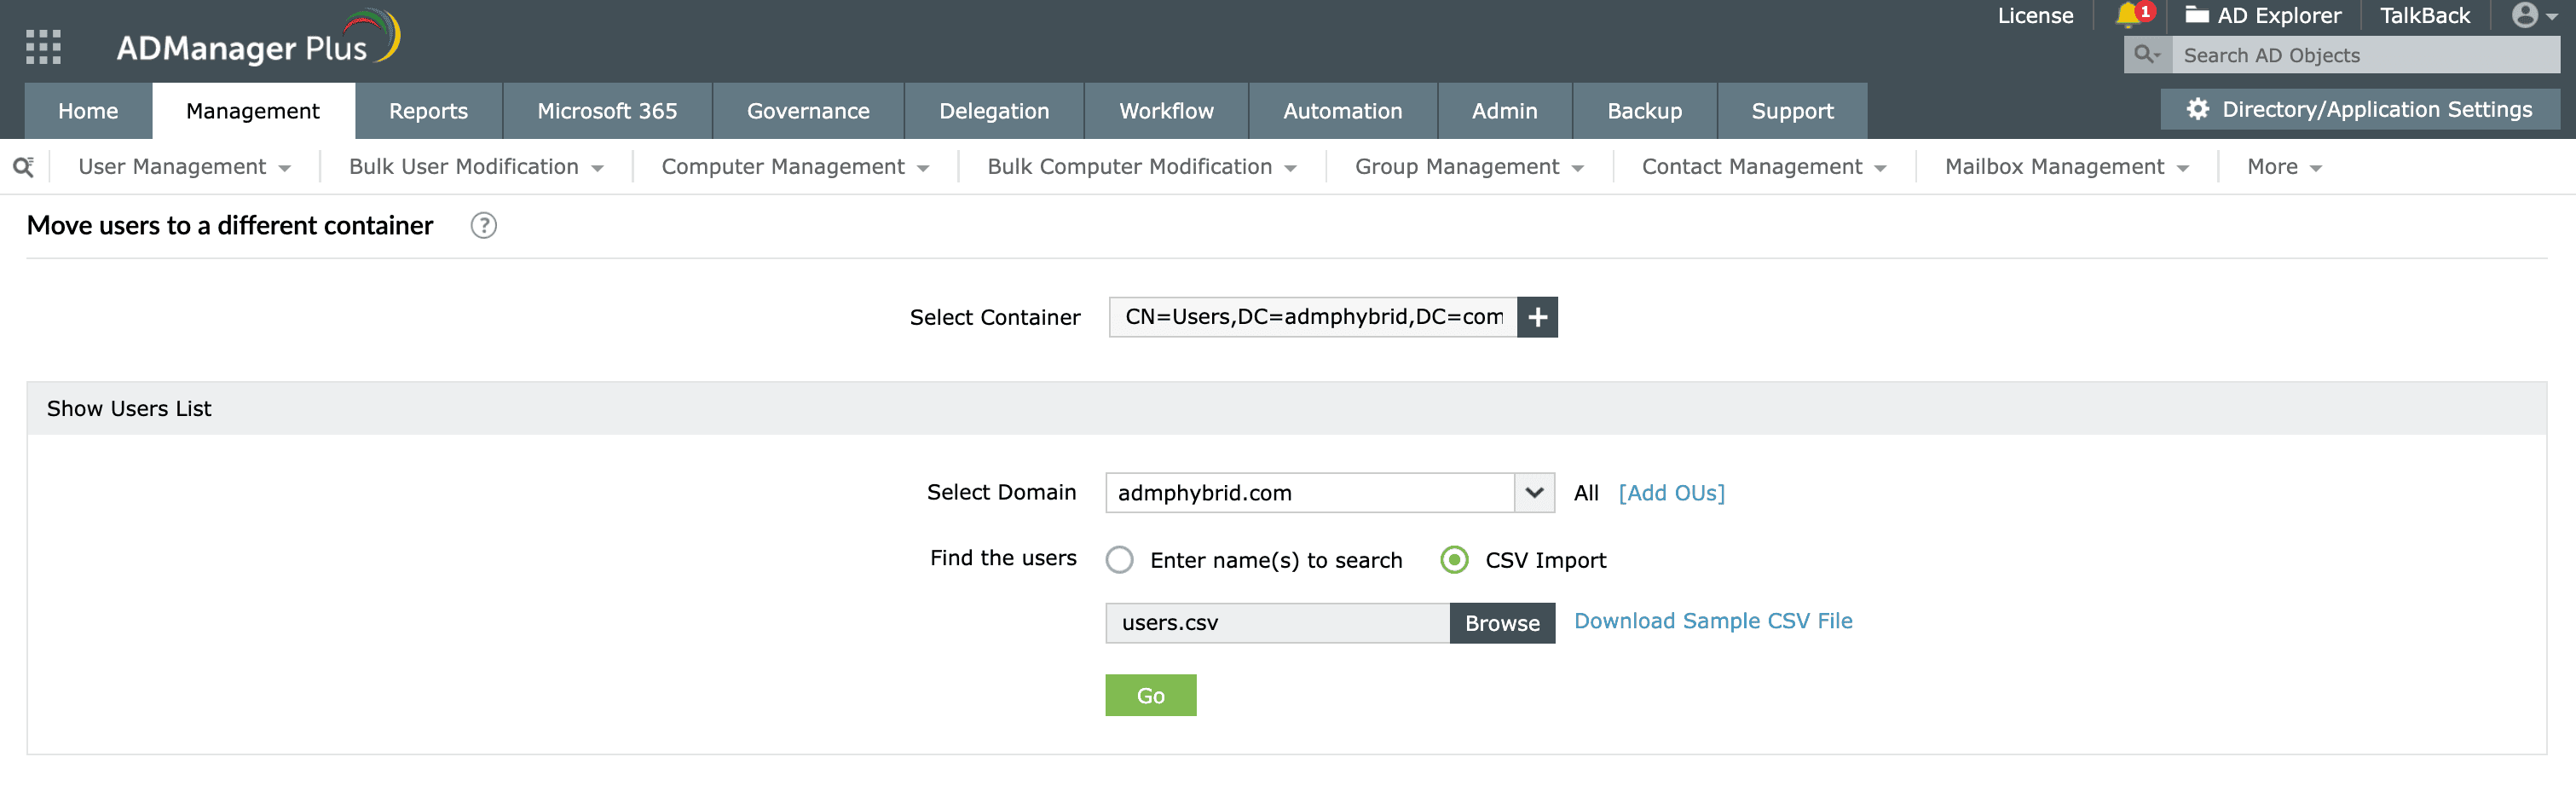
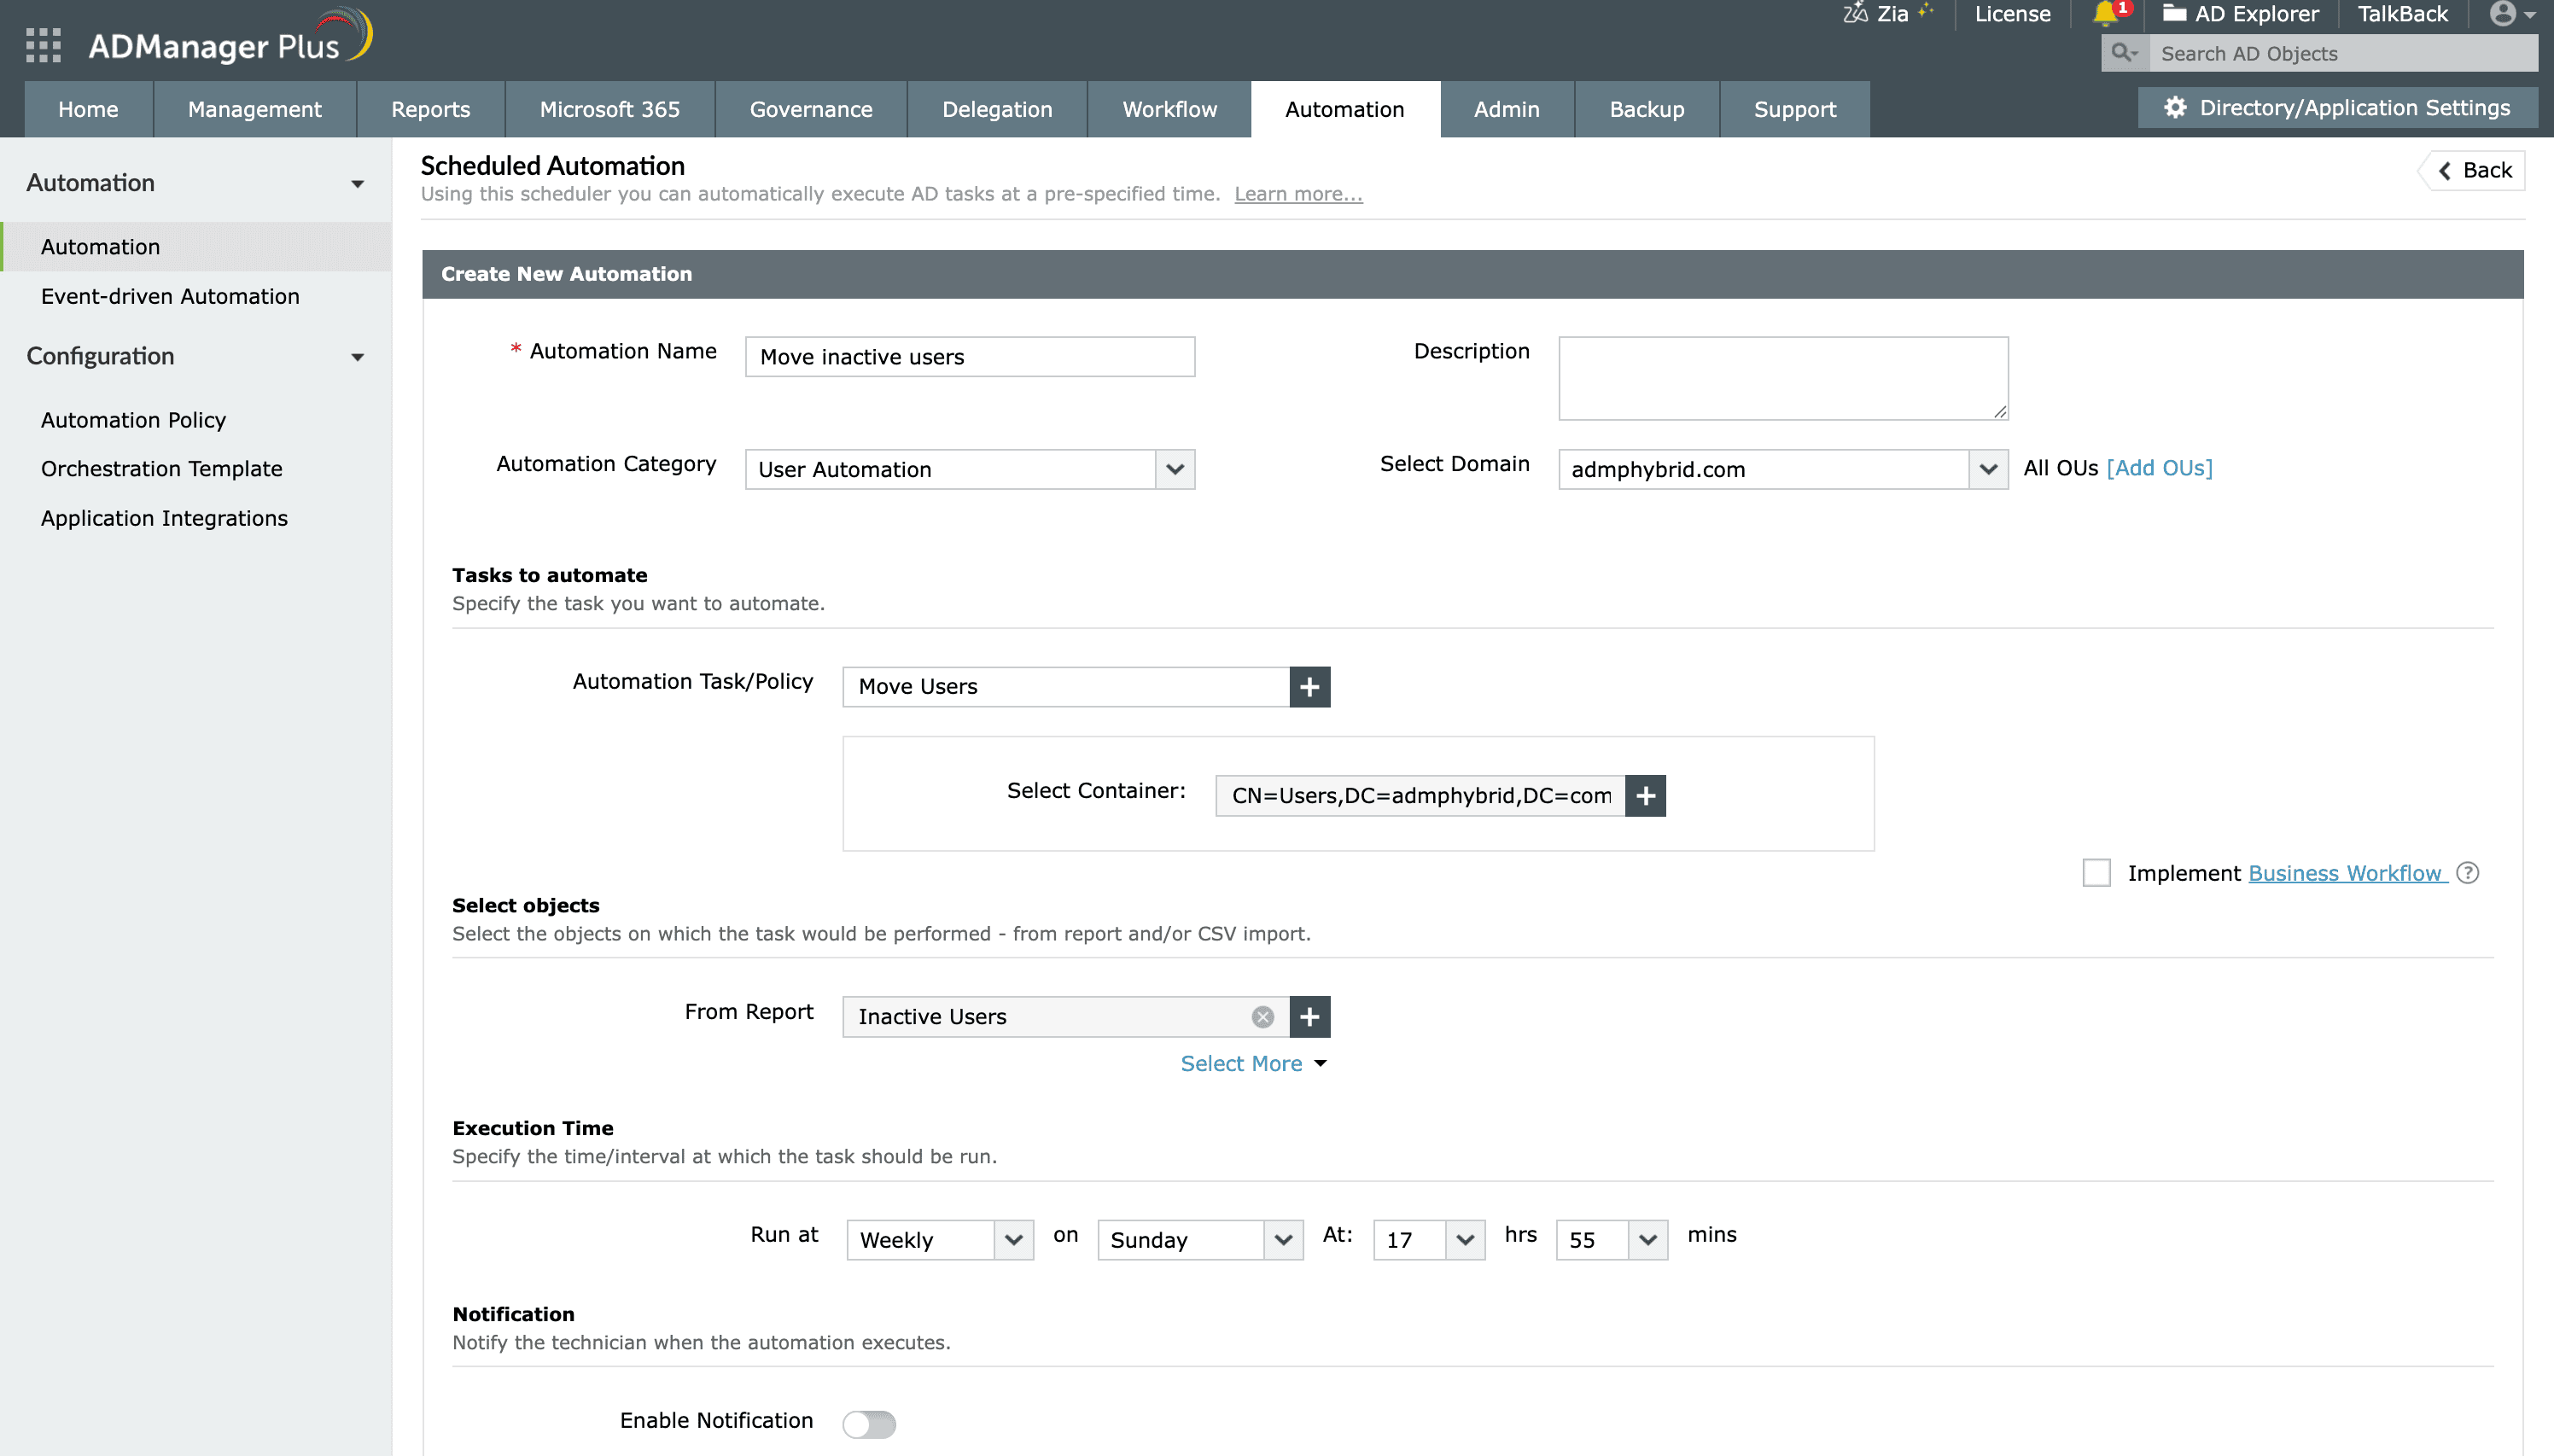
Rather than scheduling scripts, use ADManager Plus' Automation capability to run an inactive object report on a recurring basis and move the matches to a quarantine OU automatically. Chain it to a review-and-approve Workflow so a manager signs off on the move first, with notifications providing a record of who approved each change. This turns ad hoc cleanup into a repeatable, auditable process.
The moment an object lands in a new OU, the Group Policy it receives changes. It stops inheriting the GPOs linked to its old OU and immediately picks up those linked to the new OU and every parent above it in the hierarchy. Group Policy in Active Directory flows down the OU tree, so an object in a deeply nested OU inherits policy from that OU plus all its ancestors up to the domain root.
That has real consequences worth checking before a move: the object may gain stricter security settings, different software deployments, or drive mappings it didn't have. A workstation moved into a locked-down OU can suddenly enforce policies that block software the user needs; a user moved out of a department OU can lose mapped drives. Before moving objects in bulk, review which GPOs are linked to the destination OU and its parents, and confirm the resulting policy set is what you intend. Changes take effect at the next Group Policy refresh, or immediately with gpupdate /force on the affected machine.
Most move failures come down to permissions or protected objects. The common ones and their fixes:
The account running the move lacks rights on the source OU, the destination OU, or both. Moving requires Write and Create/Delete permissions on both containers. Verify the delegation-of-control settings on each OU, or run the command as a Domain Admin. Note that a per-object setting, Protect object from accidental deletion, also blocks moves. Clear it on the Object tab (with Advanced Features enabled) before retrying.
Domain controller computer accounts are meant to stay in the Domain Controllers OU. Moving them is strongly discouraged because it changes the security policy applied to the domain controller; if you must reorganize, use Group Policy linking rather than relocating the account.
The -Identity or -TargetPath DN is mistyped or the OU doesn't exist. Recheck the exact DN with Get-ADObject or Get-ADUser, and confirm the target OU's path. Running with -WhatIf first surfaces this before any change.
System or built-in objects and objects with accidental-deletion protection, resist moves. Confirm the object is a normal, movable object and that protection is cleared.
ADManager Plus replaces scripts and one-off console edits with a single place to move, track, and delegate object changes:
An Active Directory object is any entity the directory stores and manages — a user account, computer account, group, contact, printer, or an OU. Each object has a set of attributes and a unique DN that identifies its exact location in the directory hierarchy. OUs are container objects that hold other objects and are the targets you move objects into.
To find a computer object's location using PowerShell, run:
Get-ADComputer -Filter "Name -eq 'MACHINENAME'" | Select-Object Name, DistinguishedName
The DN shows exactly which OU holds it. In ADUC, enable View > Advanced Features, open the computer's Properties, and read the canonical name on the Object tab.
Yes. Once moved, the object stops inheriting the GPOs linked to its old OU and immediately inherits those linked to the new OU and its parent OUs. This can apply stricter security settings, different software, or new drive mappings—so review the destination OU's linked GPOs before moving objects, especially in bulk. The change applies at the next Group Policy refresh.
You shouldn't move a domain controller's computer account out of the Domain Controllers OU. That OU applies the Default Domain Controllers Policy, which grants the rights a domain controller needs to function; moving the account elsewhere changes its policy and can break authentication and replication. If you need different settings, create a separate GPO and link it to the Domain Controllers OU rather than relocating the account.
Add the -WhatIf parameter to Move-ADObject. It reports what the command would do and which object would move where without making any change. This helps you can catch a mistyped DN or wrong target OU before it takes effect. Remove the flag to run the move for real.