Listing users by department is one of the most common Active Directory (AD) reporting tasks, used to build organization charts, run license audits, and verify that an HR-to-AD sync populated the field correctly. There are three practical ways to do it: with the Get-ADUser PowerShell cmdlet, the Active Directory Users and Computers (ADUC) console, and ManageEngine ADManager Plus.
In AD, department is a single-valued string attribute on each user object. It is populated either manually through the ADUC Organization tab or programmatically, usually by an HR-to-AD sync. The attribute is widely used as a grouping field for reporting, dynamic distribution lists, and licensing logic. Even though it is queried frequently, department is not part of the default property set that Get-ADUser returns, which is the single biggest reason results come back blank, as is covered in detail below.
Before you retrieve users by department, a few things need to be in place:
Import the module and confirm it loaded using the following PowerShell command:
									Import-Module ActiveDirectory

									Get-Module -Name ActiveDirectory
The -Filter parameter uses PowerShell Expression Language and runs server-side, so it is faster than retrieving every user and piping to Where-Object. Because department is not a default property, include -Properties Department so the value is returned.
Match an exact department with the following PowerShell command:
									Get-ADUser -Filter "Department -eq 'Sales'" -Properties Department |

									Select-Object Name, sAMAccountName, Department
Use a wildcard to match any department beginning with a string, and -or to combine several departments in one query:
									# Any department starting with "IT"

									Get-ADUser -Filter "Department -like 'IT*'" -Properties Department |

									Select-Object Name, sAMAccountName, Department


									# Multiple departments

									Get-ADUser -Filter "Department -eq 'Sales' -or Department -eq 'Marketing'" -Properties Department |

									Select-Object Name, sAMAccountName, Department
The same query can be expressed with -LDAPFilter, which takes a raw LDAP query string. Some administrators prefer it for complex conditions or when reusing filters from other LDAP tools. The department equivalents of the examples above are captured with the following PowerShell command:
									# Exact match

									Get-ADUser -LDAPFilter "(department=Sales)" -Properties Department |

									Select-Object Name, sAMAccountName, Department


									# Wildcard match

									Get-ADUser -LDAPFilter "(department=IT*)" -Properties Department |

									Select-Object Name, sAMAccountName, Department
Both -Filter and -LDAPFilter run server-side and return the same results; the choice is a matter of syntax preference. Note that LDAP attribute names are case-insensitive but use the raw name (department), whereas -Filter uses the PowerShell property name (Department).
By default Get-ADUser returns rich objects. Use Select-Object to choose the columns for a report, and Format-Table -AutoSize for clean console output:
									Get-ADUser -Filter "Department -eq 'Engineering'" -Properties Department, Title, Manager |

									Select-Object Name, sAMAccountName, Department, Title |

									Format-Table -AutoSize
In a large directory, restricting the query to a specific OU is essential for performance. -SearchBase takes the distinguished name of the OU, and -SearchScope controls the depth, OneLevel for the immediate children only or Subtree (the default) for all nested OUs:
									# Every user under the Sales OU, with their department

									Get-ADUser -SearchBase "OU=Sales,DC=corp,DC=com" -Filter * -Properties Department |

									Select-Object Name, sAMAccountName, Department


									# One OU level only, filtered to Finance

									Get-ADUser -SearchBase "OU=HQ,DC=corp,DC=com" -SearchScope OneLevel `

									-Filter "Department -eq 'Finance'" -Properties Department
To pull users from several OUs in one run, see Get-ADUser list from multiple OUs.
Pipe Get-ADUser straight to Export-Csv, and never through Format-Table first, since formatting turns the objects into display text that doesn't export cleanly. A calculated property can substitute a readable value for blank departments and resolve each manager's distinguished name to a name:
									Get-ADUser -Filter * -Properties Department, Title, Manager |

									Select-Object Name, sAMAccountName,

									@{Name='Department'; Expression={ if ($_.Department) { $_.Department } else { 'Unassigned' } }},

									Title,

									@{Name='Manager'; Expression={ (Get-ADUser $_.Manager -ErrorAction SilentlyContinue).Name }} |

									Export-Csv -Path "C:\Reports\users-by-department.csv" -NoTypeInformation -Encoding UTF8
The calculated Department column shows Unassigned instead of a blank, so the report stays clean, and the Manager column shows a readable name rather than a distinguished name. For a reusable report, wrap the logic in a parameterized script that takes a department and OU and exports the result:
									param(

									[string]$Department,

									[string]$OU,

									[string]$OutputPath = "C:\Reports\department-report.csv"

									)

									Import-Module ActiveDirectory

									$params = @{ Properties = 'Department','Title','Manager','EmailAddress','Enabled' }

									if ($Department) { $params.Filter = "Department -eq '$Department'" } else { $params.Filter = '*' }

									if ($OU) { $params.SearchBase = $OU }

									Get-ADUser @params |

									Select-Object Name, sAMAccountName, UserPrincipalName,

									@{N='Department'; E={ if ($_.Department) { $_.Department } else { 'Unassigned' } }},

									Title,

									@{N='Manager'; E={ (Get-ADUser $_.Manager -ErrorAction SilentlyContinue).Name }},

									EmailAddress, Enabled |

									Sort-Object Department, Name |

									Export-Csv -Path $OutputPath -NoTypeInformation -Encoding UTF8
Beyond a forgotten -Properties Department, a genuinely empty department is common: the user was created without the field, the HR sync hasn't run, or the value was cleared during a role change. To find accounts where the attribute is not set, filter for a department that doesn't match any value with -notlike '*':
									Get-ADUser -Filter "Department -notlike '*'" -Properties Department |

									Select-Object Name, sAMAccountName
The LDAP equivalent is -LDAPFilter "(!(department=*))". Reporting these unassigned accounts is a useful data-quality check before an audit or a license true-up. For a broader pattern on empty fields, see filtering Get-ADUser by null attribute.
After identifying the users, use Set-ADUser to assign or change the department for an individual user. For bulk updates, import the values from a CSV file:
									# Assign Mark Jacob to the Platform department

									Set-ADUser -Identity "mjacob" -Department "Platform"


									# Bulk update using a CSV with the headers SamAccountName and Department

									Import-Csv -Path "C:\Imports\department-changes.csv" | ForEach-Object {

									Set-ADUser -Identity $_.SamAccountName -Department $_.Department

									Write-Host "Updated $($_.SamAccountName) -> $($_.Department)"

									}
To remove the department value, use the folllowing PowerShell command:
Set-ADUser -Identity "sjacobs" -Clear Department
The parameters below are used for department reporting tasks in PowerShell.
| Parameter | Description |
|---|---|
| Get-ADUser | Retrieves one or more user objects from Active Directory. |
| -Filter | Filters users server-side using PowerShell Expression Language, such as Department -eq 'Sales'. |
| -LDAPFilter | An alternative filter that takes a raw LDAP query string, such as (department=Sales). |
| -Properties | Requests non-default attributes such as Department, Title, or Manager. |
| -SearchBase | Scopes the query to a specific OU by its distinguished name. |
| -SearchScope | Sets the search depth: Base, OneLevel, or Subtree. |
ADUC shows the department field on a user's Organization tab. It is best for checking or changing one account rather than reporting across many, since it has no bulk export. To view a user's department:
To modify the value, type a new department in the same Organization tab and click OK. The change is immediate, with no undo, no approval gate, and no audit note attached.
ManageEngine ADManager Plus is a unified AD, Exchange, and Microsoft 365 management and reporting tool with predefined AD user reports that return every user across one OU, several OUs, or the whole forest—with no scripting.
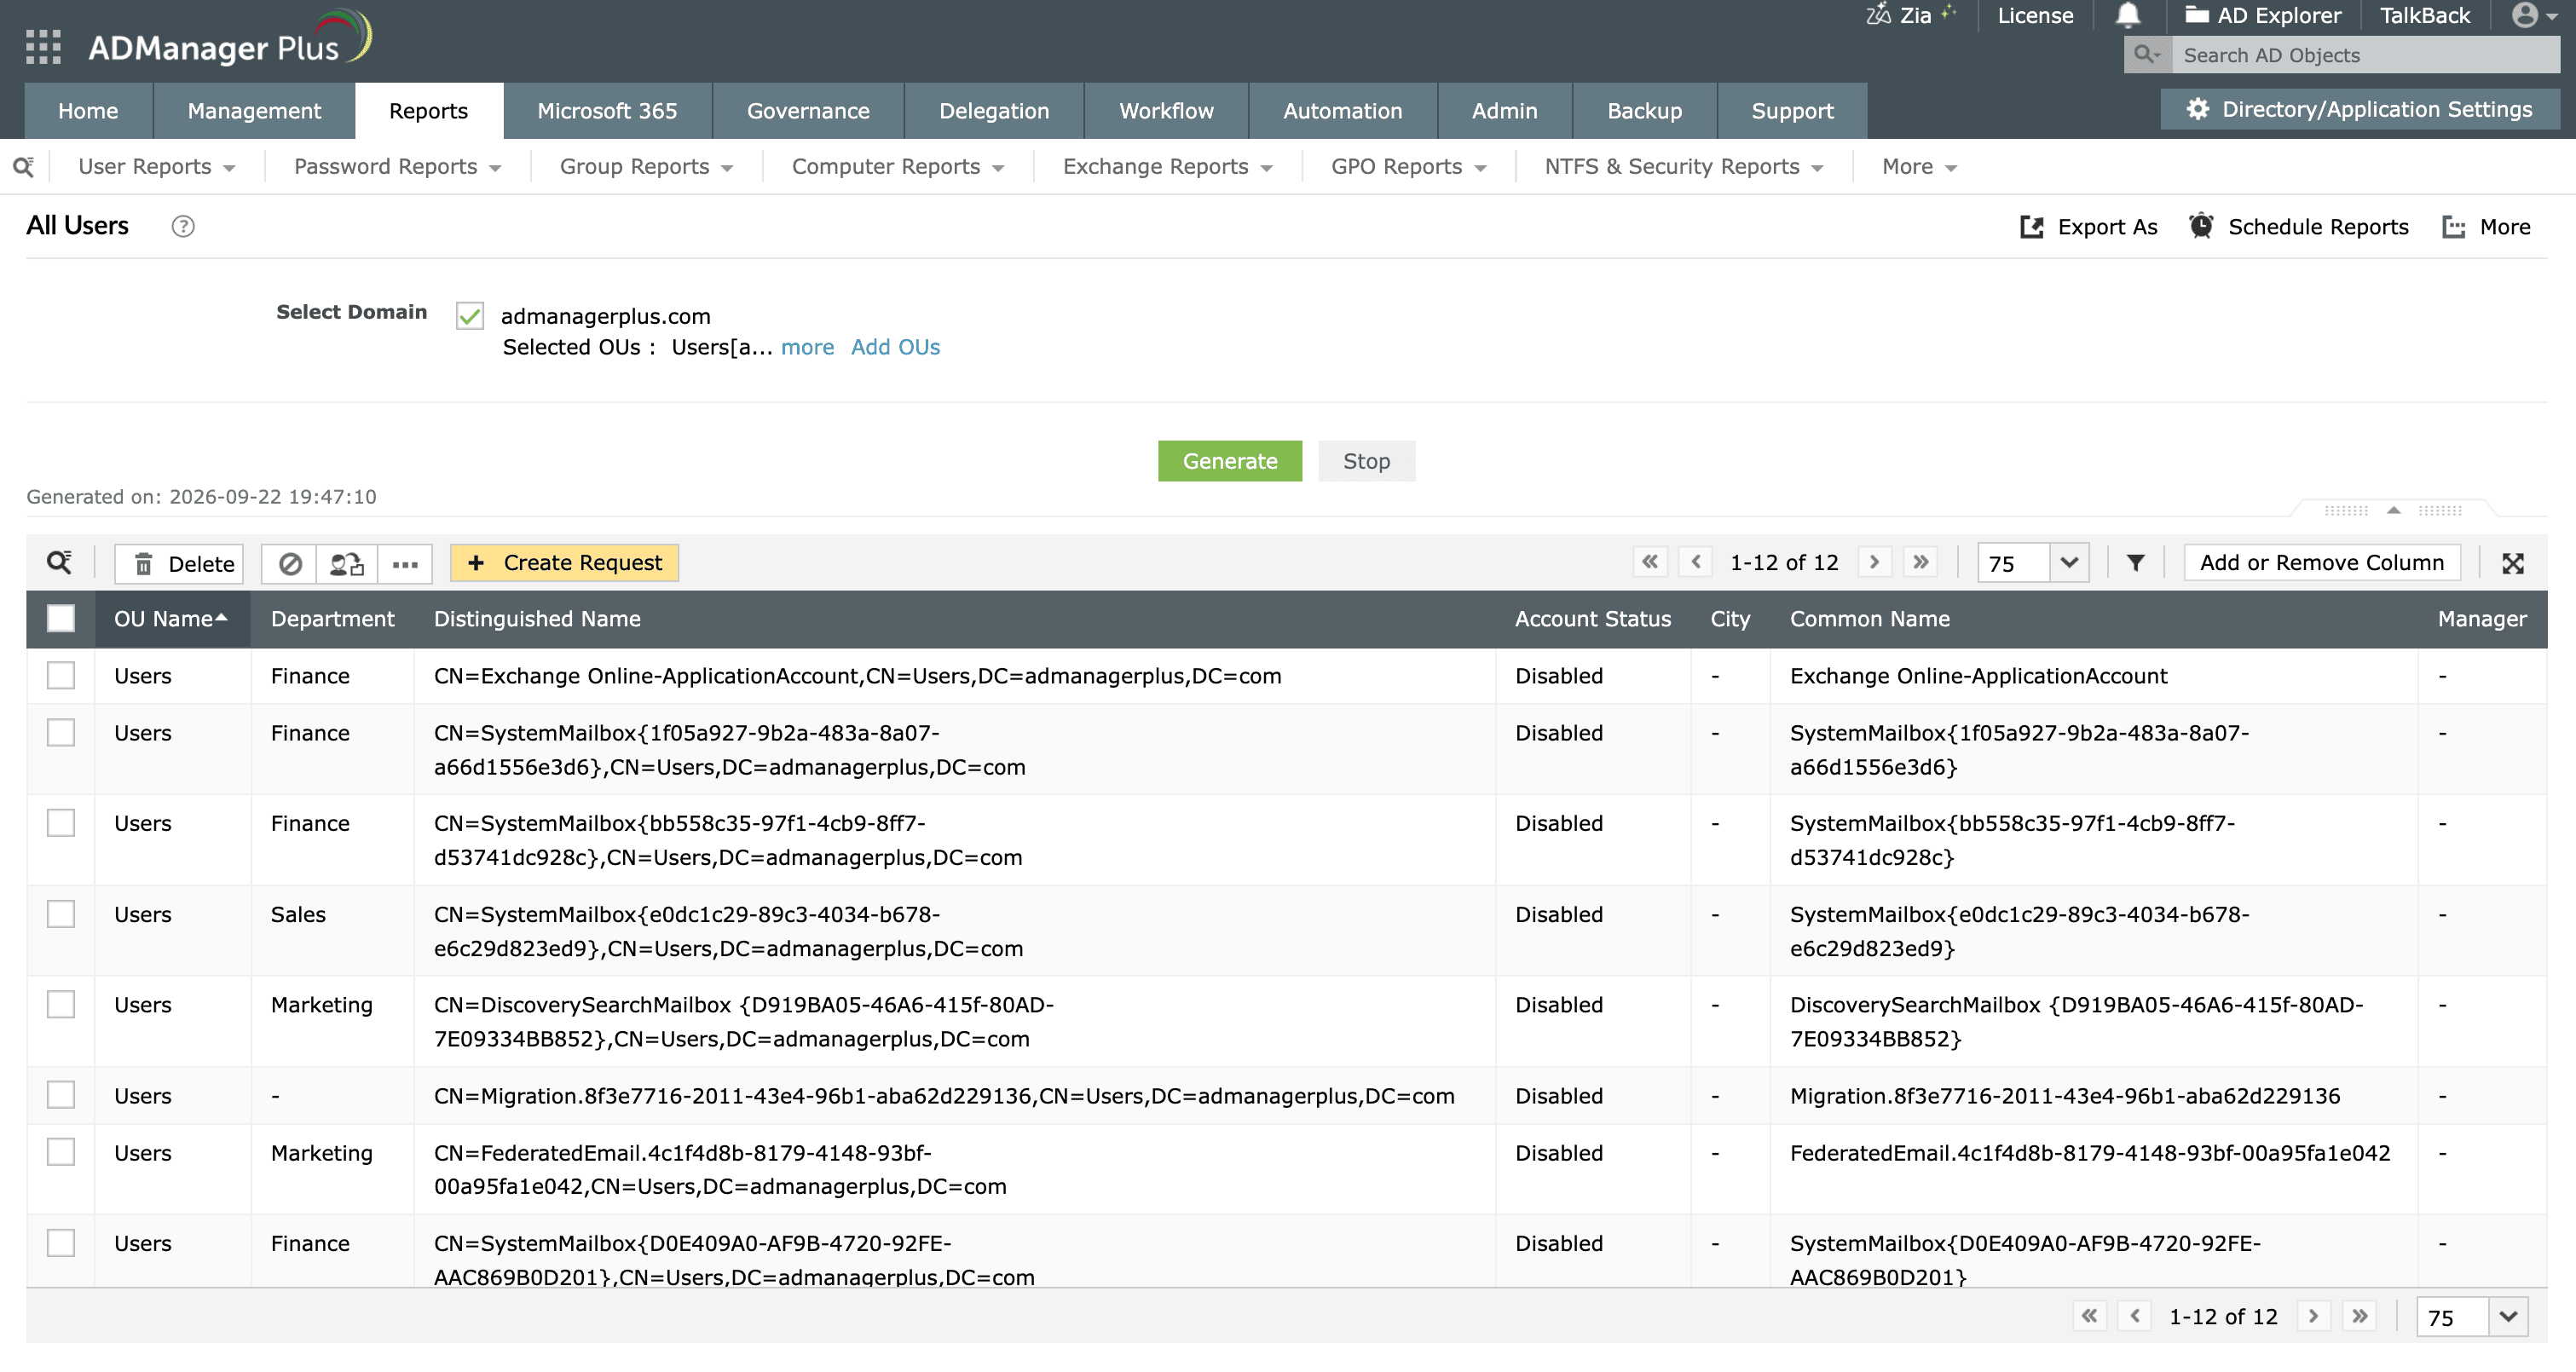
Once you have a list of users to reassign, use ADManager Plus' bulk user modification to change the department for many users at once from a CSV, or pick users directly from a generated report.
ADManager Plus replaces scripts and repetitive console edits with a single console for AD, Microsoft 365, and Exchange management and reporting:
Get-ADUser is a PowerShell cmdlet supplied by the Active Directory (AD) module that retrieves one or more user objects from AD. You query by identity, filter expression, or LDAP filter, and request additional attributes with -Properties.
The most common reason that Get-ADUser return a blank department field is that -Properties Department was not specified, since department is not in the default property set. Other causes include the user being created without the field populated, an HR sync that hasn't run, or the attribute being cleared during a role change. To find genuinely empty values, filter with Department -notlike '*'.
To get the department for all AD users at once, run Get-ADUser in a PowerShell command with a wildcard filter and request the department property:
												Get-ADUser -Filter * -Properties Department |

												Select-Object Name, sAMAccountName, Department
For domain-wide bulk exports, pipe the result to Export-Csv, or see get all AD users with PowerShell.
To change a single user's department attribute, run the following PowerShell command: Set-ADUser -Identity "sjacobs" -Department "Marketing". To clear the value, use Set-ADUser -Identity "sjacobs" -Clear department. For bulk changes, import a CSV and loop with Set-ADUser, or use bulk user modification in ADManager Plus to apply the change with an approval workflow.
You can wrap a script in Task Scheduler to schedule a recurring department report from PowerShell, but you have to build the email delivery, archival, and retention pieces yourself. ADManager Plus has built-in report scheduling that emails department reports as CSV, PDF, or other attachments on a recurring basis.