The AI-driven SIEM your SOC doesn't have to build first.
Trusted by the world's leading businesses

Most security information and event management (SIEM) solutions arrive empty. Before anything can be detected, someone has to normalize your log sources into the vendor's data model, map fields, and learn a query language. That's months of work that produces no security, and it's why AI layered on an unmodeled SIEM solution mostly generates confident nonsense.
ManageEngine Log360 normalizes and entity-resolves telemetry as it arrives across Windows and Linux, network devices, on-premises, and cloud. 2,000+ ATT&CK-mapped detections run against a coherent data model from the start. Your analysts ask questions in plain English. Your agents get data they can reason over. The detection engineering is already done; your team's effort goes into the threats, not the plumbing.
Threat detection, investigation, and response (TDIR) only works when the underlying data agrees with itself. Log360 ships the correlation, identity resolution, and detection content rather than expecting you to build them on top.
Real environments aren't limited to a single vendor, but you only need one SIEM solution to make sense of these mixed environments. Log360 normalizes everything into the same schema, so a rule written once applies everywhere.
Parsing, normalization, and entity resolution happen at ingestion, not at search time.
Log360 ships as a unified platform. Each capability below is part of the platform license, with no add-ons, no per-execution billing, and no separate products to deploy or maintain.
Every detection rule maps to MITRE ATT&CK and arrives from the cloud, so new coverage lands in Log360 without an upgrade.
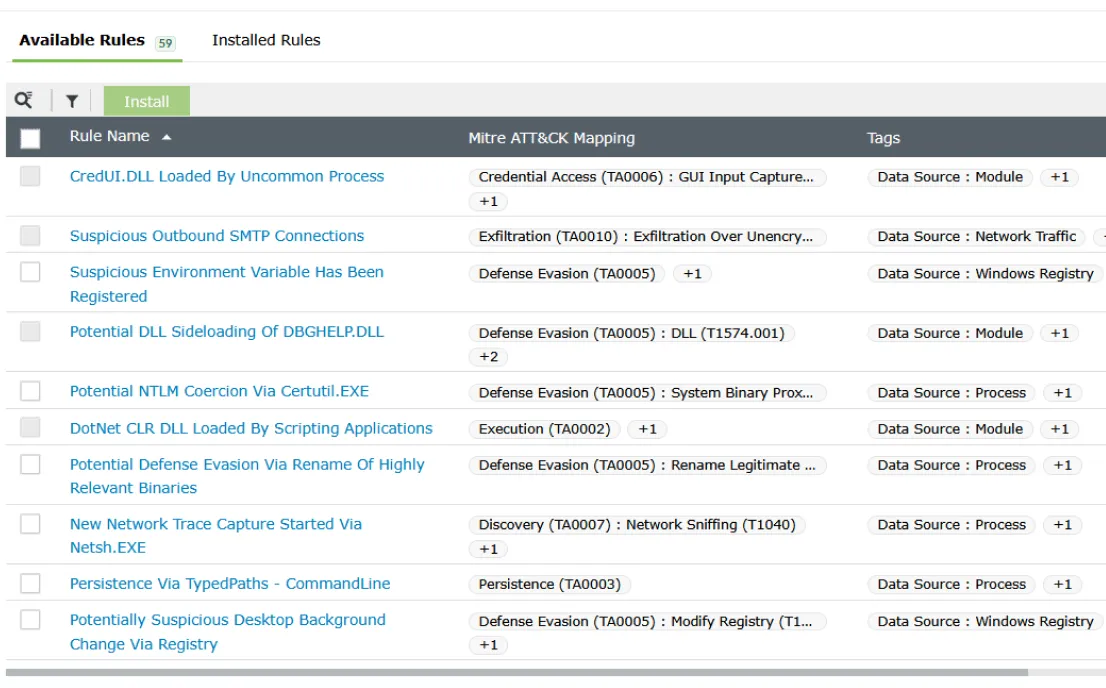
Adjust any rule in Log360 visually. No query language to learn, and none to hire for.
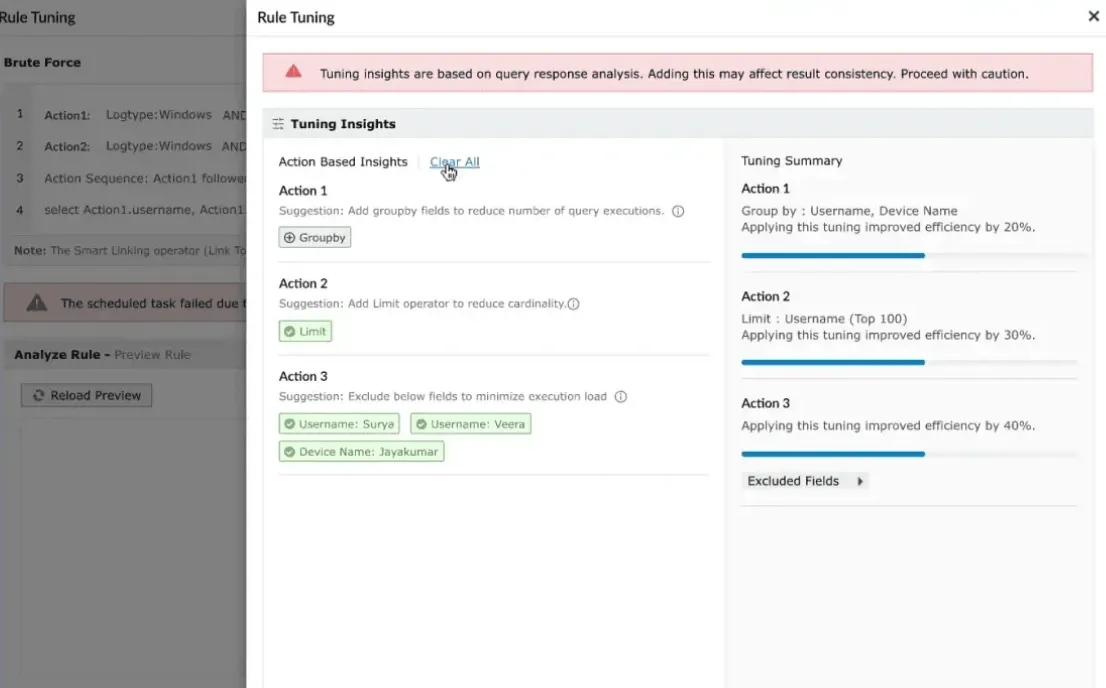
Because identity resolution happens at ingestion, baselining with Log360 works on real users rather than scattered account names.
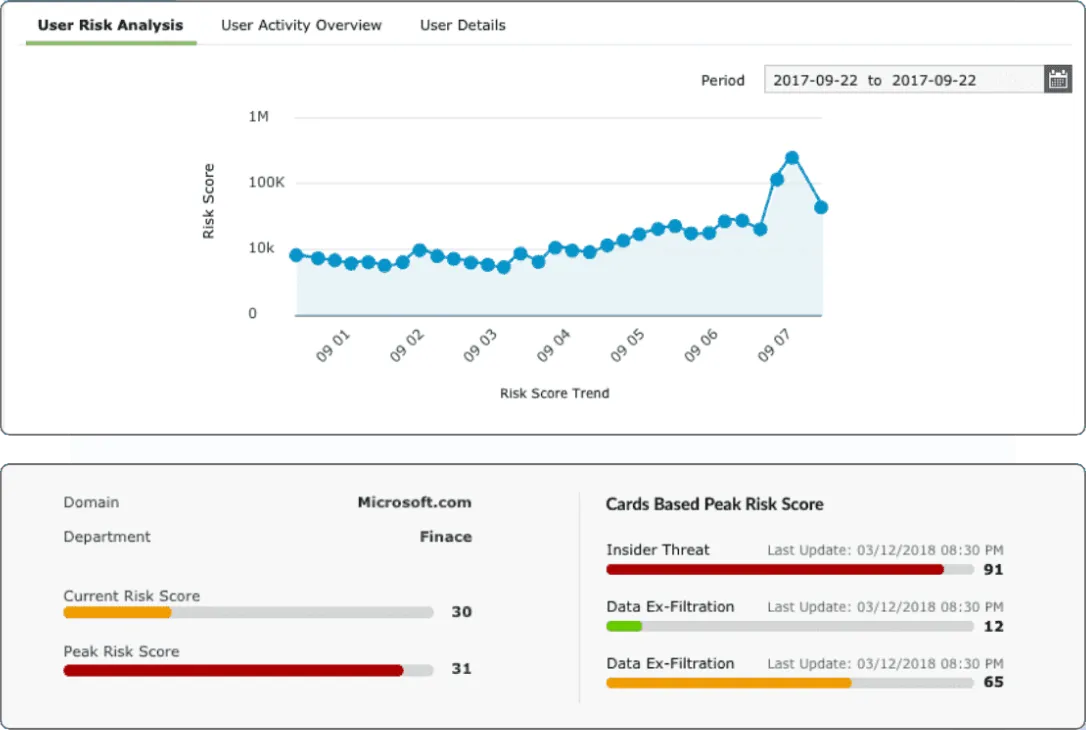
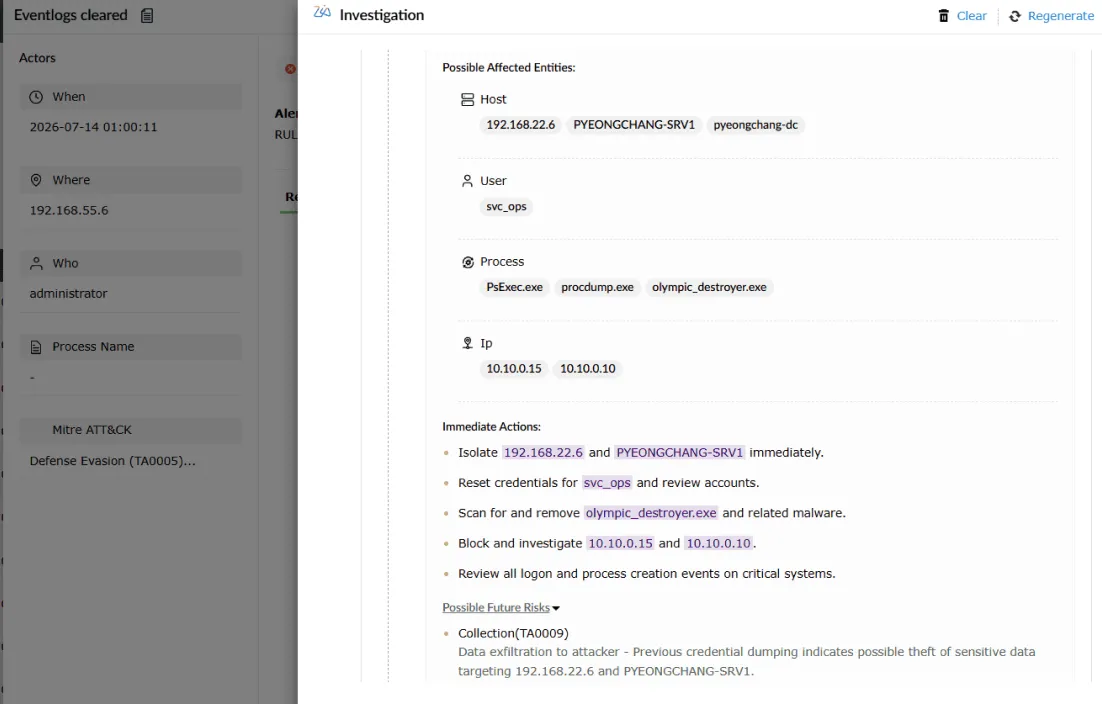
AI reasons well over modeled, entity-resolved data and badly over raw logs. Ours has the former.
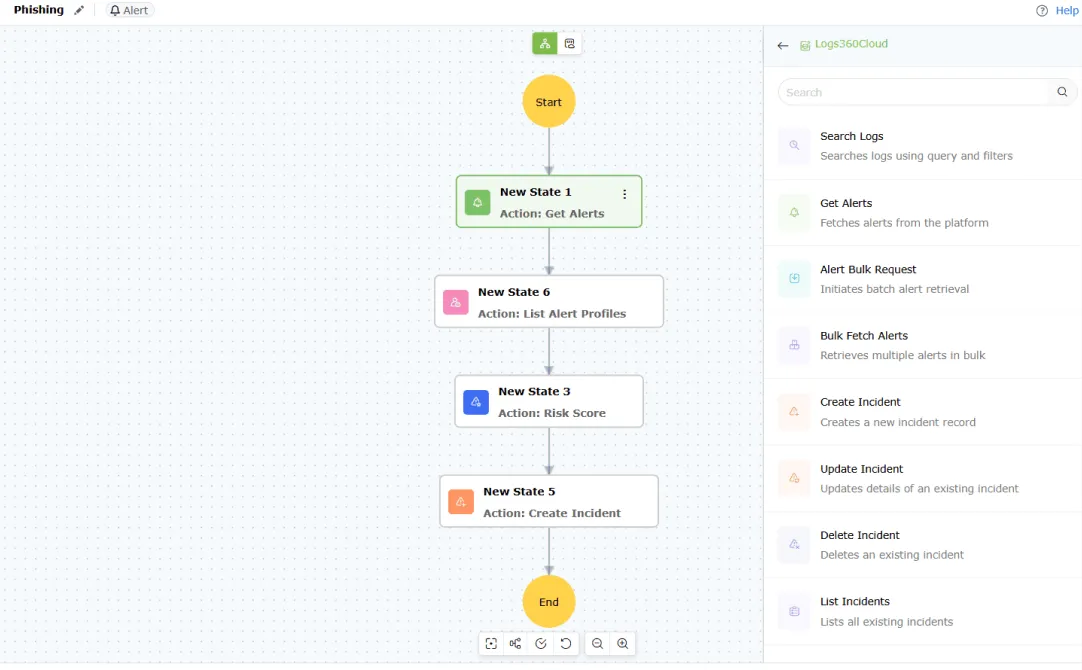
Over 50 prebuilt SOAR playbooks and a visual builder, with no per-execution charge.
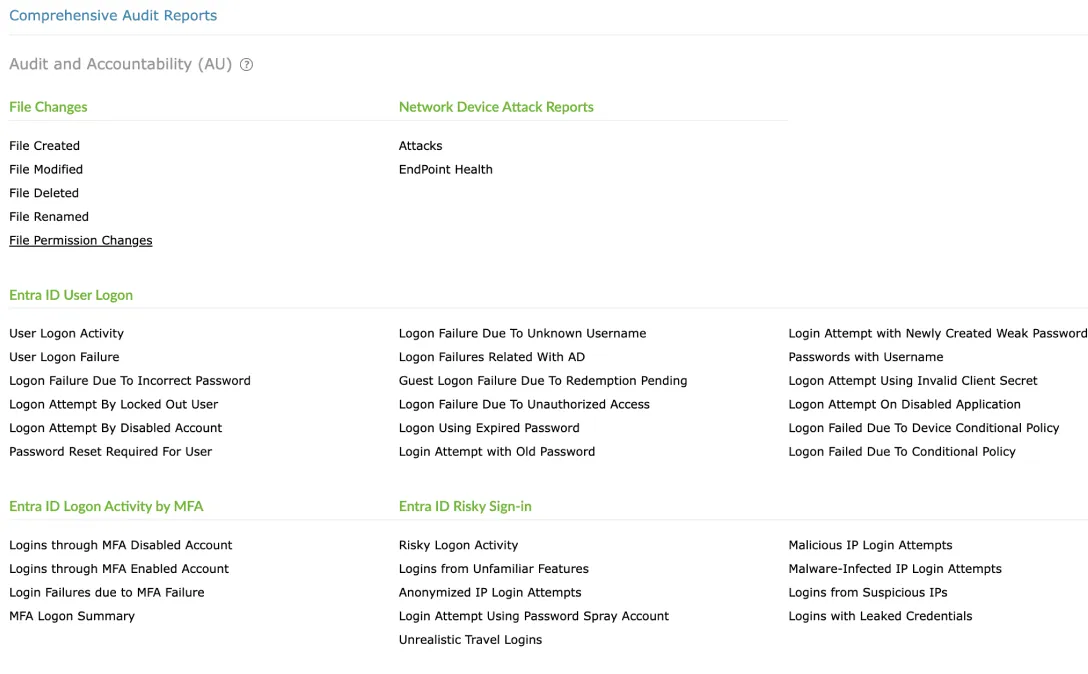
Audit-ready reporting in Log360 is a first-class engine, not a report you assemble.
2,000+ ATT&CK-mapped detections, unlimited SOAR executions, and the full AI layer under one license, priced by the assets you protect, not the data you ingest.
Log360 is licensed by what you protect, not by how much data you generate. Your bill doesn't move when log volume spikes during an incident.
| What you protect | What Log360 does with it |
|---|---|
| Active Directory | Change auditing at attribute level, including prior values. Logon and lockout tracking, group and OU permission changes, Active Directory security posture scoring. |
| Windows file servers | Access auditing, file integrity monitoring, sensitive-data discovery and classification, exfiltration detection. |
| Endpoints | Process activity, removable media, application and installation events, behavioral anomaly detection. |
| Cloud accounts | Auditing, shadow IT discovery, and cloud data protection for AWS, Azure, Google Cloud Platform, Microsoft 365, Entra ID, and Salesforce. |
| Log sources | 750+ prebuilt parsers across Linux and Unix, firewalls, network devices, databases, web servers, and applications. |
Every edition of Log360 includes the full detection library and the AI layer covered earlier. Editions differ in deployment model and operational scale, not in how much security you get; this is a genuine differentiator against competitors who gate behavioral analytics and automated response behind premium tiers.
| Capability | On-premises | Cloud | MSSP |
|---|---|---|---|
| Detection library (2,000+, ATT&CK-mapped) | |||
| Correlation and anomaly rules | |||
| Behavioral analytics | |||
| Response playbooks | Limited | ||
| AI layer (Ask Zia, Zia Insights, agents) | Limited | ||
| Compliance report templates | |||
| Storage tiering and archival | |||
| Deployment | Self-hosted | SaaS | SaaS, multi-tenant |
| Starting price | $2,130 per year | $3,140 per year | $840 per year |
If you're in the second list, we'd rather tell you now than six months into a deployment.
Organizations in financial services, healthcare, government, and manufacturing rely on Log360 to detect threats, automate response, and stay audit-ready.
"Log360 is a complete solution for all of the needs in events auditing! Subcomponents like EventLog Analyzer and ADAuditPlus are really helpful during reviews and audits."
—IT security professional, HCL Group"The drill-down options and visual dashboards make threat investigation much faster and easier. It's a truly user-friendly solution."
—Sundaram Business Services"Log360 helped detect insider threats, unusual login patterns, privilege escalations, and potential data exfiltration attempts in real time."
—The CIO of Northtown Automotive CompaniesWith an AI-enabled security information and event management (SIEM) solution, the data model is built before you buy it. In most SIEM solutions, out-of-box detections are a potentiality—they only begin triggering once your team has normalized sources into the vendor's schema. In Log360, out-of-box detections are an actuality—no normalization process needed.
That's also what makes the AI-enablement useful: AI models and AI agents reason well over modeled, entity-resolved data and badly over raw logs, which is why AI bolted onto an unmodeled SIEM solution produces plausible-sounding noise.
Yes, Log360 works outside Windows environments. Log360 parses over 750 source types: Linux and Unix environments, syslogs from firewalls and network devices, databases, web servers, hypervisors, and logs for cloud platforms like AWS, Azure, Google Cloud Platform, and Microsoft 365. Everything normalizes into the same data model, so a correlation rule written once applies across your whole estate.
No, you don't need to learn a query language. Search, rule tuning, and investigation work through the interface, and Ask Zia handles plain-English questions across logs and alerts. Analysts who already know a query language aren't disadvantaged—but nobody has to learn one to be useful.
Log360 is priced by the assets you protect—domain controllers, Windows file servers, endpoints, cloud accounts, and log sources—not by data volume. A traffic spike during an incident doesn't produce a bill, and long retention is a storage decision rather than a licensing one.
Yes, you can connect Log360 to your own AI tooling. The Log360 MCP Server exposes your security data to Claude, Copilot, or any MCP-compatible client, so agents can query it directly as part of a wider investigation.
Most of our customers don't have a security operations center (SOC). Log360 is built so a one-to-five-person team gets the level of coverage that used to require a staffed SOC—prebuilt detections instead of detection engineers, guided investigation instead of query expertise, playbooks instead of manual runbooks.
Installation takes under an hour and device discovery is automatic. Reaching meaningful coverage depends on how much of your estate you onboard—most organizations see useful detection in the first week and full coverage within a month.
Log360 ships with prebuilt templates and real-time violation alerting for HIPAA, SOX, ISO 27001, the PCI DSS, the GDPR, the CCPA, the GLBA, FISMA, and others.