[Webinar] Beyond security logs: Why operational context matters in security investigations
A security event tells you what happened. But understanding why —and what was happening across the environment at the same time—can make all the difference.
Modern security teams have access to vast amounts of security data through SIEM platforms. Logs, events, user activity, threat indicators, and alerts provide critical evidence for detecting and investigating potential incidents. But when an investigation requires understanding the underlying infrastructure, security teams may need to look beyond the security event itself.
➤ Was the network experiencing unusual traffic?
➤ Was a critical server under heavy resource pressure?
➤ Had a configuration recently changed?
➤ Was the affected device running vulnerable firmware?
➤ Was an application already experiencing performance issues?
Operational context becomes valuable here. This is where ManageEngine OpManager Nexus can complement Log360.
While Log360 provides security teams with visibility into security logs and events, OpManager Nexus adds visibility across the infrastructure—including networks, servers, applications, traffic, configurations, and connected devices.
With broader infrastructure visibility, security teams can get a more complete picture of what was happening around the event and determine whether the underlying issue is security-related, operational, or a combination of both.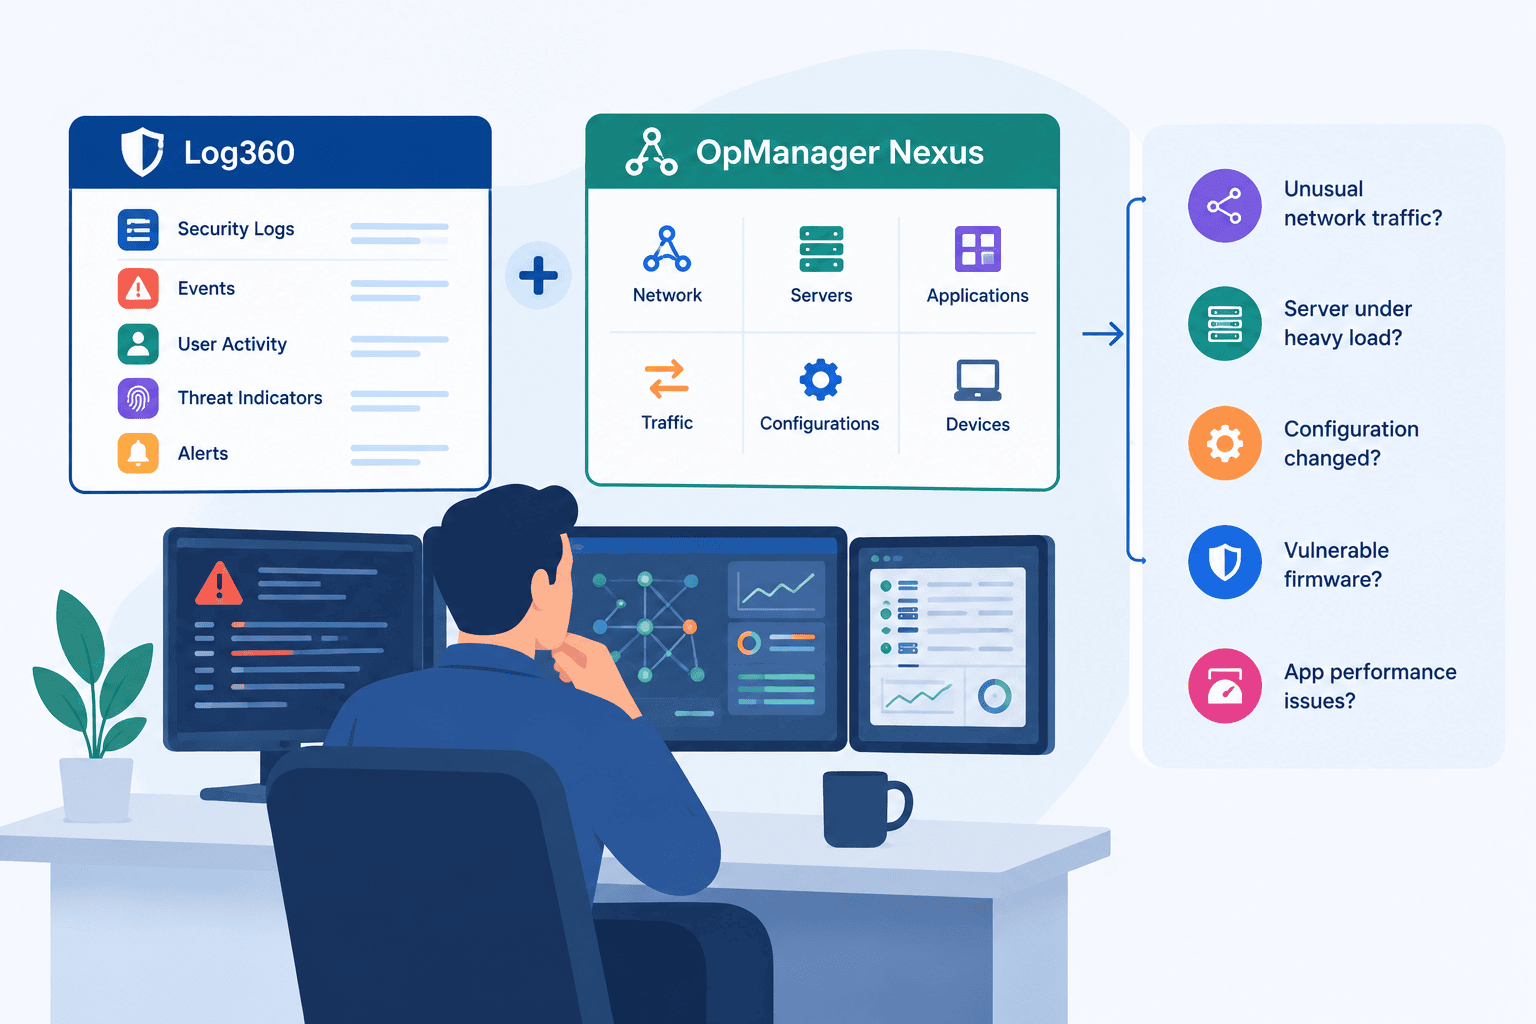
We are coming live to show this visibility in action
Join our upcoming webinar to see how ManageEngine OpManager Nexus works alongside Log360 to bring security and operational visibility closer together.
In this live session and product demo, we'll explore how infrastructure context can help security teams:
Connect security events with infrastructure context to investigate incidents with greater clarity.
Understand the potential blast radius of vulnerable assets using organization maps.
Detect unusual network traffic behavior and map suspicious activity to MITRE ATT&CK techniques.
Track configuration changes and compliance violations across network devices.
Identify firmware vulnerabilities and streamline remediation.
Detect rogue or unauthorized devices connected to the network.
Proactively monitor infrastructure and application performance to identify operational issues that may be related to security events.
The goal isn't to replace your existing security visibility. It's to add the operational context needed to make that visibility more actionable.
Webinar details:
Date: October 13th, 2026
Time: 6am GMT and 11am EDT
Register here - limited slots!