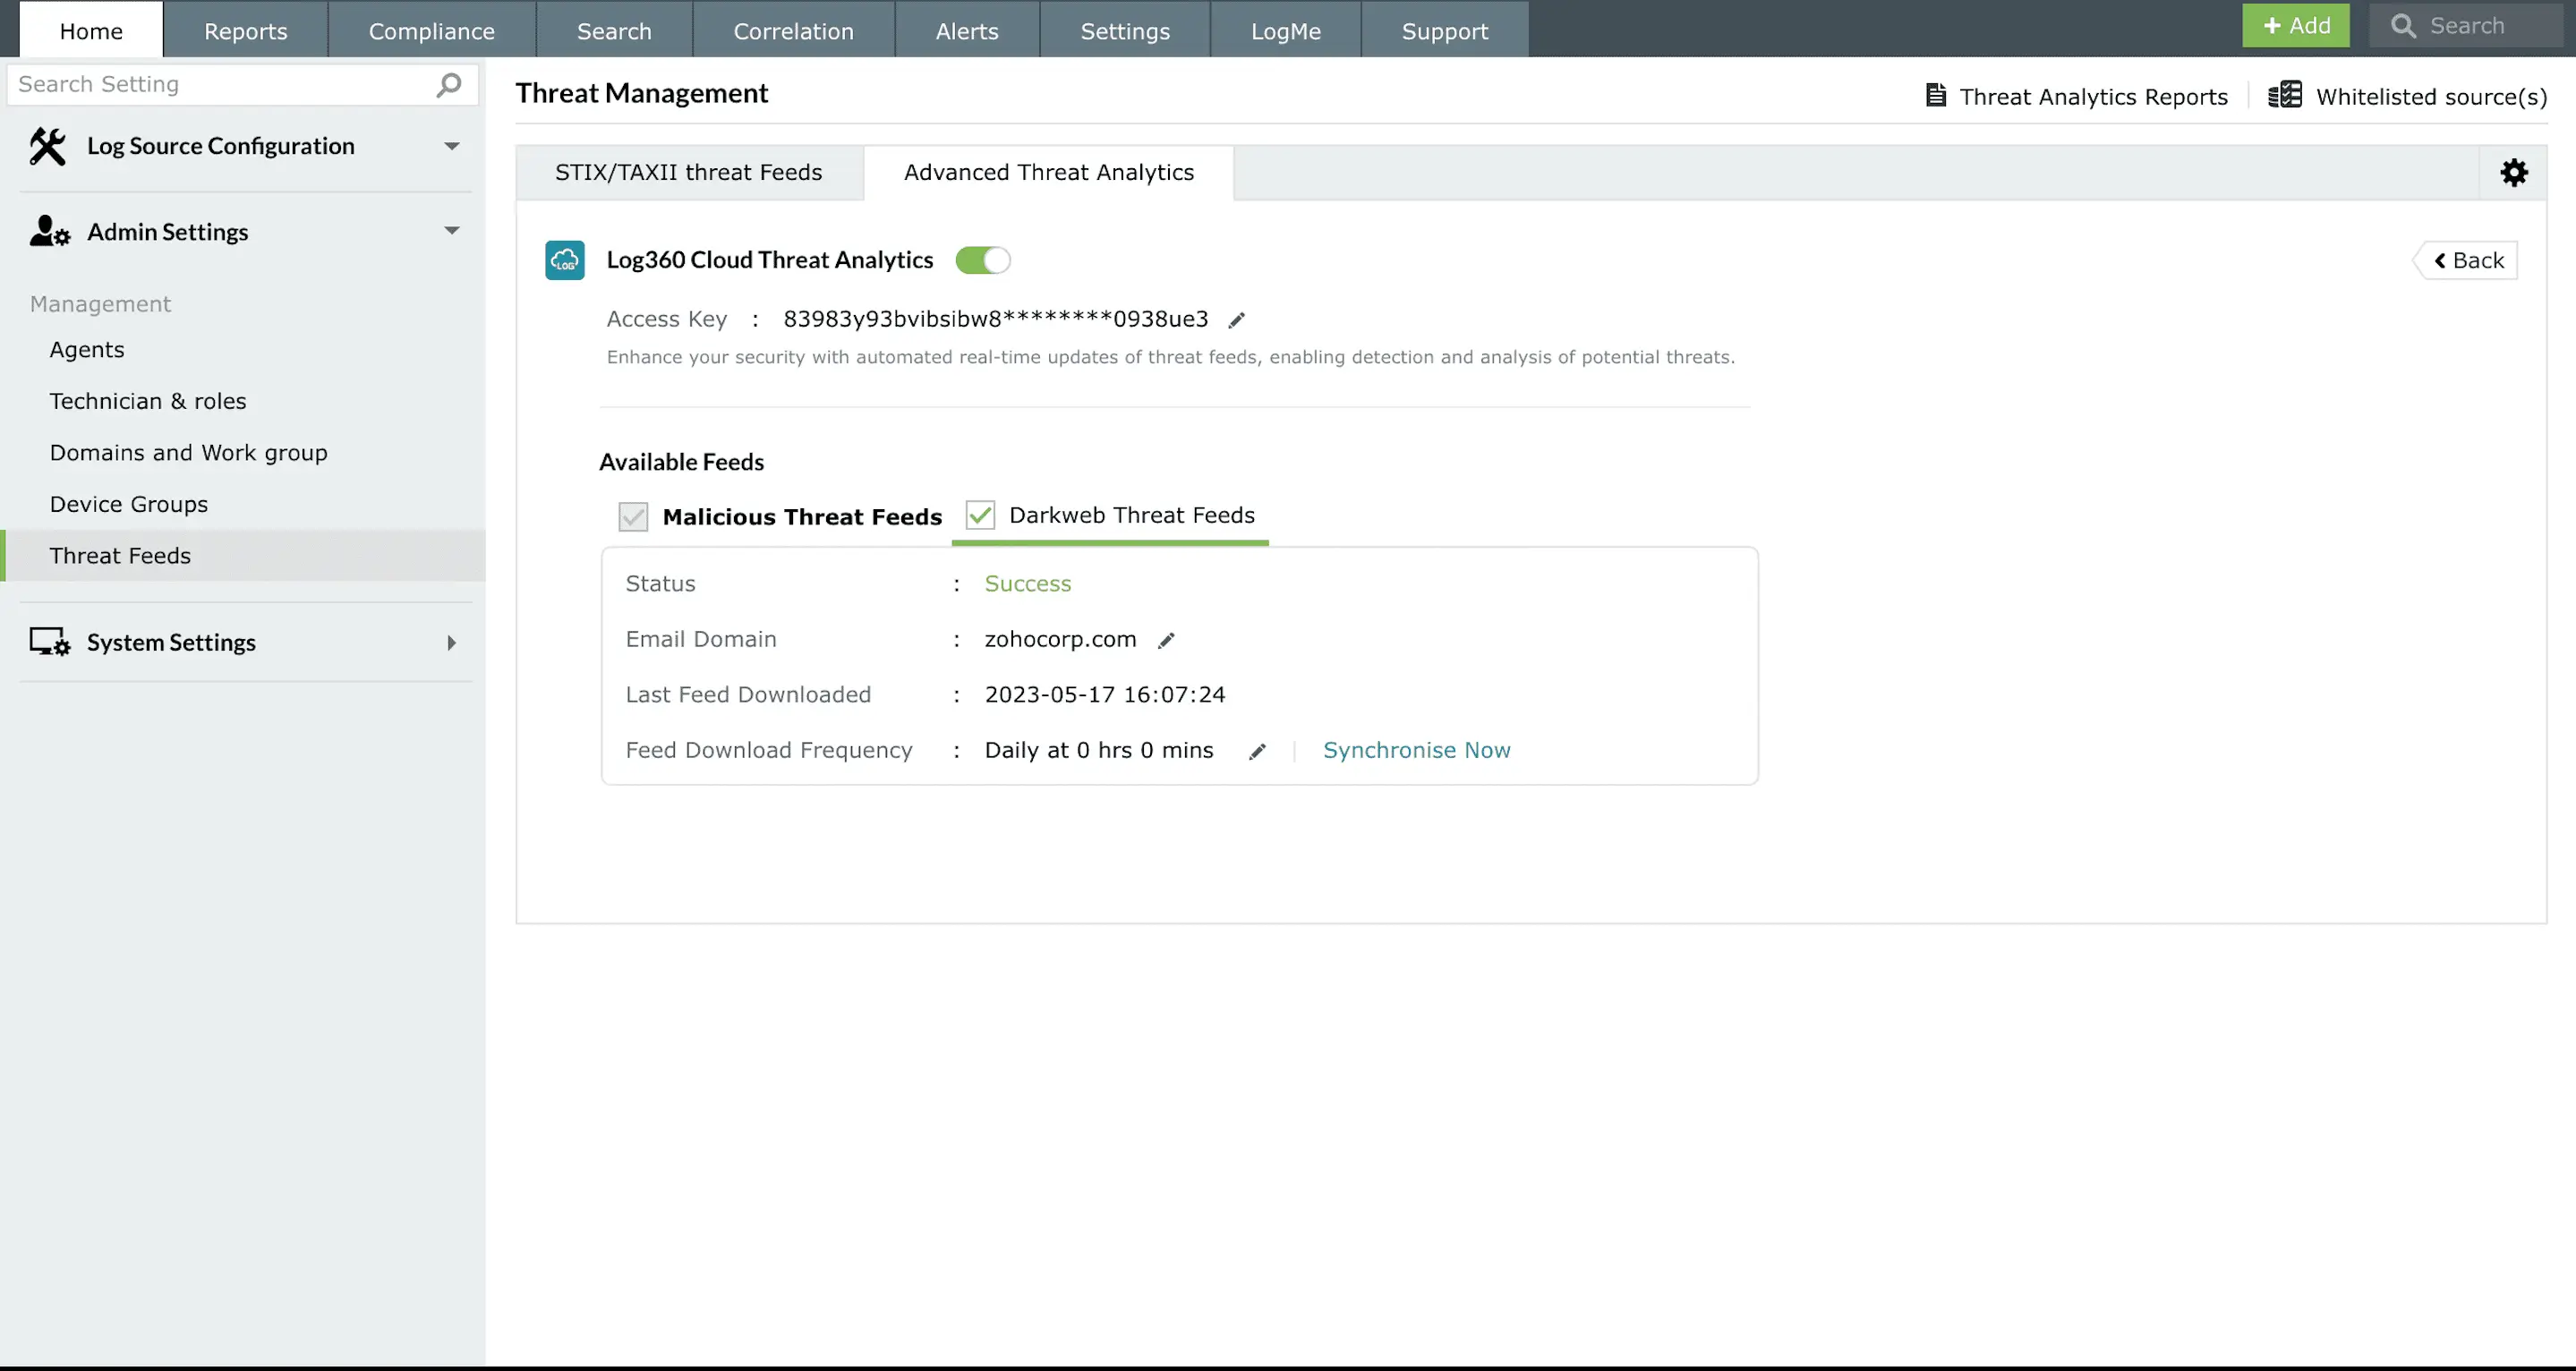
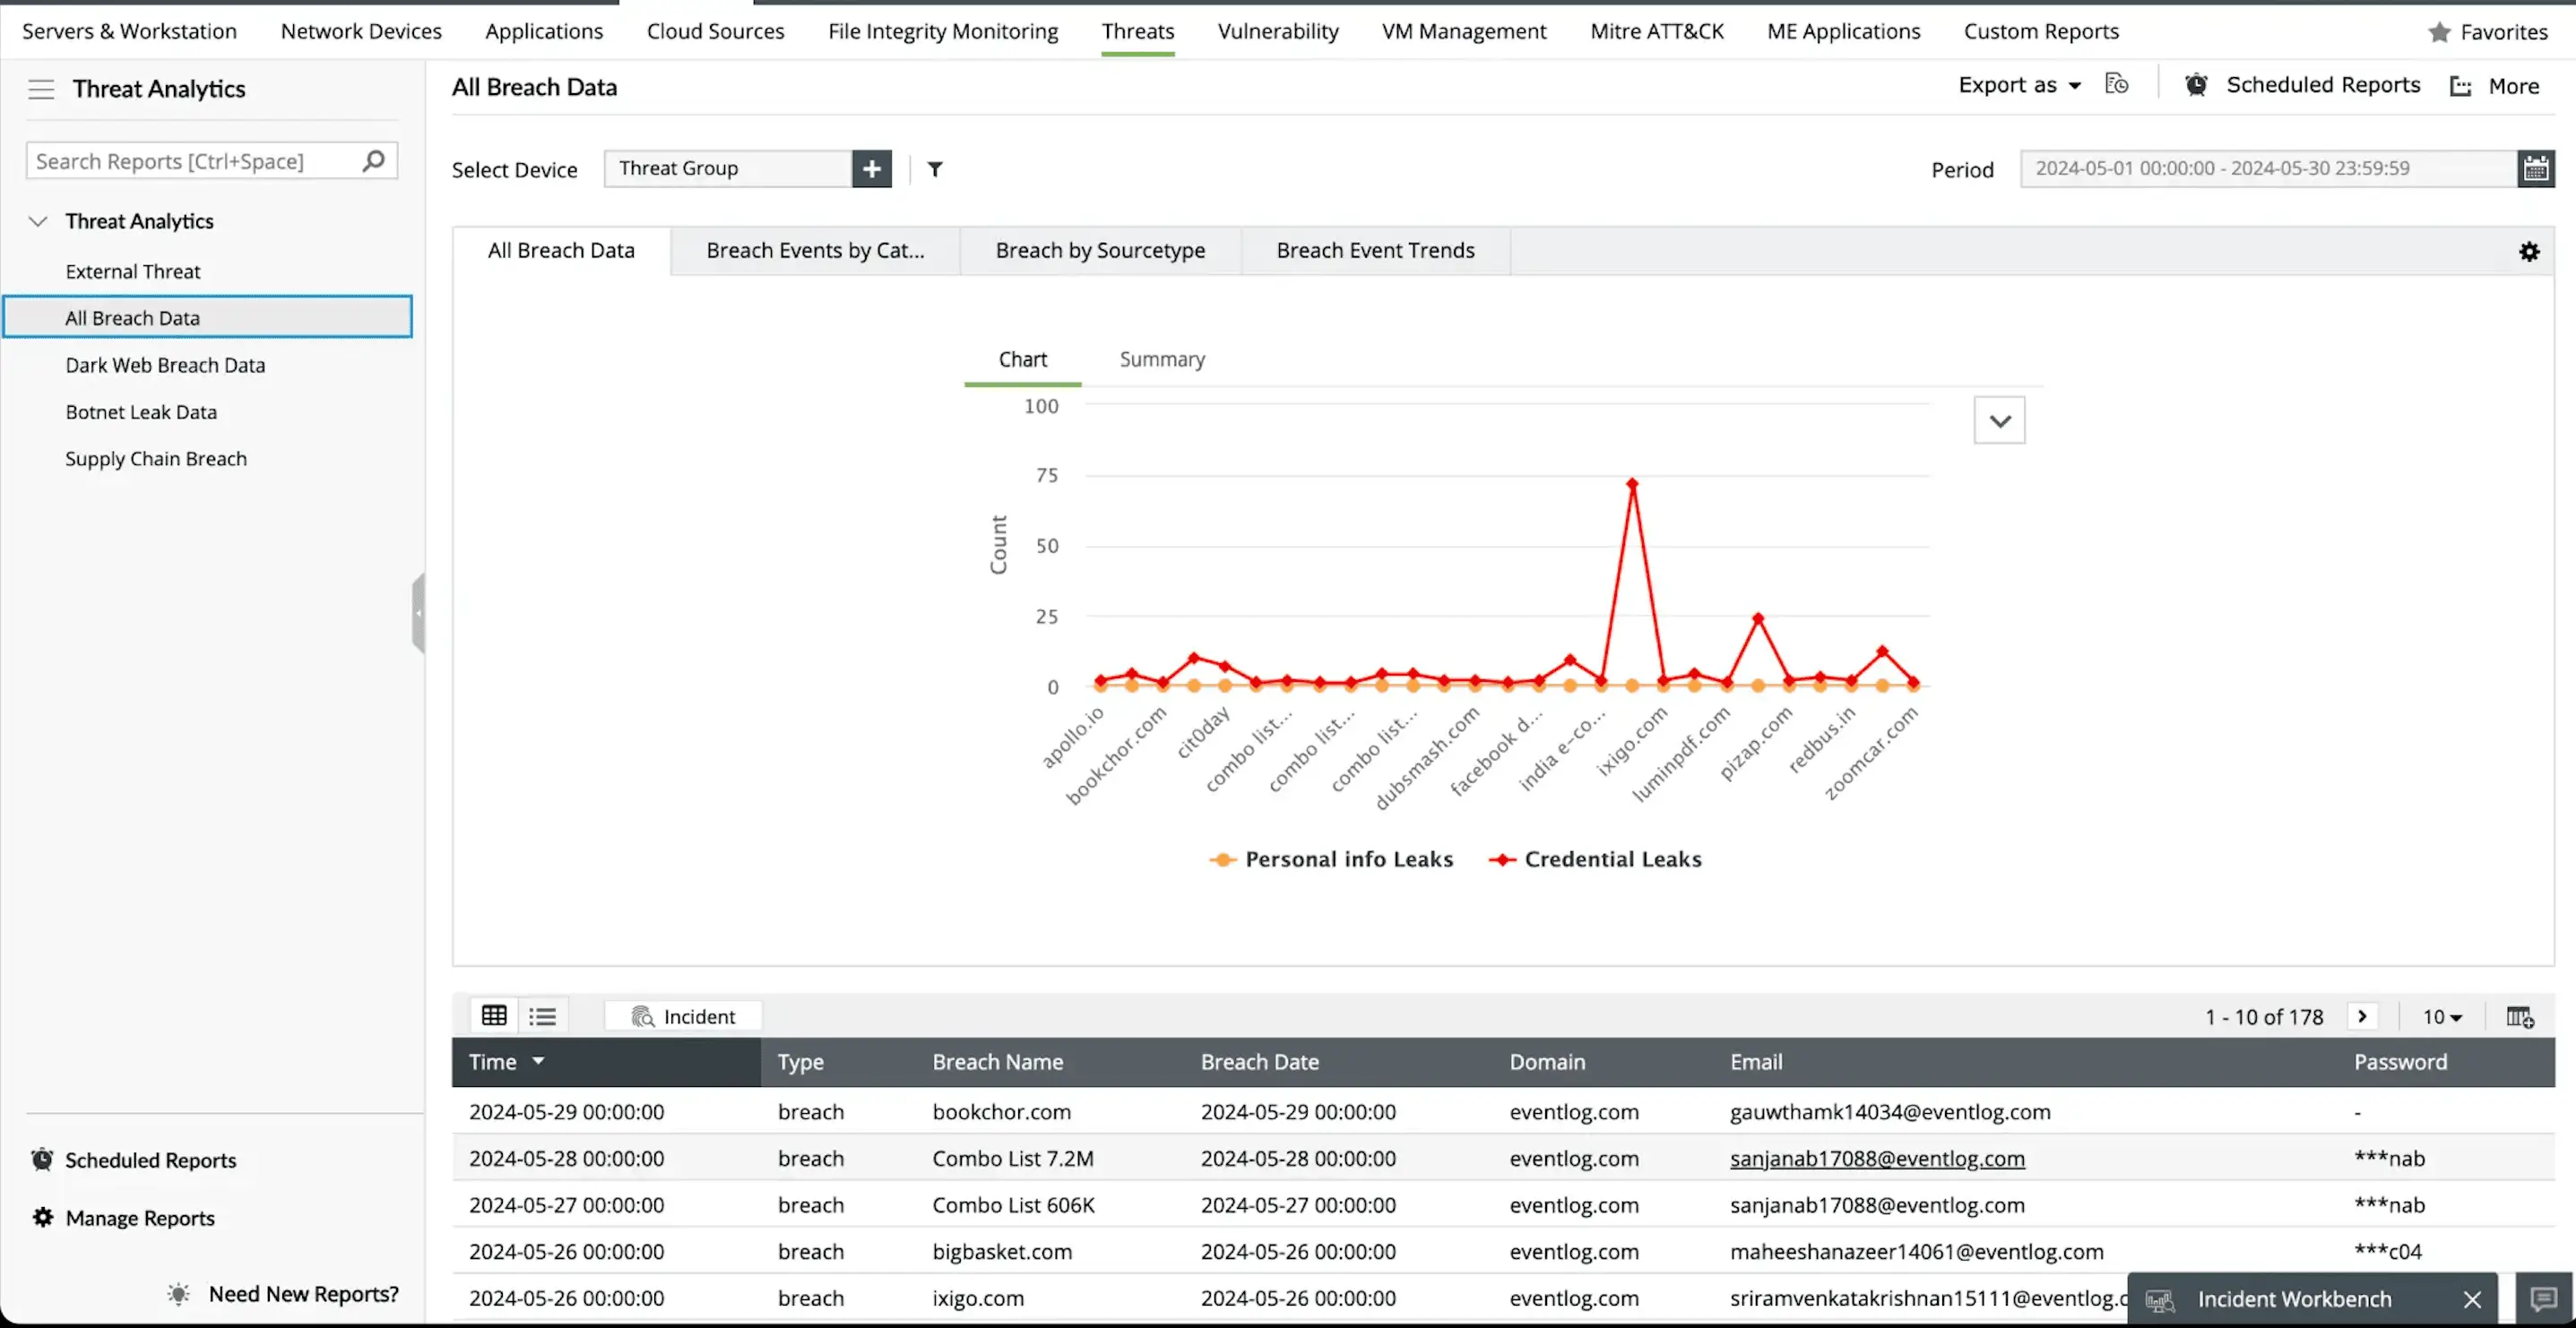
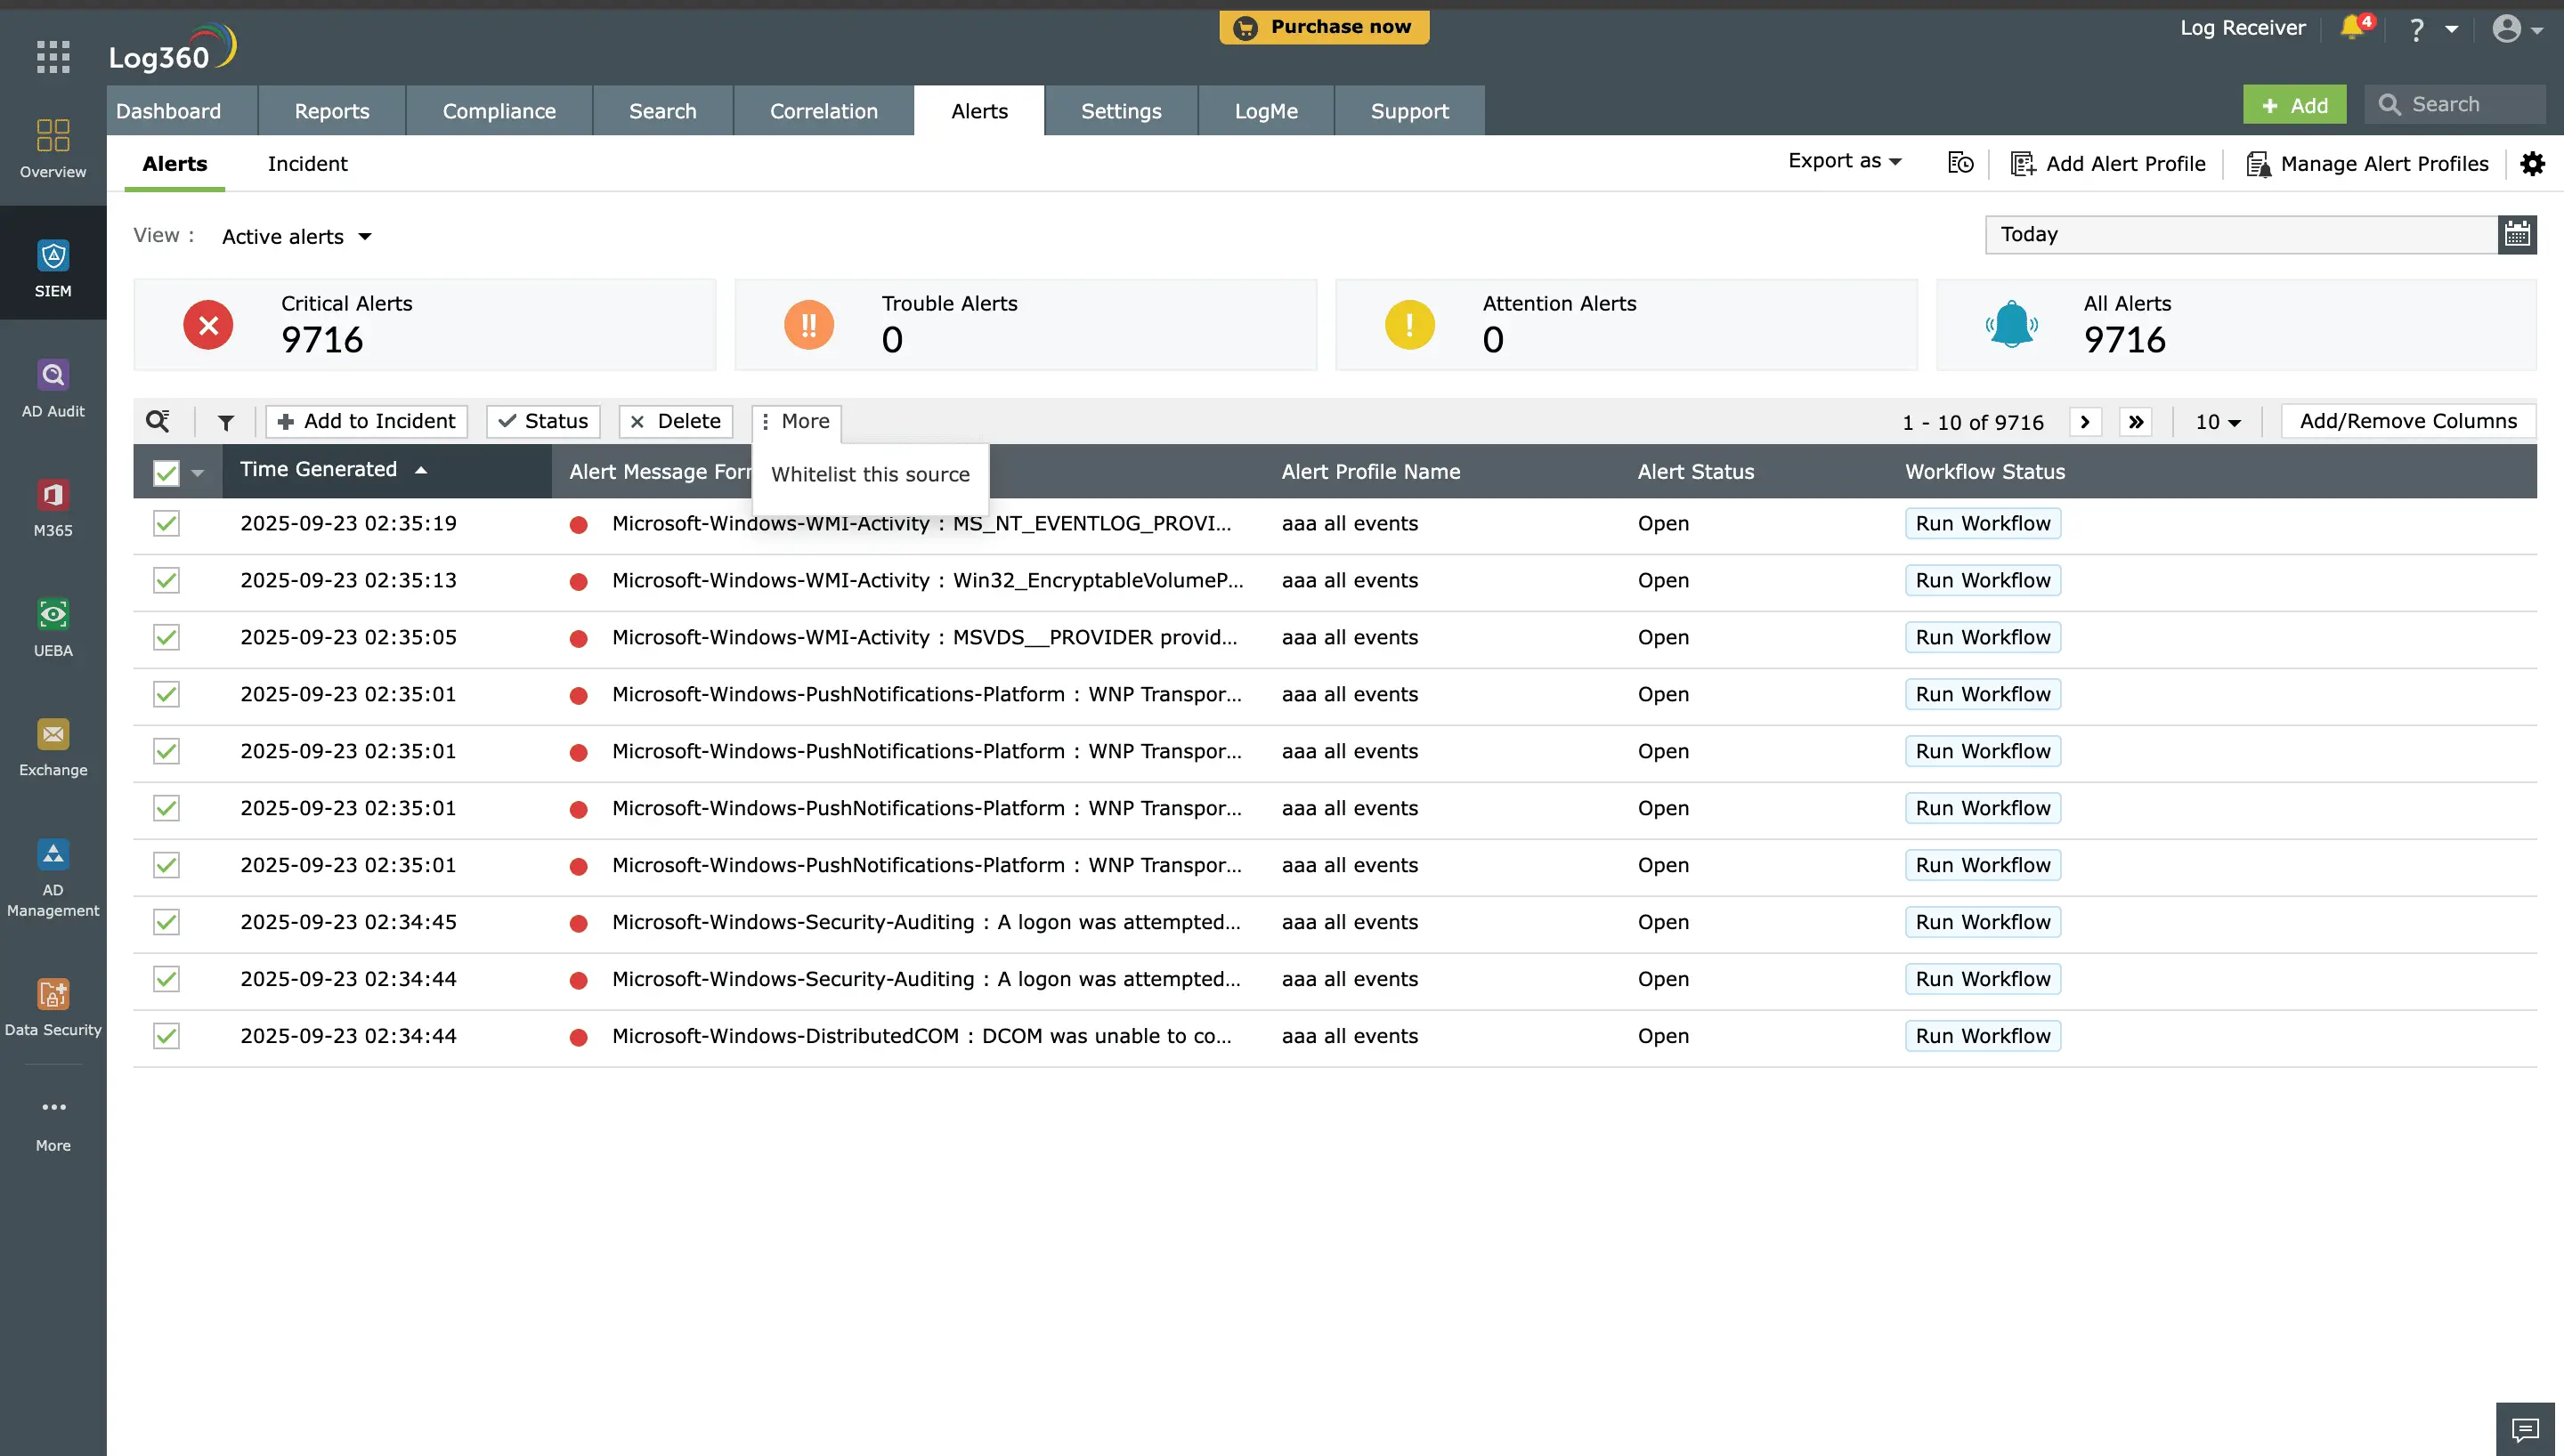
Exploiting public-facing machines and known vulnerabilities is still one method hackers use to intrude into a network. With Log360's preconfigured threat alerts, enterprises can stop not only the communication from a malicious source but also automatically trigger a workflow to add blacklisted IPs to the firewall and permanently block them.