Learn about the new product innovations we deliver every quarter. Read the release notes,
download helpful resources, and register for our release webinars!
Log360 Cloud expands its AI capabilities with alert investigation, a conversational assistant, AI agents, and MCP support. Zia helps analysts move from raw security data to actionable understanding, so they can spend less time searching and piecing together information and more time responding to threats.
The Zia Alert Investigation Agent turns a selected alert into a structured investigation, helping analysts move from an initial alert to a clear understanding of the attack in minutes instead of hours. It identifies and enriches entities, correlates related alerts and logs, reconstructs the attack chain, and presents the findings with suggested next steps.
Ask Zia lets analysts interact with Log360 Cloud using natural language questions about logs and alerts and get answers directly. Analysts can ask follow-up questions to explore the results further, summarize findings, and narrow down information based on their investigation needs.
Zia Agents brings prebuilt and custom AI agents into Log360 Cloud. Security teams can deploy prebuilt agents such as the User Activity Review Agent and Alert Correlation Agent, or build their own agents with no code. This helps teams delegate repetitive analysis or assessments to autonomous AI agents.
Log360 Cloud now supports the Model Context Protocol (MCP) through the Zoho MCP Server. Analysts can query Log360 data, investigate alerts, manage configurations, create incidents, and take other actions from Claude, Copilot, Cursor, or any MCP-compatible AI client.
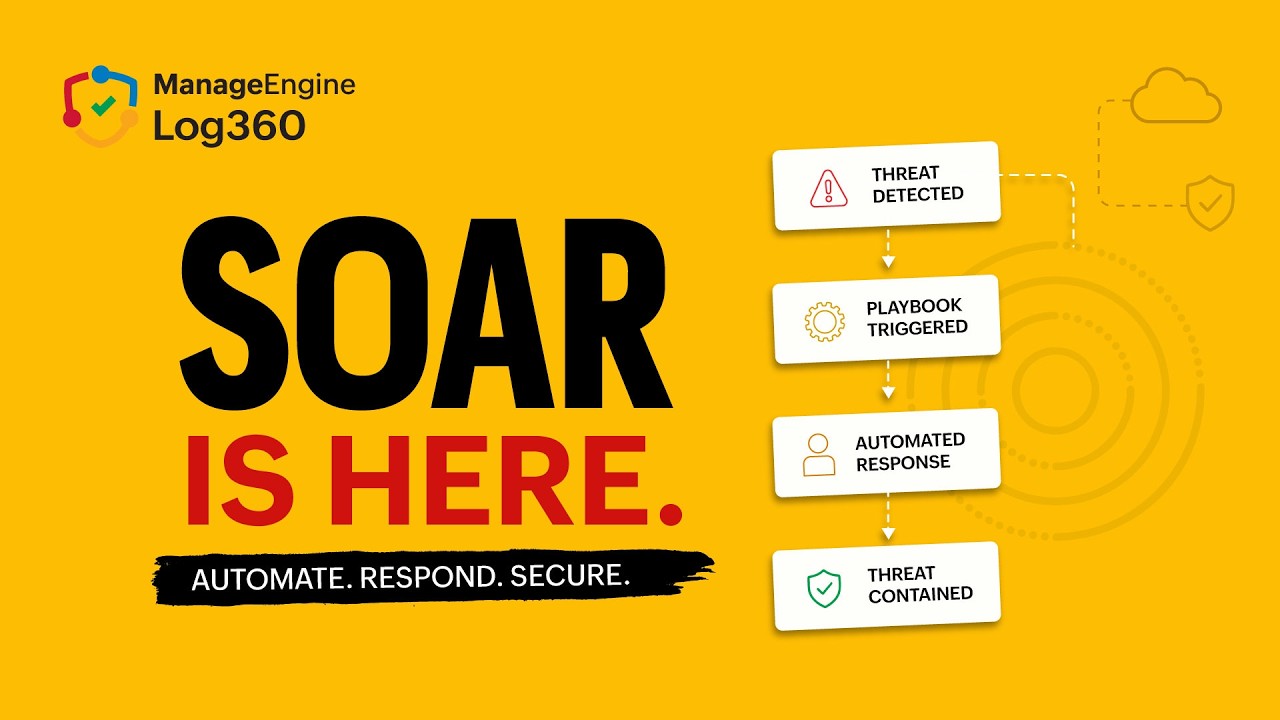
SOAR is now built directly into Log360 Cloud, enabling analysts to automate investigation and response workflows from a unified platform. Use the visual playbook builder to create low-code workflows with branching, parallel execution, custom functions, and coordinated remediation actions across security tools.
Run multiple playbooks in parallel from a single alert and reuse common workflows through nested playbooks. Retry and fallback mechanisms help maintain execution continuity, while manual retries resume from the exact point of failure instead of restarting the workflow.
Extend playbooks with custom logic using Python or Deluge functions. Build reusable workflows for threat enrichment, data parsing, ticket creation, endpoint actions, and organization-specific response logic.
Expanded Log360 Cloud’s integration ecosystem with 7 new marketplace extensions including CrowdStrike GravityZone, Bitdefender EDR, Okta, and more.
Securely manage integrations and authentication from a centralized connections framework. Configure reusable connection profiles for endpoint platforms, identity providers, cloud services, and threat intelligence tools to simplify orchestration across your security stack.
We've redesigned how Log360 detects threats. A new centralized detection console now brings together correlation logic, threat intelligence, MITRE ATT&CK mapping, UEBA insights, and a rule builder that supports standard, anomaly-based, and advanced detection logic. Detection insights helps optimize rules with real-world noise levels and usage metrics—enabling focused, high-fidelity alerts.
Fine-tune alert scope using filters based on users, groups, and OUs. These filters apply across predefined rules for use cases like privilege escalations, suspicious password resets, and admin group changes—helping reduce noise from irrelevant accounts like test users or developer machines. It's precise detection, not suppression.
Log360 now supports horizontal scalability with clustered log processors and role-based specialization for alerting, correlation, and search. You can also collect logs from distributed sites and process them centrally — ensuring high performance even in large, hybrid environments.
Get continuously updated detection content mapped to MITRE ATT&CK, without manual imports. Delivered securely from the cloud, this content is curated for emerging threats and multivector attacks, ensuring your detection logic stays current.
Log360 Cloud now features Zia Insights, a contextual AI engine powered by Azure OpenAI (BYOK). Analysts can now:
This release transforms threat investigation workflows— delivering clarity, acceleration, and actionable insights within your SIEM interface.