Proactive threat prevention
Combine behavioral analysis, AI-driven detection engines, and live threat intelligence to neutralize ransomware, malware, and zero-day exploits at the perimeter, before they reach an endpoint.
Endpoint Central unites comprehensive security features built to prevent attacks, contain breaches, and automate your IT security, without the tool sprawl.




Combine behavioral analysis, AI-driven detection engines, and live threat intelligence to neutralize ransomware, malware, and zero-day exploits at the perimeter, before they reach an endpoint.
Enforce granular control over applications, peripherals, and user privileges. Lock down USB access, blocklist unauthorized software, and remove the openings attackers rely on.
Move beyond static defenses. Monitor device compliance as it happens, flag risky configurations, and enforce security baselines to keep every endpoint healthy and policy-aligned.
When a threat gets through, trigger automated remediation, run forensic analysis, and restore endpoint integrity with no downtime, turning a potential breach into a contained event.
Isolate compromised endpoints from the network the moment a threat is flagged, terminate malicious processes, and stop lateral movement before it spreads across your fleet.
Zia's autonomous agents cut the manual load. The EDR triage agent investigates alerts and maps the attack chain, while the patch troubleshooting agent diagnoses failed deployments and surfaces root-cause fixes.
Maintain alignment with PCI-DSS, HIPAA, and GDPR through enforced encryption, data access controls, and integrated DLP, with audit-ready reporting available on demand.
Eliminate unauthorized access across every layer. Restrict peripherals, enforce least-privilege policies, and gate access to critical systems through conditional and zero trust network controls.
Keep every stakeholder informed without the manual effort. Schedule executive reports covering asset health, threat exposure, patch status, and policy compliance, delivered automatically on your defined cadence.
Full-lifecycle security that prevents threats early, contains active ones, and recovers securely from the rest.
Predict where you're exposed and impose controls to minimize risk before a threat ever reaches your endpoints.
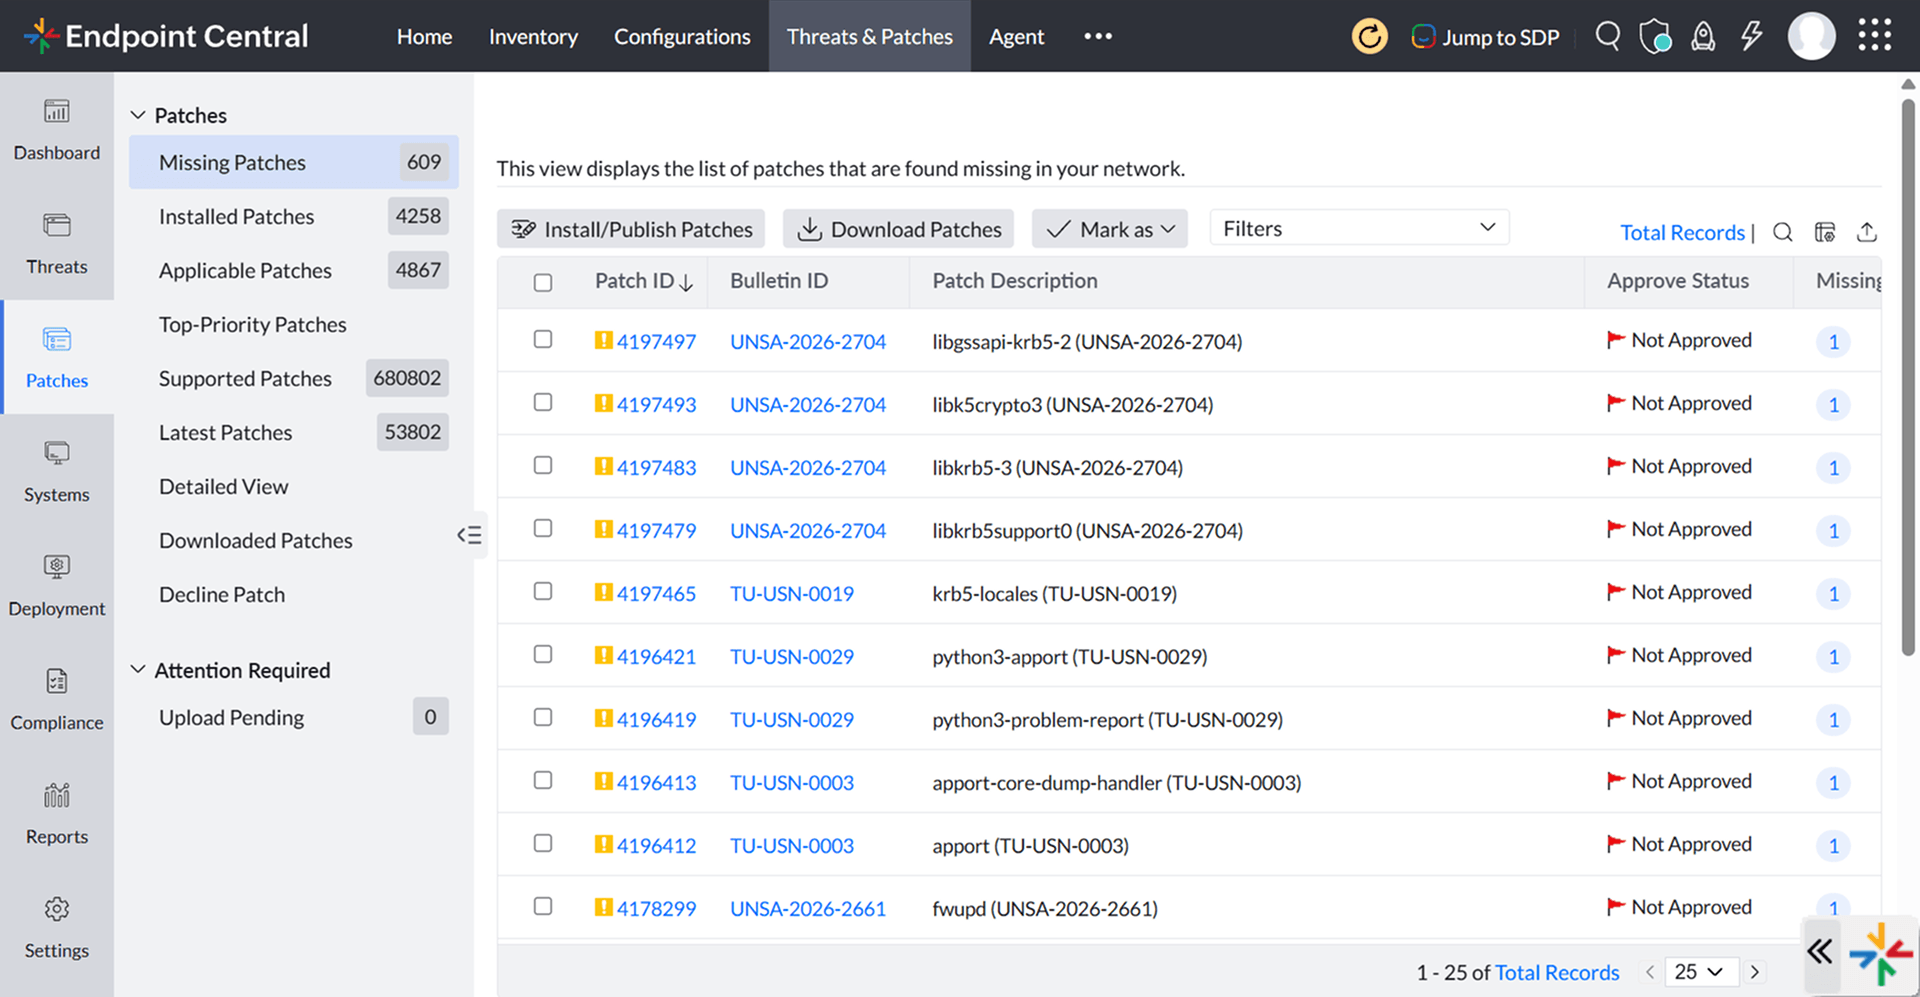
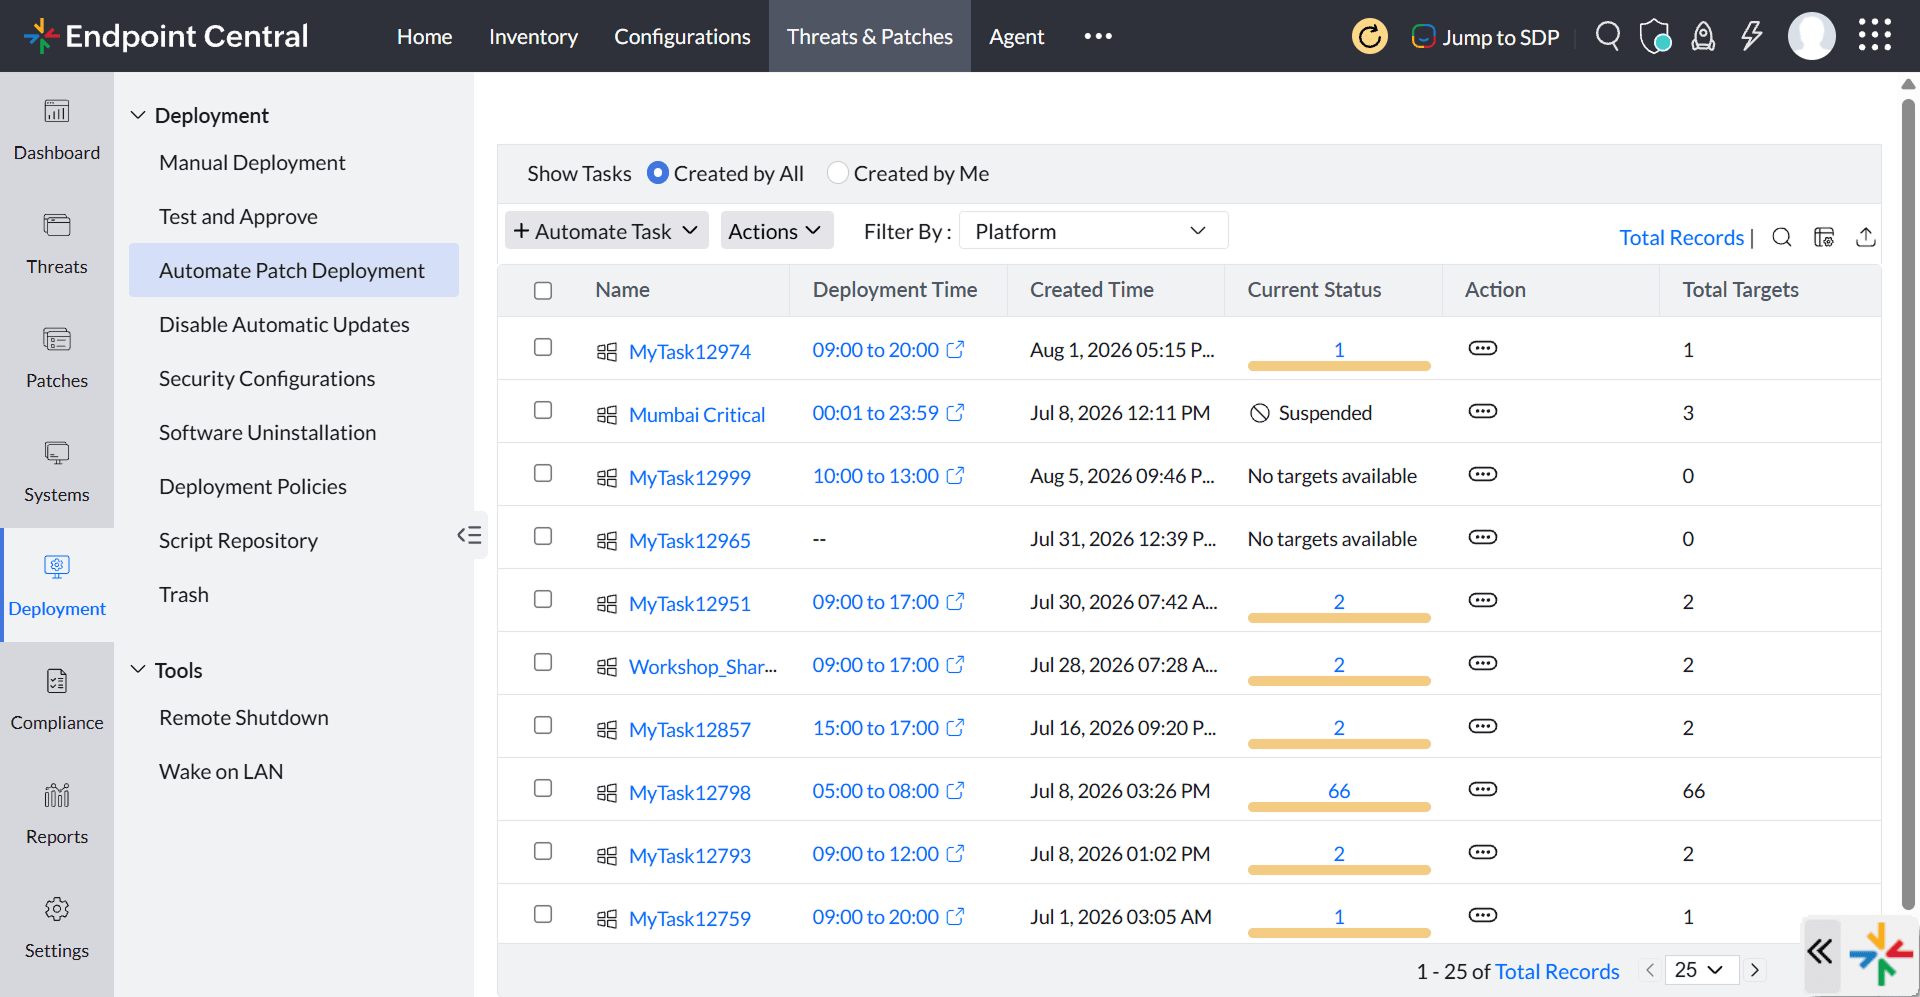
Automatically detect and deploy missing OS and third-party patches across Windows, macOS, and Linux. Closing these gaps early removes the known flaws attackers exploit most, shrinking your attack surface before a threat arrives.
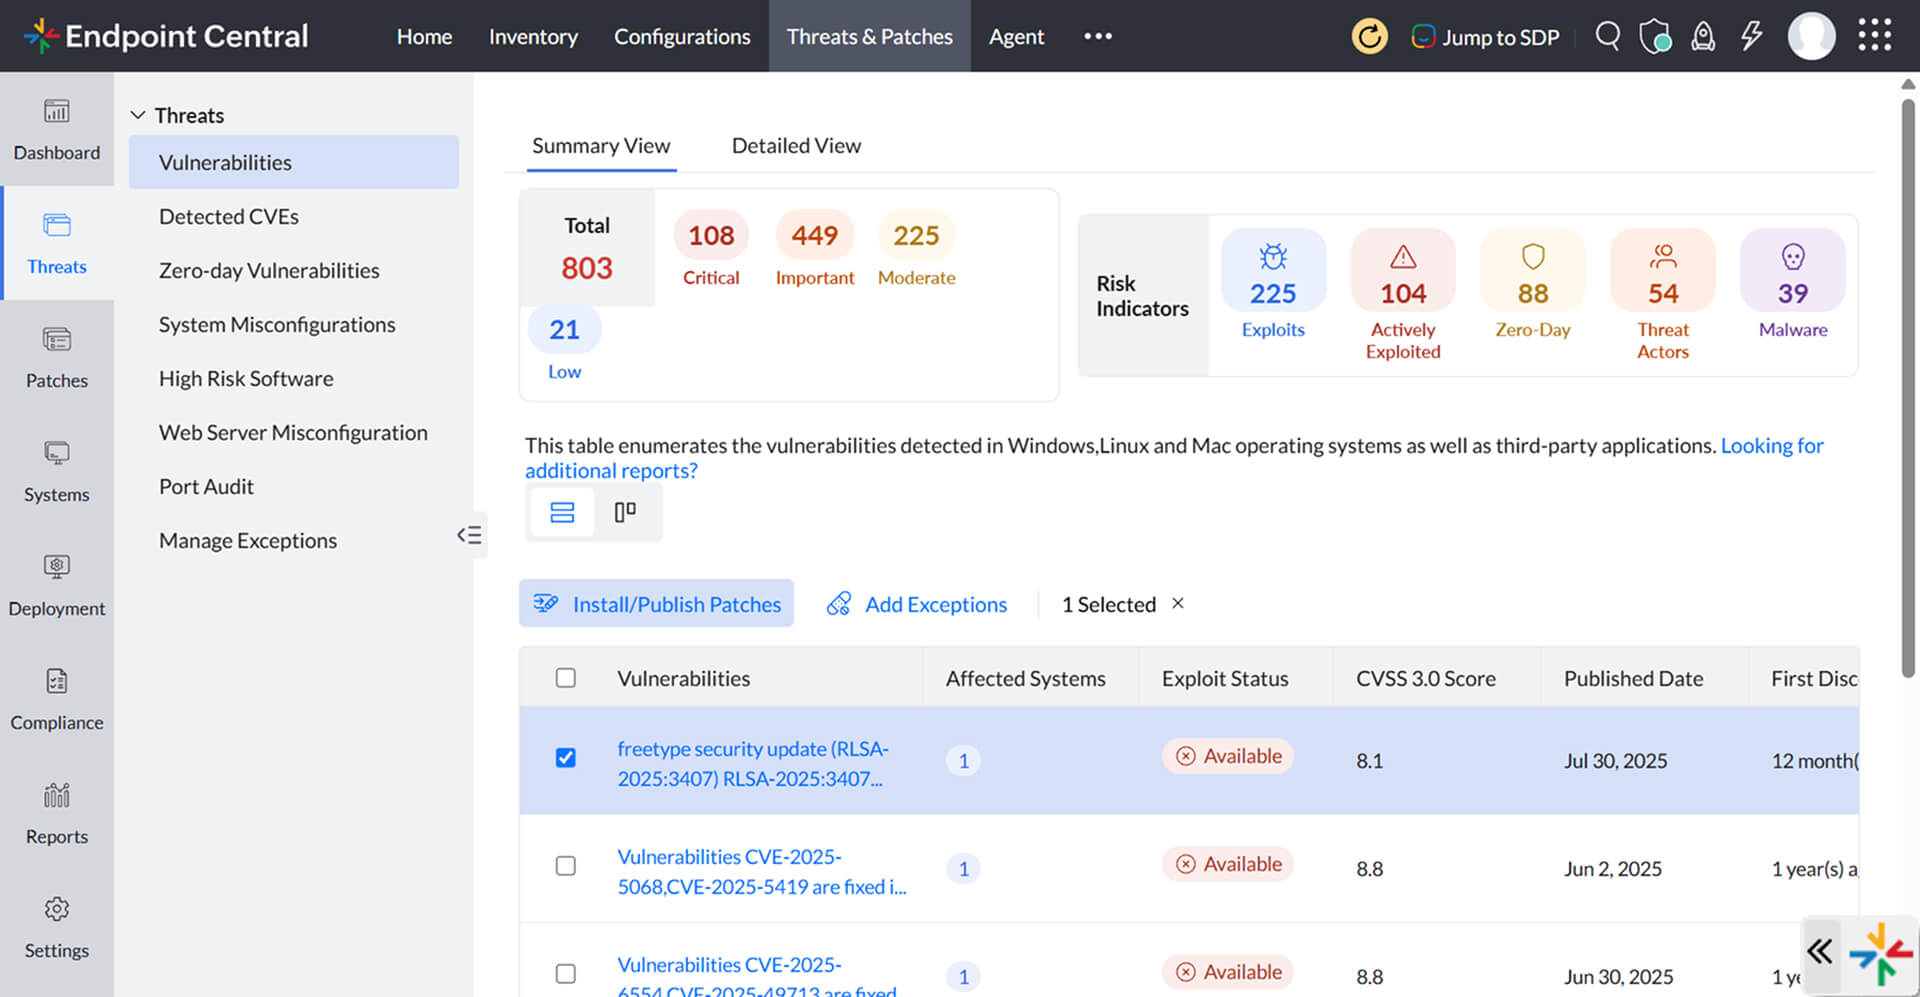
Continuously scan for known CVEs and misconfigurations. By identifying weaknesses early, you can remediate exploitable flaws before attackers find them, drastically reducing your threat surface.
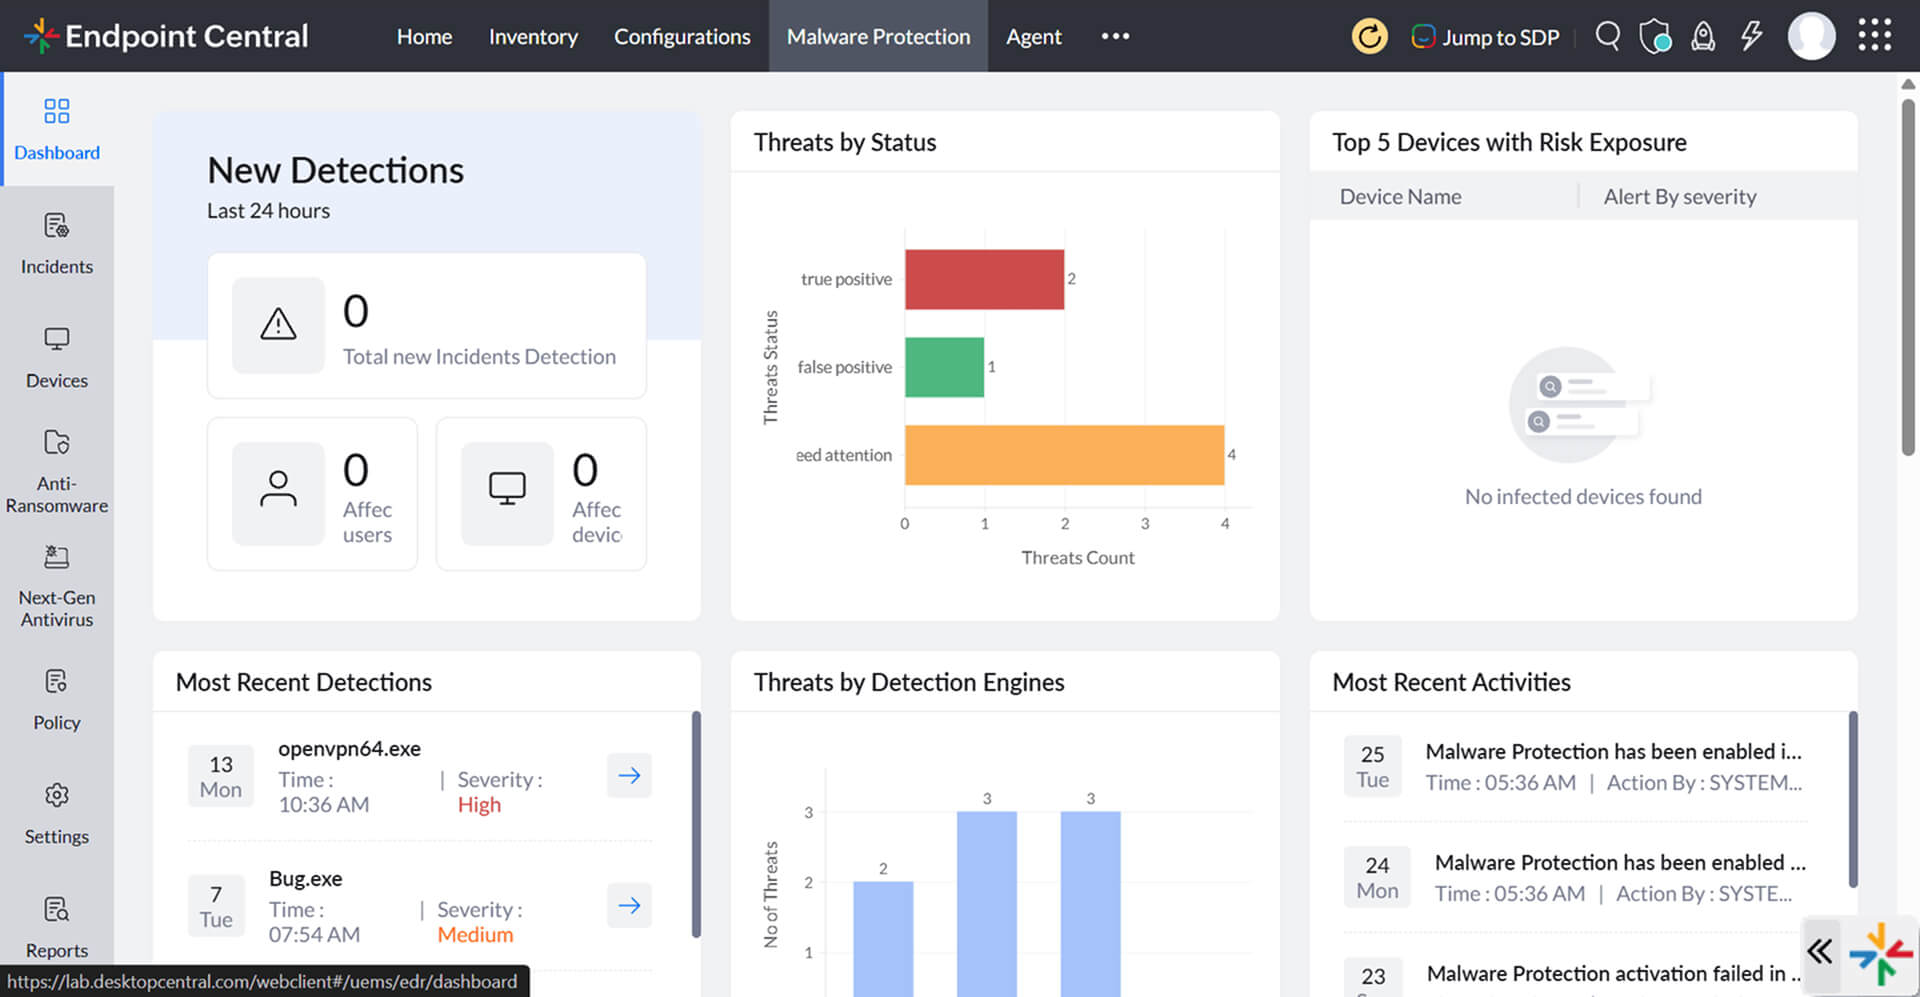
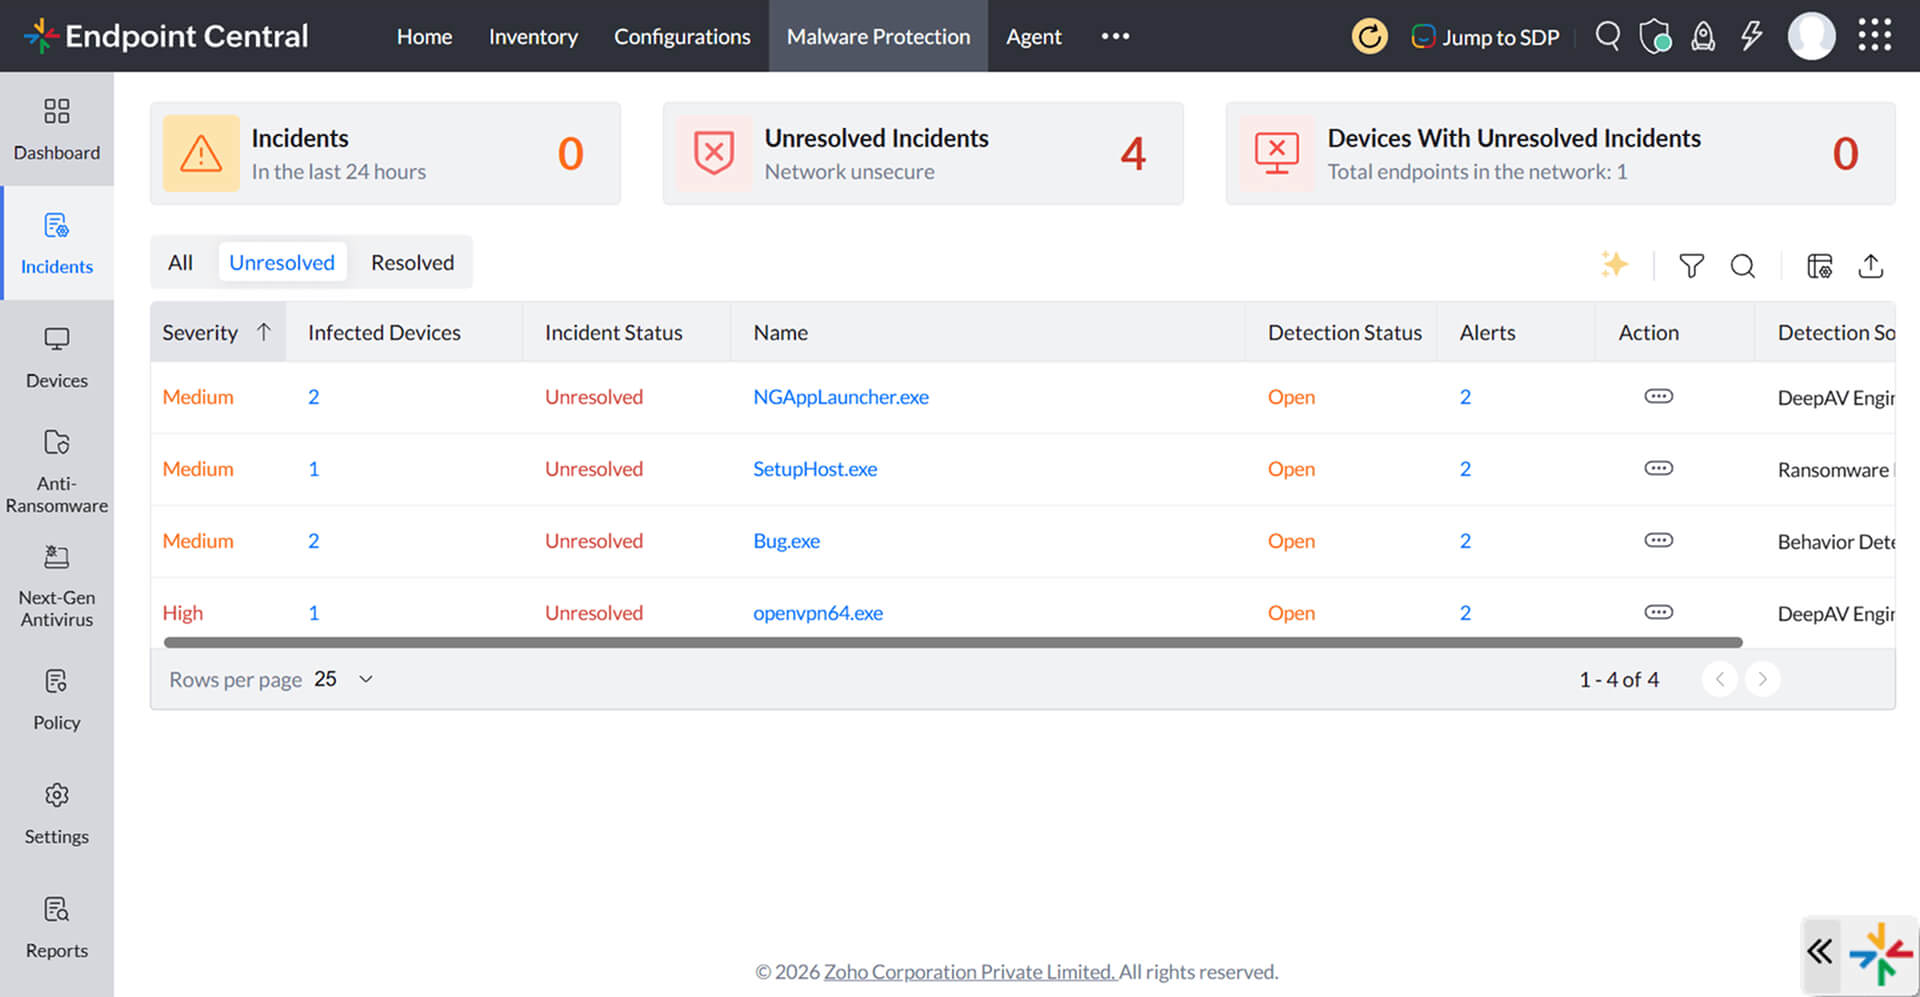
Next-Gen Antivirus pairs deep-learning and behavior-based detection with anti-ransomware to catch known and unknown malware, including fileless attacks, in real time, online or offline. Threats are identified and blocked before they can execute and take hold.
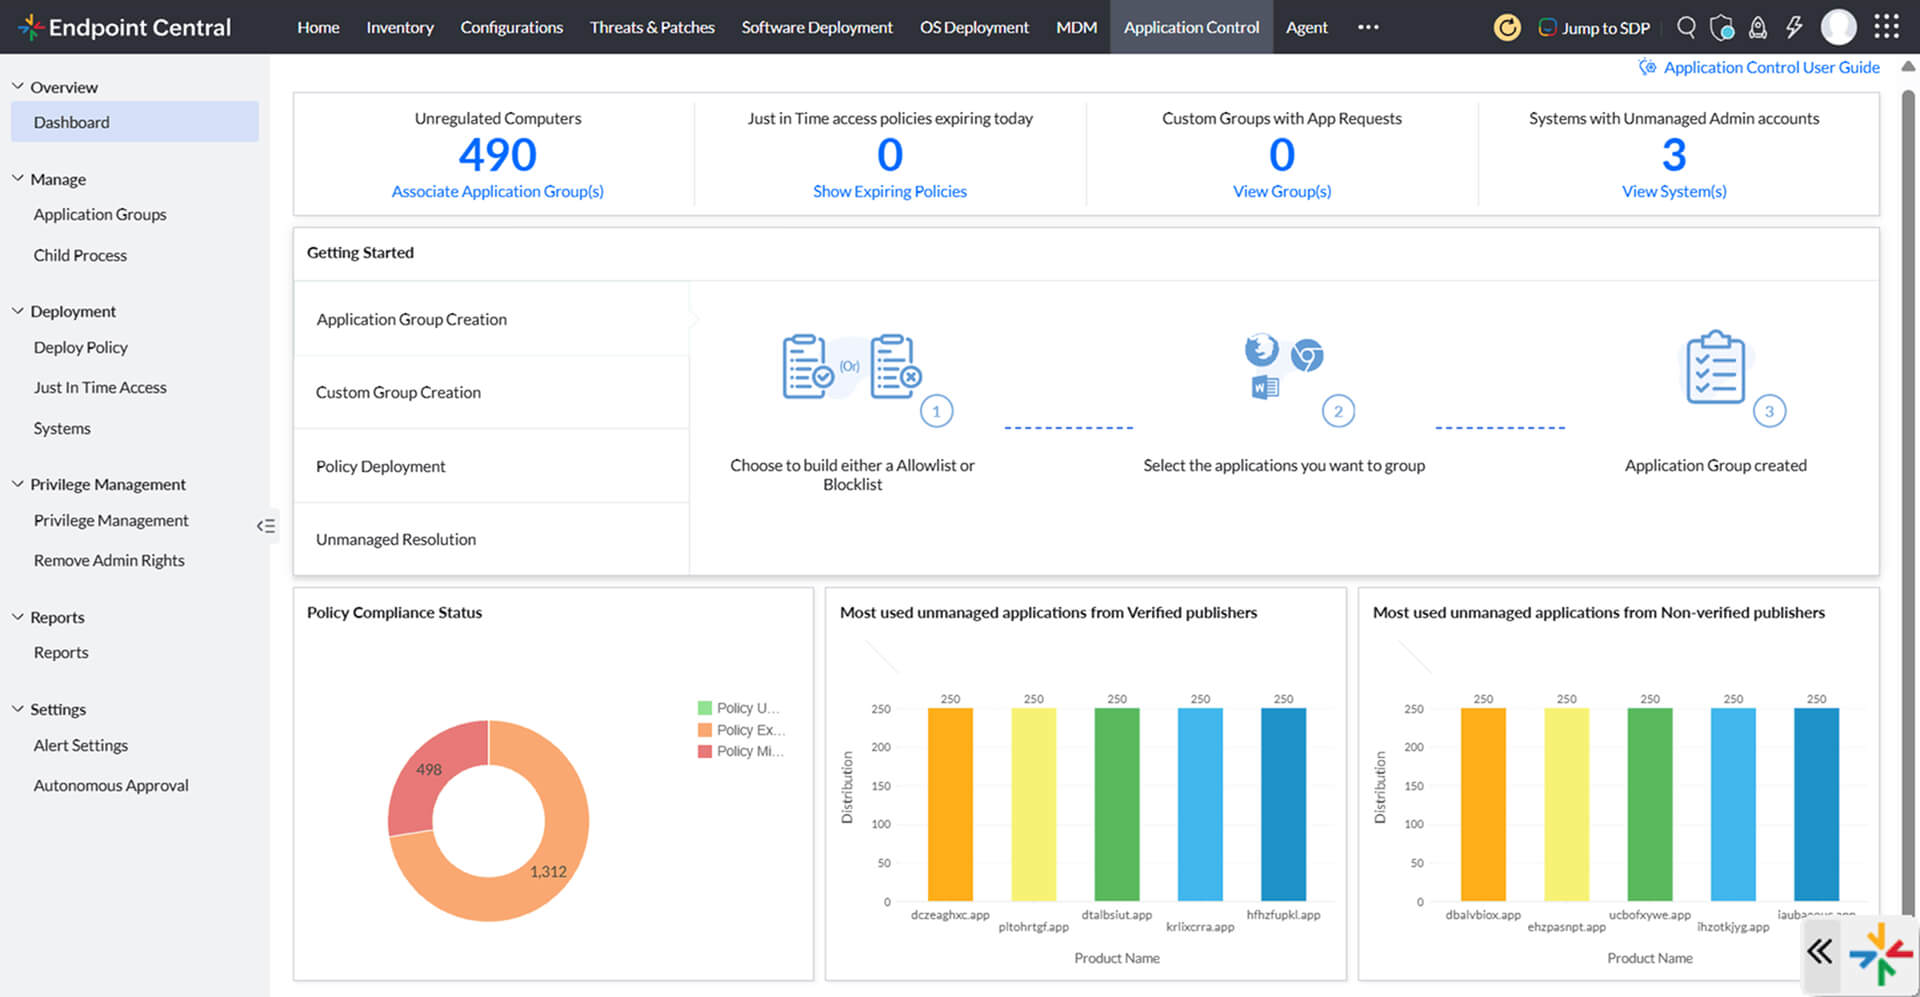
Allowlist trusted software and block everything else. Preventing unauthorized applications from running removes a common entry point long before an attacker can use it.
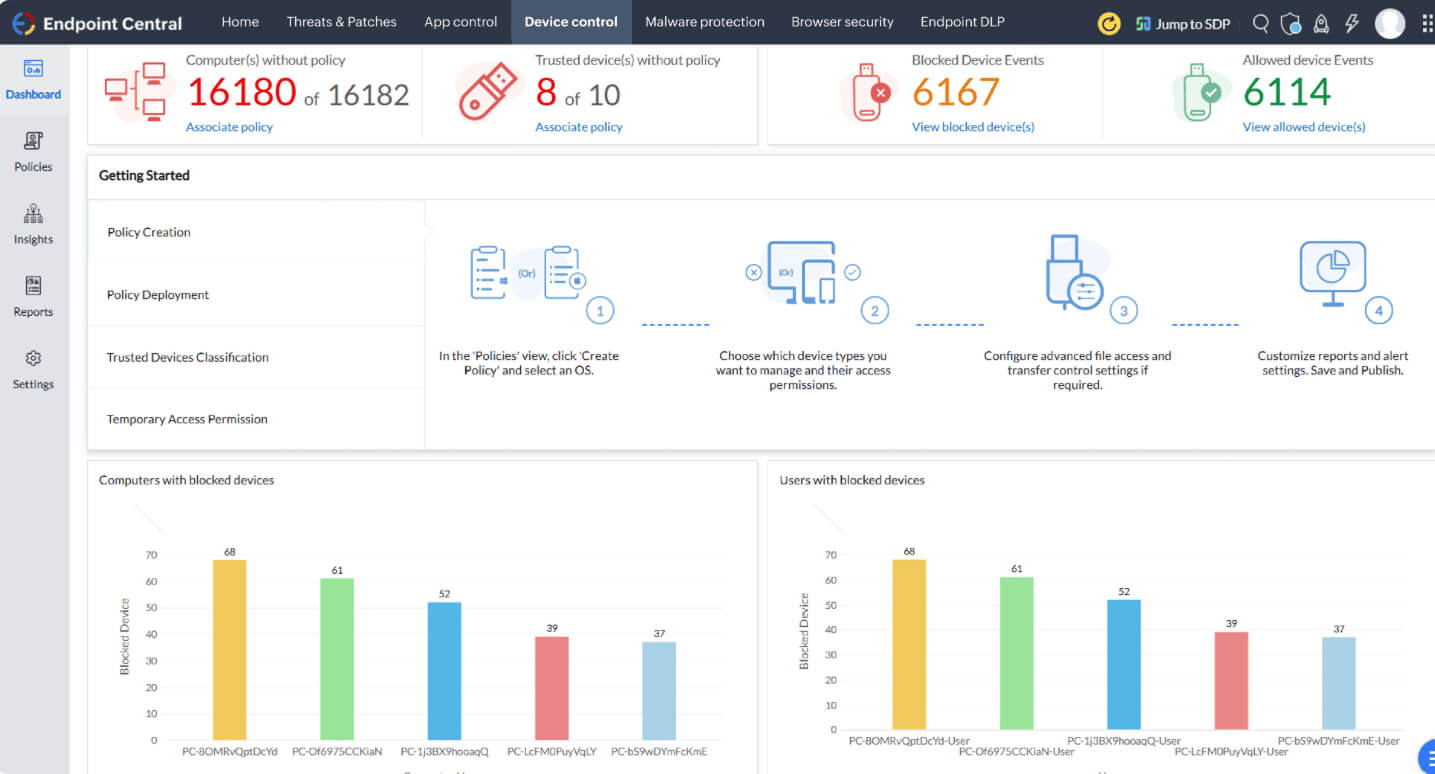
Govern USB and peripheral access with role-based policies. Locking down external devices in advance closes off a frequent path for malware and data theft.
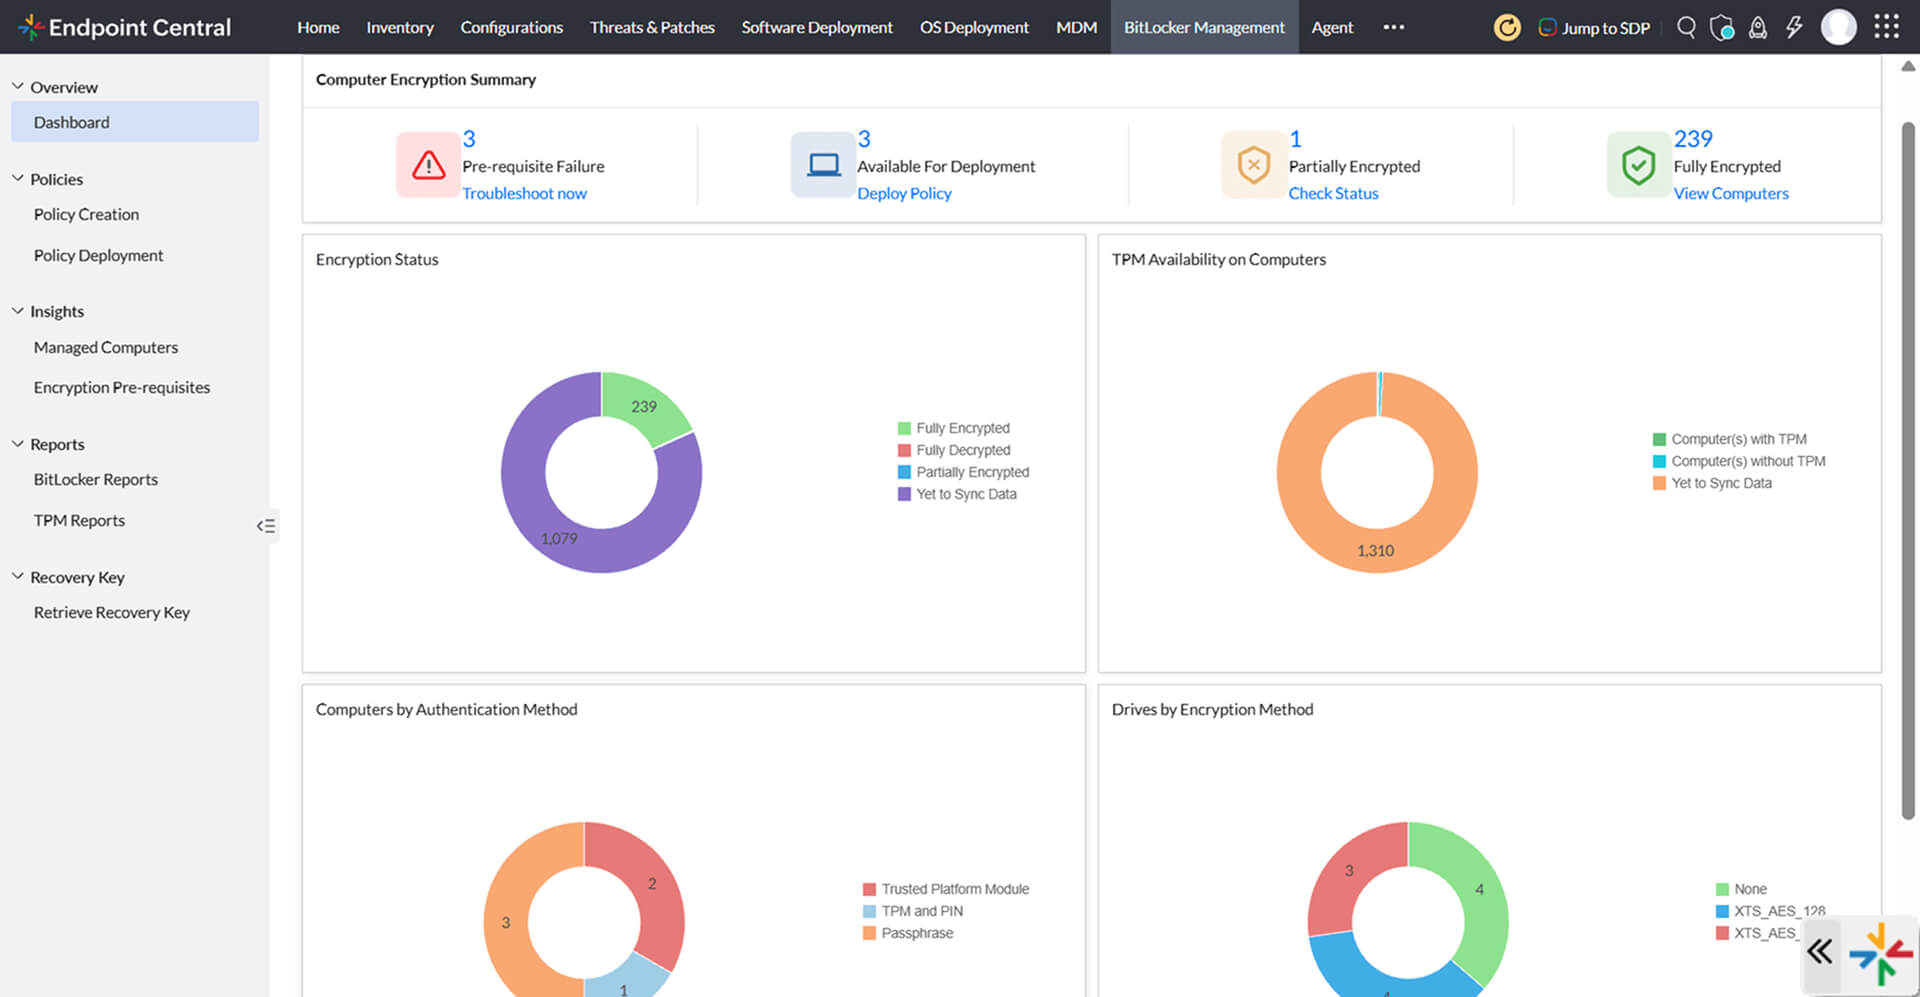
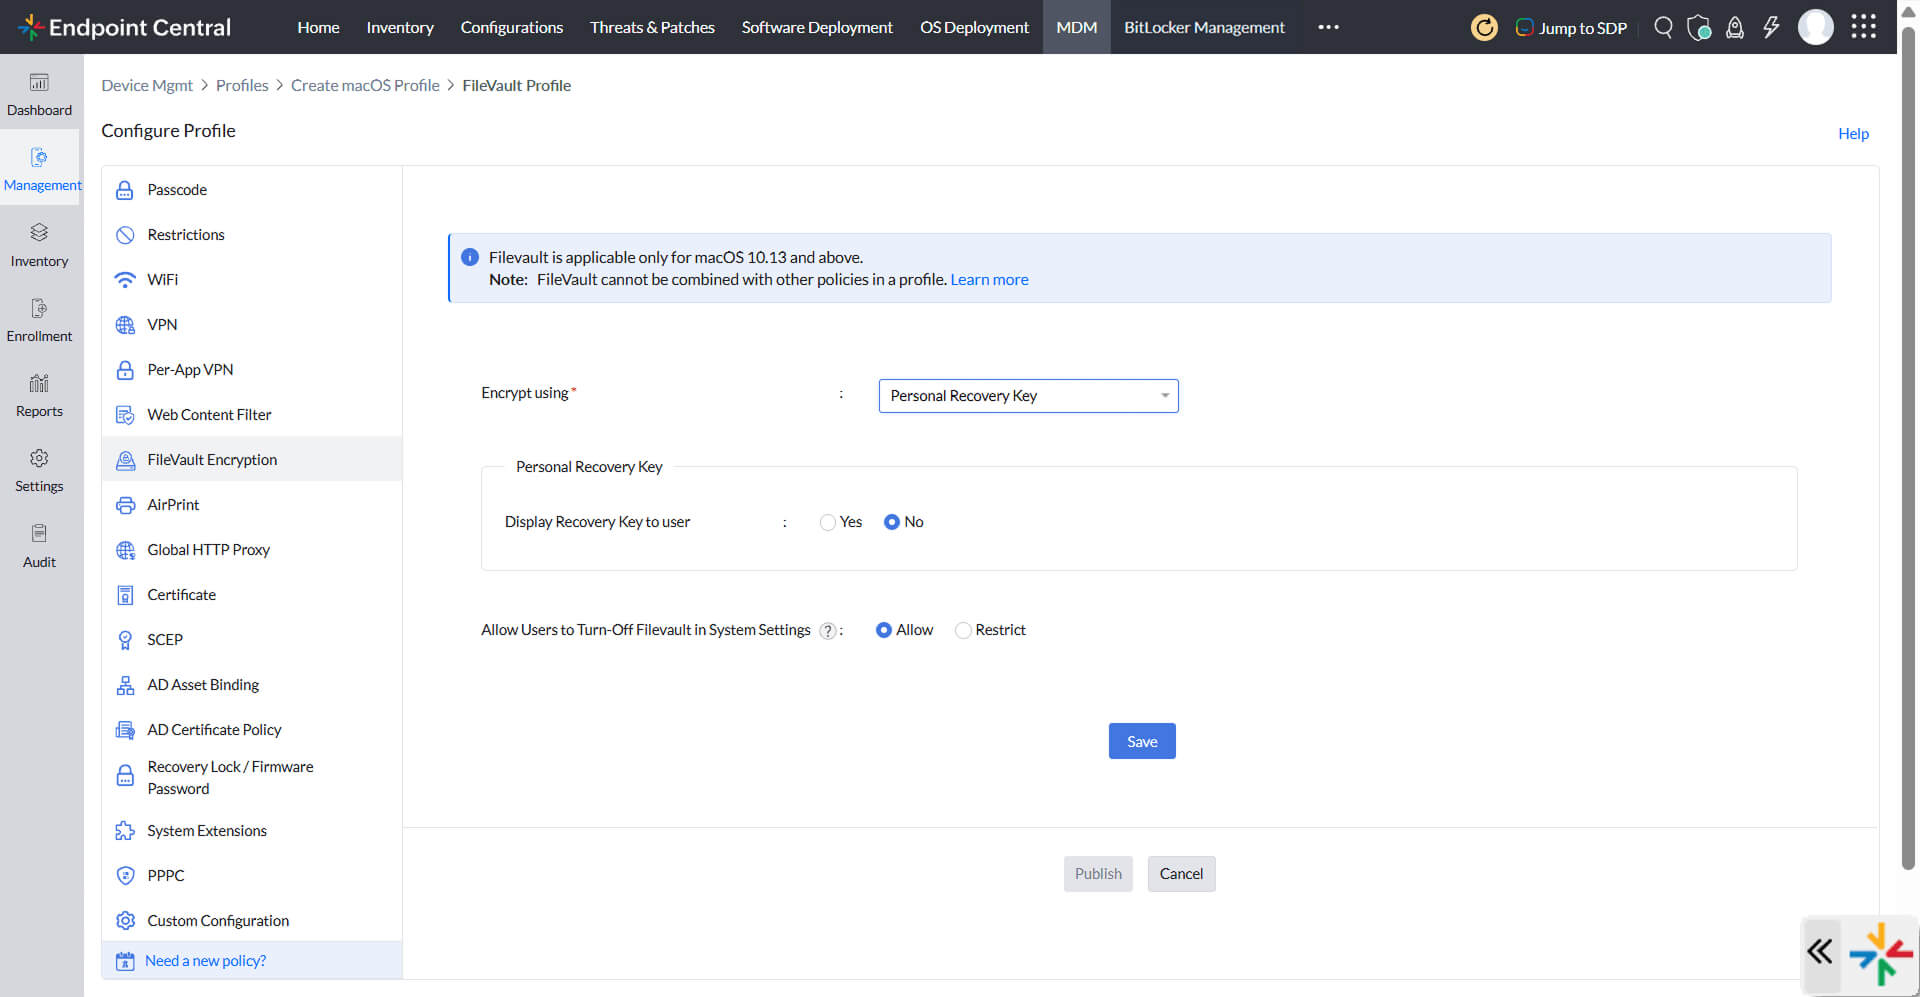
Centrally enforce full-disk encryption and manage recovery keys. Encrypting data at rest ahead of time means a lost or stolen device never becomes a breach.
Even the strongest defenses can be tested. Endpoint Central detects active threats early and shrinks the attack surface to keep them from spreading.
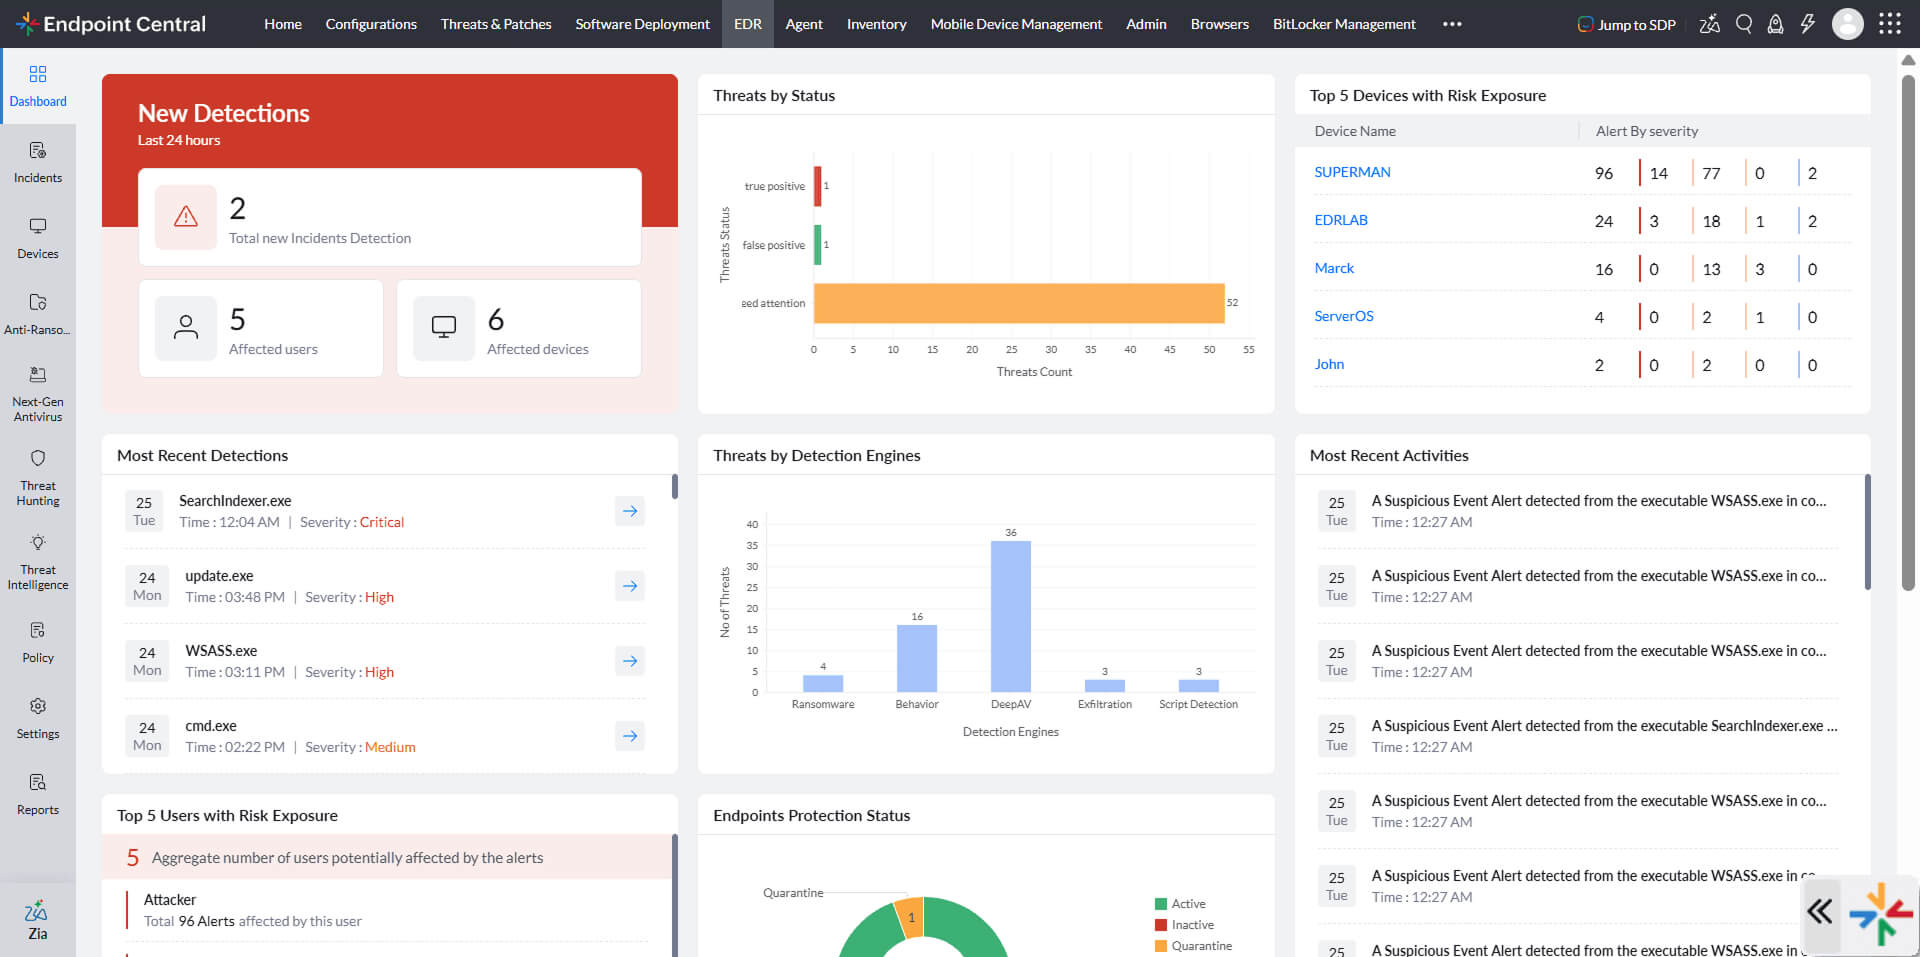
Continuously monitor endpoint telemetry to surface threats that slip past other defenses. Guided investigation and MITRE ATT&CK-mapped detections let you spot and act on an active attack in real time.
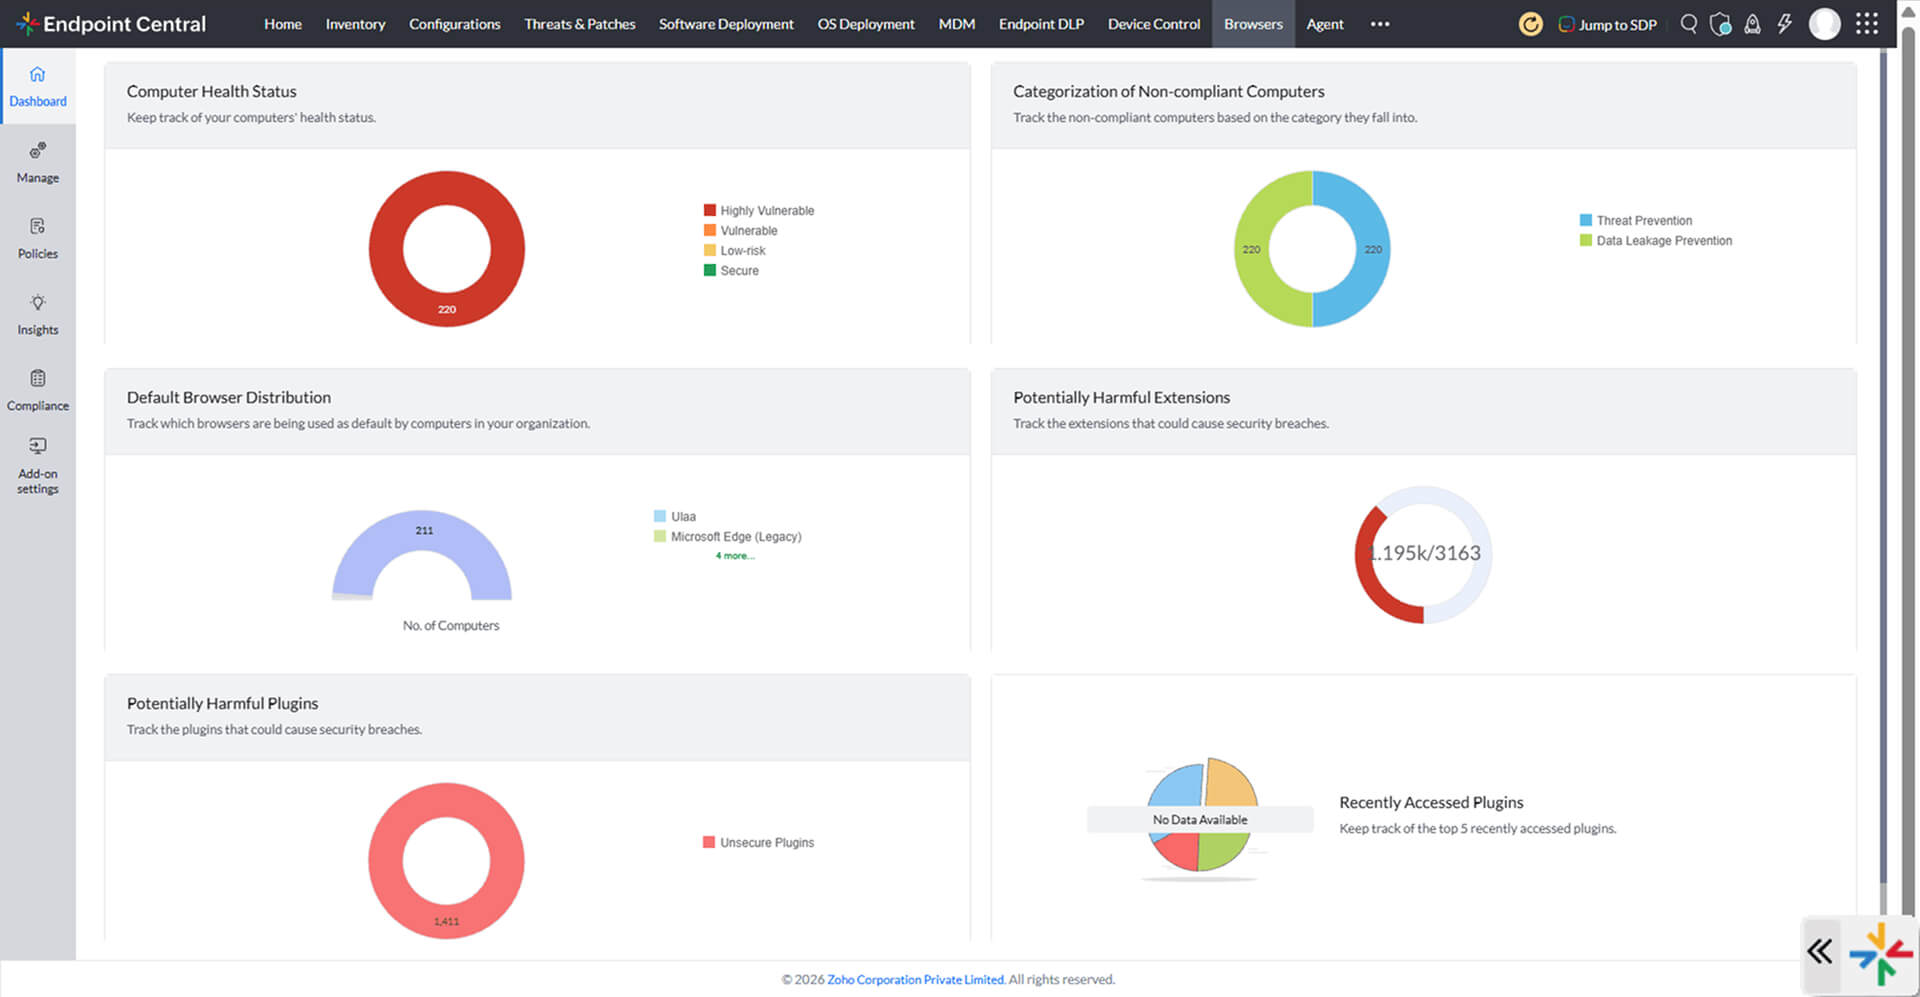
Enforce safe browsing policies and control extensions during an active campaign. Blocking phishing sites and risky downloads at the source stops credential theft before it succeeds.
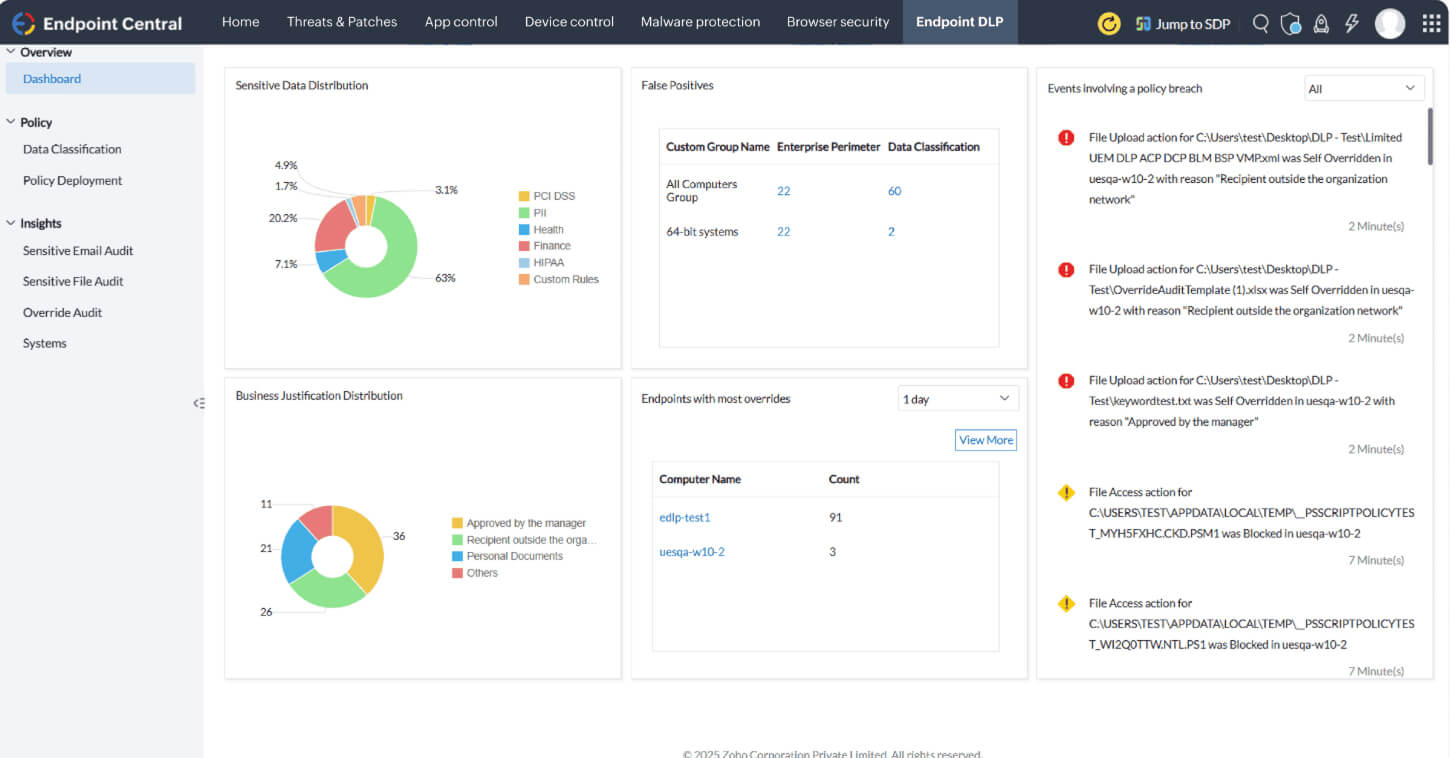
Monitor and restrict sensitive data transfers over USB, email, and cloud. When an endpoint is compromised, DLP keeps the incident from turning into an exfiltration event.
Contain the incident, recover affected data, and capture a full audit trail to minimize impact and prevent recurrence.
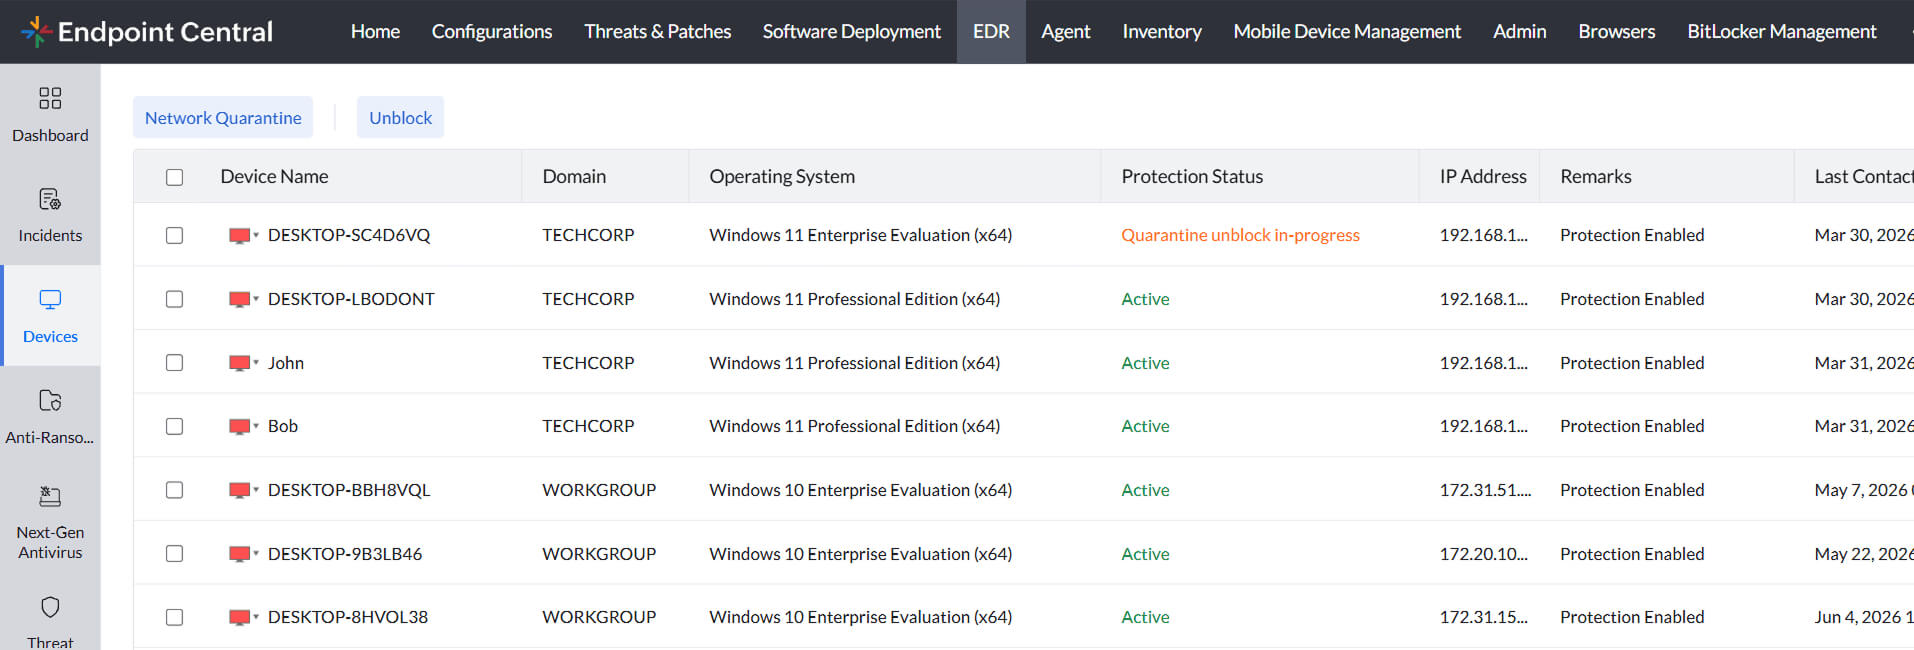
Instantly cut a compromised device off from the network and terminate malicious processes. Containing the endpoint stops lateral movement before a single machine becomes a fleet-wide breach.
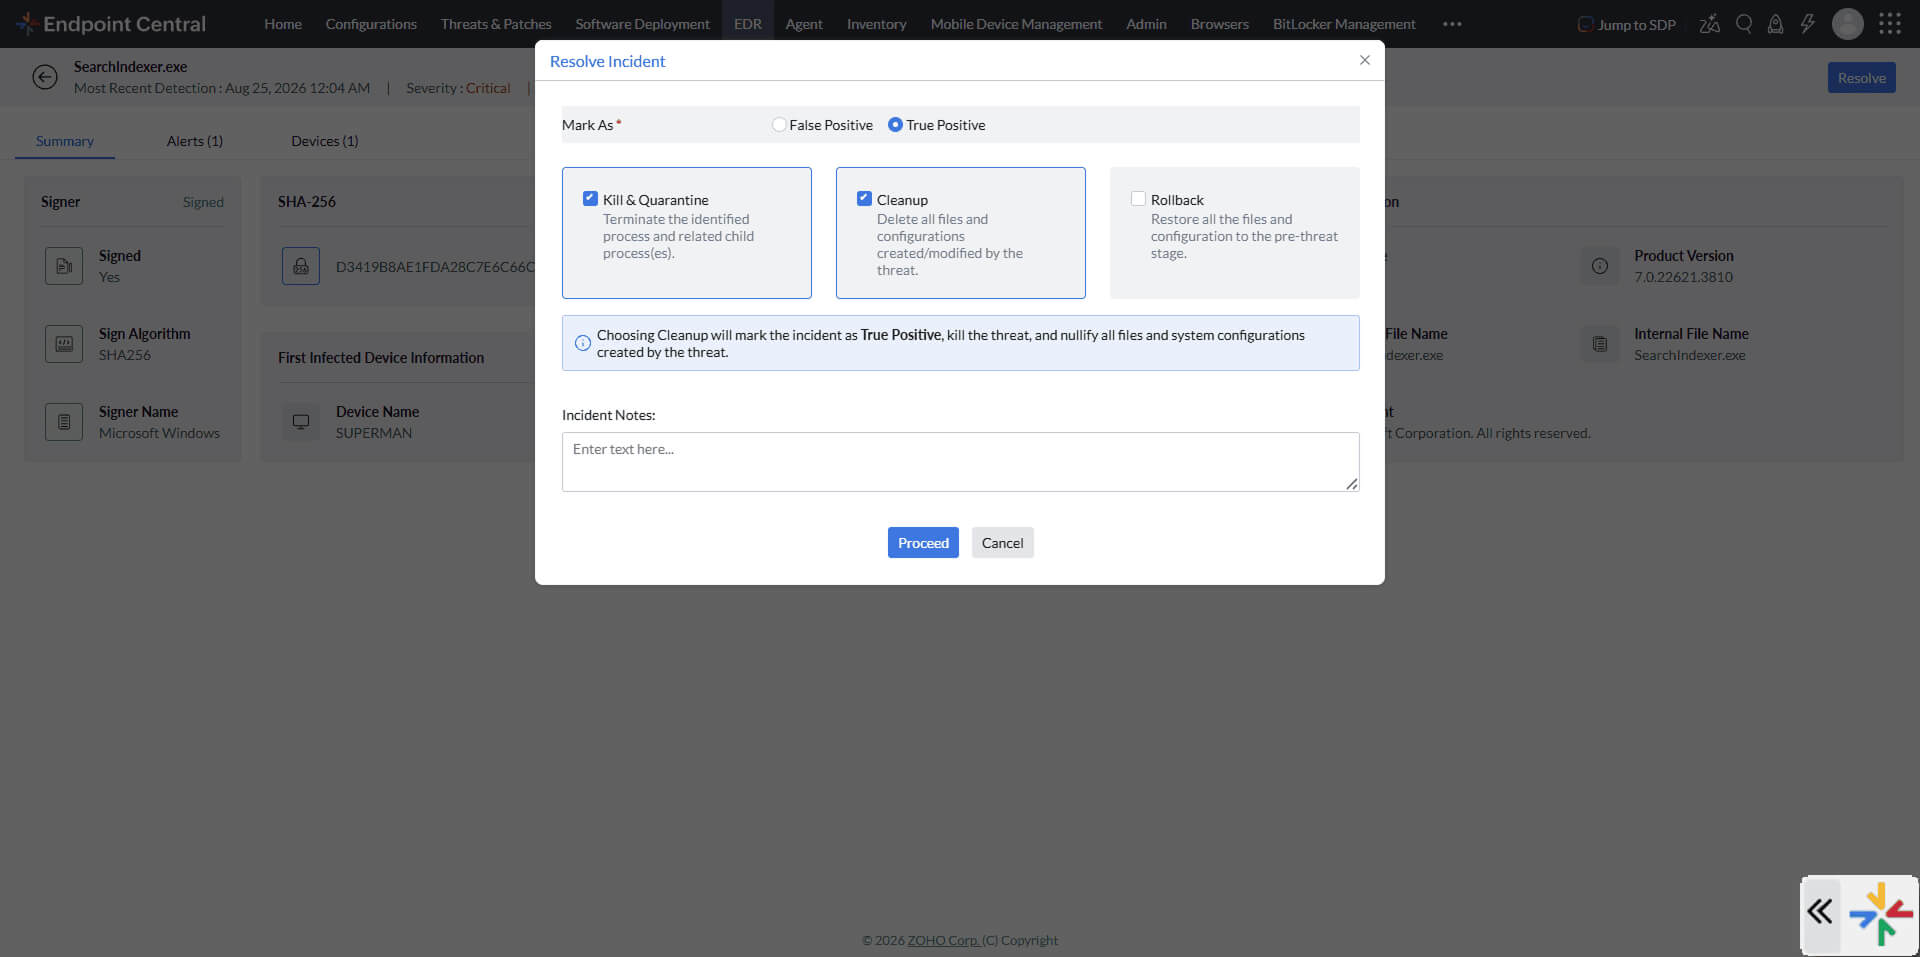
Delete every file, registry entry, and configuration change left behind by a threat, removing all traces of the attack and restoring the endpoint to a clean, trusted state.
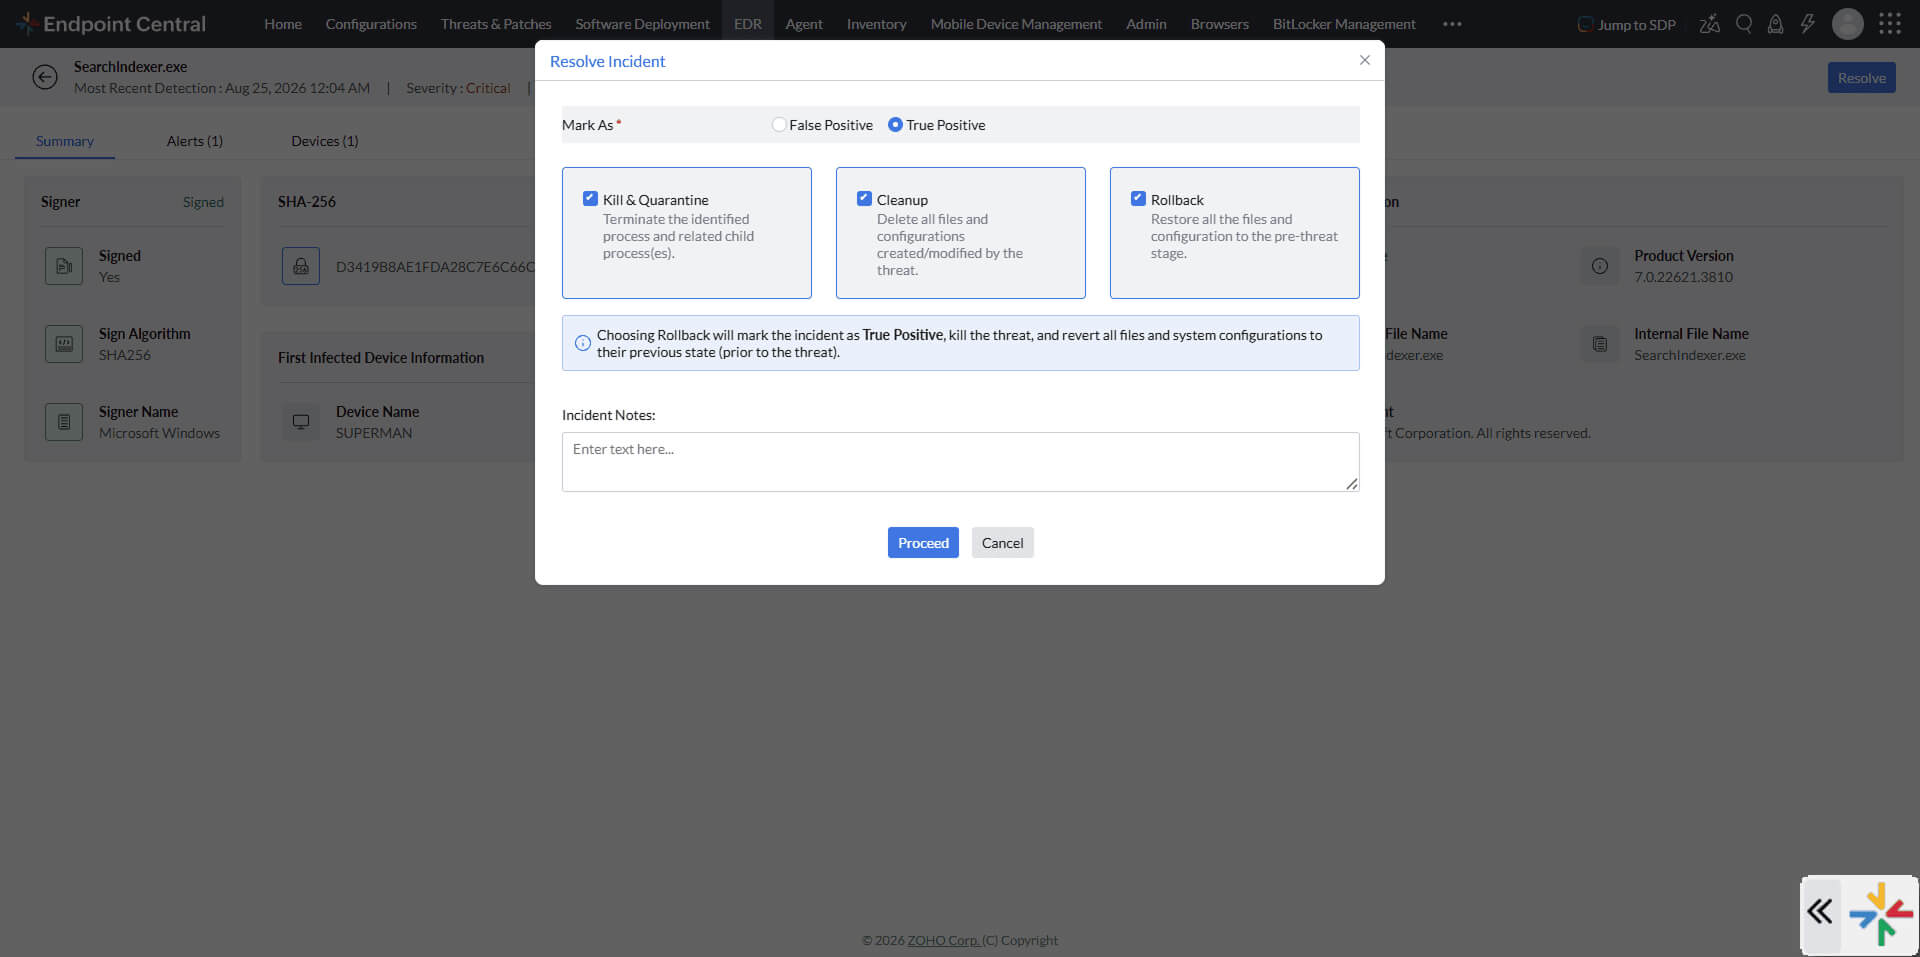
Restore files and registries to their pre-attack state with a single click, backed by a tamper-proof backup system. Even after ransomware strikes, recovery means no data is lost.
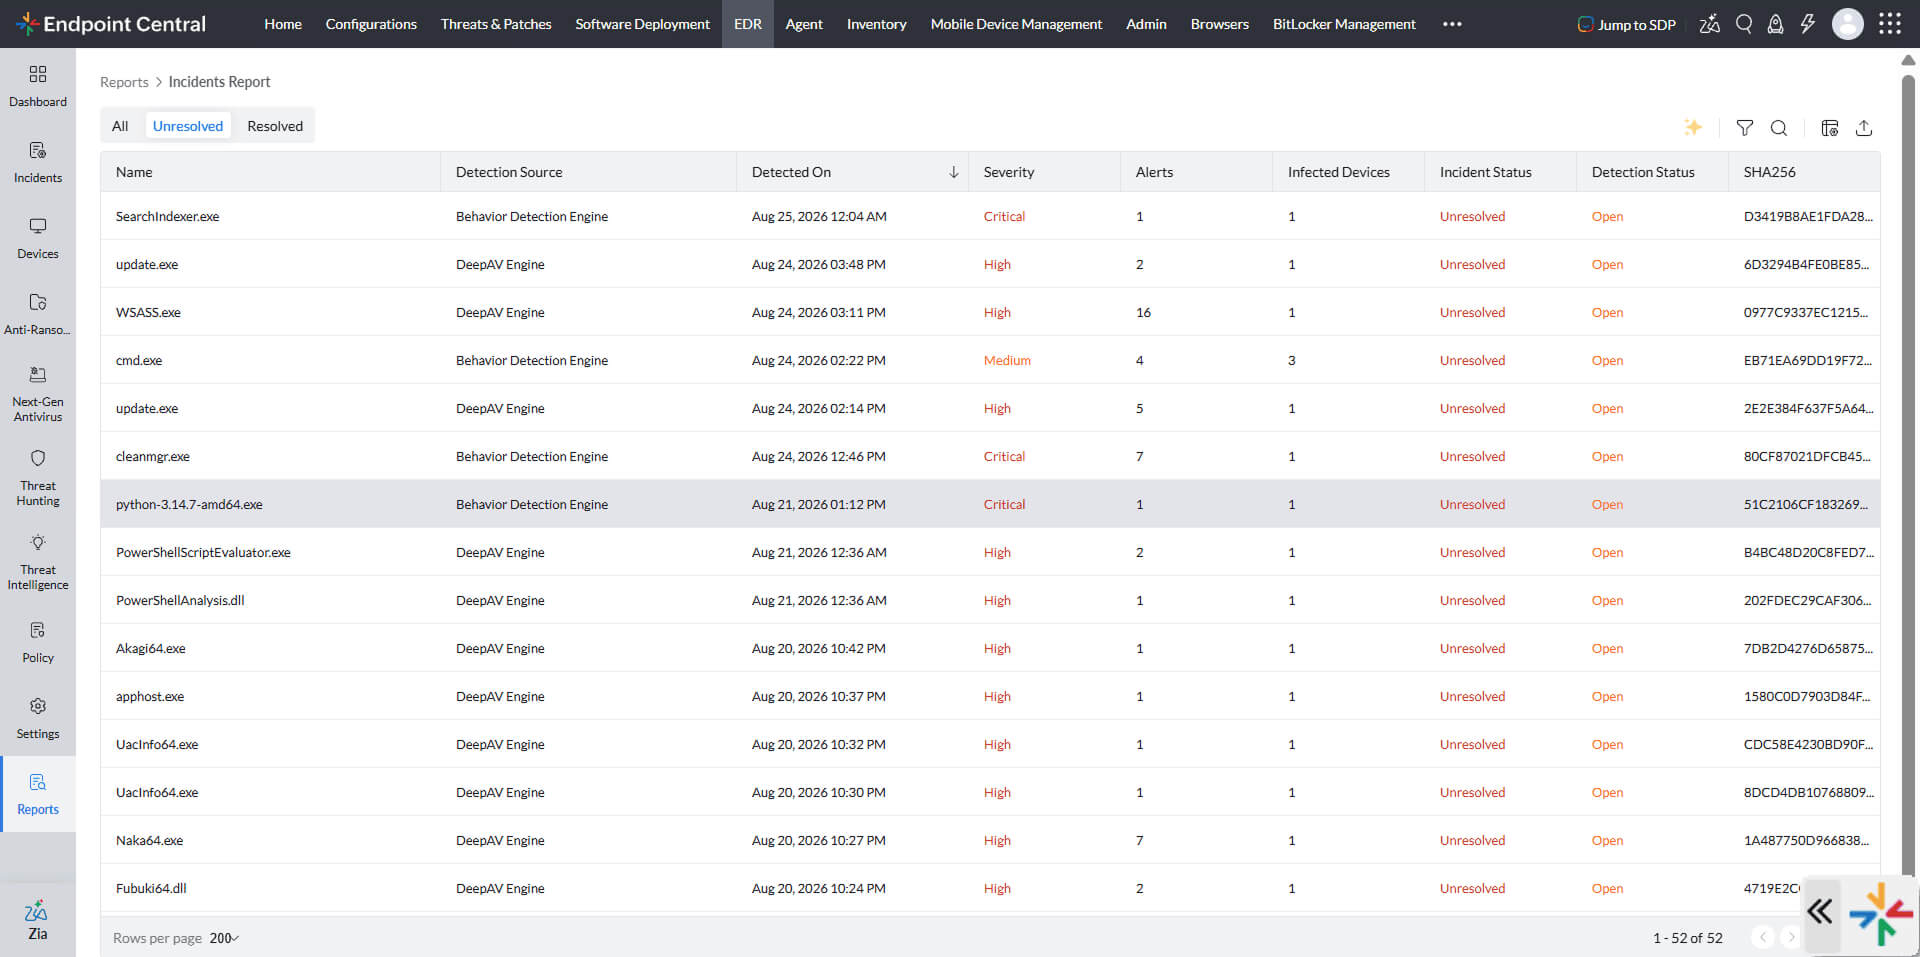
Generate detailed root-cause analysis and incident reports for every event. A complete audit trail supports compliance obligations and hardens defenses against the next attempt.
Track posture and enforce baselines across every device, on-site, remote, or mobile, without a break in visibility.
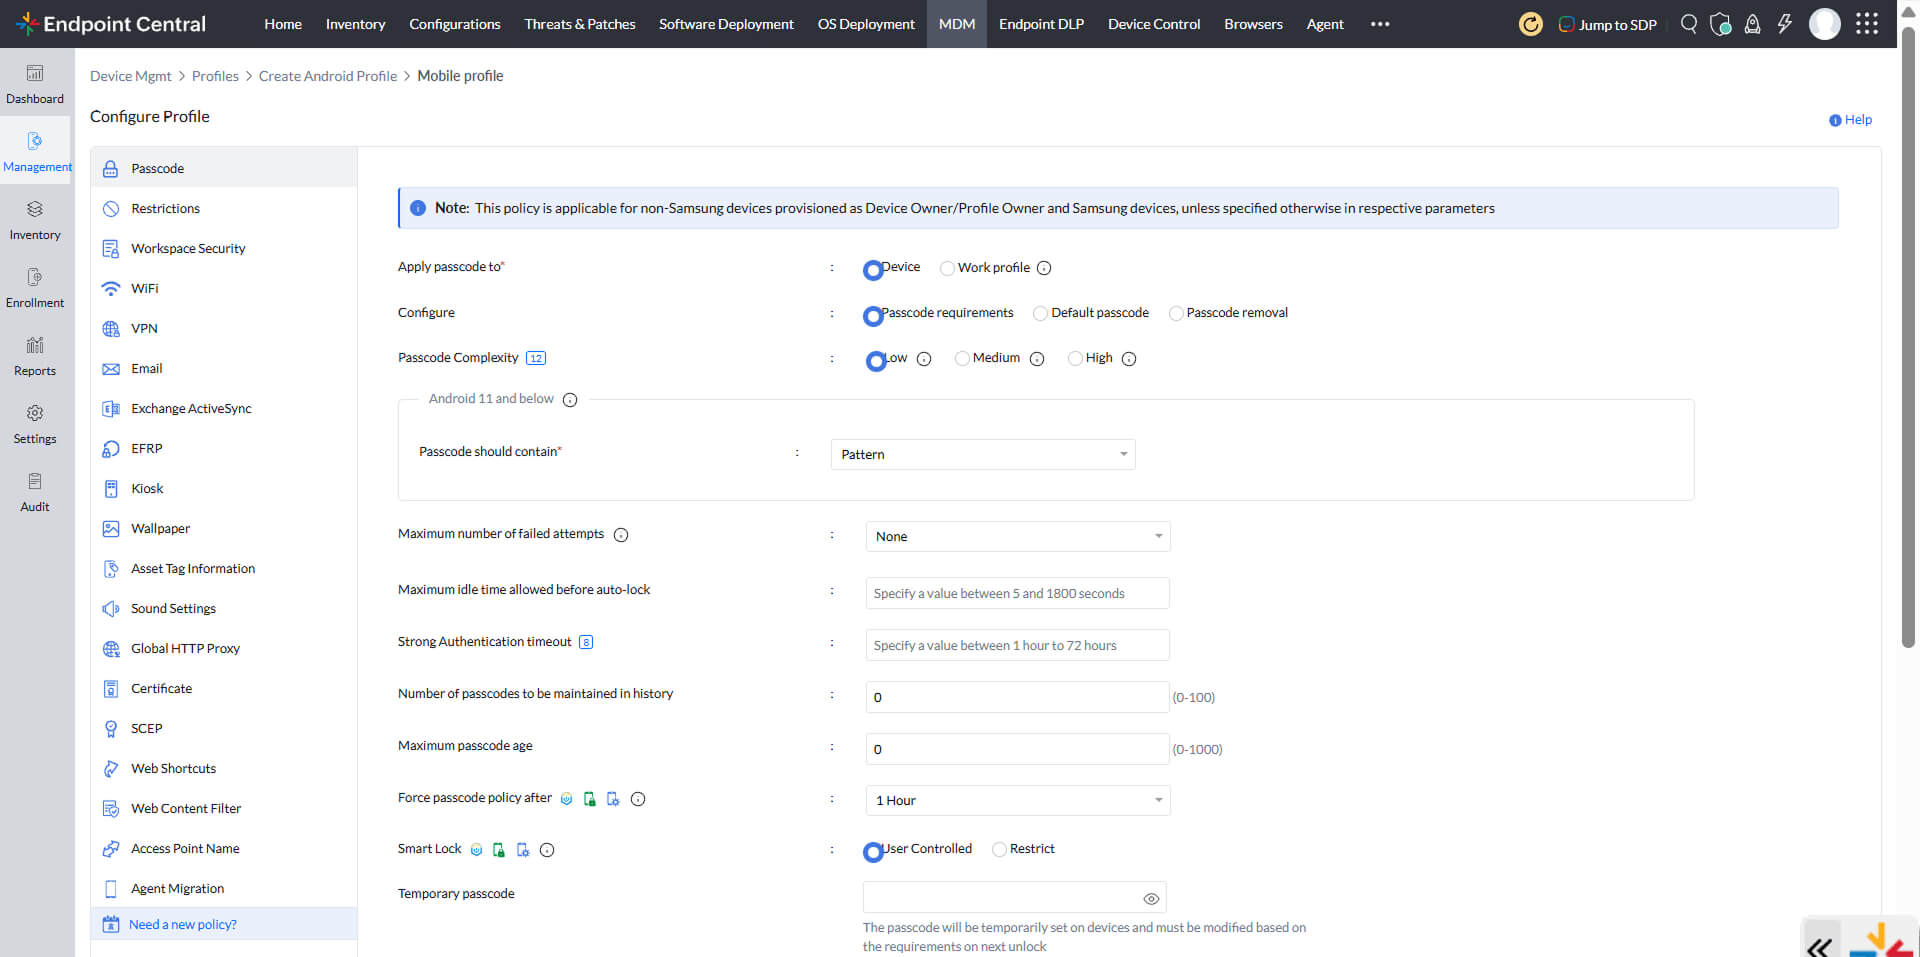
Extend the same continuous oversight to phones and tablets. Enforce BYOD policies, apply conditional access, and remotely wipe lost devices to keep mobile endpoints in a known-good state.
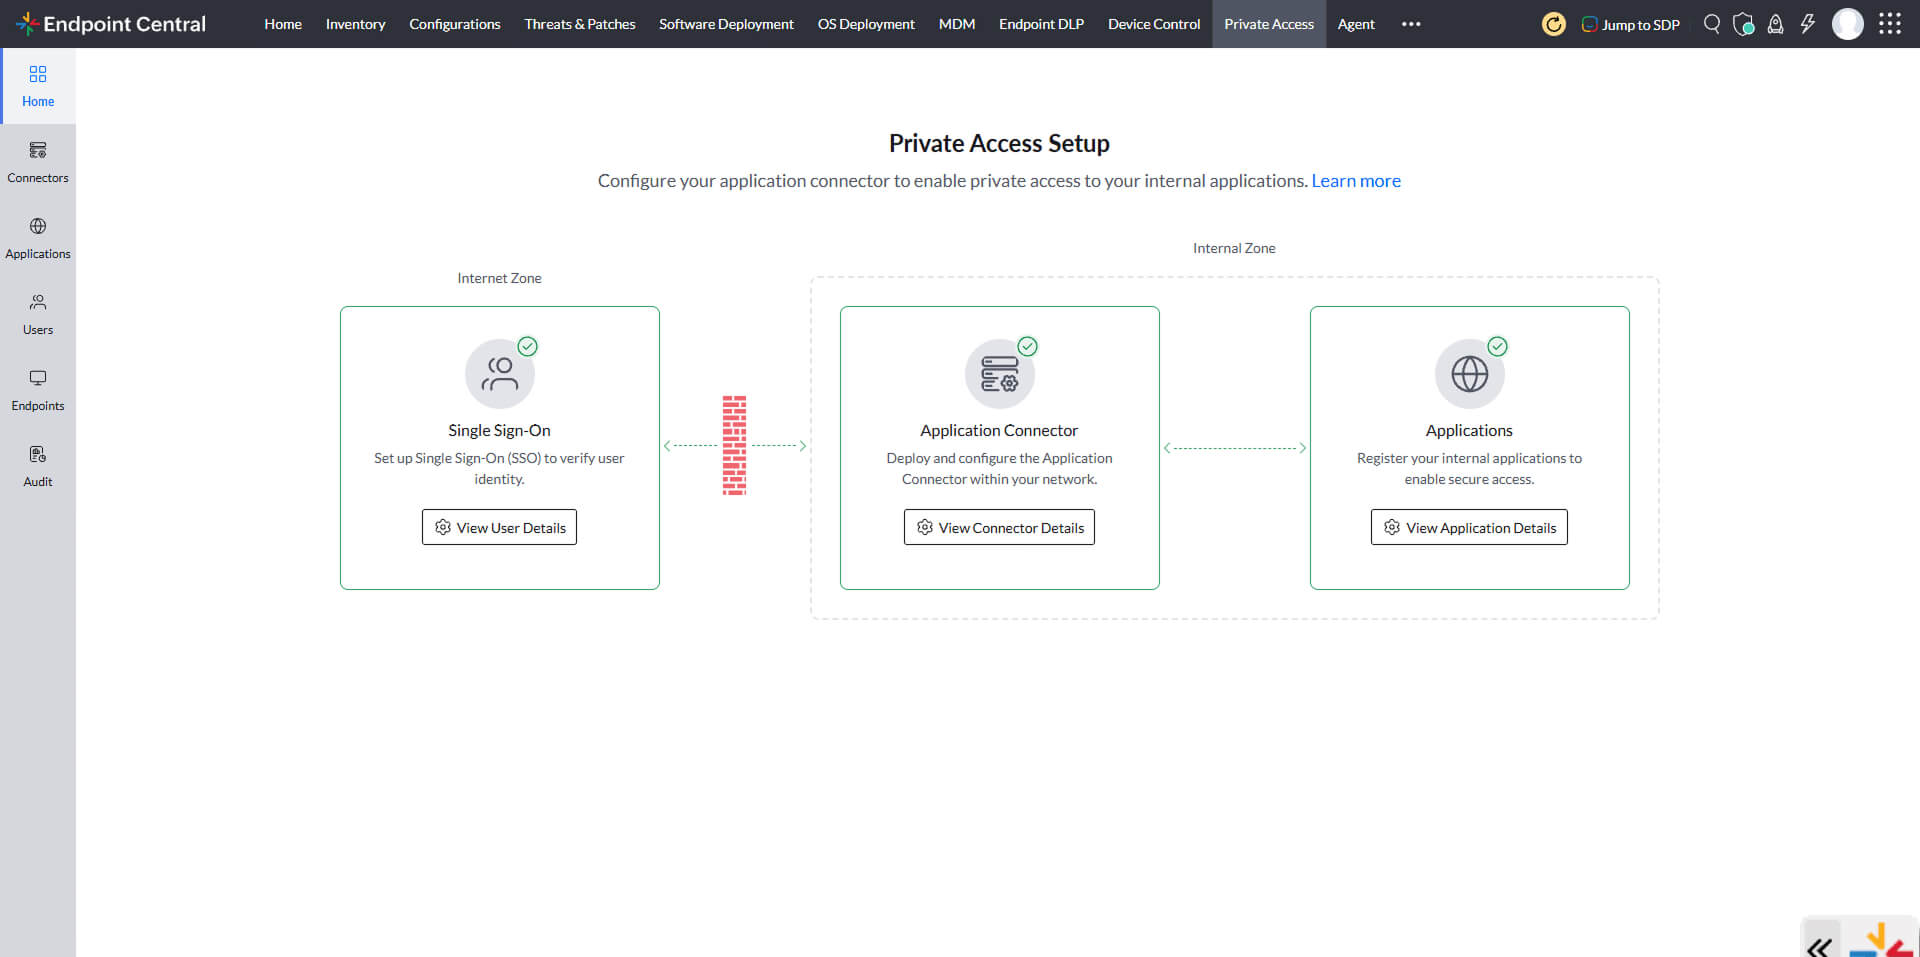
Give remote and hybrid users VPN-free access to internal apps with continuous, context-aware policy checks that verify user and device trust on every connection.
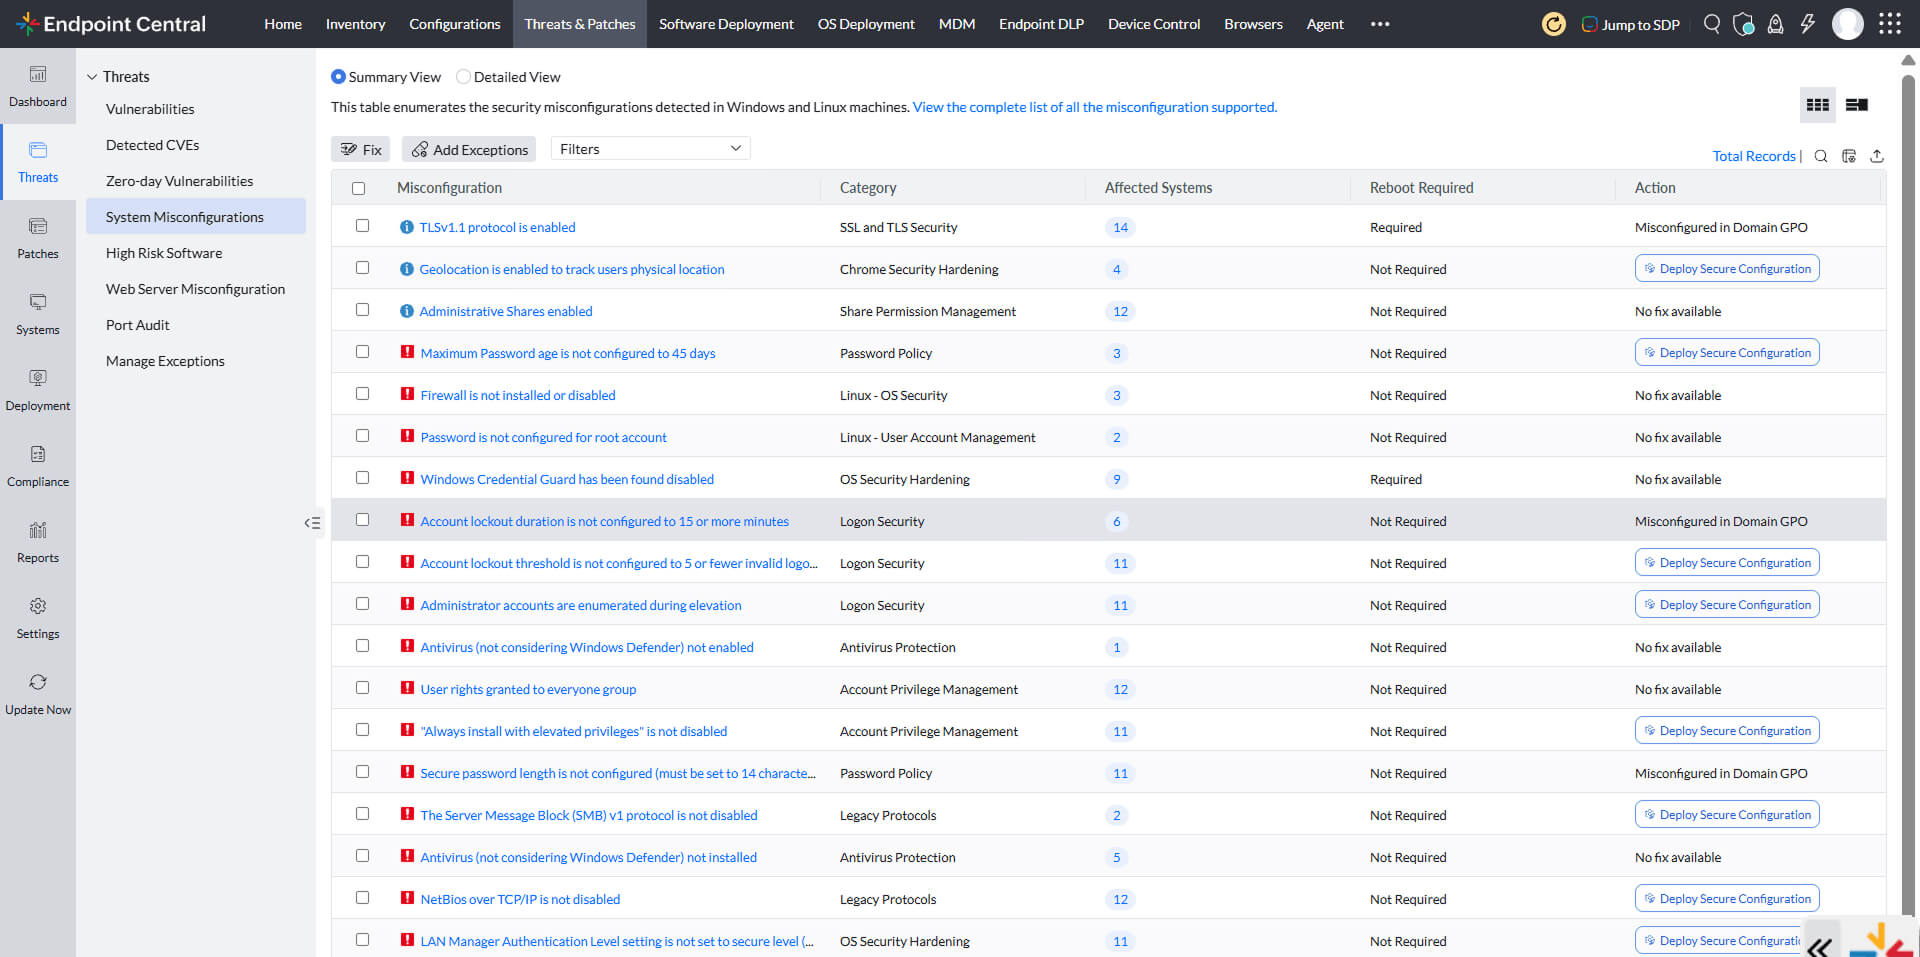
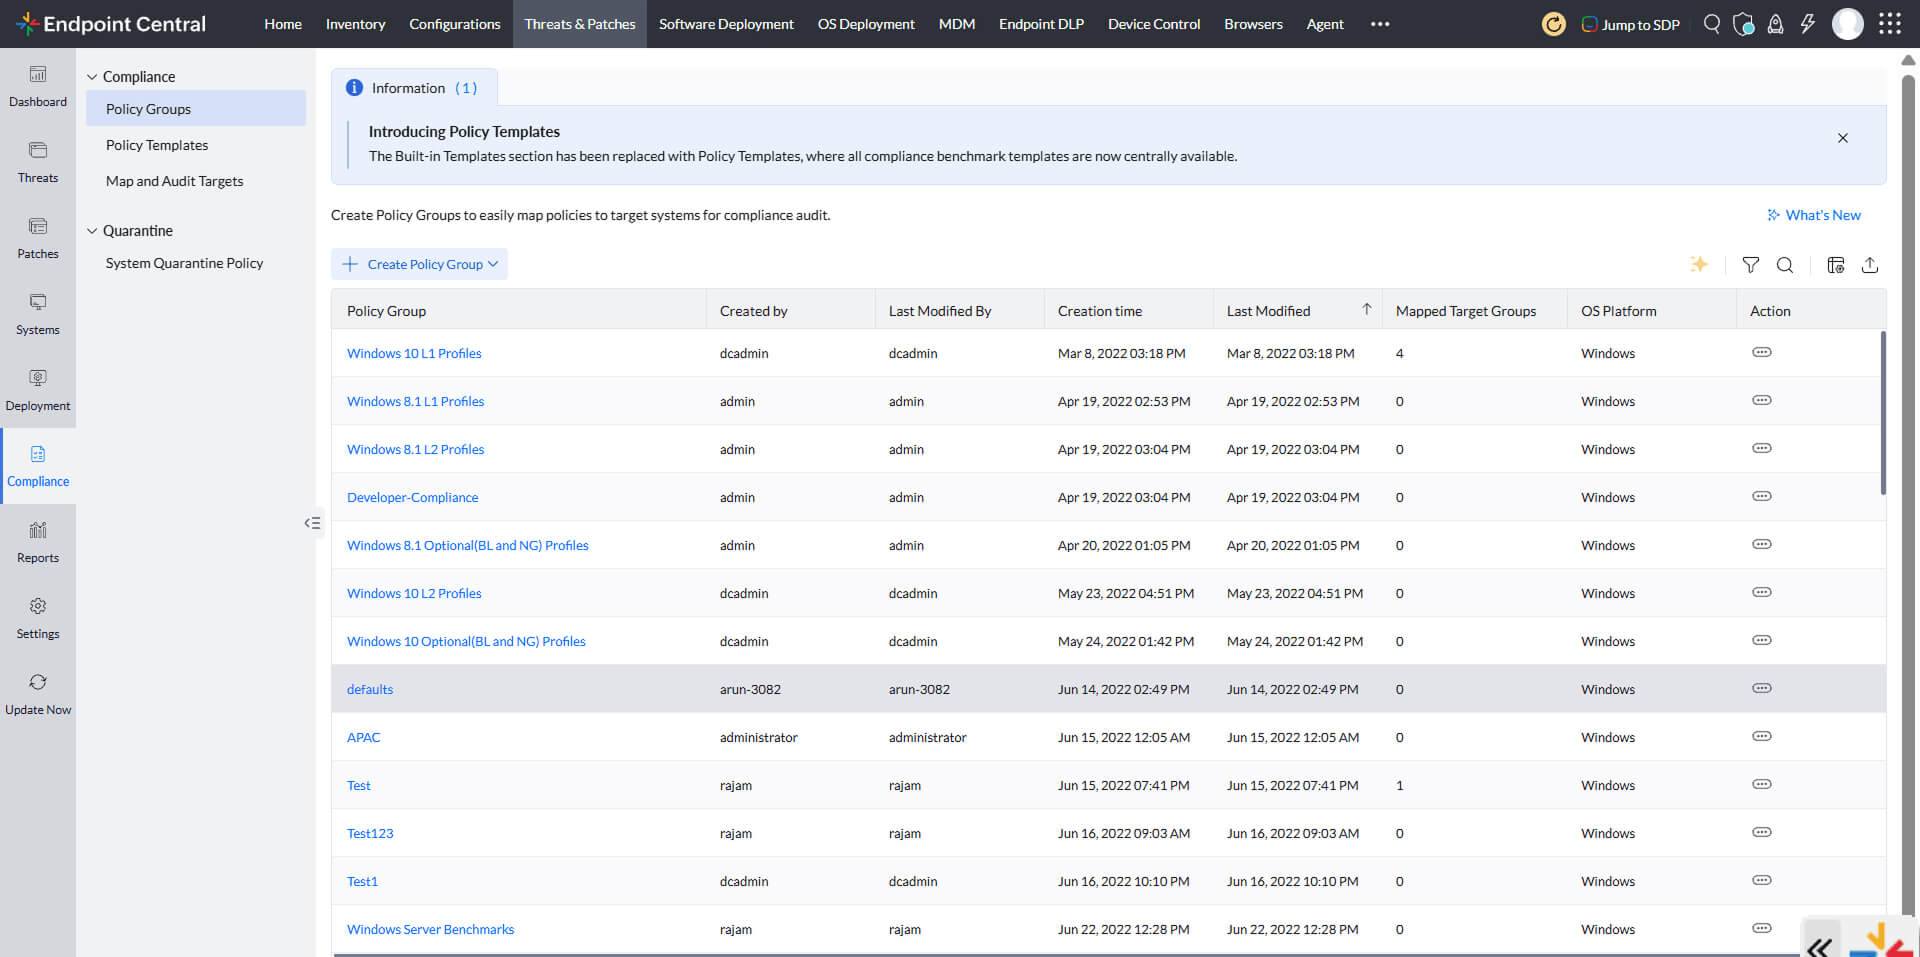
Monitor fleet-wide compliance in real time, flag risky configurations as they appear, and enforce security baselines so every endpoint stays healthy and policy-aligned.
Give SecOps and IT teams the complete picture behind every threat. Endpoint Central combines continuous telemetry, correlated signals, and attack chain visibility — equipping analysts to triage and contain incidents faster.
Consolidate the same capabilities into a single platform, eliminating the integration gaps, constant console-switching, and overlapping licenses of a multi-vendor setup.
Disconnected consoles and separate modules don't just bloat your budget. They fragment attention, bog down overall productivity, and bring security tasks to a crawl.
Endpoint Central replaces the patchwork with one platform and a single lightweight agent. Decommission legacy tools, eliminate redundant licenses, and give your team back the hours lost to switching screens. (forrester TEI report)
See what security teams around the industry have to say.
Consolidating security into one platform isn't just simpler. It's measurably more effective, faster, and lighter on your team.
Automate patching, remediation, and response so your team spends less time on repetitive work and more on what matters.
Detect and respond to threats faster than the industry average of 72 days, so exposure windows close before attackers can act.
Replace a patchwork of single-purpose vendors with one platform and cut the licensing, renewal, and integration costs that add up fast.
Correlated detections and AI-assisted triage mean your team sees fewer false positives and spends time on threats that actually matter.
Prevent threats and stay aligned with regulatory frameworks using built-in CIS benchmark templates and automated policy enforcement.
Isolate a compromised endpoint the moment a threat is flagged, cutting it off before a single breach spreads across your entire fleet.
One platform. One agent. Full visibility across every endpoint. See it in action with a free trial or a guided demo.
IT security software protects an organization's endpoints, data, and users from cyberthreats. A modern IT security solution centralizes visibility, applies policy-based controls, and automates prevention, detection, and response across on-site, remote, and mobile devices, so teams manage the whole estate from one console instead of a patchwork of tools.
Antivirus mainly detects known malware by signature. A full IT security tool adds layered protection: vulnerability and patch management, application and device control, next-gen antivirus with behavioral detection, EDR, data loss prevention, and compliance reporting. It defends across the whole attack lifecycle rather than reacting to known files alone.
Yes. Endpoint Central enrolls remote, hybrid, and BYOD devices through a single lightweight agent, applies the same policies you use on-site, and provides secure, VPN-free access to internal applications with continuous, context-aware trust checks on every connection.
Zia's autonomous agents reduce repetitive work. The EDR triage agent auto-investigates alerts, correlates the attack chain to MITRE ATT&CK, and prioritizes genuine incidents, while the patch troubleshooting agent diagnoses failed deployments and pinpoints root-cause fixes. Recommendations surface for review, so remediation actions stay under your team's control.
Yes. Endpoint Central unifies patch management, MDM, endpoint security, and asset management in one platform, and integrates with tools like ServiceNow, Active Directory, Okta, and leading security platforms. Consolidating onto one solution reduces tool sprawl and closes the gaps that open up between disconnected products.


 Ask Zia or build a query