Finding Active Directory (AD) users whose attributes are empty is a common data quality task. Accounts with a missing email address, manager, or department slip through address books, break dynamic distribution lists, and complicate audits. Being able to list every user with a null value in a given field is the first step to fixing it.
This guide shows two ways to filter for null attributes: one using PowerShell and the other via ManageEngine ADManager Plus. It includes how to group and sort the results to spot patterns, how to export them to CSV for reporting, and what errors you're most likely to hit.
An attribute in Active Directory can be empty for two different reasons, and telling them apart matters:
Before treating a blank result as a genuinely null attribute, always confirm that you asked for the property. A report of users with no department that omits -Properties Department will wrongly list everyone because the column was never populated in the output. Once you request the property, you can check whether it has a value and investigate why it's missing. This distinction is especially important when troubleshooting a Get-ADUser null attribute query.
Before you run the queries, a few things need to be in place:
Import the module and confirm it has loaded using the following PowerShell command:
									Import-Module ActiveDirectory

									Get-Module -Name ActiveDirectory
The server-side approach is the most efficient for finding users with an empty attribute because the directory does the filtering and returns only the matching accounts. For a typical Get-ADUser null attribute check that lists every user with no email address, run:
									Get-ADUser -Filter "EmailAddress -notlike '*'" -Properties EmailAddress |

									Select-Object Name, sAMAccountName
The same pattern works for any attribute. To find users with no manager assigned or without a telephone number:
									# No manager

									Get-ADUser -Filter "Manager -notlike '*'" -Properties Manager |

									Select-Object Name, sAMAccountName


									# No telephone number

									Get-ADUser -Filter "telephoneNumber -notlike '*'" -Properties telephoneNumber |

									Select-Object Name, sAMAccountName
Scoping the query to an organizational unit with -SearchBase can improve performance in a large directory and lets you check one department or site at a time:
									Get-ADUser -SearchBase "OU=Sales,DC=corp,DC=com" -Filter "EmailAddress -notlike '*'" `

									-Properties EmailAddress | Select-Object Name, sAMAccountName
The alternative is to retrieve users and filter them in the pipeline with Where-Object. This approach is slower than a server-side filter because it pulls the objects first and evaluates them locally. However, it's useful when you need conditions the -Filter syntax can't express or when you're already working with a retrieved set. The following command uses Where-Object to return users whose EmailAddress property is null or empty:
									Get-ADUser -Filter * -Properties EmailAddress |

									Where-Object { -not $_.EmailAddress } |

									Select-Object Name, sAMAccountName
The -not $_.EmailAddress test is true when the property is null or empty, isolating the users you want. For a stricter check that also catches values consisting only of spaces, test with [string]::IsNullOrWhiteSpace():
									Get-ADUser -Filter * -Properties Department |

									Where-Object { [string]::IsNullOrWhiteSpace($_.Department) } |

									Select-Object Name, sAMAccountName
As a rule, prefer the server-side -Filter for simple null checks on a single attribute and reach for Where-Object only when the logic is more complex than the filter language allows.
There are two ways to express this attribute is empty in a Get-ADUser filter. The PowerShell filter idiom uses -notlike '*', which matches objects where the attribute has no value at all since a null attribute matches no wildcard. The LDAP equivalent, passed with -LDAPFilter, is (!(attribute=*)) and read as not(attribute has any value). Both run server-side and return the same users:
									# PowerShell filter idiom

									Get-ADUser -Filter "Department -notlike '*'" -Properties Department


									# Equivalent LDAP filter

									Get-ADUser -LDAPFilter "(!(department=*))" -Properties Department
Once you have the users with a missing attribute, grouping and sorting them can help you see where the gaps cluster, which often points at the cause (a particular OU or accounts created by a certain process). To count how many users are missing a department, broken down by their office, pipe the results to Group-Object:
									Get-ADUser -Filter "Department -notlike '*'" -Properties Department, Office |

									Group-Object Office |

									Select-Object Name, Count |

									Sort-Object Count -Descending
Sort-Object orders the output, and its -Unique switch removes duplicates when you only want the distinct values. To list the distinct offices that contain users with no manager, you can use:
									Get-ADUser -Filter "Manager -notlike '*'" -Properties Manager, Office |

									Select-Object -ExpandProperty Office |

									Sort-Object -Unique
Select-Object -ExpandProperty returns the raw values of a single property rather than objects, which is what lets Sort-Object -Unique produce a clean list. Note that -ExpandProperty throws an error if the property is null on any object, so pair it with a filter that has already removed null attributes, as above.
To hand the list to someone or track it over time, export it to CSV. Pipe the filtered users to Export-Csv and select the columns that make the report useful. Never use Format-Table first since formatting turns the objects into display text that doesn't export cleanly:
									Get-ADUser -Filter "EmailAddress -notlike '*'" -Properties EmailAddress, Department, Title |

									Select-Object Name, sAMAccountName, Department, Title |

									Export-Csv -Path "C:\Reports\users-missing-email.csv" -NoTypeInformation -Encoding UTF8
For a reusable check, wrap the logic in a small script that takes the attribute name and exports the users missing it so the same tool covers email, manager, department, or any other field.
The parameters and cmdlets below are used for null-attribute reporting in PowerShell.
| Parameter or cmdlet | Description |
|---|---|
| Get-ADUser | Retrieves user objects from Active Directory. |
| -Filter | Filters users server-side; "attr -notlike ''"* matches an empty attribute. |
| -LDAPFilter | An alternative filter taking an LDAP string, such as (!(department=))*. |
| -Properties | Requests non-default attributes so their values are returned and not left blank. |
| Where-Object | Filters retrieved objects in the pipeline, such as { -not $_.EmailAddress }. |
| Group-Object | Groups results to count and spot patterns, such as null attributes per office. |
| Sort-Object | Orders results; -Unique returns distinct values. |
| Export-Csv | Writes the results to a CSV file for reporting. |
ManageEngine ADManager Plus is a unified AD, Exchange, and Microsoft 365 management and reporting tool with prebuilt reports that surface accounts with missing attributes, enabling you to fix them in bulk from the same console with no scripting.
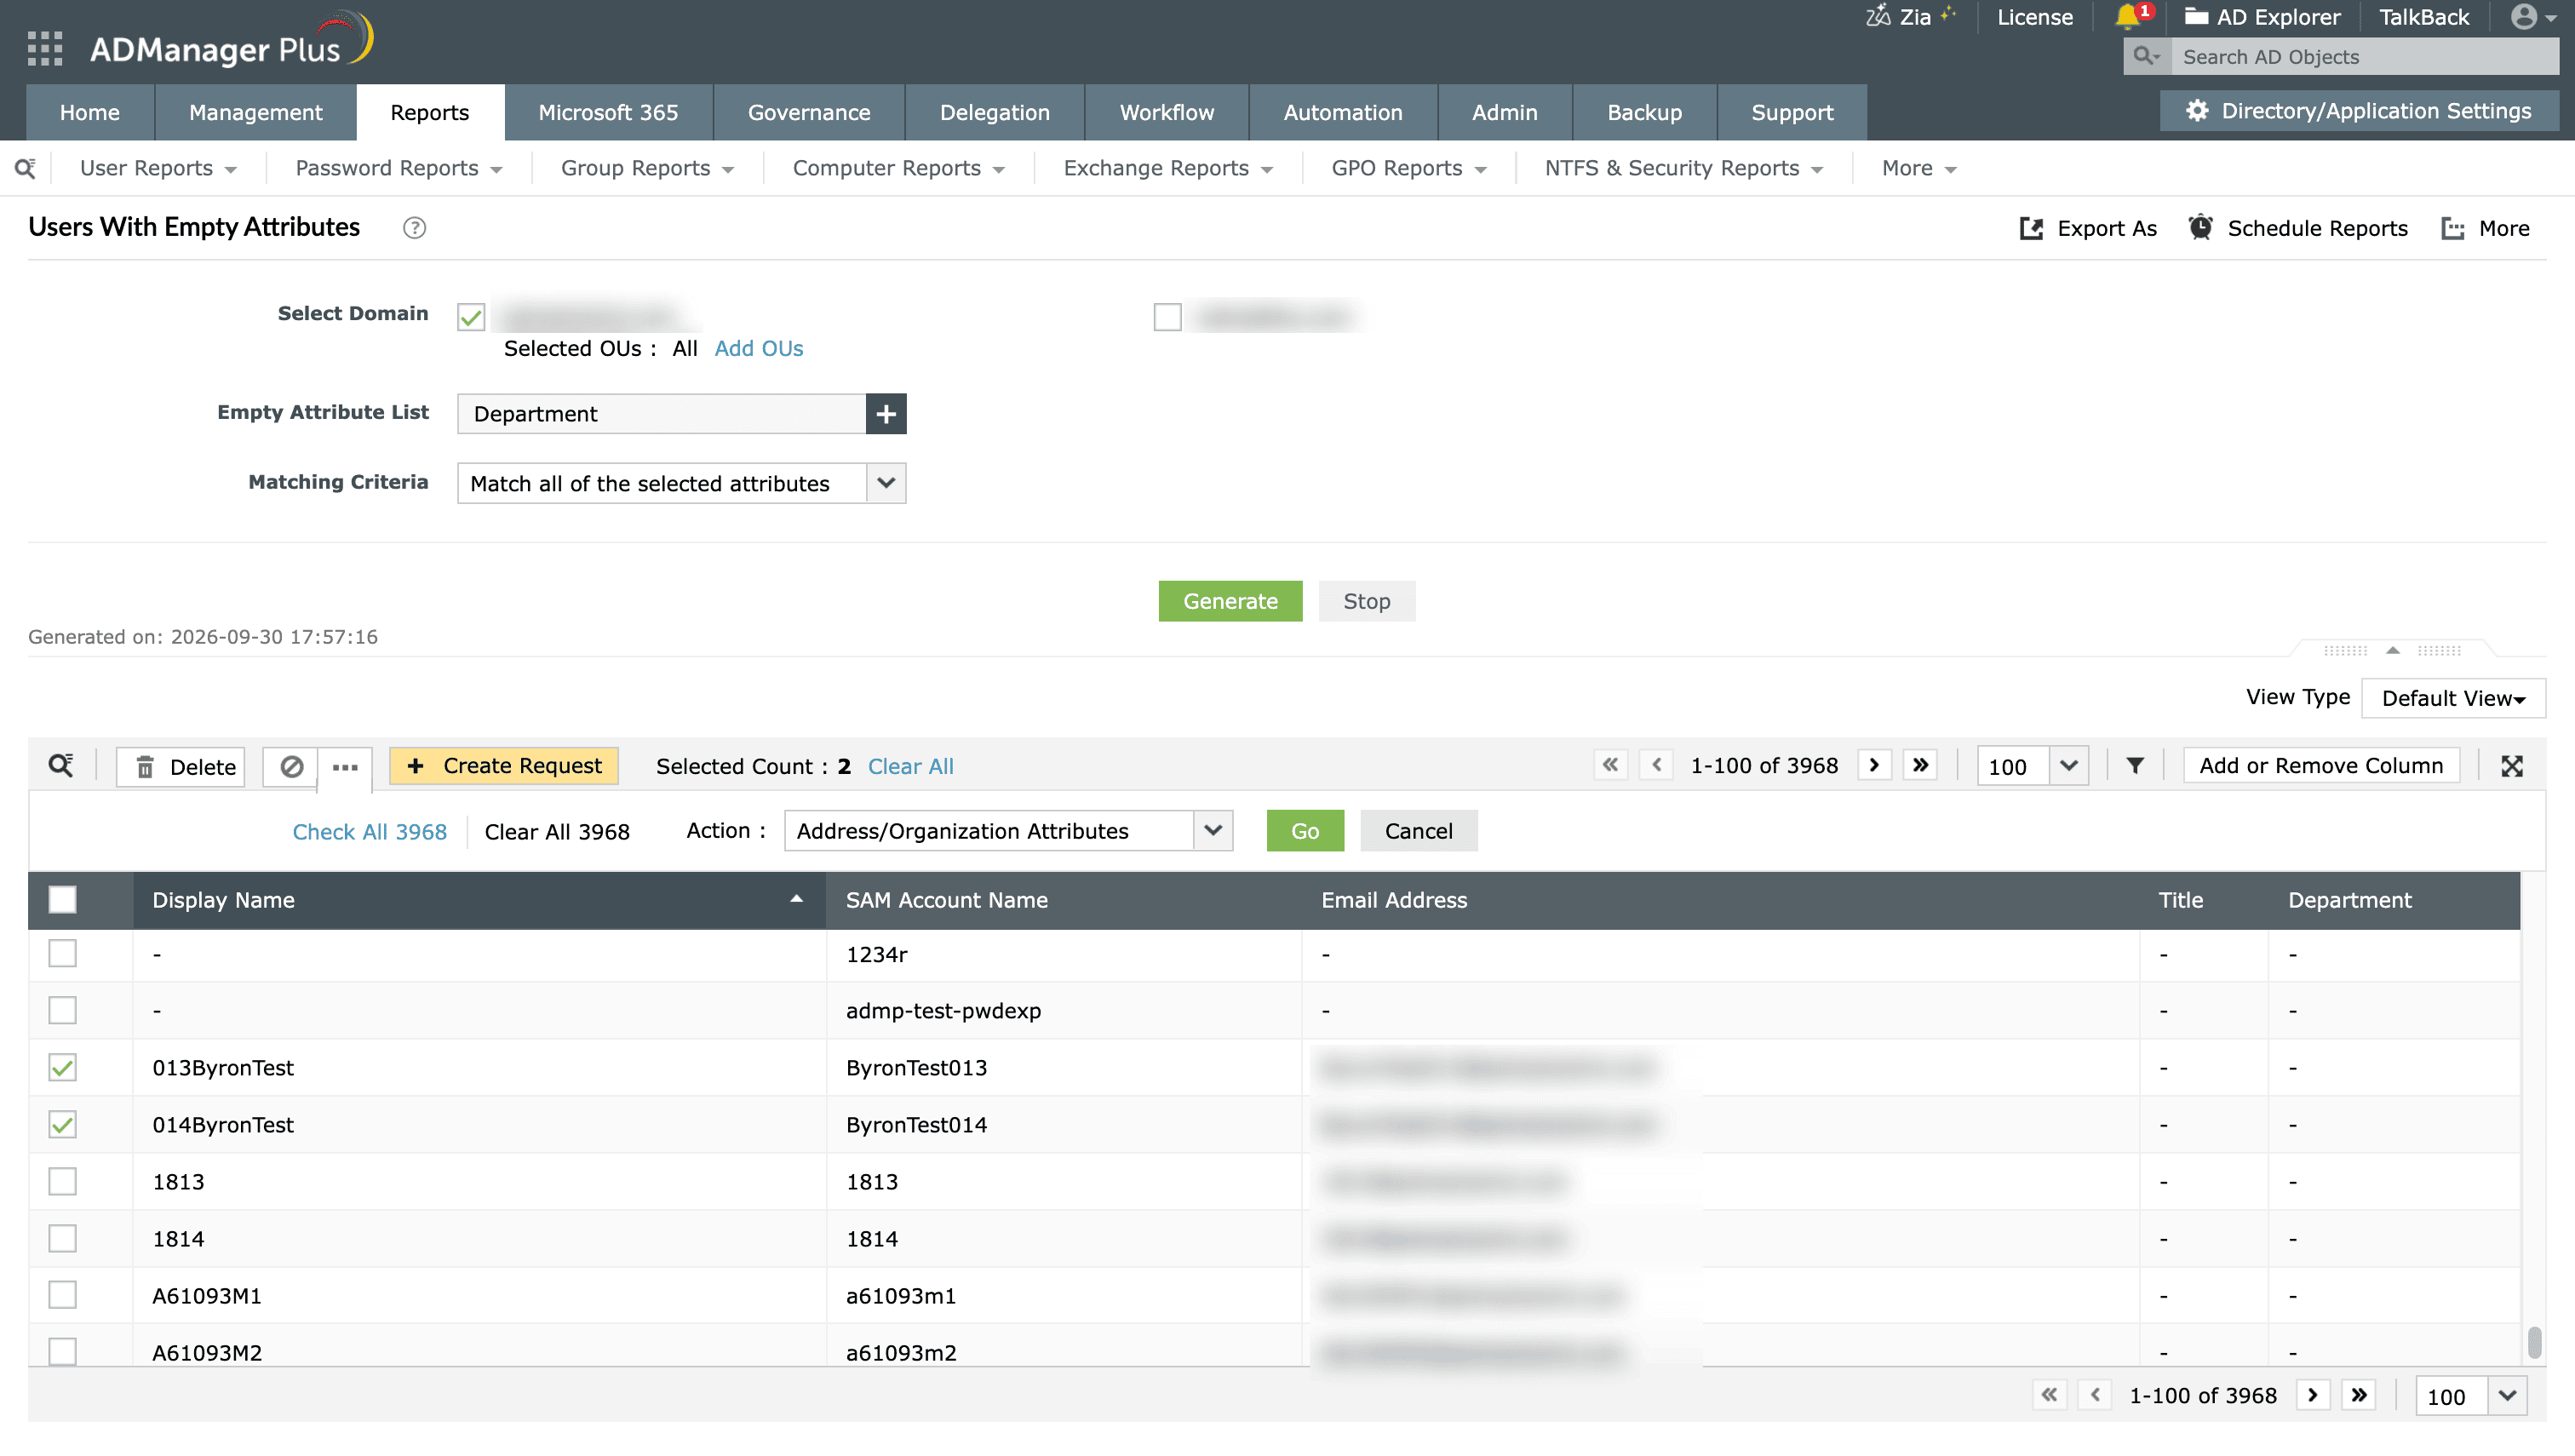
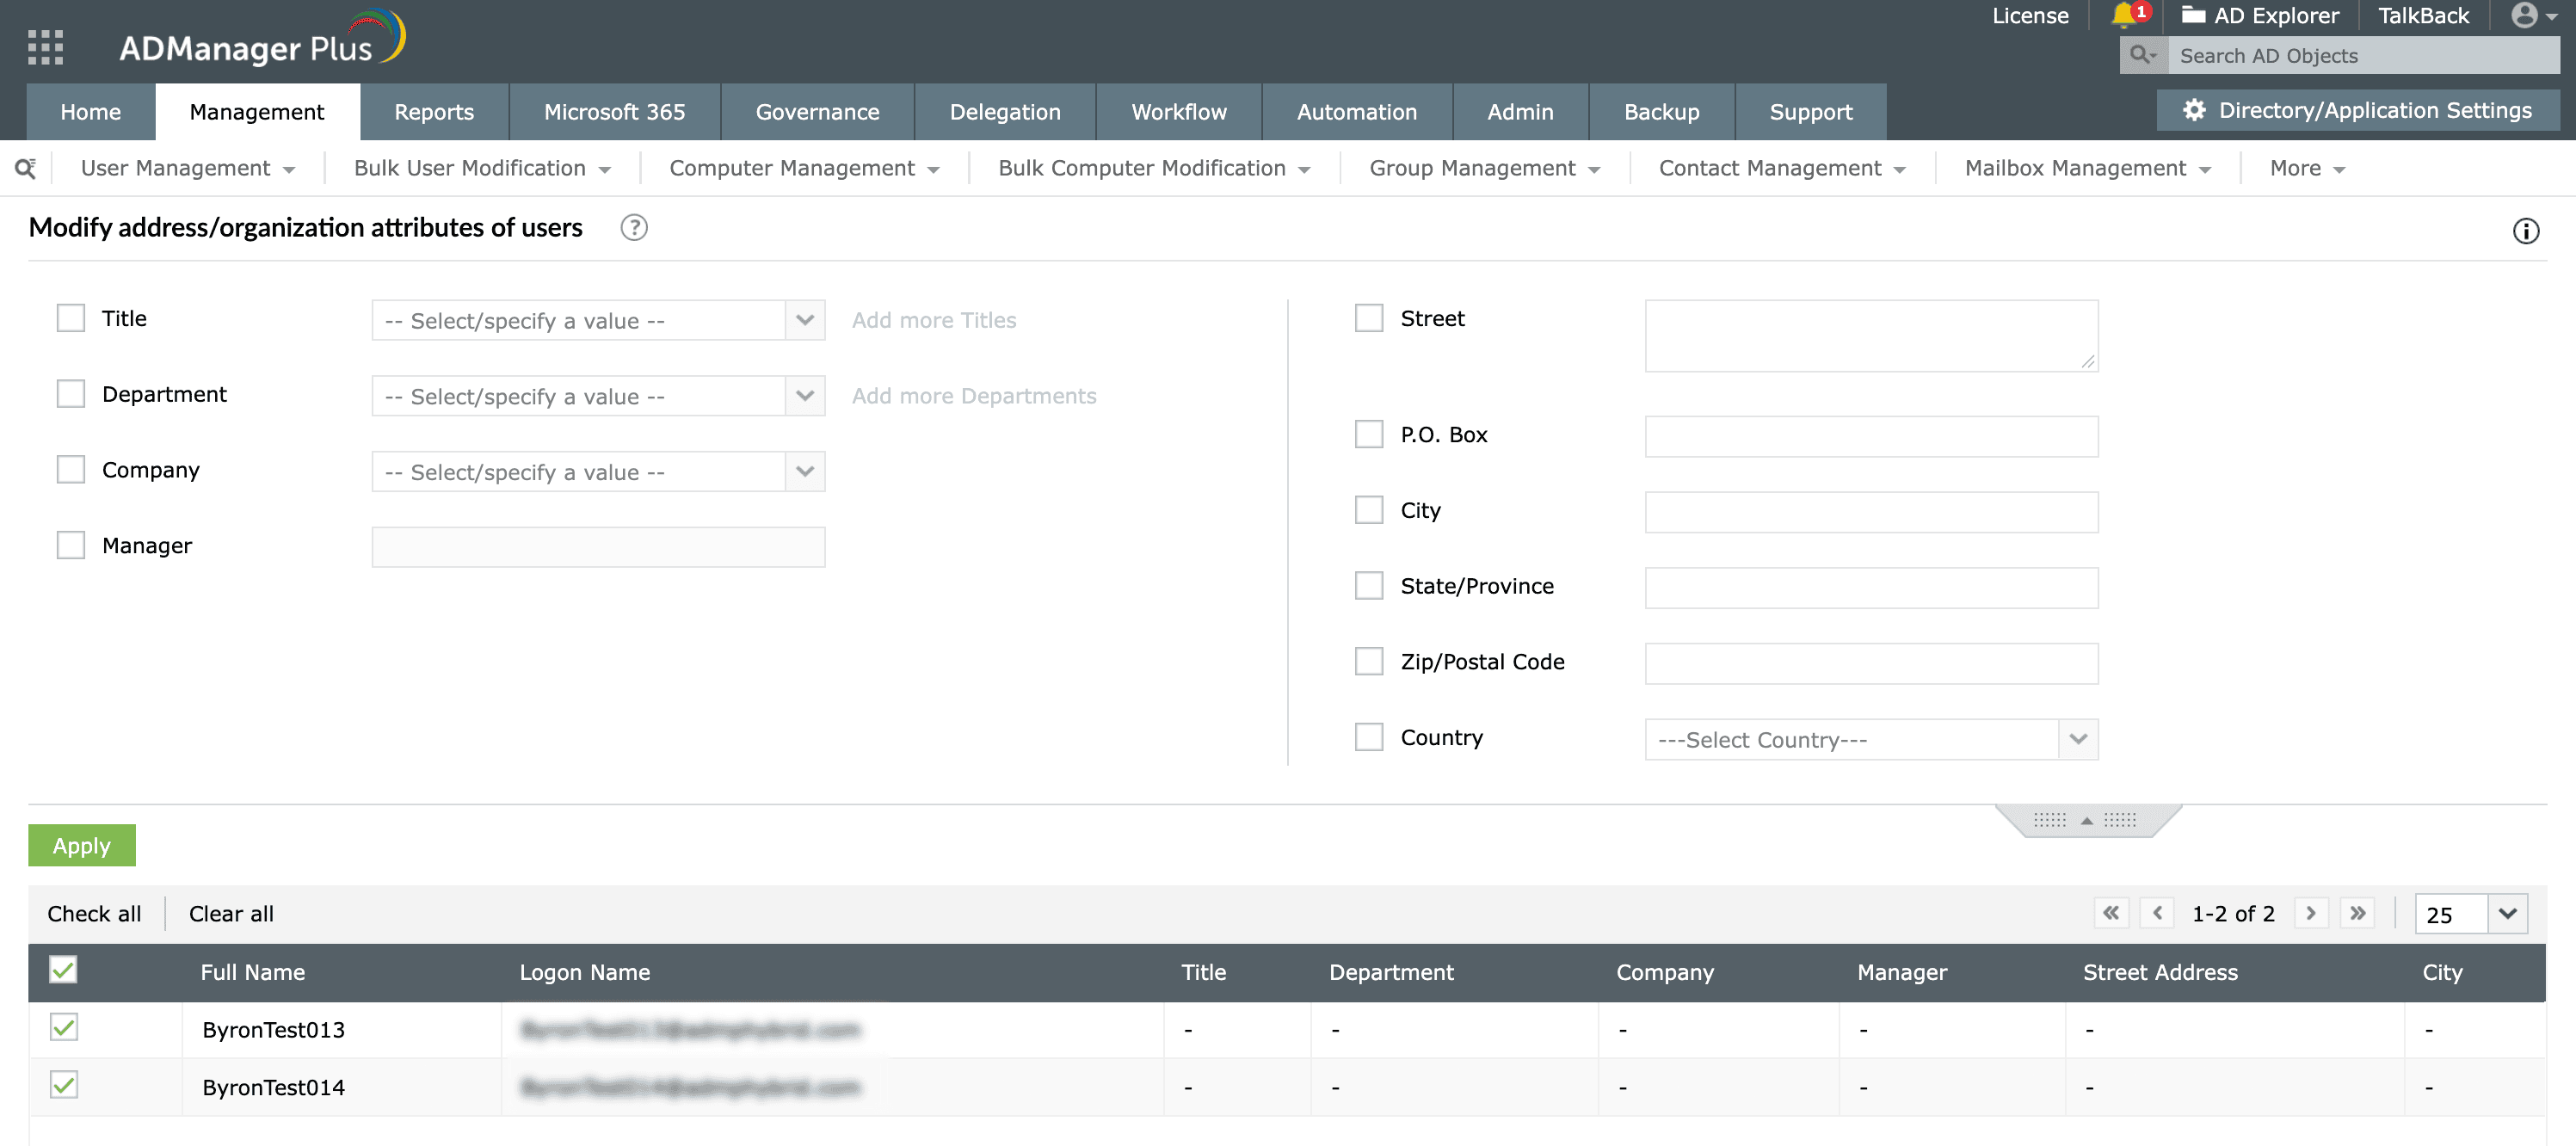
From the generated report, select users and click the ellipsis icon (...). Use the Action drop-down to choose your preferred action, such as Profile, Contact, or Address/Organization Attributes. This will open the Modify address/organization attributes of users window from where you can populate the attributes of your choice.
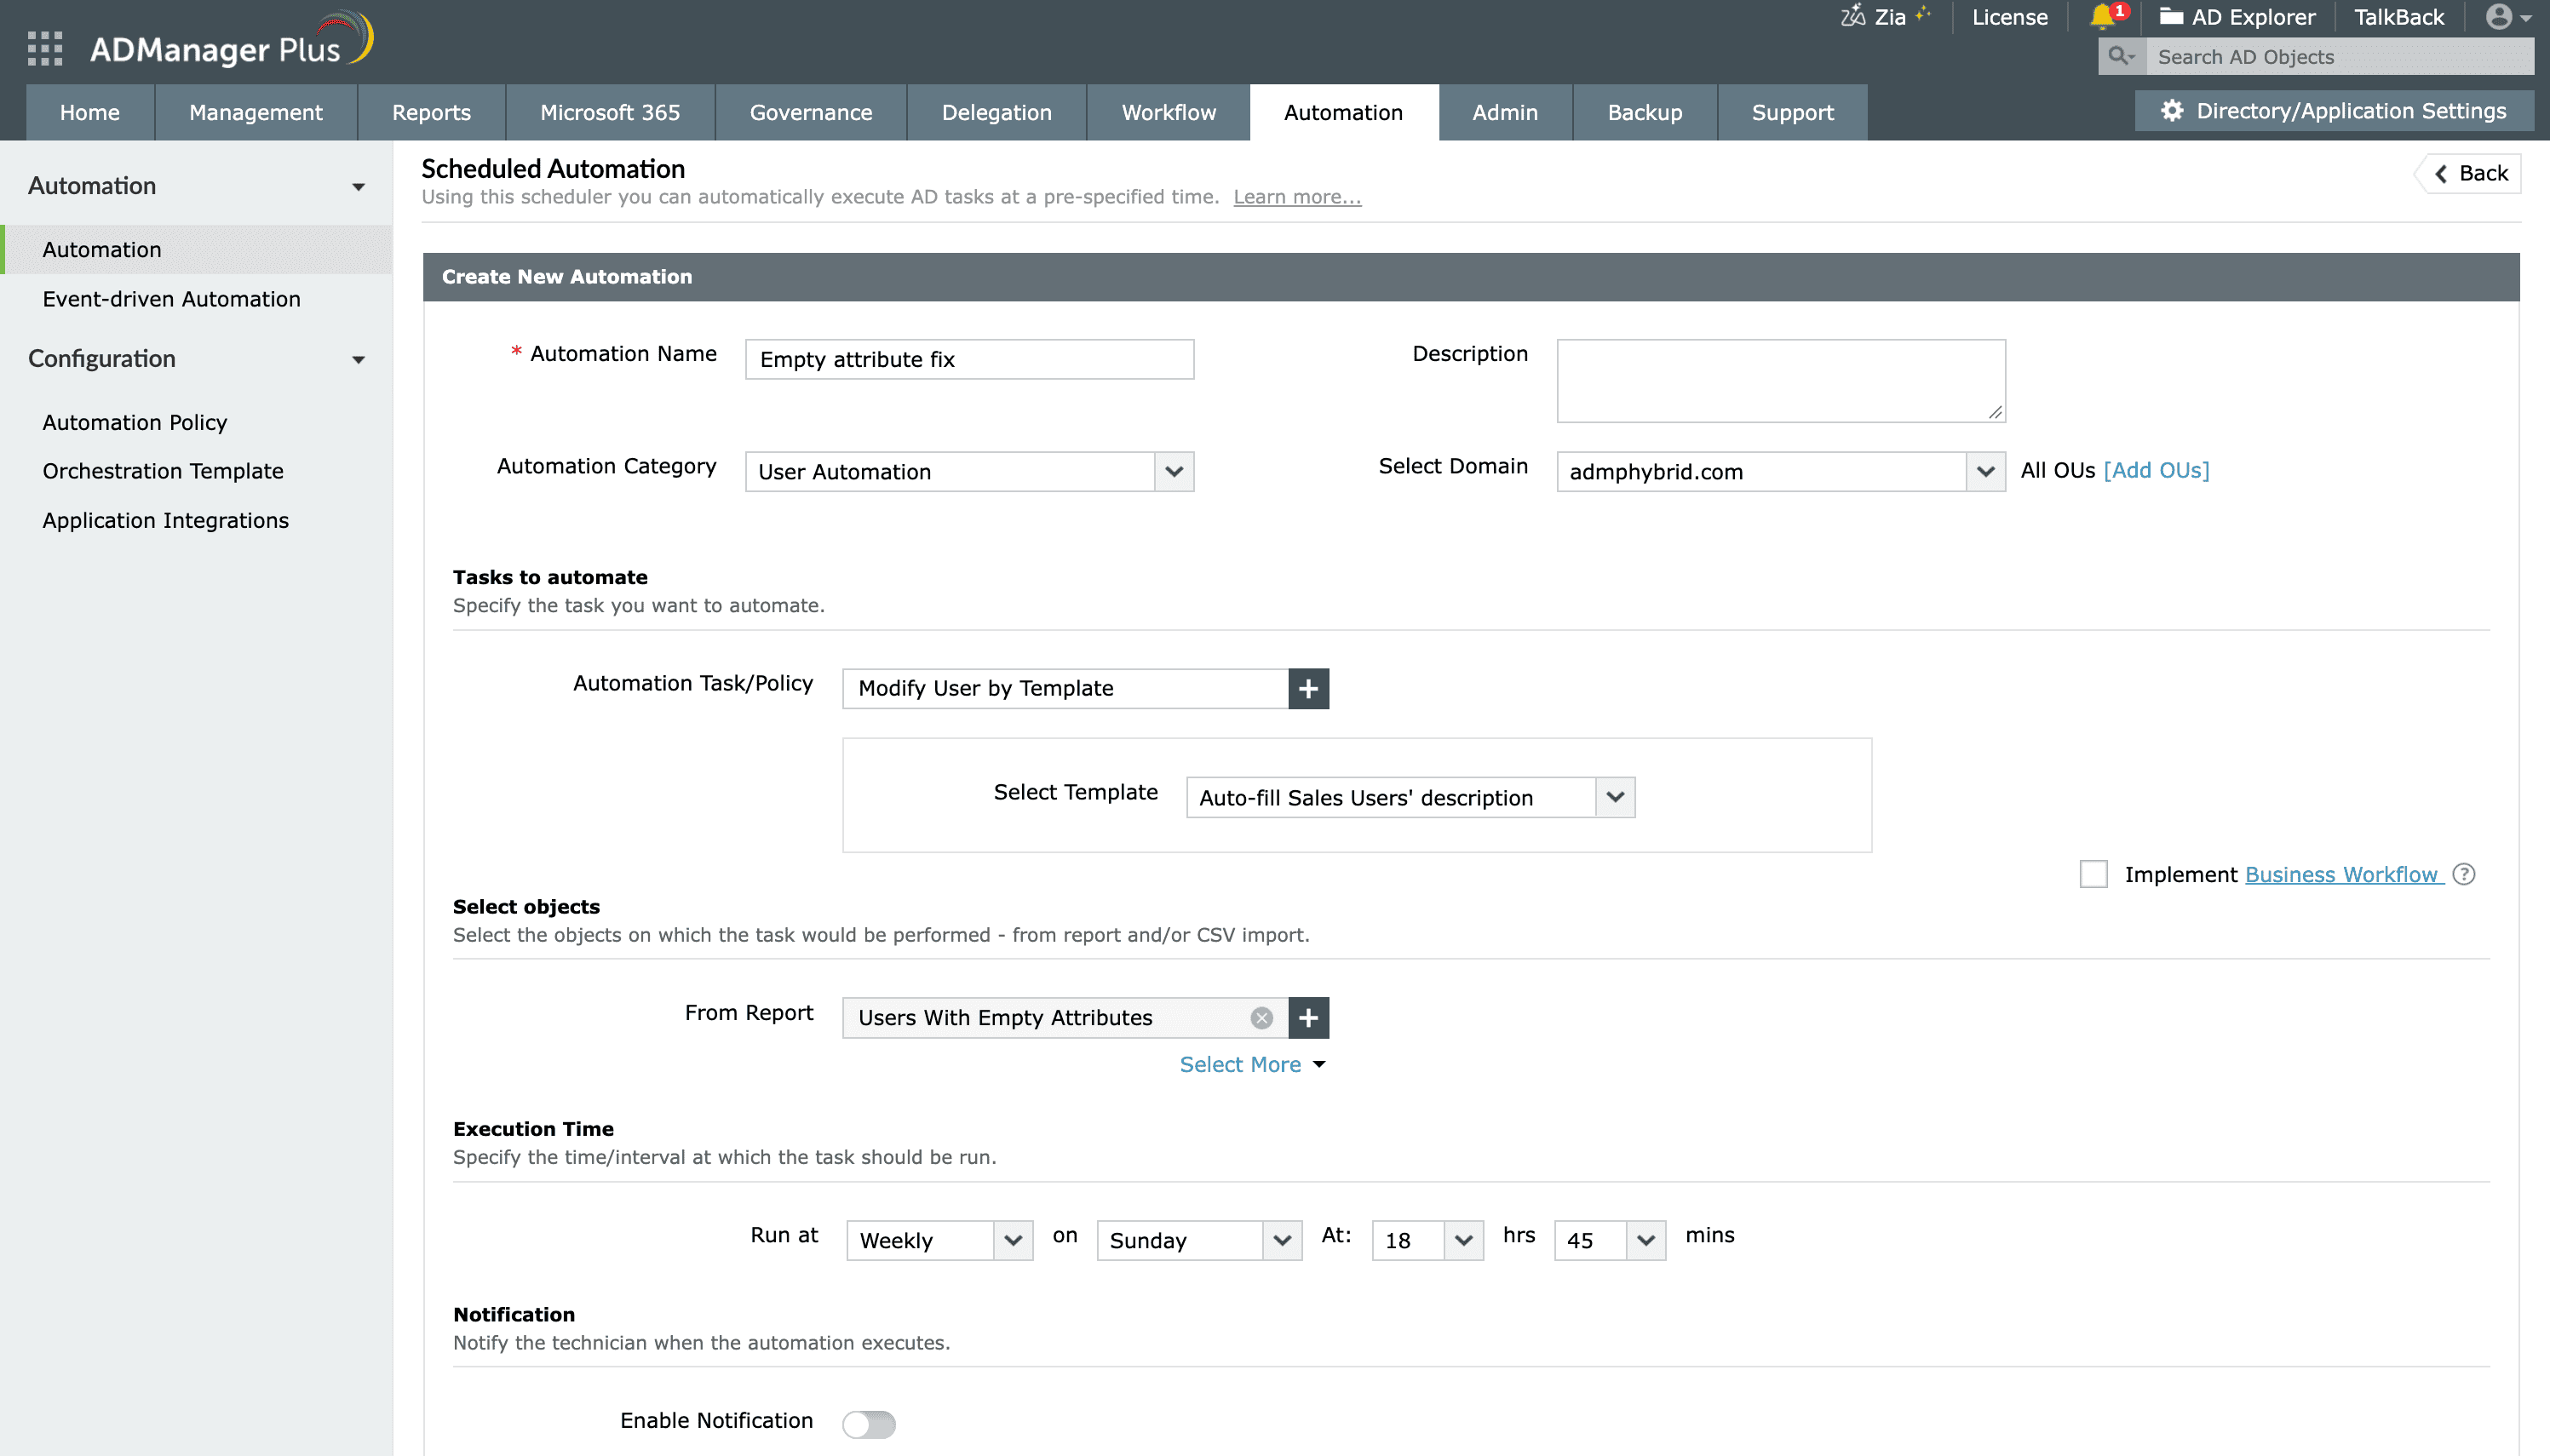
For accounts that already have gaps, ADManager Plus' Automation feature can find and fix them on a schedule instead of requiring a technician to do it by hand.
ADManager Plus replaces scripts and one-off queries with a single console for AD, Microsoft 365, and Exchange management and reporting:
User attributes are the individual fields stored on an AD user object that describe the account and the person behind it, such as sAMAccountName, DisplayName, EmailAddress, Department, Manager, and telephoneNumber. Each attribute holds a single value or, in some cases, multiple values, and together they make up the user record. Many attributes are optional, which is why they can be null, and reporting on the empty ones is how you find records that need completing.
Using PowerShell, retrieve the user with Get-ADUser and request the attributes you want with -Properties since the cmdlet returns only a default set otherwise. To see the full set of populated attributes for one user, use -Properties *:
												Get-ADUser -Identity "jsmith" -Properties * |

												Format-List
For specific attributes, name them instead of using an *, for example -Properties Department, Manager, EmailAddress.
For a script-free approach, ADManager Plus offers a wide range of reports that help you view, filter, and manage AD attributes at scale.
Use PowerShell to query the users with -Properties * and pipe them to Export-Csv. Because * returns a large number of attributes, select the ones you need for the report rather than exporting every field:
												Get-ADUser -Filter * -Properties * |

												Select-Object Name, sAMAccountName, Department, Title, EmailAddress, Manager |

												Export-Csv -Path "C:\Reports\all-user-attributes.csv" -NoTypeInformation
Exporting every attribute with Select-Object * produces an unwieldy file with system properties you rarely need, so a targeted column list is usually the better report.
ADManager Plus provides a full user-attribute report through its console without scripting.

